commit 44567b7d57448f2791c7e5710e18aa6066f460cc Author: chenc <1458513@qq.com> Date: Mon Jul 15 13:21:08 2024 +0800 source diff --git a/.gitignore b/.gitignore new file mode 100644 index 0000000..882ecd6 --- /dev/null +++ b/.gitignore @@ -0,0 +1 @@ +install.log diff --git a/LICENSE b/LICENSE new file mode 100644 index 0000000..8f71f43 --- /dev/null +++ b/LICENSE @@ -0,0 +1,202 @@ + Apache License + Version 2.0, January 2004 + http://www.apache.org/licenses/ + + TERMS AND CONDITIONS FOR USE, REPRODUCTION, AND DISTRIBUTION + + 1. Definitions. + + "License" shall mean the terms and conditions for use, reproduction, + and distribution as defined by Sections 1 through 9 of this document. + + "Licensor" shall mean the copyright owner or entity authorized by + the copyright owner that is granting the License. + + "Legal Entity" shall mean the union of the acting entity and all + other entities that control, are controlled by, or are under common + control with that entity. For the purposes of this definition, + "control" means (i) the power, direct or indirect, to cause the + direction or management of such entity, whether by contract or + otherwise, or (ii) ownership of fifty percent (50%) or more of the + outstanding shares, or (iii) beneficial ownership of such entity. + + "You" (or "Your") shall mean an individual or Legal Entity + exercising permissions granted by this License. + + "Source" form shall mean the preferred form for making modifications, + including but not limited to software source code, documentation + source, and configuration files. + + "Object" form shall mean any form resulting from mechanical + transformation or translation of a Source form, including but + not limited to compiled object code, generated documentation, + and conversions to other media types. + + "Work" shall mean the work of authorship, whether in Source or + Object form, made available under the License, as indicated by a + copyright notice that is included in or attached to the work + (an example is provided in the Appendix below). + + "Derivative Works" shall mean any work, whether in Source or Object + form, that is based on (or derived from) the Work and for which the + editorial revisions, annotations, elaborations, or other modifications + represent, as a whole, an original work of authorship. For the purposes + of this License, Derivative Works shall not include works that remain + separable from, or merely link (or bind by name) to the interfaces of, + the Work and Derivative Works thereof. + + "Contribution" shall mean any work of authorship, including + the original version of the Work and any modifications or additions + to that Work or Derivative Works thereof, that is intentionally + submitted to Licensor for inclusion in the Work by the copyright owner + or by an individual or Legal Entity authorized to submit on behalf of + the copyright owner. For the purposes of this definition, "submitted" + means any form of electronic, verbal, or written communication sent + to the Licensor or its representatives, including but not limited to + communication on electronic mailing lists, source code control systems, + and issue tracking systems that are managed by, or on behalf of, the + Licensor for the purpose of discussing and improving the Work, but + excluding communication that is conspicuously marked or otherwise + designated in writing by the copyright owner as "Not a Contribution." + + "Contributor" shall mean Licensor and any individual or Legal Entity + on behalf of whom a Contribution has been received by Licensor and + subsequently incorporated within the Work. + + 2. Grant of Copyright License. Subject to the terms and conditions of + this License, each Contributor hereby grants to You a perpetual, + worldwide, non-exclusive, no-charge, royalty-free, irrevocable + copyright license to reproduce, prepare Derivative Works of, + publicly display, publicly perform, sublicense, and distribute the + Work and such Derivative Works in Source or Object form. + + 3. Grant of Patent License. Subject to the terms and conditions of + this License, each Contributor hereby grants to You a perpetual, + worldwide, non-exclusive, no-charge, royalty-free, irrevocable + (except as stated in this section) patent license to make, have made, + use, offer to sell, sell, import, and otherwise transfer the Work, + where such license applies only to those patent claims licensable + by such Contributor that are necessarily infringed by their + Contribution(s) alone or by combination of their Contribution(s) + with the Work to which such Contribution(s) was submitted. If You + institute patent litigation against any entity (including a + cross-claim or counterclaim in a lawsuit) alleging that the Work + or a Contribution incorporated within the Work constitutes direct + or contributory patent infringement, then any patent licenses + granted to You under this License for that Work shall terminate + as of the date such litigation is filed. + + 4. Redistribution. You may reproduce and distribute copies of the + Work or Derivative Works thereof in any medium, with or without + modifications, and in Source or Object form, provided that You + meet the following conditions: + + (a) You must give any other recipients of the Work or + Derivative Works a copy of this License; and + + (b) You must cause any modified files to carry prominent notices + stating that You changed the files; and + + (c) You must retain, in the Source form of any Derivative Works + that You distribute, all copyright, patent, trademark, and + attribution notices from the Source form of the Work, + excluding those notices that do not pertain to any part of + the Derivative Works; and + + (d) If the Work includes a "NOTICE" text file as part of its + distribution, then any Derivative Works that You distribute must + include a readable copy of the attribution notices contained + within such NOTICE file, excluding those notices that do not + pertain to any part of the Derivative Works, in at least one + of the following places: within a NOTICE text file distributed + as part of the Derivative Works; within the Source form or + documentation, if provided along with the Derivative Works; or, + within a display generated by the Derivative Works, if and + wherever such third-party notices normally appear. The contents + of the NOTICE file are for informational purposes only and + do not modify the License. You may add Your own attribution + notices within Derivative Works that You distribute, alongside + or as an addendum to the NOTICE text from the Work, provided + that such additional attribution notices cannot be construed + as modifying the License. + + You may add Your own copyright statement to Your modifications and + may provide additional or different license terms and conditions + for use, reproduction, or distribution of Your modifications, or + for any such Derivative Works as a whole, provided Your use, + reproduction, and distribution of the Work otherwise complies with + the conditions stated in this License. + + 5. Submission of Contributions. Unless You explicitly state otherwise, + any Contribution intentionally submitted for inclusion in the Work + by You to the Licensor shall be under the terms and conditions of + this License, without any additional terms or conditions. + Notwithstanding the above, nothing herein shall supersede or modify + the terms of any separate license agreement you may have executed + with Licensor regarding such Contributions. + + 6. Trademarks. This License does not grant permission to use the trade + names, trademarks, service marks, or product names of the Licensor, + except as required for reasonable and customary use in describing the + origin of the Work and reproducing the content of the NOTICE file. + + 7. Disclaimer of Warranty. Unless required by applicable law or + agreed to in writing, Licensor provides the Work (and each + Contributor provides its Contributions) on an "AS IS" BASIS, + WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or + implied, including, without limitation, any warranties or conditions + of TITLE, NON-INFRINGEMENT, MERCHANTABILITY, or FITNESS FOR A + PARTICULAR PURPOSE. You are solely responsible for determining the + appropriateness of using or redistributing the Work and assume any + risks associated with Your exercise of permissions under this License. + + 8. Limitation of Liability. In no event and under no legal theory, + whether in tort (including negligence), contract, or otherwise, + unless required by applicable law (such as deliberate and grossly + negligent acts) or agreed to in writing, shall any Contributor be + liable to You for damages, including any direct, indirect, special, + incidental, or consequential damages of any character arising as a + result of this License or out of the use or inability to use the + Work (including but not limited to damages for loss of goodwill, + work stoppage, computer failure or malfunction, or any and all + other commercial damages or losses), even if such Contributor + has been advised of the possibility of such damages. + + 9. Accepting Warranty or Additional Liability. While redistributing + the Work or Derivative Works thereof, You may choose to offer, + and charge a fee for, acceptance of support, warranty, indemnity, + or other liability obligations and/or rights consistent with this + License. However, in accepting such obligations, You may act only + on Your own behalf and on Your sole responsibility, not on behalf + of any other Contributor, and only if You agree to indemnify, + defend, and hold each Contributor harmless for any liability + incurred by, or claims asserted against, such Contributor by reason + of your accepting any such warranty or additional liability. + + END OF TERMS AND CONDITIONS + + APPENDIX: How to apply the Apache License to your work. + + To apply the Apache License to your work, attach the following + boilerplate notice, with the fields enclosed by brackets "{}" + replaced with your own identifying information. (Don't include + the brackets!) The text should be enclosed in the appropriate + comment syntax for the file format. We also recommend that a + file or class name and description of purpose be included on the + same "printed page" as the copyright notice for easier + identification within third-party archives. + + Copyright {yyyy} {name of copyright owner} + + Licensed under the Apache License, Version 2.0 (the "License"); + you may not use this file except in compliance with the License. + You may obtain a copy of the License at + + http://www.apache.org/licenses/LICENSE-2.0 + + Unless required by applicable law or agreed to in writing, software + distributed under the License is distributed on an "AS IS" BASIS, + WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or implied. + See the License for the specific language governing permissions and + limitations under the License. + diff --git a/README.md b/README.md new file mode 100644 index 0000000..b2d5305 --- /dev/null +++ b/README.md @@ -0,0 +1,154 @@ +This script is written using the shell, in order to quickly deploy `LEMP`/`LAMP`/`LNMP`/`LNMPA`/`LTMP`(Linux, Nginx/Tengine/OpenResty, MySQL in a production environment/MariaDB/Percona, PHP, JAVA), applicable to RHEL 7, 8, 9(including CentOS,RedHat,AlmaLinux,Rocky), Debian 9, 10, 11, 12, Ubuntu 16, 18, 20, 22 and Fedora 27+ of 64. + +Script properties: +- Continually updated, Provide Shell Interaction and Autoinstall +- Source compiler installation, most stable source is the latest version, and download from the official site +- Some security optimization +- Providing a plurality of database versions (MySQL-8.0, MySQL-5.7, MySQL-5.6, MySQL-5.5, MariaDB-10.11, MariaDB-10.5, MariaDB-10.4, MariaDB-5.5, Percona-8.0, Percona-5.7, Percona-5.6, Percona-5.5, PostgreSQL, MongoDB) +- Providing multiple PHP versions (PHP-8.3, PHP-8.2, PHP-8.1, PHP-8.0, PHP-7.4, PHP-7.3, PHP-7.2, PHP-7.1, PHP-7.0, PHP-5.6, PHP-5.5, PHP-5.4, PHP-5.3) +- Provide Nginx, Tengine, OpenResty, Caddy, Apache and ngx_lua_waf +- Providing a plurality of Tomcat version (Tomcat-10, Tomcat-9, Tomcat-8, Tomcat-7) +- Providing a plurality of JDK version (OpenJDK-8, OpenJDK-11, OpenJDK-17) +- According to their needs to install PHP Cache Accelerator provides ZendOPcache, xcache, apcu, eAccelerator. And php extensions,include ZendGuardLoader,ionCube,SourceGuardian,imagick,gmagick,fileinfo,imap,ldap,calendar,phalcon,yaf,yar,redis,memcached,memcache,mongodb,swoole,xdebug +- Installation Nodejs, Pureftpd, phpMyAdmin according to their needs +- Install memcached, redis according to their needs +- Jemalloc optimize MySQL, Nginx +- Providing add a virtual host script, include Let's Encrypt SSL certificate +- Provide Nginx/Tengine/OpenResty/Apache/Tomcat, MySQL/MariaDB/Percona, PHP, Redis, Memcached, phpMyAdmin upgrade script +- Provide local,remote(rsync between servers),Aliyun OSS,Qcloud COS,UPYUN,QINIU,Amazon S3,Google Drive and Dropbox backup script + +## Installation + +Install the dependencies for your distro, download the source and run the installation script. + +#### CentOS/Redhat + +```bash +yum -y install wget screen +``` + +#### Debian/Ubuntu + +```bash +apt-get -y install wget screen +``` + +#### Download Source and Install + +```bash +wget http://mirrors.oneinstack.com/oneinstack-full.tar.gz +tar xzf oneinstack-full.tar.gz +cd oneinstack +``` + +If you disconnect during installation, you can execute the command `screen -r oneinstack` to reconnect to the install window +```bash +screen -S oneinstack +``` + +If you need to modify the directory (installation, data storage, Nginx logs), modify `options.conf` file before running install.sh +```bash +./install.sh +``` + +## How to install another PHP version + +```bash +~/oneinstack/install.sh --mphp_ver 54 + +``` + +## How to add Extensions + +```bash +~/oneinstack/addons.sh + +``` + +## How to add a virtual host + +```bash +~/oneinstack/vhost.sh +``` + +## How to delete a virtual host + +```bash +~/oneinstack/vhost.sh --del +``` + +## How to add FTP virtual user + +```bash +~/oneinstack/pureftpd_vhost.sh +``` + +## How to backup + +```bash +~/oneinstack/backup_setup.sh // Backup parameters +~/oneinstack/backup.sh // Perform the backup immediately +crontab -l // Can be added to scheduled tasks, such as automatic backups every day 1:00 + 0 1 * * * cd ~/oneinstack/backup.sh > /dev/null 2>&1 & +``` + +## How to manage service + +Nginx/Tengine/OpenResty: +```bash +systemctl {start|stop|status|restart|reload} nginx +``` +MySQL/MariaDB/Percona: +```bash +systemctl {start|stop|restart|reload|status} mysqld +``` +PostgreSQL: +```bash +systemctl {start|stop|restart|status} postgresql +``` +MongoDB: +```bash +systemctl {start|stop|status|restart|reload} mongod +``` +PHP: +```bash +systemctl {start|stop|restart|reload|status} php-fpm +``` +Apache: +```bash +systemctl {start|restart|stop} httpd +``` +Tomcat: +```bash +systemctl {start|stop|status|restart} tomcat +``` +Pure-FTPd: +```bash +systemctl {start|stop|restart|status} pureftpd +``` +Redis: +```bash +systemctl {start|stop|status|restart|reload} redis-server +``` +Memcached: +```bash +systemctl {start|stop|status|restart|reload} memcached +``` + +## How to upgrade + +```bash +~/oneinstack/upgrade.sh +``` + +## How to uninstall + +```bash +~/oneinstack/uninstall.sh +``` + +## Installation + +For feedback, questions, and to follow the progress of the project:
+[Telegram Group](https://t.me/oneinstack)
+[OneinStack](https://oneinstack.com)
diff --git a/addons.sh b/addons.sh new file mode 100644 index 0000000..4649a08 --- /dev/null +++ b/addons.sh @@ -0,0 +1,185 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin +clear +printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# Install/Uninstall Extensions # +# For more information please visit https://oneinstack.com # +####################################################################### +" +# Check if user is root +# shellcheck disable=SC2046 +[ $(id -u) != '0' ] && { echo "${CFAILURE}Error: You must be root to run this script${CEND}"; exit 1; } + +oneinstack_dir=$(dirname "`readlink -f $0`") +# shellcheck disable=SC2164 +pushd ${oneinstack_dir} > /dev/null + +. ./versions.txt +. ./options.conf +. ./include/color.sh +. ./include/check_os.sh +. ./include/download.sh +. ./include/get_char.sh + +. ./include/composer.sh + +. ./include/fail2ban.sh + +. ./include/ngx_lua_waf.sh + +# get the out ip country +OUTIP_STATE=$(./include/ois.${ARCH} ip_state) + +# shellcheck disable=SC2154 +Show_Help() { + echo + echo "Usage: $0 command ... + --help, -h Show this help message + --install, -i Install + --uninstall, -u Uninstall + --composer Composer + --fail2ban Fail2ban + --ngx_lua_waf Ngx_lua_waf + " +} + +ARG_NUM=$# +TEMP=`getopt -o hiu --long help,install,uninstall,composer,fail2ban,ngx_lua_waf -- "$@" 2>/dev/null` +[ $? != 0 ] && echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 +eval set -- "${TEMP}" +while :; do + [ -z "$1" ] && break; + case "$1" in + -h|--help) + Show_Help; exit 0 + ;; + -i|--install) + install_flag=y; shift 1 + ;; + -u|--uninstall) + uninstall_flag=y; shift 1 + ;; + --composer) + composer_flag=y; shift 1 + ;; + --fail2ban) + fail2ban_flag=y; shift 1 + ;; + --ngx_lua_waf) + ngx_lua_waf_flag=y; shift 1 + ;; + --) + shift + ;; + *) + echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 + ;; + esac +done + +ACTION_FUN() { + while :; do + echo + echo "Please select an action:" + echo -e "\t${CMSG}1${CEND}. install" + echo -e "\t${CMSG}2${CEND}. uninstall" + read -e -p "Please input a number:(Default 1 press Enter) " ACTION + ACTION=${ACTION:-1} + if [[ ! "${ACTION}" =~ ^[1,2]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~2${CEND}" + else + [ "${ACTION}" == '1' ] && install_flag=y + [ "${ACTION}" == '2' ] && uninstall_flag=y + break + fi + done +} + +Menu() { + while :;do + printf " +What Are You Doing? +\t${CMSG}1${CEND}. Install/Uninstall PHP Composer +\t${CMSG}2${CEND}. Install/Uninstall fail2ban +\t${CMSG}3${CEND}. Install/Uninstall ngx_lua_waf +\t${CMSG}q${CEND}. Exit +" + read -e -p "Please input the correct option: " Number + if [[ ! "${Number}" =~ ^[1-3,q]$ ]]; then + echo "${CFAILURE}input error! Please only input 1~3 and q${CEND}" + else + case "${Number}" in + 1) + ACTION_FUN + if [ "${install_flag}" = 'y' ]; then + Install_composer + elif [ "${uninstall_flag}" = 'y' ]; then + Uninstall_composer + fi + ;; + 2) + ACTION_FUN + if [ "${install_flag}" = 'y' ]; then + Install_fail2ban + elif [ "${uninstall_flag}" = 'y' ]; then + Uninstall_fail2ban + fi + ;; + 3) + ACTION_FUN + if [ "${install_flag}" = 'y' ]; then + # shellcheck disable=SC2154 + [ -e "${nginx_install_dir}/sbin/nginx" ] && Nginx_lua_waf + # shellcheck disable=SC2154 + [ -e "${tengine_install_dir}/sbin/nginx" ] && Tengine_lua_waf + enable_lua_waf + elif [ "${uninstall_flag}" = 'y' ]; then + disable_lua_waf + fi + ;; + q) + exit + ;; + esac + fi + done +} + +if [ ${ARG_NUM} == 0 ]; then + Menu +else + if [ "${composer_flag}" == 'y' ]; then + if [ "${install_flag}" = 'y' ]; then + Install_composer + elif [ "${uninstall_flag}" = 'y' ]; then + Uninstall_composer + fi + fi + if [ "${fail2ban_flag}" == 'y' ]; then + if [ "${install_flag}" = 'y' ]; then + Install_fail2ban + elif [ "${uninstall_flag}" = 'y' ]; then + Uninstall_fail2ban + fi + fi + if [ "${ngx_lua_waf_flag}" == 'y' ]; then + if [ "${install_flag}" = 'y' ]; then + [ -e "${nginx_install_dir}/sbin/nginx" ] && Nginx_lua_waf + [ -e "${tengine_install_dir}/sbin/nginx" ] && Tengine_lua_waf + enable_lua_waf + elif [ "${uninstall_flag}" = 'y' ]; then + disable_lua_waf + fi + fi +fi diff --git a/backup.sh b/backup.sh new file mode 100644 index 0000000..526252d --- /dev/null +++ b/backup.sh @@ -0,0 +1,297 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin + +# Check if user is root +[ $(id -u) != "0" ] && { echo "${CFAILURE}Error: You must be root to run this script${CEND}"; exit 1; } + +oneinstack_dir=$(dirname "`readlink -f $0`") +pushd ${oneinstack_dir}/tools > /dev/null +. ../options.conf +[ ! -e "${backup_dir}" ] && mkdir -p ${backup_dir} + +DB_Local_BK() { + for D in `echo ${db_name} | tr ',' ' '` + do + ./db_bk.sh ${D} + done +} + +DB_Remote_BK() { + for D in `echo ${db_name} | tr ',' ' '` + do + ./db_bk.sh ${D} + DB_GREP="DB_${D}_`date +%Y%m%d`" + DB_FILE=`ls -lrt ${backup_dir} | grep ${DB_GREP} | tail -1 | awk '{print $NF}'` + echo "file:::${backup_dir}/${DB_FILE} ${backup_dir} push" >> config_backup.txt + echo "com:::[ -e "${backup_dir}/${DB_FILE}" ] && rm -rf ${backup_dir}/DB_${D}_$(date +%Y%m%d --date="${expired_days} days ago")_*.tgz" >> config_backup.txt + done +} + +DB_OSS_BK() { + for D in `echo ${db_name} | tr ',' ' '` + do + ./db_bk.sh ${D} + DB_GREP="DB_${D}_`date +%Y%m%d`" + DB_FILE=`ls -lrt ${backup_dir} | grep ${DB_GREP} | tail -1 | awk '{print $NF}'` + ossutil cp -f ${backup_dir}/${DB_FILE} oss://${oss_bucket}/`date +%F`/${DB_FILE} + if [ $? -eq 0 ]; then + ossutil rm -rf oss://${oss_bucket}/`date +%F --date="${expired_days} days ago"`/ + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${backup_dir}/${DB_FILE} + fi + done +} + +DB_COS_BK() { + for D in `echo ${db_name} | tr ',' ' '` + do + ./db_bk.sh ${D} + DB_GREP="DB_${D}_`date +%Y%m%d`" + DB_FILE=`ls -lrt ${backup_dir} | grep ${DB_GREP} | tail -1 | awk '{print $NF}'` + coscli sync ${backup_dir}/${DB_FILE} cos://${cos_bucket}/`date +%F`/${DB_FILE} + if [ $? -eq 0 ]; then + coscli rm -rf cos://${cos_bucket}/`date +%F --date="${expired_days} days ago"` > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${backup_dir}/${DB_FILE} + fi + done +} + +DB_UPYUN_BK() { + for D in `echo ${db_name} | tr ',' ' '` + do + ./db_bk.sh ${D} + DB_GREP="DB_${D}_`date +%Y%m%d`" + DB_FILE=`ls -lrt ${backup_dir} | grep ${DB_GREP} | tail -1 | awk '{print $NF}'` + upx put ${backup_dir}/${DB_FILE} /`date +%F`/${DB_FILE} + if [ $? -eq 0 ]; then + upx rm -a `date +%F --date="${expired_days} days ago"` > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${backup_dir}/${DB_FILE} + fi + done +} + +DB_QINIU_BK() { + for D in `echo ${db_name} | tr ',' ' '` + do + ./db_bk.sh ${D} + DB_GREP="DB_${D}_`date +%Y%m%d`" + DB_FILE=`ls -lrt ${backup_dir} | grep ${DB_GREP} | tail -1 | awk '{print $NF}'` + qshell rput ${qiniu_bucket} /`date +%F`/${DB_FILE} ${backup_dir}/${DB_FILE} + if [ $? -eq 0 ]; then + qshell listbucket ${qiniu_bucket} /`date +%F --date="${expired_days} days ago"` /tmp/qiniu.txt > /dev/null 2>&1 + qshell batchdelete -force ${qiniu_bucket} /tmp/qiniu.txt > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${backup_dir}/${DB_FILE} + rm -f /tmp/qiniu.txt + fi + done +} + +DB_S3_BK() { + for D in `echo ${db_name} | tr ',' ' '` + do + ./db_bk.sh ${D} + DB_GREP="DB_${D}_`date +%Y%m%d`" + DB_FILE=`ls -lrt ${backup_dir} | grep ${DB_GREP} | tail -1 | awk '{print $NF}'` + aws s3 sync ${backup_dir}/${DB_FILE} s3://${s3_bucket}/`date +%F`/${DB_FILE} + if [ $? -eq 0 ]; then + aws s3 rm -r s3://${s3_bucket}/`date +%F --date="${expired_days} days ago"` > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${backup_dir}/${DB_FILE} + fi + done +} + +DB_DROPBOX_BK() { + for D in `echo ${db_name} | tr ',' ' '` + do + ./db_bk.sh ${D} + DB_GREP="DB_${D}_`date +%Y%m%d`" + DB_FILE=`ls -lrt ${backup_dir} | grep ${DB_GREP} | tail -1 | awk '{print $NF}'` + dbxcli put ${backup_dir}/${DB_FILE} `date +%F`/${DB_FILE} + if [ $? -eq 0 ]; then + dbxcli rm -f `date +%F --date="${expired_days} days ago"` > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${backup_dir}/${DB_FILE} + fi + done +} + +WEB_LOCAL_BK() { + for W in `echo ${website_name} | tr ',' ' '` + do + ./website_bk.sh $W + done +} + +WEB_Remote_BK() { + for W in `echo ${website_name} | tr ',' ' '` + do + if [ `du -sm "${wwwroot_dir}/${WebSite}" | awk '{print $1}'` -lt 2048 ]; then + ./website_bk.sh $W + Web_GREP="Web_${W}_`date +%Y%m%d`" + Web_FILE=`ls -lrt ${backup_dir} | grep ${Web_GREP} | tail -1 | awk '{print $NF}'` + echo "file:::${backup_dir}/${Web_FILE} ${backup_dir} push" >> config_backup.txt + echo "com:::[ -e "${backup_dir}/${Web_FILE}" ] && rm -rf ${backup_dir}/Web_${W}_$(date +%Y%m%d --date="${expired_days} days ago")_*.tgz" >> config_backup.txt + else + echo "file:::${wwwroot_dir}/$W ${backup_dir} push" >> config_backup.txt + fi + done +} + +WEB_OSS_BK() { + for W in `echo $website_name | tr ',' ' '` + do + [ ! -e "${wwwroot_dir}/${WebSite}" ] && { echo "[${wwwroot_dir}/${WebSite}] not exist"; break; } + PUSH_FILE="${backup_dir}/Web_${W}_$(date +%Y%m%d_%H).tgz" + if [ ! -e "${PUSH_FILE}" ]; then + pushd ${wwwroot_dir} > /dev/null + tar czf ${PUSH_FILE} ./$W + popd > /dev/null + fi + ossutil cp -f ${PUSH_FILE} oss://${oss_bucket}/`date +%F`/${PUSH_FILE##*/} + if [ $? -eq 0 ]; then + ossutil rm -rf oss://${oss_bucket}/`date +%F --date="${expired_days} days ago"`/ + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${PUSH_FILE} + fi + done +} + +WEB_COS_BK() { + for W in `echo ${website_name} | tr ',' ' '` + do + [ ! -e "${wwwroot_dir}/${WebSite}" ] && { echo "[${wwwroot_dir}/${WebSite}] not exist"; break; } + PUSH_FILE="${backup_dir}/Web_${W}_$(date +%Y%m%d_%H).tgz" + if [ ! -e "${PUSH_FILE}" ]; then + pushd ${wwwroot_dir} > /dev/null + tar czf ${PUSH_FILE} ./$W + popd > /dev/null + fi + coscli sync ${PUSH_FILE} cos://${cos_bucket}/`date +%F`/${PUSH_FILE##*/} + if [ $? -eq 0 ]; then + coscli rm -rf cos://${cos_bucket}/`date +%F --date="${expired_days} days ago"` > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${PUSH_FILE} + fi + done +} + +WEB_UPYUN_BK() { + for W in `echo ${website_name} | tr ',' ' '` + do + [ ! -e "${wwwroot_dir}/${WebSite}" ] && { echo "[${wwwroot_dir}/${WebSite}] not exist"; break; } + [ ! -e "${backup_dir}" ] && mkdir -p ${backup_dir} + PUSH_FILE="${backup_dir}/Web_${W}_$(date +%Y%m%d_%H).tgz" + if [ ! -e "${PUSH_FILE}" ]; then + pushd ${wwwroot_dir} > /dev/null + tar czf ${PUSH_FILE} ./$W + popd > /dev/null + fi + upx put ${PUSH_FILE} /`date +%F`/${PUSH_FILE##*/} + if [ $? -eq 0 ]; then + upx rm -a `date +%F --date="${expired_days} days ago"` > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${PUSH_FILE} + fi + done +} + +WEB_QINIU_BK() { + for W in `echo ${website_name} | tr ',' ' '` + do + [ ! -e "${wwwroot_dir}/${WebSite}" ] && { echo "[${wwwroot_dir}/${WebSite}] not exist"; break; } + [ ! -e "${backup_dir}" ] && mkdir -p ${backup_dir} + PUSH_FILE="${backup_dir}/Web_${W}_$(date +%Y%m%d_%H).tgz" + if [ ! -e "${PUSH_FILE}" ]; then + pushd ${wwwroot_dir} > /dev/null + tar czf ${PUSH_FILE} ./$W + popd > /dev/null + fi + qshell rput ${qiniu_bucket} /`date +%F`/${PUSH_FILE##*/} ${PUSH_FILE} + if [ $? -eq 0 ]; then + qshell listbucket ${qiniu_bucket} /`date +%F --date="${expired_days} days ago"` /tmp/qiniu.txt > /dev/null 2>&1 + qshell batchdelete -force ${qiniu_bucket} /tmp/qiniu.txt > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${PUSH_FILE} + rm -f /tmp/qiniu.txt + fi + done +} + +WEB_S3_BK() { + for W in `echo ${website_name} | tr ',' ' '` + do + [ ! -e "${wwwroot_dir}/${WebSite}" ] && { echo "[${wwwroot_dir}/${WebSite}] not exist"; break; } + [ ! -e "${backup_dir}" ] && mkdir -p ${backup_dir} + PUSH_FILE="${backup_dir}/Web_${W}_$(date +%Y%m%d_%H).tgz" + if [ ! -e "${PUSH_FILE}" ]; then + pushd ${wwwroot_dir} > /dev/null + tar czf ${PUSH_FILE} ./$W + popd > /dev/null + fi + aws s3 sync ${PUSH_FILE} s3://${s3_bucket}/`date +%F`/${PUSH_FILE##*/} + if [ $? -eq 0 ]; then + aws s3 rm -r s3://${s3_bucket}/`date +%F --date="${expired_days} days ago"` > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${PUSH_FILE} + fi + done +} + +WEB_DROPBOX_BK() { + for W in `echo ${website_name} | tr ',' ' '` + do + [ ! -e "${wwwroot_dir}/${WebSite}" ] && { echo "[${wwwroot_dir}/${WebSite}] not exist"; break; } + [ ! -e "${backup_dir}" ] && mkdir -p ${backup_dir} + PUSH_FILE="${backup_dir}/Web_${W}_$(date +%Y%m%d_%H).tgz" + if [ ! -e "${PUSH_FILE}" ]; then + pushd ${wwwroot_dir} > /dev/null + tar czf ${PUSH_FILE} ./$W + popd > /dev/null + fi + dbxcli put ${PUSH_FILE} `date +%F`/${PUSH_FILE##*/} + if [ $? -eq 0 ]; then + dbxcli rm -f `date +%F --date="${expired_days} days ago"` > /dev/null 2>&1 + [ -z "`echo ${backup_destination} | grep -ow 'local'`" ] && rm -f ${PUSH_FILE} + fi + done +} + +for DEST in `echo ${backup_destination} | tr ',' ' '` +do + if [ "${DEST}" == 'local' ]; then + [ -n "`echo ${backup_content} | grep -ow db`" ] && DB_Local_BK + [ -n "`echo ${backup_content} | grep -ow web`" ] && WEB_LOCAL_BK + fi + if [ "${DEST}" == 'remote' ]; then + echo "com:::[ ! -e "${backup_dir}" ] && mkdir -p ${backup_dir}" > config_backup.txt + [ -n "`echo ${backup_content} | grep -ow db`" ] && DB_Remote_BK + [ -n "`echo ${backup_content} | grep -ow web`" ] && WEB_Remote_BK + ./mabs.sh -c config_backup.txt -T -1 | tee -a mabs.log + fi + if [ "${DEST}" == 'oss' ]; then + [ -n "`echo ${backup_content} | grep -ow db`" ] && DB_OSS_BK + [ -n "`echo ${backup_content} | grep -ow web`" ] && WEB_OSS_BK + fi + if [ "${DEST}" == 'cos' ]; then + [ -n "`echo ${backup_content} | grep -ow db`" ] && DB_COS_BK + [ -n "`echo ${backup_content} | grep -ow web`" ] && WEB_COS_BK + fi + if [ "${DEST}" == 'upyun' ]; then + [ -n "`echo ${backup_content} | grep -ow db`" ] && DB_UPYUN_BK + [ -n "`echo ${backup_content} | grep -ow web`" ] && WEB_UPYUN_BK + fi + if [ "${DEST}" == 'qiniu' ]; then + [ -n "`echo ${backup_content} | grep -ow db`" ] && DB_QINIU_BK + [ -n "`echo ${backup_content} | grep -ow web`" ] && WEB_QINIU_BK + fi + if [ "${DEST}" == 's3' ]; then + [ -n "`echo ${backup_content} | grep -ow db`" ] && DB_S3_BK + [ -n "`echo ${backup_content} | grep -ow web`" ] && WEB_S3_BK + fi + if [ "${DEST}" == 'dropbox' ]; then + [ -n "`echo ${backup_content} | grep -ow db`" ] && DB_DROPBOX_BK + [ -n "`echo ${backup_content} | grep -ow web`" ] && WEB_DROPBOX_BK + fi +done diff --git a/backup_setup.sh b/backup_setup.sh new file mode 100644 index 0000000..6b41016 --- /dev/null +++ b/backup_setup.sh @@ -0,0 +1,563 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin +clear +printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# Setup the backup parameters # +# For more information please visit https://oneinstack.com # +####################################################################### +" +# Check if user is root +[ $(id -u) != "0" ] && { echo "${CFAILURE}Error: You must be root to run this script${CEND}"; exit 1; } + +oneinstack_dir=$(dirname "`readlink -f $0`") +pushd ${oneinstack_dir} > /dev/null +. ./options.conf +. ./versions.txt +. ./include/color.sh +. ./include/check_os.sh +. ./include/check_dir.sh +. ./include/download.sh + +while :; do echo + echo 'Please select your backup destination:' + echo -e "\t${CMSG}1${CEND}. Localhost" + echo -e "\t${CMSG}2${CEND}. Remote host" + echo -e "\t${CMSG}3${CEND}. Aliyun OSS" + echo -e "\t${CMSG}4${CEND}. Qcloud COS" + echo -e "\t${CMSG}5${CEND}. UPYUN" + echo -e "\t${CMSG}6${CEND}. QINIU" + echo -e "\t${CMSG}7${CEND}. Amazon S3" + echo -e "\t${CMSG}8${CEND}. Dropbox" + read -e -p "Please input numbers:(Default 1 press Enter) " desc_bk + desc_bk=${desc_bk:-'1'} + array_desc=(${desc_bk}) + array_all=(1 2 3 4 5 6 7 8) + for v in ${array_desc[@]} + do + [ -z "`echo ${array_all[@]} | grep -w ${v}`" ] && desc_flag=1 + done + if [ "${desc_flag}" == '1' ]; then + unset desc_flag + echo; echo "${CWARNING}input error! Please only input number 1 3 4 and so on${CEND}"; echo + continue + else + sed -i 's@^backup_destination=.*@backup_destination=@' ./options.conf + break + fi +done + +[ -n "`echo ${desc_bk} | grep -w 1`" ] && sed -i 's@^backup_destination=.*@backup_destination=local@' ./options.conf +[ -n "`echo ${desc_bk} | grep -w 2`" ] && sed -i 's@^backup_destination=.*@&,remote@' ./options.conf +[ -n "`echo ${desc_bk} | grep -w 3`" ] && sed -i 's@^backup_destination=.*@&,oss@' ./options.conf +[ -n "`echo ${desc_bk} | grep -w 4`" ] && sed -i 's@^backup_destination=.*@&,cos@' ./options.conf +[ -n "`echo ${desc_bk} | grep -w 5`" ] && sed -i 's@^backup_destination=.*@&,upyun@' ./options.conf +[ -n "`echo ${desc_bk} | grep -w 6`" ] && sed -i 's@^backup_destination=.*@&,qiniu@' ./options.conf +[ -n "`echo ${desc_bk} | grep -w 7`" ] && sed -i 's@^backup_destination=.*@&,s3@' ./options.conf +[ -n "`echo ${desc_bk} | grep -w 8`" ] && sed -i 's@^backup_destination=.*@&,dropbox@' ./options.conf +sed -i 's@^backup_destination=,@backup_destination=@' ./options.conf + +while :; do echo + echo 'Please select your backup content:' + echo -e "\t${CMSG}1${CEND}. Only Database" + echo -e "\t${CMSG}2${CEND}. Only Website" + echo -e "\t${CMSG}3${CEND}. Database and Website" + read -e -p "Please input a number:(Default 1 press Enter) " content_bk + content_bk=${content_bk:-1} + if [[ ! ${content_bk} =~ ^[1-3]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~3${CEND}" + else + break + fi +done + +[ "${content_bk}" == '1' ] && sed -i 's@^backup_content=.*@backup_content=db@' ./options.conf +[ "${content_bk}" == '2' ] && sed -i 's@^backup_content=.*@backup_content=web@' ./options.conf +[ "${content_bk}" == '3' ] && sed -i 's@^backup_content=.*@backup_content=db,web@' ./options.conf + +if [ -n "`echo ${desc_bk} | grep -Ew '1|2'`" ]; then + while :; do echo + echo "Please enter the directory for save the backup file: " + read -e -p "(Default directory: ${backup_dir}): " new_backup_dir + new_backup_dir=${new_backup_dir:-${backup_dir}} + if [ -z "`echo ${new_backup_dir}| grep '^/'`" ]; then + echo "${CWARNING}input error! ${CEND}" + else + break + fi + done + sed -i "s@^backup_dir=.*@backup_dir=${new_backup_dir}@" ./options.conf +fi + +while :; do echo + echo "Please enter a valid backup number of days: " + read -e -p "(Default days: 5): " expired_days + expired_days=${expired_days:-5} + [ -n "`echo ${expired_days} | sed -n "/^[0-9]\+$/p"`" ] && break || echo "${CWARNING}input error! Please only enter numbers! ${CEND}" +done +sed -i "s@^expired_days=.*@expired_days=${expired_days}@" ./options.conf + +if [ "${content_bk}" != '2' ]; then + databases=`${db_install_dir}/bin/mysql -uroot -p$dbrootpwd -e "show databases\G" | grep Database | awk '{print $2}' | grep -Evw "(performance_schema|information_schema|mysql|sys)"` + while :; do echo + echo "Please enter one or more name for database, separate multiple database names with commas: " + read -e -p "(Default database: `echo $databases | tr ' ' ','`) " db_name + db_name=`echo ${db_name} | tr -d ' '` + [ -z "${db_name}" ] && db_name="`echo $databases | tr ' ' ','`" + D_tmp=0 + for D in `echo ${db_name} | tr ',' ' '` + do + [ -z "`echo $databases | grep -w $D`" ] && { echo "${CWARNING}$D was not exist! ${CEND}" ; D_tmp=1; } + done + [ "$D_tmp" != '1' ] && break + done + sed -i "s@^db_name=.*@db_name=${db_name}@" ./options.conf +fi + +if [ "${content_bk}" != '1' ]; then + websites=`ls ${wwwroot_dir}` + while :; do echo + echo "Please enter one or more name for website, separate multiple website names with commas: " + read -e -p "(Default website: `echo $websites | tr ' ' ','`) " website_name + website_name=`echo ${website_name} | tr -d ' '` + [ -z "${website_name}" ] && website_name="`echo $websites | tr ' ' ','`" + W_tmp=0 + for W in `echo ${website_name} | tr ',' ' '` + do + [ ! -e "${wwwroot_dir}/$W" ] && { echo "${CWARNING}${wwwroot_dir}/$W not exist! ${CEND}" ; W_tmp=1; } + done + [ "$W_tmp" != '1' ] && break + done + sed -i "s@^website_name=.*@website_name=${website_name}@" ./options.conf +fi + +echo +echo "You have to backup the content:" +[ "${content_bk}" != '2' ] && echo "Database: ${CMSG}${db_name}${CEND}" +[ "${content_bk}" != '1' ] && echo "Website: ${CMSG}${website_name}${CEND}" + +if [ -n "`echo ${desc_bk} | grep -w 2`" ]; then + > tools/iplist.txt + while :; do echo + read -e -p "Please enter the remote host address: " remote_address + [ -z "${remote_address}" -o "${remote_address}" == '127.0.0.1' ] && continue + echo + read -e -p "Please enter the remote host port(Default: 22) : " remote_port + remote_port=${remote_port:-22} + echo + read -e -p "Please enter the remote host user(Default: root) : " remote_user + remote_user=${remote_user:-root} + echo + read -e -p "Please enter the remote host password: " remote_password + IPcode=$(echo "ibase=16;$(echo "${remote_address}" | xxd -ps -u)"|bc|tr -d '\\'|tr -d '\n') + Portcode=$(echo "ibase=16;$(echo "${remote_port}" | xxd -ps -u)"|bc|tr -d '\\'|tr -d '\n') + PWcode=$(echo "ibase=16;$(echo "$remote_password" | xxd -ps -u)"|bc|tr -d '\\'|tr -d '\n') + [ -e "~/.ssh/known_hosts" ] && grep ${remote_address} ~/.ssh/known_hosts | sed -i "/${remote_address}/d" ~/.ssh/known_hosts + ./tools/mssh.exp ${IPcode}P ${remote_user} ${PWcode}P ${Portcode}P true 10 + if [ $? -eq 0 ]; then + [ -z "`grep ${remote_address} tools/iplist.txt`" ] && echo "${remote_address} ${remote_port} ${remote_user} $remote_password" >> tools/iplist.txt || echo "${CWARNING}${remote_address} has been added! ${CEND}" + while :; do + read -e -p "Do you want to add more host ? [y/n]: " morehost_flag + if [[ ! ${morehost_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + [ "${morehost_flag}" == 'n' ] && break + fi + done +fi + +if [ -n "`echo ${desc_bk} | grep -w 3`" ]; then + if [ ! -e "/usr/local/bin/ossutil" ]; then + if [ "${armplatform}" == 'y' ]; then + wget -qc https://gosspublic.alicdn.com/ossutil/1.7.16/ossutilarm64 -O /usr/local/bin/ossutil + else + wget -qc https://gosspublic.alicdn.com/ossutil/1.7.16/ossutil64 -O /usr/local/bin/ossutil + fi + chmod +x /usr/local/bin/ossutil + fi + while :; do echo + echo 'Please select your backup aliyun datacenter:' + echo -e "\t ${CMSG}1${CEND}. cn-hangzhou-华东1 (杭州) ${CMSG}2${CEND}. cn-shanghai-华东2 (上海)" + echo -e "\t ${CMSG}3${CEND}. cn-nanjing-华东5 (南京) ${CMSG}4${CEND}. cn-fuzhou-华东6 (福州)" + echo -e "\t ${CMSG}5${CEND}. cn-qingdao-华北1 (青岛) ${CMSG}6${CEND}. cn-beijing-华北2 (北京)" + echo -e "\t ${CMSG}7${CEND}. cn-zhangjiakou-华北3 (张家口) ${CMSG}8${CEND}. cn-huhehaote-华北5 (呼和浩特)" + echo -e "\t ${CMSG}9${CEND}. cn-wulanchabu-华北6 (乌兰察布) ${CMSG}10${CEND}. cn-shenzhen-华南1 (深圳)" + echo -e "\t${CMSG}11${CEND}. cn-heyuan-华南2 (河源) ${CMSG}12${CEND}. cn-guangzhou-华南3 (广州)" + echo -e "\t${CMSG}13${CEND}. cn-chengdu-西南1 (成都) ${CMSG}14${CEND}. cn-hongkong-香港" + echo -e "\t${CMSG}15${CEND}. us-west-1-美国 (硅谷) ${CMSG}16${CEND}. us-east-1-美国 (弗吉尼亚)" + echo -e "\t${CMSG}17${CEND}. ap-northeast-1-日本 (东京) ${CMSG}18${CEND}. ap-northeast-2-韩国 (首尔)" + echo -e "\t${CMSG}19${CEND}. ap-southeast-1-新加坡 ${CMSG}20${CEND}. ap-southeast-2-澳大利亚 (悉尼)" + echo -e "\t${CMSG}21${CEND}. ap-southeast-3-马来西亚 (吉隆坡) ${CMSG}22${CEND}. ap-southeast-5-印度尼西亚 (雅加达)" + echo -e "\t${CMSG}23${CEND}. ap-southeast-6-菲律宾 (马尼拉) ${CMSG}24${CEND}. ap-southeast-7-泰国 (曼谷)" + echo -e "\t${CMSG}25${CEND}. ap-south-1-印度 (孟买) ${CMSG}26${CEND}. eu-central-1-德国 (法兰克福)" + echo -e "\t${CMSG}27${CEND}. eu-west-1-英国 (伦敦) ${CMSG}28${CEND}. me-east-1-阿联酋 (迪拜)" + read -e -p "Please input a number:(Default 1 press Enter) " Location + Location=${Location:-1} + if [[ "${Location}" =~ ^[1-9]$|^1[0-9]$|^2[0-8]$ ]]; then + break + else + echo "${CWARNING}input error! Please only input number 1~28${CEND}" + fi + done + [ "${Location}" == '1' ] && Host=oss-cn-hangzhou-internal.aliyuncs.com + [ "${Location}" == '2' ] && Host=oss-cn-shanghai-internal.aliyuncs.com + [ "${Location}" == '3' ] && Host=oss-cn-nanjing-internal.aliyuncs.com + [ "${Location}" == '4' ] && Host=oss-cn-fuzhou-internal.aliyuncs.com + [ "${Location}" == '5' ] && Host=oss-cn-qingdao-internal.aliyuncs.com + [ "${Location}" == '6' ] && Host=oss-cn-beijing-internal.aliyuncs.com + [ "${Location}" == '7' ] && Host=oss-cn-zhangjiakou-internal.aliyuncs.com + [ "${Location}" == '8' ] && Host=oss-cn-huhehaote-internal.aliyuncs.com + [ "${Location}" == '9' ] && Host=oss-cn-wulanchabu-internal.aliyuncs.com + [ "${Location}" == '10' ] && Host=oss-cn-shenzhen-internal.aliyuncs.com + [ "${Location}" == '11' ] && Host=oss-cn-heyuan-internal.aliyuncs.com + [ "${Location}" == '12' ] && Host=oss-cn-guangzhou-internal.aliyuncs.com + [ "${Location}" == '13' ] && Host=oss-cn-chengdu-internal.aliyuncs.com + [ "${Location}" == '14' ] && Host=oss-cn-hongkong-internal.aliyuncs.com + [ "${Location}" == '15' ] && Host=oss-us-west-1-internal.aliyuncs.com + [ "${Location}" == '16' ] && Host=oss-us-east-1-internal.aliyuncs.com + [ "${Location}" == '17' ] && Host=oss-ap-northeast-1-internal.aliyuncs.com + [ "${Location}" == '18' ] && Host=oss-ap-northeast-2-internal.aliyuncs.com + [ "${Location}" == '19' ] && Host=oss-ap-southeast-1-internal.aliyuncs.com + [ "${Location}" == '20' ] && Host=oss-ap-southeast-2-internal.aliyuncs.com + [ "${Location}" == '21' ] && Host=oss-ap-southeast-3-internal.aliyuncs.com + [ "${Location}" == '22' ] && Host=oss-ap-southeast-5-internal.aliyuncs.com + [ "${Location}" == '23' ] && Host=oss-ap-southeast-6-internal.aliyuncs.com + [ "${Location}" == '24' ] && Host=oss-ap-southeast-7-internal.aliyuncs.com + [ "${Location}" == '25' ] && Host=oss-ap-south-1-internal.aliyuncs.com + [ "${Location}" == '26' ] && Host=oss-eu-central-1-internal.aliyuncs.com + [ "${Location}" == '27' ] && Host=oss-eu-west-1-internal.aliyuncs.com + [ "${Location}" == '28' ] && Host=oss-me-east-1-internal.aliyuncs.com + [ "$(./include/ois.${ARCH} conn_port --host ${Host} --port 80)" == "false" ] && Host=`echo ${Host} | sed 's@-internal@@g'` + [ -e "/root/.ossutilconfig" ] && rm -f /root/.ossutilconfig + while :; do echo + read -e -p "Please enter the aliyun oss Access Key ID: " KeyID + [ -z "${KeyID}" ] && continue + echo + read -e -p "Please enter the aliyun oss Access Key Secret: " KeySecret + [ -z "${KeySecret}" ] && continue + ossutil ls -e ${Host} -i ${KeyID} -k ${KeySecret} > /dev/null 2>&1 + if [ $? -eq 0 ]; then + ossutil config -e ${Host} -i ${KeyID} -k ${KeySecret} > /dev/null 2>&1 + while :; do echo + read -e -p "Please enter the aliyun oss bucket: " OSS_BUCKET + ossutil mb oss://${OSS_BUCKET} > /dev/null 2>&1 + if [ $? -eq 0 ]; then + echo "${CMSG}Bucket oss://${OSS_BUCKET}/ created${CEND}" + sed -i "s@^oss_bucket=.*@oss_bucket=${OSS_BUCKET}@" ./options.conf + break + else + echo "${CWARNING}[${OSS_BUCKET}] already exists, You need to use the OSS Console to create a bucket for storing.${CEND}" + fi + done + break + fi + done +fi + +if [ -n "`echo ${desc_bk} | grep -w 4`" ]; then + if [ ! -e "/usr/local/bin/coscli" ]; then + wget -qc https://cosbrowser.cloud.tencent.com/software/coscli/coscli-linux -O /usr/local/bin/coscli + chmod +x /usr/local/bin/coscli + fi + + while :; do echo + echo 'Please select your backup qcloud datacenter:' + echo -e "\t ${CMSG} 1${CEND}. ap-beijing-北京 ${CMSG}2${CEND}. ap-nanjing-南京" + echo -e "\t ${CMSG} 3${CEND}. ap-shanghai-上海 ${CMSG}4${CEND}. ap-guangzhou-广州" + echo -e "\t ${CMSG} 5${CEND}. ap-chengdu-成都 ${CMSG}6${CEND}. ap-chongqing-重庆" + echo -e "\t ${CMSG} 7${CEND}. ap-shenzhen-fsi-深圳金融 ${CMSG}8${CEND}. ap-shanghai-fsi-上海金融" + echo -e "\t ${CMSG} 9${CEND}. ap-beijing-fsi-北京金融 ${CMSG}10${CEND}. ap-hongkong-香港" + echo -e "\t ${CMSG}11${CEND}. ap-singapore-新加坡 ${CMSG}12${CEND}. ap-mumbai-孟买" + echo -e "\t ${CMSG}13${CEND}. ap-jakarta-雅加达 ${CMSG}14${CEND}. ap-seoul-首尔" + echo -e "\t ${CMSG}15${CEND}. ap-bangkok-曼谷 ${CMSG}16${CEND}. ap-tokyo-东京" + echo -e "\t ${CMSG}17${CEND}. na-siliconvalley-硅谷 ${CMSG}18${CEND}. na-ashburn-弗吉尼亚" + echo -e "\t ${CMSG}19${CEND}. na-toronto-多伦多 ${CMSG}20${CEND}. sa-saopaulo-圣保罗" + echo -e "\t ${CMSG}21${CEND}. eu-frankfurt-法兰克福" + read -e -p "Please input a number:(Default 1 press Enter) " Location + Location=${Location:-1} + if [[ "${Location}" =~ ^[1-9]$|^1[0-9]$|^2[0-1]$ ]]; then + break + else + echo "${CWARNING}input error! Please only input number 1~21${CEND}" + fi + done + [ "${Location}" == '1' ] && REGION='ap-beijing' + [ "${Location}" == '2' ] && REGION='ap-nanjing' + [ "${Location}" == '3' ] && REGION='ap-shanghai' + [ "${Location}" == '4' ] && REGION='ap-guangzhou' + [ "${Location}" == '5' ] && REGION='ap-chengdu' + [ "${Location}" == '6' ] && REGION='ap-chongqing' + [ "${Location}" == '7' ] && REGION='ap-shenzhen-fsi' + [ "${Location}" == '8' ] && REGION='ap-shanghai-fsi' + [ "${Location}" == '9' ] && REGION='ap-beijing-fsi' + [ "${Location}" == '10' ] && REGION='ap-hongkong' + [ "${Location}" == '11' ] && REGION='ap-singapore' + [ "${Location}" == '12' ] && REGION='ap-mumbai' + [ "${Location}" == '13' ] && REGION='ap-jakarta' + [ "${Location}" == '14' ] && REGION='ap-seoul' + [ "${Location}" == '15' ] && REGION='ap-bangkok' + [ "${Location}" == '16' ] && REGION='ap-tokyo' + [ "${Location}" == '17' ] && REGION='na-siliconvalley' + [ "${Location}" == '18' ] && REGION='na-ashburn' + [ "${Location}" == '19' ] && REGION='na-toronto' + [ "${Location}" == '20' ] && REGION='sa-saopaulo' + [ "${Location}" == '21' ] && REGION='eu-frankfurt' + while :; do echo + read -e -p "Please enter the Qcloud COS SECRET_ID: " SECRET_ID + [ -z "${SECRET_ID}" ] && continue + echo + read -e -p "Please enter the Qcloud COS SECRET_KEY: " SECRET_KEY + [ -z "${SECRET_KEY}" ] && continue + echo + read -e -p "Please enter the Qcloud COS BUCKET: " COS_BUCKET + [ -z "${COS_BUCKET}" ] && continue + cat > ~/.cos.yaml << EOF +cos: + base: + secretid: ${SECRET_ID} + secretkey: ${SECRET_KEY} + protocol: https + buckets: + - name: ${COS_BUCKET} + endpoint: cos.${REGION}.myqcloud.com +EOF + coscli ls cos://${COS_BUCKET} > /dev/null 2>&1 + if [ $? -eq 0 ]; then + echo "${CMSG}SECRET_ID/SECRET_KEY/REGION/BUCKET OK${CEND}" + sed -i "s@^cos_bucket=.*@cos_bucket=${COS_BUCKET}@" ./options.conf + echo + break + else + coscli mb cos://${COS_BUCKET} -e cos.${REGION}.myqcloud.com > /dev/null 2>&1 + if [ $? -eq 0 ]; then + echo "${CMSG}Bucket ${COS_BUCKET} created${CEND}" + sed -i "s@^cos_bucket=.*@cos_bucket=${COS_BUCKET}@" ./options.conf + echo + break + else + echo "${CWARNING}input error! SECRET_ID/SECRET_KEY/REGION/BUCKET invalid${CEND}" + continue + fi + fi + done +fi + +if [ -n "`echo ${desc_bk} | grep -w 5`" ]; then + if [ ! -e "/usr/local/bin/upx" ]; then + if [ "${armplatform}" == 'y' ]; then + wget -qc http://collection.b0.upaiyun.com/softwares/upx/upx_0.4.3_linux_arm64.tar.gz -O /tmp/upx_0.4.3_linux_arm64.tar.gz + tar xzf /tmp/upx_0.4.3_linux_arm64.tar.gz -C /tmp/ + else + wget -qc http://collection.b0.upaiyun.com/softwares/upx/upx_0.4.3_linux_x86_64.tar.gz -O /tmp/upx_0.4.3_linux_x86_64.tar.gz + tar xzf /tmp/upx_0.4.3_linux_x86_64.tar.gz -C /tmp/ + fi + /bin/mv /tmp/upx /usr/local/bin/upx + chmod +x /usr/local/bin/upx + rm -f /tmp/{upx_*,LICENSE,README.md} + fi + while :; do echo + read -e -p "Please enter the upyun ServiceName: " ServiceName + [ -z "${ServiceName}" ] && continue + echo + read -e -p "Please enter the upyun Operator: " Operator + [ -z "${Operator}" ] && continue + echo + read -e -p "Please enter the upyun Password: " Password + [ -z "${Password}" ] && continue + echo + upx login ${ServiceName} ${Operator} ${Password} > /dev/null 2>&1 + if [ $? = 0 ]; then + echo "${CMSG}ServiceName/Operator/Password OK${CEND}" + echo + break + else + echo "${CWARNING}input error! ServiceName/Operator/Password invalid${CEND}" + fi + done +fi + +if [ -n "`echo ${desc_bk} | grep -w 6`" ]; then + if [ ! -e "/usr/local/bin/qshell" ]; then + if [ "${armplatform}" == 'y' ]; then + wget -qc https://devtools.qiniu.com/qshell-v2.12.0-linux-arm64.tar.gz -O /tmp/qshell-v2.12.0-linux-arm64.tar.gz + tar xzf /tmp/qshell-v2.12.0-linux-arm64.tar.gz -C /usr/local/bin/ + else + wget -qc https://devtools.qiniu.com/qshell-v2.12.0-linux-amd64.tar.gz -O /tmp/qshell-v2.12.0-linux-amd64.tar.gz + tar xzf /tmp/qshell-v2.12.0-linux-amd64.tar.gz -C /usr/local/bin/ + fi + chmod +x /usr/local/bin/qshell + rm -f /tmp/qshell* + fi + while :; do echo + echo 'Please select your backup qiniu datacenter:' + echo -e "\t ${CMSG} 1${CEND}. 华东 ${CMSG}2${CEND}. 华北" + echo -e "\t ${CMSG} 3${CEND}. 华南 ${CMSG}4${CEND}. 北美" + echo -e "\t ${CMSG} 5${CEND}. 东南亚 ${CMSG}6${CEND}. 华东-浙江2" + read -e -p "Please input a number:(Default 1 press Enter) " Location + Location=${Location:-1} + if [[ "${Location}" =~ ^[1-6]$ ]]; then + break + else + echo "${CWARNING}input error! Please only input number 1~6${CEND}" + fi + done + [ "${Location}" == '1' ] && zone='z0' + [ "${Location}" == '2' ] && zone='z1' + [ "${Location}" == '3' ] && zone='z2' + [ "${Location}" == '4' ] && zone='na0' + [ "${Location}" == '5' ] && zone='as0' + [ "${Location}" == '6' ] && zone='cn-east-2' + while :; do echo + read -e -p "Please enter the qiniu AccessKey: " AccessKey + [ -z "${AccessKey}" ] && continue + echo + read -e -p "Please enter the qiniu SecretKey: " SecretKey + [ -z "${SecretKey}" ] && continue + echo + read -e -p "Please enter the qiniu bucket: " QINIU_BUCKET + [ -z "${QINIU_BUCKET}" ] && continue + echo + qshell account ${AccessKey} ${SecretKey} backup + if qshell buckets | grep -w ${QINIU_BUCKET} > /dev/null 2>&1; then + sed -i "s@^qiniu_bucket=.*@qiniu_bucket=${QINIU_BUCKET}@" ./options.conf + echo "${CMSG}AccessKey/SecretKey/Bucket OK${CEND}" + echo + break + else + echo "${CWARNING}input error! AccessKey/SecretKey/Bucket invalid${CEND}" + fi + done +fi + +if [ -n "`echo ${desc_bk} | grep -w 7`" ]; then + if [ ! -e "/usr/local/bin/aws" ] && [ ! -e "/usr/bin/aws" ]; then + wget -qc https://awscli.amazonaws.com/awscli-exe-linux-$(arch).zip -O /tmp/awscliv2.zip + unzip /tmp/awscliv2.zip -d /tmp/ + /tmp/aws/install + rm -rf /tmp/{awscliv2.zip,aws} + fi + while :; do echo + echo 'Please select your backup amazon datacenter:' + echo -e "\t ${CMSG} 1${CEND}. us-east-2 ${CMSG} 2${CEND}. us-east-1" + echo -e "\t ${CMSG} 3${CEND}. us-west-1 ${CMSG} 4${CEND}. us-west-2" + echo -e "\t ${CMSG} 5${CEND}. af-south-1 ${CMSG} 6${CEND}. ap-east-1" + echo -e "\t ${CMSG} 7${CEND}. ap-south-2 ${CMSG} 8${CEND}. ap-southeast-3" + echo -e "\t ${CMSG} 9${CEND}. ap-southeast-4 ${CMSG}10${CEND}. ap-south-1" + echo -e "\t ${CMSG}11${CEND}. ap-northeast-3 ${CMSG}12${CEND}. ap-northeast-2" + echo -e "\t ${CMSG}13${CEND}. ap-southeast-1 ${CMSG}14${CEND}. ap-southeast-2" + echo -e "\t ${CMSG}15${CEND}. ap-northeast-1 ${CMSG}16${CEND}. ca-central-1" + echo -e "\t ${CMSG}17${CEND}. eu-central-1 ${CMSG}18${CEND}. eu-west-1" + echo -e "\t ${CMSG}19${CEND}. eu-west-2 ${CMSG}20${CEND}. eu-south-1" + echo -e "\t ${CMSG}21${CEND}. eu-west-3 ${CMSG}22${CEND}. eu-south-2" + echo -e "\t ${CMSG}23${CEND}. eu-north-1 ${CMSG}24${CEND}. eu-central-2" + echo -e "\t ${CMSG}25${CEND}. me-south-1 ${CMSG}26${CEND}. me-central-1" + echo -e "\t ${CMSG}27${CEND}. sa-east-1 ${CMSG}28${CEND}. us-gov-east-1" + echo -e "\t ${CMSG}29${CEND}. us-gov-west-1 ${CMSG}30${CEND}. cn-north-1" + echo -e "\t ${CMSG}31${CEND}. cn-northwest-1" + read -e -p "Please input a number:(Default 1 press Enter) " Location + Location=${Location:-1} + if [[ "${Location}" =~ ^[1-9]$|^[1-2][0-9]$|^3[0-1]$ ]]; then + break + else + echo "${CWARNING}input error! Please only input number 1~31${CEND}" + fi + done + [ "${Location}" == '1' ] && REGION='us-east-2' + [ "${Location}" == '2' ] && REGION='us-east-1' + [ "${Location}" == '3' ] && REGION='us-west-1' + [ "${Location}" == '4' ] && REGION='us-west-2' + [ "${Location}" == '5' ] && REGION='af-south-1' + [ "${Location}" == '6' ] && REGION='ap-east-1' + [ "${Location}" == '7' ] && REGION='ap-south-2' + [ "${Location}" == '8' ] && REGION='ap-southeast-3' + [ "${Location}" == '9' ] && REGION='ap-southeast-4' + [ "${Location}" == '10' ] && REGION='ap-south-1' + [ "${Location}" == '11' ] && REGION='ap-northeast-3' + [ "${Location}" == '12' ] && REGION='ap-northeast-2' + [ "${Location}" == '13' ] && REGION='ap-southeast-1' + [ "${Location}" == '14' ] && REGION='ap-southeast-2' + [ "${Location}" == '15' ] && REGION='ap-northeast-1' + [ "${Location}" == '16' ] && REGION='ca-central-1' + [ "${Location}" == '17' ] && REGION='eu-central-1' + [ "${Location}" == '18' ] && REGION='eu-west-1' + [ "${Location}" == '19' ] && REGION='eu-west-2' + [ "${Location}" == '20' ] && REGION='eu-south-1' + [ "${Location}" == '21' ] && REGION='eu-west-3' + [ "${Location}" == '22' ] && REGION='eu-south-2' + [ "${Location}" == '23' ] && REGION='eu-north-1' + [ "${Location}" == '24' ] && REGION='eu-central-2' + [ "${Location}" == '25' ] && REGION='me-south-1' + [ "${Location}" == '26' ] && REGION='me-central-1' + [ "${Location}" == '27' ] && REGION='sa-east-1' + [ "${Location}" == '28' ] && REGION='us-gov-east-1' + [ "${Location}" == '29' ] && REGION='us-gov-west-1' + [ "${Location}" == '30' ] && REGION='cn-north-1' + [ "${Location}" == '31' ] && REGION='cn-northwest-1' + while :; do echo + read -e -p "Please enter the AWS Access Key: " ACCESS_KEY + [ -z "${ACCESS_KEY}" ] && continue + echo + read -e -p "Please enter the AWS Access Key: " SECRET_KEY + [ -z "${SECRET_KEY}" ] && continue + aws configure set aws_access_key_id ${ACCESS_KEY} + aws configure set aws_secret_access_key ${SECRET_KEY} + aws configure set region ${REGION} + aws sts get-caller-identity > /dev/null 2>&1 + if [ $? -eq 0 ]; then + echo "${CMSG}ACCESS_KEY/SECRET_KEY OK${CEND}" + while :; do echo + read -e -p "Please enter the Amazon S3 bucket: " S3_BUCKET + [ -z "${S3_BUCKET}" ] && continue + aws s3 ls s3://${S3_BUCKET} > /dev/null 2>&1 + if [ $? -eq 0 ]; then + echo "${CMSG}Bucket s3://${S3_BUCKET}/ existed${CEND}" + sed -i "s@^s3_bucket=.*@s3_bucket=${S3_BUCKET}@" ./options.conf + break + else + aws s3 mb s3://${S3_BUCKET} > /dev/null 2>&1 + if [ $? -eq 0 ]; then + echo "${CMSG}Bucket s3://${S3_BUCKET}/ created${CEND}" + sed -i "s@^s3_bucket=.*@s3_bucket=${S3_BUCKET}@" ./options.conf + break + else + echo "${CWARNING}The requested bucket name is not available. The bucket namespace is shared by all users of the system. Please select a different name and try again.${CEND}" + continue + fi + fi + done + break + else + echo "${CWARNING}input error! ACCESS_KEY/SECRET_KEY invalid${CEND}" + continue + fi + done +fi + +if [ -n "`echo ${desc_bk} | grep -w 8`" ]; then + if [ ! -e "/usr/local/bin/dbxcli" ]; then + if [ "${armplatform}" == 'y' ]; then + wget -qc ${mirror_link}/oneinstack/src/dbxcli-linux-arm -O /usr/local/bin/dbxcli + else + wget -qc ${mirror_link}/oneinstack/src/dbxcli-linux-amd64 -O /usr/local/bin/dbxcli + fi + chmod +x /usr/local/bin/dbxcli + fi + while :; do echo + if dbxcli account; then + break + fi + done +fi diff --git a/config/Caddyfile b/config/Caddyfile new file mode 100644 index 0000000..d59ef97 --- /dev/null +++ b/config/Caddyfile @@ -0,0 +1,26 @@ +# The Caddyfile is an easy way to configure your Caddy web server. +# +# Unless the file starts with a global options block, the first +# uncommented line is always the address of your site. +# +# To use your own domain name (with automatic HTTPS), first make +# sure your domain's A/AAAA DNS records are properly pointed to +# this machine's public IP, then replace ":80" below with your +# domain name. + +:80 { + # Set this path to your site's directory. + root * /data/wwwroot/default + + # Enable the static file server. + file_server + + # Another common task is to set up a reverse proxy: + # reverse_proxy localhost:8080 + + # Or serve a PHP site through php-fpm: + # php_fastcgi localhost:9000 +} + +# Refer to the Caddy docs for more information: +# https://caddyserver.com/docs/caddyfile diff --git a/config/cloudflare.conf b/config/cloudflare.conf new file mode 100644 index 0000000..ac462ea --- /dev/null +++ b/config/cloudflare.conf @@ -0,0 +1,25 @@ +set_real_ip_from 103.21.244.0/22; +set_real_ip_from 103.22.200.0/22; +set_real_ip_from 103.31.4.0/22; +set_real_ip_from 104.16.0.0/12; +set_real_ip_from 108.162.192.0/18; +set_real_ip_from 131.0.72.0/22; +set_real_ip_from 141.101.64.0/18; +set_real_ip_from 162.158.0.0/15; +set_real_ip_from 172.64.0.0/13; +set_real_ip_from 173.245.48.0/20; +set_real_ip_from 188.114.96.0/20; +set_real_ip_from 190.93.240.0/20; +set_real_ip_from 197.234.240.0/22; +set_real_ip_from 198.41.128.0/17; +set_real_ip_from 2400:cb00::/32; +set_real_ip_from 2606:4700::/32; +set_real_ip_from 2803:f800::/32; +set_real_ip_from 2405:b500::/32; +set_real_ip_from 2405:8100::/32; +set_real_ip_from 2c0f:f248::/32; +set_real_ip_from 2a06:98c0::/29; + +# use any of the following two +real_ip_header CF-Connecting-IP; +#real_ip_header X-Forwarded-For; diff --git a/config/codeigniter.conf b/config/codeigniter.conf new file mode 100644 index 0000000..ac112d4 --- /dev/null +++ b/config/codeigniter.conf @@ -0,0 +1,3 @@ +location / { + try_files $uri $uri/ /index.php?/$request_uri; +} diff --git a/config/discuz.conf b/config/discuz.conf new file mode 100644 index 0000000..d3166e9 --- /dev/null +++ b/config/discuz.conf @@ -0,0 +1,12 @@ +rewrite ^([^\.]*)/topic-(.+)\.html$ $1/portal.php?mod=topic&topic=$2 last; +rewrite ^([^\.]*)/article-([0-9]+)-([0-9]+)\.html$ $1/portal.php?mod=view&aid=$2&page=$3 last; +rewrite ^([^\.]*)/forum-(\w+)-([0-9]+)\.html$ $1/forum.php?mod=forumdisplay&fid=$2&page=$3 last; +rewrite ^([^\.]*)/thread-([0-9]+)-([0-9]+)-([0-9]+)\.html$ $1/forum.php?mod=viewthread&tid=$2&extra=page%3D$4&page=$3 last; +rewrite ^([^\.]*)/group-([0-9]+)-([0-9]+)\.html$ $1/forum.php?mod=group&fid=$2&page=$3 last; +rewrite ^([^\.]*)/space-(username|uid)-(.+)\.html$ $1/home.php?mod=space&$2=$3 last; +rewrite ^([^\.]*)/blog-([0-9]+)-([0-9]+)\.html$ $1/home.php?mod=space&uid=$2&do=blog&id=$3 last; +rewrite ^([^\.]*)/(fid|tid)-([0-9]+)\.html$ $1/index.php?action=$2&value=$3 last; +rewrite ^([^\.]*)/([a-z]+[a-z0-9_]*)-([a-z0-9_\-]+)\.html$ $1/plugin.php?id=$2:$3 last; +#if (!-e $request_filename) { +# return 404; +#} diff --git a/config/drupal.conf b/config/drupal.conf new file mode 100644 index 0000000..a4de4e9 --- /dev/null +++ b/config/drupal.conf @@ -0,0 +1,4 @@ +if (!-e $request_filename) { + rewrite ^/update.php(.*)$ /update.php?q=$1 last; + rewrite ^/(.*)$ /index.php?q=$1 last; +} diff --git a/config/ecshop.conf b/config/ecshop.conf new file mode 100644 index 0000000..25bc858 --- /dev/null +++ b/config/ecshop.conf @@ -0,0 +1,31 @@ +if (!-e $request_filename) { + rewrite "^/index\.html" /index.php last; + rewrite "^/category$" /index.php last; + rewrite "^/feed-c([0-9]+)\.xml$" /feed.php?cat=$1 last; + rewrite "^/feed-b([0-9]+)\.xml$" /feed.php?brand=$1 last; + rewrite "^/feed\.xml$" /feed.php last; + rewrite "^/category-([0-9]+)-b([0-9]+)-min([0-9]+)-max([0-9]+)-attr([^-]*)-([0-9]+)-(.+)-([a-zA-Z]+)(.*)\.html$" /category.php?id=$1&brand=$2&price_min=$3&price_max=$4&filter_attr=$5&page=$6&sort=$7&order=$8 last; + rewrite "^/category-([0-9]+)-b([0-9]+)-min([0-9]+)-max([0-9]+)-attr([^-]*)(.*)\.html$" /category.php?id=$1&brand=$2&price_min=$3&price_max=$4&filter_attr=$5 last; + rewrite "^/category-([0-9]+)-b([0-9]+)-([0-9]+)-(.+)-([a-zA-Z]+)(.*)\.html$" /category.php?id=$1&brand=$2&page=$3&sort=$4&order=$5 last; + rewrite "^/category-([0-9]+)-b([0-9]+)-([0-9]+)(.*)\.html$" /category.php?id=$1&brand=$2&page=$3 last; + rewrite "^/category-([0-9]+)-b([0-9]+)(.*)\.html$" /category.php?id=$1&brand=$2 last; + rewrite "^/category-([0-9]+)(.*)\.html$" /category.php?id=$1 last; + rewrite "^/goods-([0-9]+)(.*)\.html" /goods.php?id=$1 last; + rewrite "^/article_cat-([0-9]+)-([0-9]+)-(.+)-([a-zA-Z]+)(.*)\.html$" /article_cat.php?id=$1&page=$2&sort=$3&order=$4 last; + rewrite "^/article_cat-([0-9]+)-([0-9]+)(.*)\.html$" /article_cat.php?id=$1&page=$2 last; + rewrite "^/article_cat-([0-9]+)(.*)\.html$" /article_cat.php?id=$1 last; + rewrite "^/article-([0-9]+)(.*)\.html$" /article.php?id=$1 last; + rewrite "^/brand-([0-9]+)-c([0-9]+)-([0-9]+)-(.+)-([a-zA-Z]+)\.html" /brand.php?id=$1&cat=$2&page=$3&sort=$4&order=$5 last; + rewrite "^/brand-([0-9]+)-c([0-9]+)-([0-9]+)(.*)\.html" /brand.php?id=$1&cat=$2&page=$3 last; + rewrite "^/brand-([0-9]+)-c([0-9]+)(.*)\.html" /brand.php?id=$1&cat=$2 last; + rewrite "^/brand-([0-9]+)(.*)\.html" /brand.php?id=$1 last; + rewrite "^/tag-(.*)\.html" /search.php?keywords=$1 last; + rewrite "^/snatch-([0-9]+)\.html$" /snatch.php?id=$1 last; + rewrite "^/group_buy-([0-9]+)\.html$" /group_buy.php?act=view&id=$1 last; + rewrite "^/auction-([0-9]+)\.html$" /auction.php?act=view&id=$1 last; + rewrite "^/exchange-id([0-9]+)(.*)\.html$" /exchange.php?id=$1&act=view last; + rewrite "^/exchange-([0-9]+)-min([0-9]+)-max([0-9]+)-([0-9]+)-(.+)-([a-zA-Z]+)(.*)\.html$" /exchange.php?cat_id=$1&integral_min=$2&integral_max=$3&page=$4&sort=$5&order=$6 last; + rewrite "^/exchange-([0-9]+)-([0-9]+)-(.+)-([a-zA-Z]+)(.*)\.html$" /exchange.php?cat_id=$1&page=$2&sort=$3&order=$4 last; + rewrite "^/exchange-([0-9]+)-([0-9]+)(.*)\.html$" /exchange.php?cat_id=$1&page=$2 last; + rewrite "^/exchange-([0-9]+)(.*)\.html$" /exchange.php?cat_id=$1 last; +} diff --git a/config/index.html b/config/index.html new file mode 100644 index 0000000..f4787a2 --- /dev/null +++ b/config/index.html @@ -0,0 +1,321 @@ + + + + + + + + Welcome to use OneinStack + + + + + + +
+
+ + +
+ +
+

Control center

+ +
+ +
+

Congratulations, OneinStack installed successfully!

+

OneinStack Linux+Nginx/Tengine+MySQL/MariaDB/Percona
+PHP+Pureftpd+phpMyAdmin+redis+memcached+jemalloc.

+ +
+ +
+

Tools

+ prober + phpinfo + phpMyAdmin + Opcache +
+ +
+

Steps

+
+
+
+

Dns analysis

+
+
+

Domain control

+
    +
  • Cloudflare
  • +
  • Alibabacloud
  • +
  • DNSPOD
  • +
+ BROWSE DOCS +
+
+
+
+

Add virtual host

+
+
+

Create website

+
    +
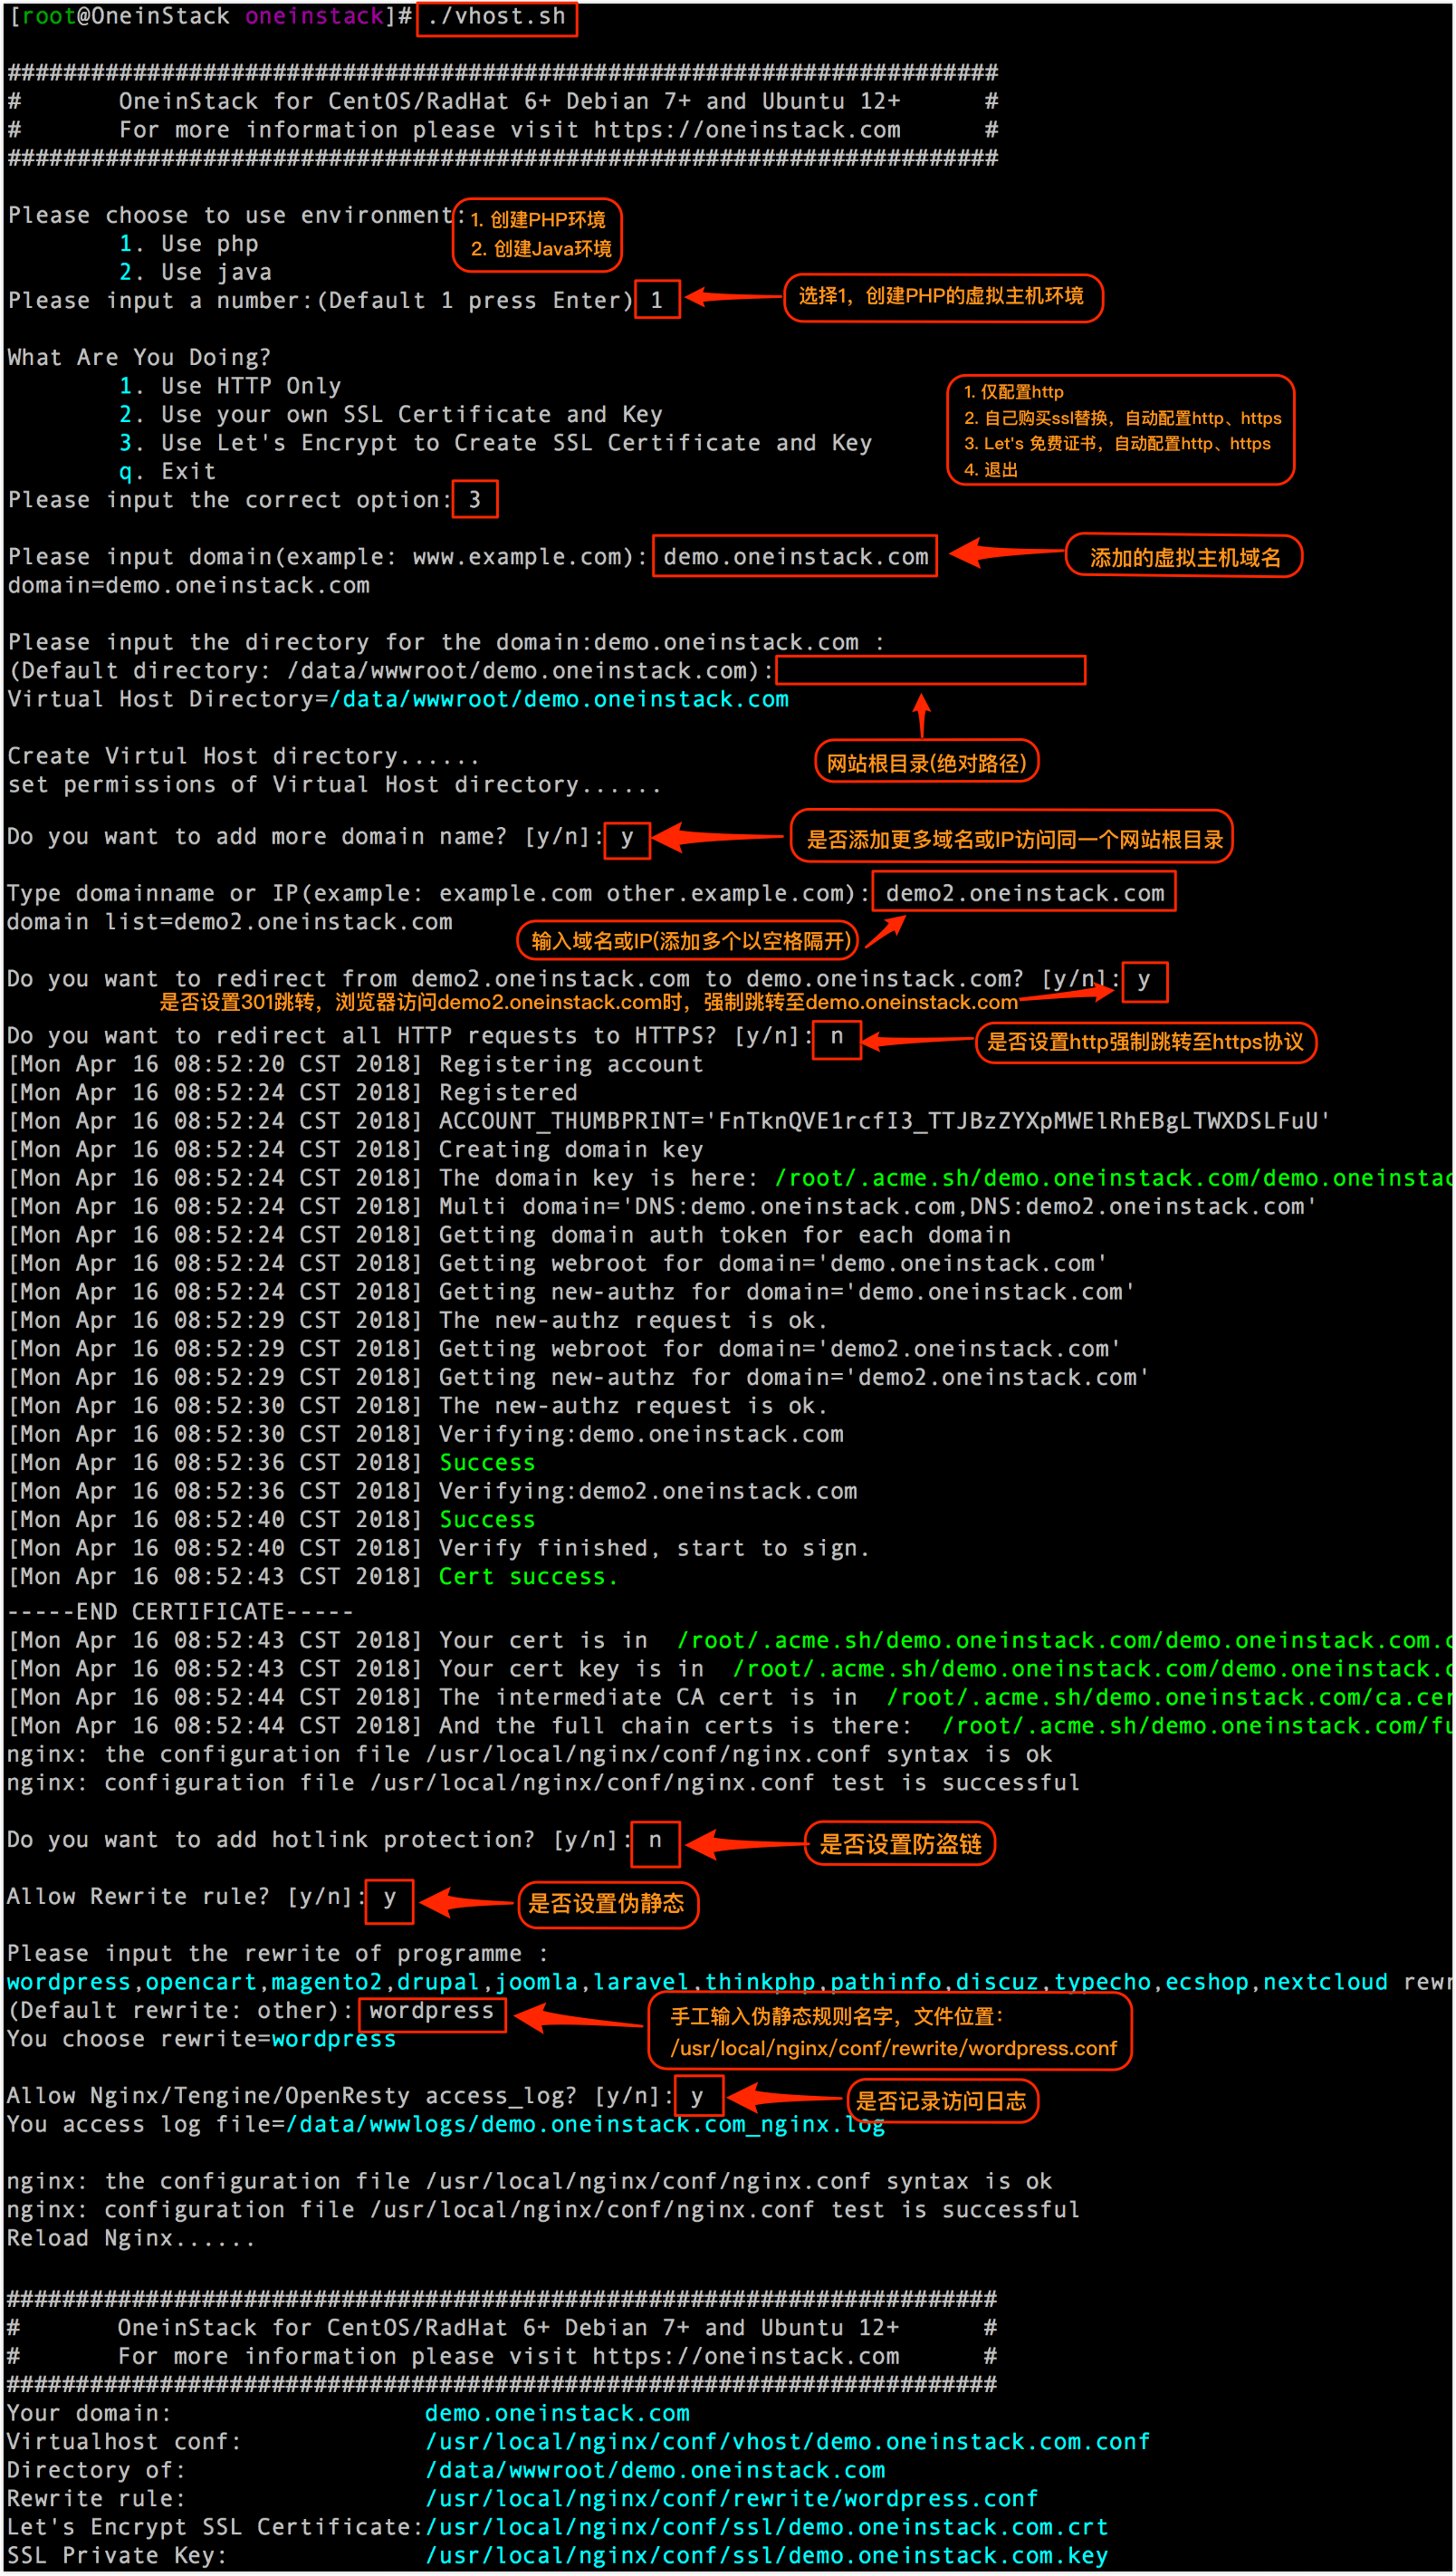
  • Add virtual host: ./vhost.sh
  • +
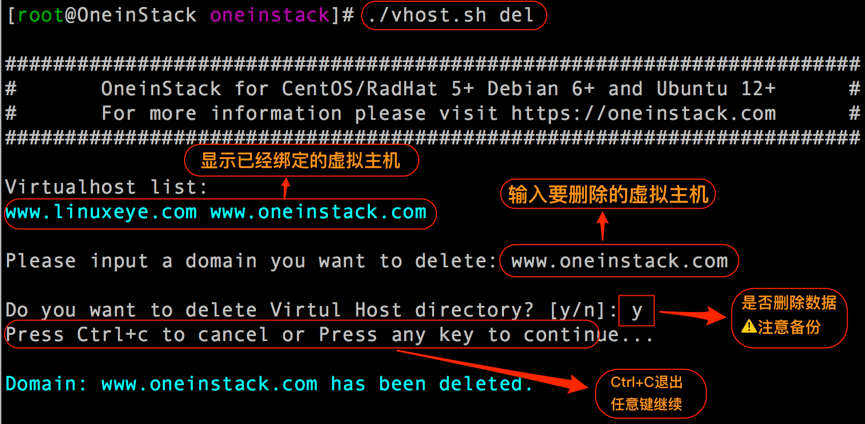
  • Del virtual host: ./vhost.sh --del
  • +
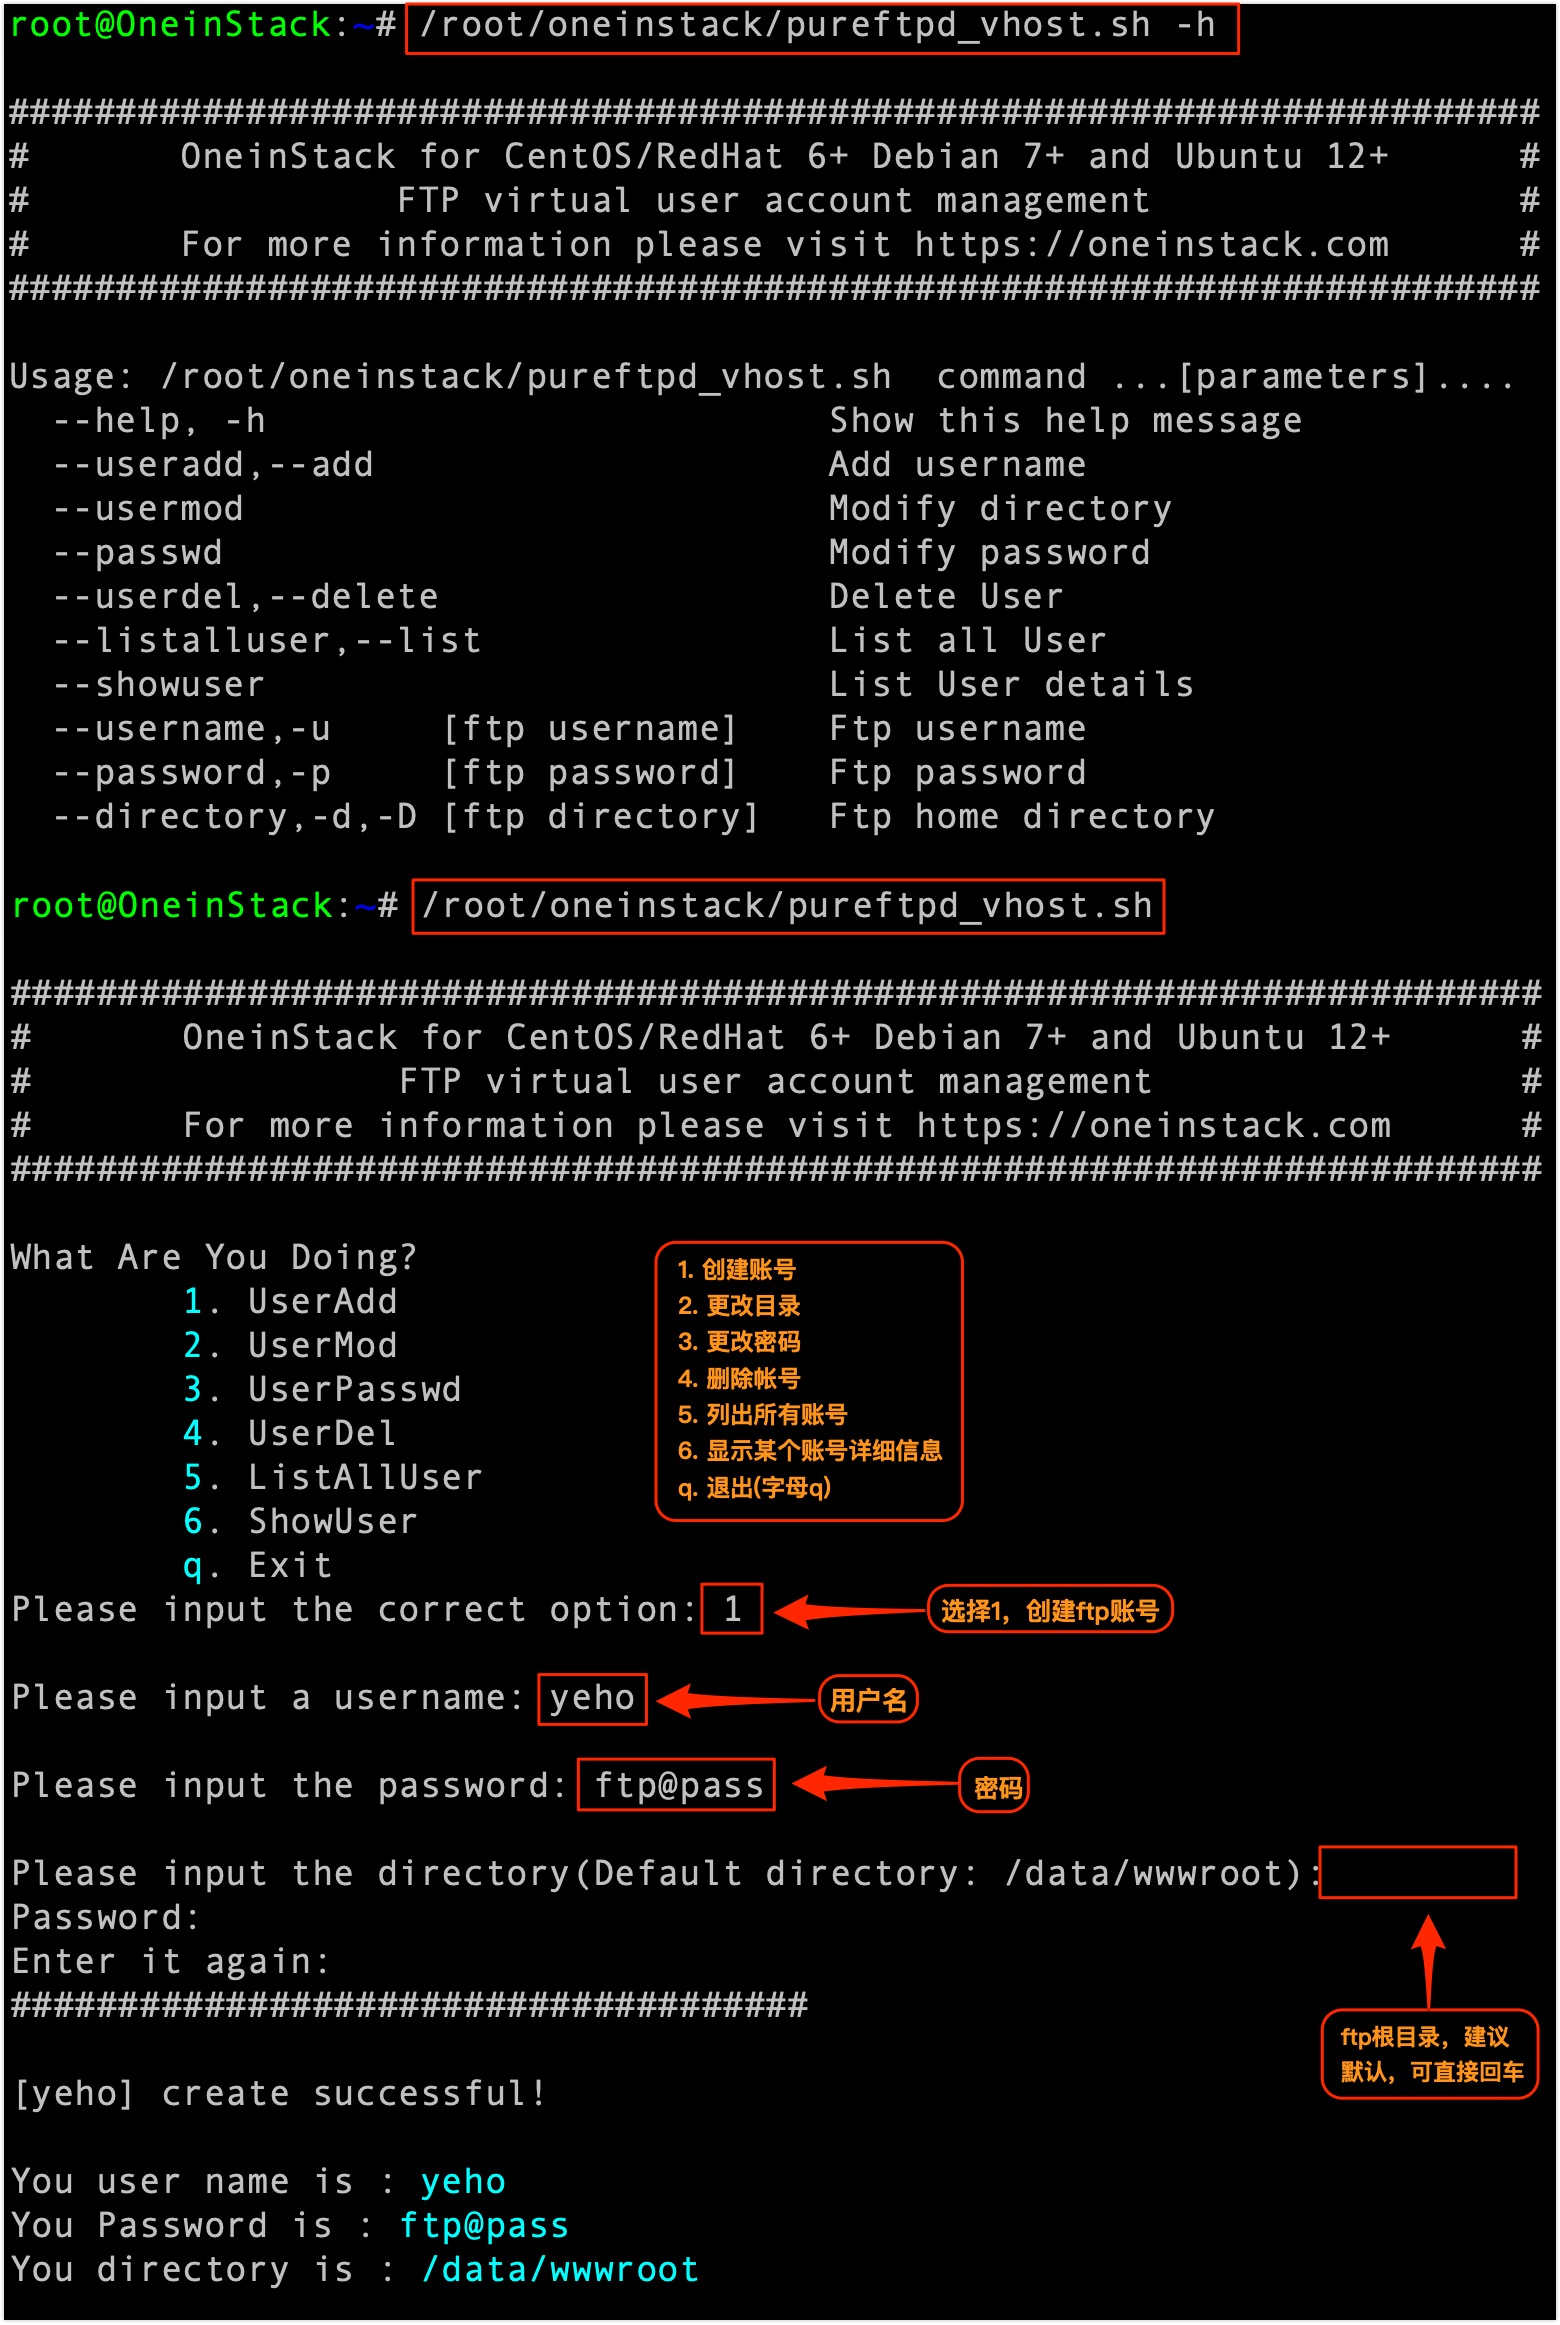
  • Manage FTP account: ./pureftpd_vhost.sh
  • +
+ BROWSE DOCS +
+
+
+
+

Deploy website

+
+
+

Online running

+
    +
  • phpMyAdmin
  • +
  • Manage FTP account: ./pureftpd_vhost.sh
  • +
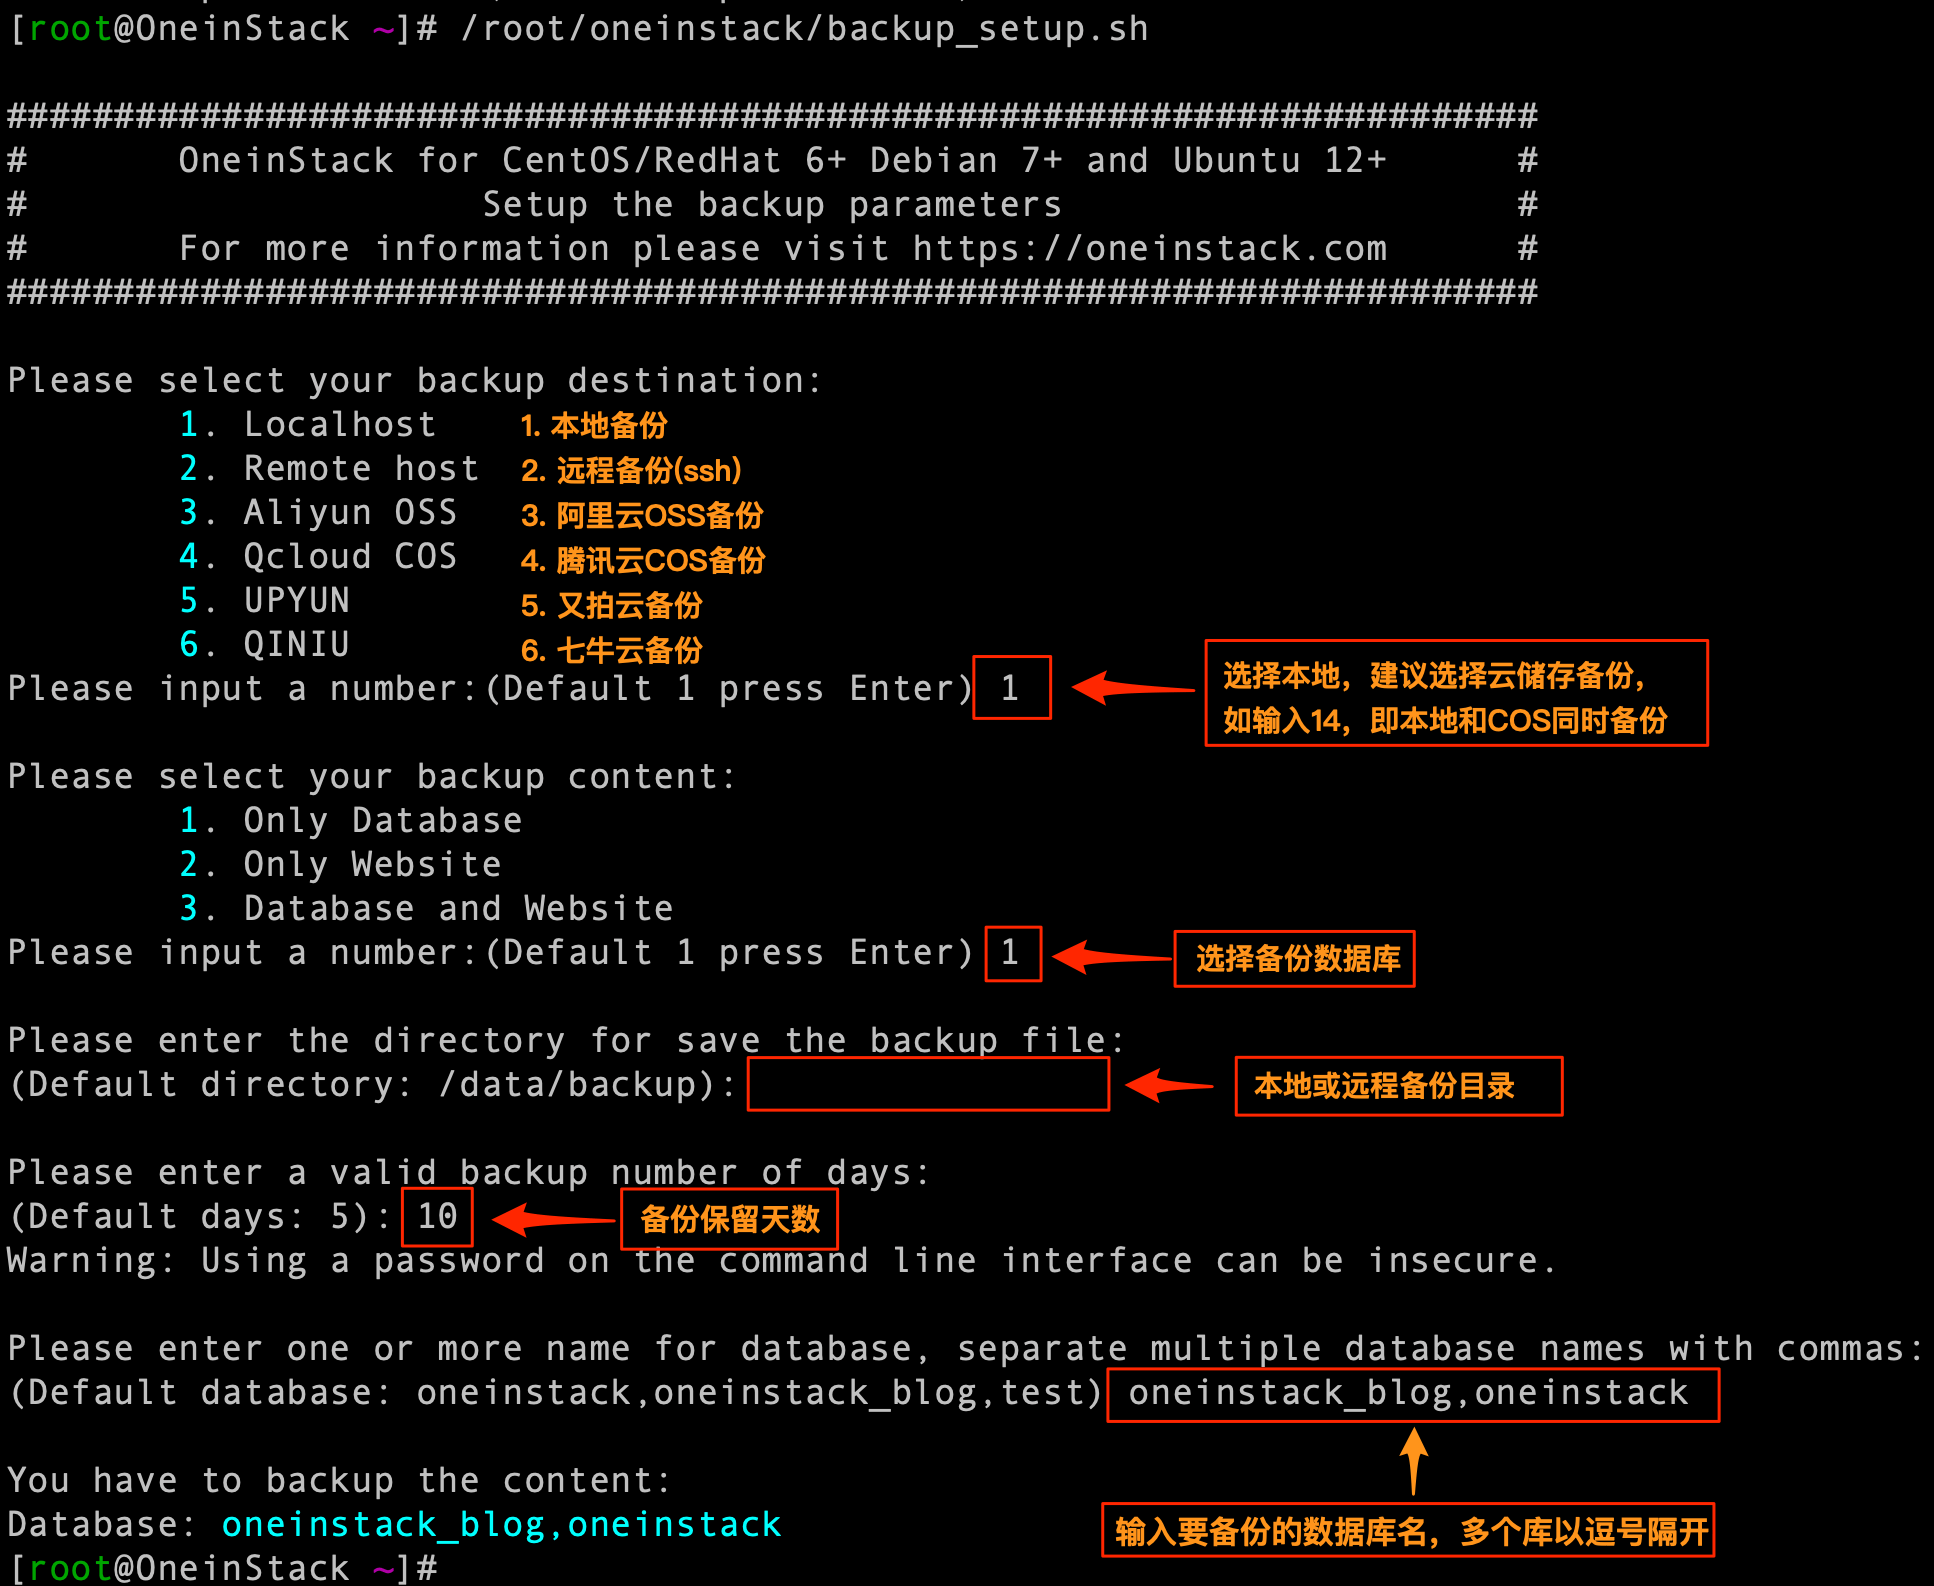
  • Backup: ./backup_setup.sh
  • +
+ BROWSE DOCS +
+
+
+
+ +
+

How to add a virtual host?

+ + 《Interactive install》 +

How to delete a virtual host?

+ + 《Interactive install》 +
+ +
+

FTP Client

+

FileZilla: Download address

+

How to add FTP virtual user?

+ + 《Interactive install》 +
+ +
+

Database

+ +
+ +
+

How to backup?

+ + 《Interactive install》 + +
+ +
+

How to manage service?

+

Nginx/Tengine/OpenResty:

+ +

MySQL/MariaDB/Percona:

+ +

PostgreSQL:

+ +

MongoDB:

+ +

PHP:

+ +

Apache:

+ +

Tomcat:

+ +

Pure-Ftpd:

+ +

Redis:

+ +

Memcached:

+ +
+ +
+

How to upgrade?

+ + +

How to uninstall?

+ + +
+ +
+
+
+ You must specify port numbers (for TCP): +
+
    +
  • ssh: 22
  • +
  • http: 80
  • +
  • https: 443
  • +
  • ftp: 21, 20000~30000
  • +
+
+ +
+ +
+
+

+ OneinStack by LinuxEye +         Telegram Group:   t.me/oneinstack +

+

Top

+
+
+
+
+ + + diff --git a/config/index_cn.html b/config/index_cn.html new file mode 100644 index 0000000..da49040 --- /dev/null +++ b/config/index_cn.html @@ -0,0 +1,322 @@ + + + + + + + + 欢迎您使用OneinStack + + + + + + +
+
+ + +
+ +
+

控制中心

+ +
+ +
+

Congratulations, OneinStack installed successfully!

+

OneinStack Linux+Nginx/Tengine+MySQL/MariaDB/Percona
+PHP+Pureftpd+phpMyAdmin+redis+memcached+jemalloc.

+ +
+ +
+

主机工具

+ 探针 + phpinfo + phpMyAdmin + Opcache +
+ +
+

基本使用步骤

+
+
+
+

域名解析

+
+
+

域名控制

+
    +
  • 阿里云(万网)
  • +
  • DNSPOD
  • +
  • Cloudflare
  • +
+ 详细教程 +
+
+
+
+

新建虚拟主机

+
+
+

建立网站

+
    +
  • 新建虚拟主机 ./vhost.sh
  • +
  • 删除虚拟主机 ./vhost.sh --del
  • +
  • 管理FTP账号 ./pureftpd_vhost.sh
  • +
+ 详细教程 +
+
+
+
+

部署网站

+
+
+

上线运行

+
    +
  • phpMyAdmin
  • +
  • 管理FTP账号 ./pureftpd_vhost.sh
  • +
  • 备份 ./backup_setup.sh
  • +
+ 详细教程 +
+
+
+
+ +
+

如何添加虚拟主机?

+ + 《交互安装》 +

如何删除虚拟主机?

+ + 《交互安装》 +
+ +
+

FTP客户端推荐

+

FileZilla: 下载地址

+

如何管理FTP账号?

+ + 《交互安装》 +
+ +
+

数据库

+ +
+ +
+

如何备份?

+ + 《交互安装》 + +
+ +
+

如何管理服务?

+

Nginx/Tengine/OpenResty:

+ +

MySQL/MariaDB/Percona:

+ +

PostgreSQL:

+ +

MongoDB:

+ +

PHP:

+ +

Apache:

+ +

Tomcat:

+ +

Pure-Ftpd:

+ +

Redis:

+ +

Memcached:

+ +
+ +
+

如何更新版本?

+ + +

如何卸载?

+ + +
+ +
+ +
+
+ 云主机安全组必须打开如下端口: +
+
    +
  • ssh: 22
  • +
  • http: 80
  • +
  • https: 443
  • +
  • ftp: 21, 20000~30000
  • +
+
+ +
+ +
+
+

+ OneinStack by LinuxEye +         QQ群:   262601796(新) 558540514(付费千人群) +

+

回顶部

+
+
+
+
+ + + diff --git a/config/joomla.conf b/config/joomla.conf new file mode 100644 index 0000000..2af92c0 --- /dev/null +++ b/config/joomla.conf @@ -0,0 +1,3 @@ +location / { + try_files $uri $uri/ /index.php?$args; +} diff --git a/config/laravel.conf b/config/laravel.conf new file mode 100644 index 0000000..4b488fd --- /dev/null +++ b/config/laravel.conf @@ -0,0 +1,3 @@ +location / { + try_files $uri $uri/ /index.php?$query_string; +} diff --git a/config/magento2.conf b/config/magento2.conf new file mode 100644 index 0000000..35e18c1 --- /dev/null +++ b/config/magento2.conf @@ -0,0 +1,171 @@ +server { + listen 80; + server_name oneinstack.com; + set $MAGE_ROOT /data/wwwroot/default; + root $MAGE_ROOT/pub; + index index.php; + autoindex off; + charset UTF-8; + error_page 404 403 /errors/404.php; + #add_header "X-UA-Compatible" "IE=Edge"; + + # PHP entry point for setup application + location ~* ^/setup($|/) { + root $MAGE_ROOT; + location ~ ^/setup/index.php { + fastcgi_split_path_info ^(.+?\.php)(/.*)$; + fastcgi_pass unix:/dev/shm/php-cgi.sock; + fastcgi_index index.php; + fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name; + include fastcgi_params; + } + + location ~ ^/setup/(?!pub/). { + deny all; + } + + location ~ ^/setup/pub/ { + add_header X-Frame-Options "SAMEORIGIN"; + } + } + + # PHP entry point for update application + location ~* ^/update($|/) { + root $MAGE_ROOT; + location ~ ^/update/index.php { + fastcgi_split_path_info ^(/update/index.php)(/.+)$; + fastcgi_pass unix:/dev/shm/php-cgi.sock; + fastcgi_index index.php; + fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name; + fastcgi_param PATH_INFO $fastcgi_path_info; + include fastcgi_params; + } + + # Deny everything but index.php + location ~ ^/update/(?!pub/). { + deny all; + } + + location ~ ^/update/pub/ { + add_header X-Frame-Options "SAMEORIGIN"; + } + } + + location / { + try_files $uri $uri/ /index.php?$args; + } + + location /pub/ { + location ~ ^/pub/media/(downloadable|customer|import|theme_customization/.*\.xml) { + deny all; + } + alias $MAGE_ROOT/pub/; + add_header X-Frame-Options "SAMEORIGIN"; + } + + location /static/ { + # Uncomment the following line in production mode + # expires max; + # Remove signature of the static files that is used to overcome the browser cache + location ~ ^/static/version { + rewrite ^/static/(version\d*/)?(.*)$ /static/$2 last; + } + + location ~* \.(ico|jpg|jpeg|png|gif|svg|js|css|swf|eot|ttf|otf|woff|woff2)$ { + add_header Cache-Control "public"; + add_header X-Frame-Options "SAMEORIGIN"; + expires +1y; + if (!-f $request_filename) { + rewrite ^/static/(version\d*/)?(.*)$ /static.php?resource=$2 last; + } + } + + location ~* \.(zip|gz|gzip|bz2|csv|xml)$ { + add_header Cache-Control "no-store"; + add_header X-Frame-Options "SAMEORIGIN"; + expires off; + if (!-f $request_filename) { + rewrite ^/static/(version\d*/)?(.*)$ /static.php?resource=$2 last; + } + } + + if (!-f $request_filename) { + rewrite ^/static/(version\d*/)?(.*)$ /static.php?resource=$2 last; + } + add_header X-Frame-Options "SAMEORIGIN"; + } + + location /media/ { + try_files $uri $uri/ /get.php?$args; + location ~ ^/media/theme_customization/.*\.xml { + deny all; + } + + location ~* \.(ico|jpg|jpeg|png|gif|svg|js|css|swf|eot|ttf|otf|woff|woff2)$ { + add_header Cache-Control "public"; + add_header X-Frame-Options "SAMEORIGIN"; + expires +1y; + try_files $uri $uri/ /get.php?$args; + } + location ~* \.(zip|gz|gzip|bz2|csv|xml)$ { + add_header Cache-Control "no-store"; + add_header X-Frame-Options "SAMEORIGIN"; + expires off; + try_files $uri $uri/ /get.php?$args; + } + add_header X-Frame-Options "SAMEORIGIN"; + } + + location /media/customer/ { + deny all; + } + + location /media/downloadable/ { + deny all; + } + + location /media/import/ { + deny all; + } + + # PHP entry point for main application + location ~ (index|get|static|report|404|503)\.php$ { + try_files $uri =404; + fastcgi_pass unix:/dev/shm/php-cgi.sock; + fastcgi_buffers 1024 4k; + + fastcgi_param PHP_FLAG "session.auto_start=off \n suhosin.session.cryptua=off"; + fastcgi_param PHP_VALUE "memory_limit=768M \n max_execution_time=600"; + fastcgi_read_timeout 600s; + fastcgi_connect_timeout 600s; + + fastcgi_index index.php; + fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name; + include fastcgi_params; + } + + gzip on; + gzip_disable "msie6"; + gzip_comp_level 6; + gzip_min_length 1100; + gzip_buffers 16 8k; + gzip_proxied any; + gzip_types + text/plain + text/css + text/js + text/xml + text/javascript + application/javascript + application/x-javascript + application/json + application/xml + application/xml+rss + image/svg+xml; + gzip_vary on; + + # Banned locations (only reached if the earlier PHP entry point regexes don't match) + location ~* (\.php$|\.htaccess$|\.git) { + deny all; + } +} diff --git a/config/nextcloud.conf b/config/nextcloud.conf new file mode 100644 index 0000000..ca6eed8 --- /dev/null +++ b/config/nextcloud.conf @@ -0,0 +1,82 @@ +#(可选)添加如下header主要为了安全 +add_header X-Content-Type-Options nosniff; +add_header X-XSS-Protection "1; mode=block"; +add_header X-Robots-Tag none; +add_header X-Download-Options noopen; +add_header X-Permitted-Cross-Domain-Policies none; + +#(可选)为了支持user_webfinger app +rewrite ^/.well-known/host-meta /public.php?service=host-meta last; +rewrite ^/.well-known/host-meta.json /public.php?service=host-meta-json last; + +#这儿是为了支持日历和联系人,建议加上 +location = /.well-known/carddav { + return 301 $scheme://$host/remote.php/dav; +} +location = /.well-known/caldav { + return 301 $scheme://$host/remote.php/dav; +} + +#设置上传文件的最大大小(还和php里的那个设置有关) +client_max_body_size 512M; +fastcgi_buffers 64 4K; + +#最主要的,将所有请求转发到index.php上 +location / { + rewrite ^ /index.php$uri; +} + +#安全设置,禁止访问部分敏感内容 +location ~ ^/(?:build|tests|config|lib|3rdparty|templates|data)/ { + deny all; +} +location ~ ^/(?:\.|autotest|occ|issue|indie|db_|console) { + deny all; +} + +#这部分吧,默认就有,不过有所不同,所以我合并了下,替换原来的就行 +location ~ ^/(?:index|remote|public|cron|core/ajax/update|status|ocs/v[12]|updater/.+|ocs-provider/.+)\.php(?:$|/) { + fastcgi_split_path_info ^(.+\.php)(/.*)$; + fastcgi_param PATH_INFO $fastcgi_path_info; + fastcgi_param modHeadersAvailable true; + fastcgi_param front_controller_active true; + fastcgi_pass unix:/dev/shm/php-cgi.sock; + fastcgi_intercept_errors on; + fastcgi_request_buffering off; + include fastcgi.conf; +} + +#安全设置,禁止访问部分敏感内容 +location ~ ^/(?:updater|ocs-provider)(?:$|/) { + try_files $uri/ =404; + index index.php; +} + +location ~ \.(?:css|js|woff|svg|gif)$ { + try_files $uri /index.php$uri$is_args$args; + add_header Cache-Control "public, max-age=15778463"; + add_header X-Content-Type-Options nosniff; + add_header X-XSS-Protection "1; mode=block"; + add_header X-Robots-Tag none; + add_header X-Download-Options noopen; + add_header X-Permitted-Cross-Domain-Policies none; + access_log off; +} + +location ~ \.(?:png|html|ttf|ico|jpg|jpeg)$ { + try_files $uri /index.php$uri$is_args$args; + access_log off; +} + +location = /robots.txt { + allow all; + log_not_found off; + access_log off; +} + +gzip on; +gzip_vary on; +gzip_comp_level 4; +gzip_min_length 256; +gzip_proxied expired no-cache no-store private no_last_modified no_etag auth; +gzip_types application/atom+xml application/javascript application/json application/ld+json application/manifest+json application/rss+xml application/vnd.geo+json application/vnd.ms-fontobject application/x-font-ttf application/x-web-app-manifest+json application/xhtml+xml application/xml font/opentype image/bmp image/svg+xml image/x-icon text/cache-manifest text/css text/plain text/vcard text/vnd.rim.location.xloc text/vtt text/x-component text/x-cross-domain-policy; diff --git a/config/nginx.conf b/config/nginx.conf new file mode 100644 index 0000000..8e72207 --- /dev/null +++ b/config/nginx.conf @@ -0,0 +1,123 @@ +user www www; +worker_processes auto; + +error_log /data/wwwlogs/error_nginx.log crit; +pid /var/run/nginx.pid; +worker_rlimit_nofile 51200; + +events { + use epoll; + worker_connections 51200; + multi_accept on; +} + +http { + include mime.types; + default_type application/octet-stream; + server_names_hash_bucket_size 128; + client_header_buffer_size 32k; + large_client_header_buffers 4 32k; + client_max_body_size 1024m; + client_body_buffer_size 10m; + sendfile on; + tcp_nopush on; + keepalive_timeout 120; + server_tokens off; + tcp_nodelay on; + + fastcgi_connect_timeout 300; + fastcgi_send_timeout 300; + fastcgi_read_timeout 300; + fastcgi_buffer_size 64k; + fastcgi_buffers 4 64k; + fastcgi_busy_buffers_size 128k; + fastcgi_temp_file_write_size 128k; + fastcgi_intercept_errors on; + + #Gzip Compression + gzip on; + gzip_buffers 16 8k; + gzip_comp_level 6; + gzip_http_version 1.1; + gzip_min_length 256; + gzip_proxied any; + gzip_vary on; + gzip_types + text/xml application/xml application/atom+xml application/rss+xml application/xhtml+xml image/svg+xml + text/javascript application/javascript application/x-javascript + text/x-json application/json application/x-web-app-manifest+json + text/css text/plain text/x-component + font/opentype application/x-font-ttf application/vnd.ms-fontobject + image/x-icon; + gzip_disable "MSIE [1-6]\.(?!.*SV1)"; + + ##Brotli Compression + #brotli on; + #brotli_comp_level 6; + #brotli_types text/plain text/css application/json application/x-javascript text/xml application/xml application/xml+rss text/javascript application/javascript image/svg+xml; + + ##If you have a lot of static files to serve through Nginx then caching of the files' metadata (not the actual files' contents) can save some latency. + #open_file_cache max=1000 inactive=20s; + #open_file_cache_valid 30s; + #open_file_cache_min_uses 2; + #open_file_cache_errors on; + + log_format json escape=json '{"@timestamp":"$time_iso8601",' + '"server_addr":"$server_addr",' + '"remote_addr":"$remote_addr",' + '"scheme":"$scheme",' + '"request_method":"$request_method",' + '"request_uri": "$request_uri",' + '"request_length": "$request_length",' + '"uri": "$uri", ' + '"request_time":$request_time,' + '"body_bytes_sent":$body_bytes_sent,' + '"bytes_sent":$bytes_sent,' + '"status":"$status",' + '"upstream_time":"$upstream_response_time",' + '"upstream_host":"$upstream_addr",' + '"upstream_status":"$upstream_status",' + '"host":"$host",' + '"http_referer":"$http_referer",' + '"http_user_agent":"$http_user_agent"' + '}'; + +######################## default ############################ + server { + listen 80; + server_name _; + access_log /data/wwwlogs/access_nginx.log combined; + root /data/wwwroot/default; + index index.html index.htm index.php; + #error_page 404 /404.html; + #error_page 502 /502.html; + location /nginx_status { + stub_status on; + access_log off; + allow 127.0.0.1; + deny all; + } + location ~ [^/]\.php(/|$) { + #fastcgi_pass remote_php_ip:9000; + fastcgi_pass unix:/dev/shm/php-cgi.sock; + fastcgi_index index.php; + include fastcgi.conf; + } + location ~ .*\.(gif|jpg|jpeg|png|bmp|swf|flv|mp4|ico)$ { + expires 30d; + access_log off; + } + location ~ .*\.(js|css)?$ { + expires 7d; + access_log off; + } + location ~ ^/(\.user.ini|\.ht|\.git|\.svn|\.project|LICENSE|README.md) { + deny all; + } + location /.well-known { + allow all; + } + } +########################## vhost ############################# + include vhost/*.conf; +} diff --git a/config/nginx_apache.conf b/config/nginx_apache.conf new file mode 100644 index 0000000..ee6399b --- /dev/null +++ b/config/nginx_apache.conf @@ -0,0 +1,128 @@ +user www www; +worker_processes auto; + +error_log /data/wwwlogs/error_nginx.log crit; +pid /var/run/nginx.pid; +worker_rlimit_nofile 51200; + +events { + use epoll; + worker_connections 51200; + multi_accept on; +} + +http { + include mime.types; + default_type application/octet-stream; + server_names_hash_bucket_size 128; + client_header_buffer_size 32k; + large_client_header_buffers 4 32k; + client_max_body_size 1024m; + client_body_buffer_size 10m; + sendfile on; + tcp_nopush on; + keepalive_timeout 120; + server_tokens off; + tcp_nodelay on; + + fastcgi_connect_timeout 300; + fastcgi_send_timeout 300; + fastcgi_read_timeout 300; + fastcgi_buffer_size 64k; + fastcgi_buffers 4 64k; + fastcgi_busy_buffers_size 128k; + fastcgi_temp_file_write_size 128k; + fastcgi_intercept_errors on; + + #Gzip Compression + gzip on; + gzip_buffers 16 8k; + gzip_comp_level 6; + gzip_http_version 1.1; + gzip_min_length 256; + gzip_proxied any; + gzip_vary on; + gzip_types + text/xml application/xml application/atom+xml application/rss+xml application/xhtml+xml image/svg+xml + text/javascript application/javascript application/x-javascript + text/x-json application/json application/x-web-app-manifest+json + text/css text/plain text/x-component + font/opentype application/x-font-ttf application/vnd.ms-fontobject + image/x-icon; + gzip_disable "MSIE [1-6]\.(?!.*SV1)"; + + ##Brotli Compression + #brotli on; + #brotli_comp_level 6; + #brotli_types text/plain text/css application/json application/x-javascript text/xml application/xml application/xml+rss text/javascript application/javascript image/svg+xml; + + ##If you have a lot of static files to serve through Nginx then caching of the files' metadata (not the actual files' contents) can save some latency. + #open_file_cache max=1000 inactive=20s; + #open_file_cache_valid 30s; + #open_file_cache_min_uses 2; + #open_file_cache_errors on; + + log_format json escape=json '{"@timestamp":"$time_iso8601",' + '"server_addr":"$server_addr",' + '"remote_addr":"$remote_addr",' + '"scheme":"$scheme",' + '"request_method":"$request_method",' + '"request_uri": "$request_uri",' + '"request_length": "$request_length",' + '"uri": "$uri", ' + '"request_time":$request_time,' + '"body_bytes_sent":$body_bytes_sent,' + '"bytes_sent":$bytes_sent,' + '"status":"$status",' + '"upstream_time":"$upstream_response_time",' + '"upstream_host":"$upstream_addr",' + '"upstream_status":"$upstream_status",' + '"host":"$host",' + '"http_referer":"$http_referer",' + '"http_user_agent":"$http_user_agent"' + '}'; + +######################## default ############################ + server { + listen 80; + server_name _; + access_log /data/wwwlogs/access_nginx.log combined; + root /data/wwwroot/default; + index index.html index.htm index.php; + #error_page 404 /404.html; + #error_page 502 /502.html; + location /nginx_status { + stub_status on; + access_log off; + allow 127.0.0.1; + deny all; + } + location / { + try_files $uri @apache; + } + location @apache { + proxy_pass http://127.0.0.1:88; + include proxy.conf; + } + location ~ [^/]\.php(/|$) { + proxy_pass http://127.0.0.1:88; + include proxy.conf; + } + location ~ .*\.(gif|jpg|jpeg|png|bmp|swf|flv|mp4|ico)$ { + expires 30d; + access_log off; + } + location ~ .*\.(js|css)?$ { + expires 7d; + access_log off; + } + location ~ ^/(\.user.ini|\.ht|\.git|\.svn|\.project|LICENSE|README.md) { + deny all; + } + location /.well-known { + allow all; + } + } +########################## vhost ############################# + include vhost/*.conf; +} diff --git a/config/nginx_tomcat.conf b/config/nginx_tomcat.conf new file mode 100644 index 0000000..710c68e --- /dev/null +++ b/config/nginx_tomcat.conf @@ -0,0 +1,121 @@ +user www www; +worker_processes auto; + +error_log /data/wwwlogs/error_nginx.log crit; +pid /var/run/nginx.pid; +worker_rlimit_nofile 51200; + +events { + use epoll; + worker_connections 51200; + multi_accept on; +} + +http { + include mime.types; + default_type application/octet-stream; + server_names_hash_bucket_size 128; + client_header_buffer_size 32k; + large_client_header_buffers 4 32k; + client_max_body_size 1024m; + client_body_buffer_size 10m; + sendfile on; + tcp_nopush on; + keepalive_timeout 120; + server_tokens off; + tcp_nodelay on; + + fastcgi_connect_timeout 300; + fastcgi_send_timeout 300; + fastcgi_read_timeout 300; + fastcgi_buffer_size 64k; + fastcgi_buffers 4 64k; + fastcgi_busy_buffers_size 128k; + fastcgi_temp_file_write_size 128k; + fastcgi_intercept_errors on; + + #Gzip Compression + gzip on; + gzip_buffers 16 8k; + gzip_comp_level 6; + gzip_http_version 1.1; + gzip_min_length 256; + gzip_proxied any; + gzip_vary on; + gzip_types + text/xml application/xml application/atom+xml application/rss+xml application/xhtml+xml image/svg+xml + text/javascript application/javascript application/x-javascript + text/x-json application/json application/x-web-app-manifest+json + text/css text/plain text/x-component + font/opentype application/x-font-ttf application/vnd.ms-fontobject + image/x-icon; + gzip_disable "MSIE [1-6]\.(?!.*SV1)"; + + ##Brotli Compression + #brotli on; + #brotli_comp_level 6; + #brotli_types text/plain text/css application/json application/x-javascript text/xml application/xml application/xml+rss text/javascript application/javascript image/svg+xml; + + ##If you have a lot of static files to serve through Nginx then caching of the files' metadata (not the actual files' contents) can save some latency. + #open_file_cache max=1000 inactive=20s; + #open_file_cache_valid 30s; + #open_file_cache_min_uses 2; + #open_file_cache_errors on; + + log_format json escape=json '{"@timestamp":"$time_iso8601",' + '"server_addr":"$server_addr",' + '"remote_addr":"$remote_addr",' + '"scheme":"$scheme",' + '"request_method":"$request_method",' + '"request_uri": "$request_uri",' + '"request_length": "$request_length",' + '"uri": "$uri", ' + '"request_time":$request_time,' + '"body_bytes_sent":$body_bytes_sent,' + '"bytes_sent":$bytes_sent,' + '"status":"$status",' + '"upstream_time":"$upstream_response_time",' + '"upstream_host":"$upstream_addr",' + '"upstream_status":"$upstream_status",' + '"host":"$host",' + '"http_referer":"$http_referer",' + '"http_user_agent":"$http_user_agent"' + '}'; + +######################## default ############################ + server { + listen 80; + server_name _; + access_log /data/wwwlogs/access_nginx.log combined; + root /data/wwwroot/default; + index index.html index.htm index.jsp; + #error_page 404 /404.html; + #error_page 502 /502.html; + location /nginx_status { + stub_status on; + access_log off; + allow 127.0.0.1; + deny all; + } + location ~ .*\.(gif|jpg|jpeg|png|bmp|swf|flv|mp4|ico)$ { + expires 30d; + access_log off; + } + location ~ .*\.(js|css)?$ { + expires 7d; + access_log off; + } + location ~ { + proxy_pass http://127.0.0.1:8080; + include proxy.conf; + } + location ~ ^/(\.user.ini|\.ht|\.git|\.svn|\.project|LICENSE|README.md) { + deny all; + } + location /.well-known { + allow all; + } + } +########################## vhost ############################# + include vhost/*.conf; +} diff --git a/config/opencart.conf b/config/opencart.conf new file mode 100644 index 0000000..d52b219 --- /dev/null +++ b/config/opencart.conf @@ -0,0 +1,13 @@ +location = /sitemap.xml { + rewrite ^(.*)$ /index.php?route=feed/google_sitemap break; +} +location = /googlebase.xml { + rewrite ^(.*)$ /index.php?route=feed/google_base break; +} +location / { + # This try_files directive is used to enable SEO-friendly URLs for OpenCart + try_files $uri $uri/ @opencart; +} +location @opencart { + rewrite ^/(.+)$ /index.php?_route_=$1 last; +} diff --git a/config/pure-ftpd.conf b/config/pure-ftpd.conf new file mode 100644 index 0000000..a9dd557 --- /dev/null +++ b/config/pure-ftpd.conf @@ -0,0 +1,444 @@ + +############################################################ +# # +# Configuration file for pure-ftpd wrappers # +# # +############################################################ + +# If you want to run Pure-FTPd with this configuration +# instead of command-line options, please run the +# following command : +# +# /usr/local/pureftpd/sbin/pure-config.pl /usr/local/pureftpd/etc/pure-ftpd.conf +# +# Please don't forget to have a look at documentation at +# http://www.pureftpd.org/documentation.shtml for a complete list of +# options. + +# Cage in every user in his home directory + +ChrootEveryone yes + + + +# If the previous option is set to "no", members of the following group +# won't be caged. Others will be. If you don't want chroot()ing anyone, +# just comment out ChrootEveryone and TrustedGID. + +# TrustedGID 100 + + + +# Turn on compatibility hacks for broken clients + +BrokenClientsCompatibility no + + + +# Maximum number of simultaneous users + +MaxClientsNumber 5000 + + + +# Fork in background + +Daemonize yes + + + +# Maximum number of sim clients with the same IP address + +MaxClientsPerIP 500 + + + +# If you want to log all client commands, set this to "yes". +# This directive can be duplicated to also log server responses. + +VerboseLog no + + + +# List dot-files even when the client doesn't send "-a". + +DisplayDotFiles yes + + + +# Don't allow authenticated users - have a public anonymous FTP only. + +AnonymousOnly no + + + +# Disallow anonymous connections. Only allow authenticated users. + +NoAnonymous yes + + + +# Syslog facility (auth, authpriv, daemon, ftp, security, user, local*) +# The default facility is "ftp". "none" disables logging. + +SyslogFacility ftp + + + +# Display fortune cookies + +# FortunesFile /usr/share/fortune/zippy + + + +# Don't resolve host names in log files. Logs are less verbose, but +# it uses less bandwidth. Set this to "yes" on very busy servers or +# if you don't have a working DNS. + +DontResolve yes + + + +# Maximum idle time in minutes (default = 15 minutes) + +MaxIdleTime 15 + + + +# LDAP configuration file (see README.LDAP) + +# LDAPConfigFile /etc/pureftpd-ldap.conf + + + +# MySQL configuration file (see README.MySQL) + +# MySQLConfigFile /usr/local/pureftpd/etc/pureftpd-mysql.conf + + +# Postgres configuration file (see README.PGSQL) + +# PGSQLConfigFile /etc/pureftpd-pgsql.conf + + +# PureDB user database (see README.Virtual-Users) + +PureDB /usr/local/pureftpd/etc/pureftpd.pdb + + +# Path to pure-authd socket (see README.Authentication-Modules) + +# ExtAuth /var/run/ftpd.sock + + + +# If you want to enable PAM authentication, uncomment the following line + +# PAMAuthentication yes + + + +# If you want simple Unix (/etc/passwd) authentication, uncomment this + +UnixAuthentication yes + + + +# Please note that LDAPConfigFile, MySQLConfigFile, PAMAuthentication and +# UnixAuthentication can be used only once, but they can be combined +# together. For instance, if you use MySQLConfigFile, then UnixAuthentication, +# the SQL server will be asked. If the SQL authentication fails because the +# user wasn't found, another try # will be done with /etc/passwd and +# /etc/shadow. If the SQL authentication fails because the password was wrong, +# the authentication chain stops here. Authentication methods are chained in +# the order they are given. + + + +# 'ls' recursion limits. The first argument is the maximum number of +# files to be displayed. The second one is the max subdirectories depth + +LimitRecursion 2000 8 + + + +# Are anonymous users allowed to create new directories ? + +AnonymousCanCreateDirs no + + + +# If the system is more loaded than the following value, +# anonymous users aren't allowed to download. + +MaxLoad 4 + + + +# Port range for passive connections replies. - for firewalling. + +PassivePortRange 20000 30000 + + + +# Force an IP address in PASV/EPSV/SPSV replies. - for NAT. +# Symbolic host names are also accepted for gateways with dynamic IP +# addresses. + +# ForcePassiveIP 192.168.0.1 + + + +# Upload/download ratio for anonymous users. + +# AnonymousRatio 1 10 + + + +# Upload/download ratio for all users. +# This directive superscedes the previous one. + +# UserRatio 1 10 + + + +# Disallow downloading of files owned by "ftp", ie. +# files that were uploaded but not validated by a local admin. + +AntiWarez yes + + + +# IP address/port to listen to (default=all IP and port 21). + +# Bind 127.0.0.1,21 + + + +# Maximum bandwidth for anonymous users in KB/s + +# AnonymousBandwidth 8 + + + +# Maximum bandwidth for *all* users (including anonymous) in KB/s +# Use AnonymousBandwidth *or* UserBandwidth, both makes no sense. + +# UserBandwidth 8 + + + +# File creation mask. : . +# 177:077 if you feel paranoid. + +Umask 133:022 + + + +# Minimum UID for an authenticated user to log in. + +MinUID 100 + + + +# Allow FXP transfers for authenticated users. + +AllowUserFXP no + + + +# Allow anonymous FXP for anonymous and non-anonymous users. + +AllowAnonymousFXP no + + + +# Users can't delete/write files beginning with a dot ('.') +# even if they own them. If TrustedGID is enabled, this group +# will have access to dot-files, though. + +ProhibitDotFilesWrite no + + + +# Prohibit *reading* of files beginning with a dot (.history, .ssh...) + +ProhibitDotFilesRead no + + + +# Never overwrite files. When a file whoose name already exist is uploaded, +# it get automatically renamed to file.1, file.2, file.3, ... + +AutoRename no + + + +# Disallow anonymous users to upload new files (no = upload is allowed) + +AnonymousCantUpload no + + + +# Only connections to this specific IP address are allowed to be +# non-anonymous. You can use this directive to open several public IPs for +# anonymous FTP, and keep a private firewalled IP for remote administration. +# You can also only allow a non-routable local IP (like 10.x.x.x) to +# authenticate, and keep a public anon-only FTP server on another IP. + +#TrustedIP 10.1.1.1 + + + +# If you want to add the PID to every logged line, uncomment the following +# line. + +#LogPID yes + + + +# Create an additional log file with transfers logged in a Apache-like format : +# fw.c9x.org - jedi [13/Dec/1975:19:36:39] "GET /ftp/linux.tar.bz2" 200 21809338 +# This log file can then be processed by www traffic analyzers. + +# AltLog clf:/var/log/pureftpd.log + + + +# Create an additional log file with transfers logged in a format optimized +# for statistic reports. + +# AltLog stats:/var/log/pureftpd.log + + + +# Create an additional log file with transfers logged in the standard W3C +# format (compatible with most commercial log analyzers) + +# AltLog w3c:/var/log/pureftpd.log + + + +# Disallow the CHMOD command. Users can't change perms of their files. + +#NoChmod yes + + + +# Allow users to resume and upload files, but *NOT* to delete them. + +#KeepAllFiles yes + + + +# Automatically create home directories if they are missing + +CreateHomeDir no + + + +# Enable virtual quotas. The first number is the max number of files. +# The second number is the max size of megabytes. +# So 1000:10 limits every user to 1000 files and 10 Mb. + +#Quota 1000:10 + + + +# If your pure-ftpd has been compiled with standalone support, you can change +# the location of the pid file. The default is /var/run/pure-ftpd.pid + +#PIDFile /var/run/pure-ftpd.pid + + + +# If your pure-ftpd has been compiled with pure-uploadscript support, +# this will make pure-ftpd write info about new uploads to +# /var/run/pure-ftpd.upload.pipe so pure-uploadscript can read it and +# spawn a script to handle the upload. + +#CallUploadScript yes + + + +# This option is useful with servers where anonymous upload is +# allowed. As /var/ftp is in /var, it save some space and protect +# the log files. When the partition is more that X percent full, +# new uploads are disallowed. + +MaxDiskUsage 99 + + + +# Set to 'yes' if you don't want your users to rename files. + +#NoRename yes + + + +# Be 'customer proof' : workaround against common customer mistakes like +# 'chmod 0 public_html', that are valid, but that could cause ignorant +# customers to lock their files, and then keep your technical support busy +# with silly issues. If you're sure all your users have some basic Unix +# knowledge, this feature is useless. If you're a hosting service, enable it. + +CustomerProof yes + + + +# Per-user concurrency limits. It will only work if the FTP server has +# been compiled with --with-peruserlimits (and this is the case on +# most binary distributions) . +# The format is : : +# For instance, 3:20 means that the same authenticated user can have 3 active +# sessions max. And there are 20 anonymous sessions max. + +# PerUserLimits 3:20 + + + +# When a file is uploaded and there is already a previous version of the file +# with the same name, the old file will neither get removed nor truncated. +# Upload will take place in a temporary file and once the upload is complete, +# the switch to the new version will be atomic. For instance, when a large PHP +# script is being uploaded, the web server will still serve the old version and +# immediatly switch to the new one as soon as the full file will have been +# transfered. This option is incompatible with virtual quotas. + +# NoTruncate yes + + + +# This option can accept three values : +# 0 : disable SSL/TLS encryption layer (default). +# 1 : accept both traditional and encrypted sessions. +# 2 : refuse connections that don't use SSL/TLS security mechanisms, +# including anonymous sessions. +# Do _not_ uncomment this blindly. Be sure that : +# 1) Your server has been compiled with SSL/TLS support (--with-tls), +# 2) A valid certificate is in place, +# 3) Only compatible clients will log in. + +# TLS 1 + + + +# Listen only to IPv4 addresses in standalone mode (ie. disable IPv6) +# By default, both IPv4 and IPv6 are enabled. + +# IPV4Only yes + + + +# Listen only to IPv6 addresses in standalone mode (ie. disable IPv4) +# By default, both IPv4 and IPv6 are enabled. + +# IPV6Only yes + +# UTF-8 support for file names (RFC 2640) +# Define charset of the server filesystem and optionnally the default charset +# for remote clients if they don't use UTF-8. +# Works only if pure-ftpd has been compiled with --with-rfc2640 + +# FileSystemCharset big5 +# ClientCharset big5 diff --git a/config/server.xml b/config/server.xml new file mode 100644 index 0000000..1ba0a98 --- /dev/null +++ b/config/server.xml @@ -0,0 +1,42 @@ + + +]> + + + + + + + + + + + + + + + + + &vhost-localhost; + + + diff --git a/config/thinkphp.conf b/config/thinkphp.conf new file mode 100644 index 0000000..47d387e --- /dev/null +++ b/config/thinkphp.conf @@ -0,0 +1,6 @@ +location / { + if (!-e $request_filename) { + rewrite ^(.*)$ /index.php?s=$1 last; + break; + } +} diff --git a/config/typecho.conf b/config/typecho.conf new file mode 100644 index 0000000..890a06d --- /dev/null +++ b/config/typecho.conf @@ -0,0 +1,5 @@ +location / { + if (!-e $request_filename) { + rewrite ^(.*)$ /index.php$1 last; + } +} diff --git a/config/whmcs.conf b/config/whmcs.conf new file mode 100644 index 0000000..3423145 --- /dev/null +++ b/config/whmcs.conf @@ -0,0 +1,39 @@ +location ~ /announcements/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/announcements/$1; +} + +location ~ /download/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/download$1; +} + +location ~ /knowledgebase/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/knowledgebase/$1; +} + +location ~ /store/ssl-certificates/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/store/ssl-certificates/$1; +} + +location ~ /store/sitelock/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/store/sitelock/$1; +} + +location ~ /store/website-builder/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/store/website-builder/$1; +} + +location ~ /store/order/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/store/order/$1; +} + +location ~ /cart/domain/renew/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/cart/domain/renew$1; +} + +location ~ /account/paymentmethods/?(.*)$ { + rewrite ^/(.*)$ /index.php?rp=/account/paymentmethods$1; +} + +location ~ /admin/(addons|apps|domains|help\/license|services|setup|utilities\/system\/php-compat)(.*) { + rewrite ^/(.*)$ /admin/index.php?rp=/admin/$1$2 last; +} diff --git a/config/wordpress.conf b/config/wordpress.conf new file mode 100644 index 0000000..bbf67b9 --- /dev/null +++ b/config/wordpress.conf @@ -0,0 +1,7 @@ +location / { + try_files $uri $uri/ /index.php?$args; +} +rewrite /wp-admin$ $scheme://$host$uri/ permanent; +location ~* ^/wp-content/uploads/.*\.php$ { + deny all; +} diff --git a/config/zblog.conf b/config/zblog.conf new file mode 100644 index 0000000..21f911d --- /dev/null +++ b/config/zblog.conf @@ -0,0 +1,11 @@ +location / { + if (-f $request_filename/index.html){ + rewrite (.*) $1/index.html break; + } + if (-f $request_filename/index.php){ + rewrite (.*) $1/index.php; + } + if (!-f $request_filename){ + rewrite (.*) /index.php; + } +} diff --git a/include/GraphicsMagick.sh b/include/GraphicsMagick.sh new file mode 100644 index 0000000..7b2c590 --- /dev/null +++ b/include/GraphicsMagick.sh @@ -0,0 +1,67 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_GraphicsMagick() { + if [ -d "${gmagick_install_dir}" ]; then + echo "${CWARNING}GraphicsMagick already installed! ${CEND}" + else + pushd ${oneinstack_dir}/src > /dev/null + tar xzf GraphicsMagick-${graphicsmagick_ver}.tar.gz + pushd GraphicsMagick-${graphicsmagick_ver} > /dev/null + ./configure --prefix=${gmagick_install_dir} --enable-shared --enable-static --enable-symbol-prefix + make -j ${THREAD} && make install + popd > /dev/null + rm -rf GraphicsMagick-${graphicsmagick_ver} + popd > /dev/null + fi +} + +Uninstall_GraphicsMagick() { + if [ -d "${gmagick_install_dir}" ]; then + rm -rf ${gmagick_install_dir} + echo; echo "${CMSG}GraphicsMagick uninstall completed${CEND}" + fi +} + +Install_pecl_gmagick() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=`${php_install_dir}/bin/php-config --extension-dir` + if [ "`${php_install_dir}/bin/php-config --version | awk -F. '{print $1}'`" == '5' ]; then + tar xzf gmagick-${gmagick_oldver}.tgz + pushd gmagick-${gmagick_oldver} > /dev/null + else + tar xzf gmagick-${gmagick_ver}.tgz + pushd gmagick-${gmagick_ver} > /dev/null + fi + export PKG_CONFIG_PATH=/usr/local/lib/pkgconfig + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config --with-gmagick=${gmagick_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/gmagick.so" ]; then + echo 'extension=gmagick.so' > ${php_install_dir}/etc/php.d/03-gmagick.ini + echo "${CSUCCESS}PHP gmagick module installed successfully! ${CEND}" + rm -rf gmagick-${gmagick_ver} gmagick-${gmagick_oldver} + else + echo "${CFAILURE}PHP gmagick module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_gmagick() { + if [ -e "${php_install_dir}/etc/php.d/03-gmagick.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/03-gmagick.ini + echo; echo "${CMSG}PHP gmagick module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP gmagick module does not exist! ${CEND}" + fi +} diff --git a/include/ImageMagick.sh b/include/ImageMagick.sh new file mode 100644 index 0000000..530372e --- /dev/null +++ b/include/ImageMagick.sh @@ -0,0 +1,74 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_ImageMagick() { + if [ -d "${imagick_install_dir}" ]; then + echo "${CWARNING}ImageMagick already installed! ${CEND}" + else + pushd ${oneinstack_dir}/src > /dev/null + tar xzf ImageMagick-${imagemagick_ver}.tar.gz + #if [ "${PM}" == 'yum' ]; then + # yum -y install libwebp-devel + #elif [ "${PM}" == 'apt-get' ]; then + # yum -y install libwebp-dev + #fi + pushd ImageMagick-${imagemagick_ver} > /dev/null + ./configure --prefix=${imagick_install_dir} --enable-shared --enable-static + make -j ${THREAD} && make install + popd > /dev/null + rm -rf ImageMagick-${imagemagick_ver} + popd > /dev/null + fi +} + +Uninstall_ImageMagick() { + if [ -d "${imagick_install_dir}" ]; then + rm -rf ${imagick_install_dir} + echo; echo "${CMSG}ImageMagick uninstall completed${CEND}" + fi +} + +Install_pecl_imagick() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + phpExtensionDir=`${php_install_dir}/bin/php-config --extension-dir` + if [[ "${PHP_main_ver}" =~ ^5.3$ ]]; then + tar xzf imagick-${imagick_oldver}.tgz + pushd imagick-${imagick_oldver} > /dev/null + else + tar xzf imagick-${imagick_ver}.tgz + pushd imagick-${imagick_ver} > /dev/null + fi + export PKG_CONFIG_PATH=/usr/local/lib/pkgconfig + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config --with-imagick=${imagick_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/imagick.so" ]; then + echo 'extension=imagick.so' > ${php_install_dir}/etc/php.d/03-imagick.ini + echo "${CSUCCESS}PHP imagick module installed successfully! ${CEND}" + rm -rf imagick-${imagick_ver} imagick-${imagick_oldver} + else + echo "${CFAILURE}PHP imagick module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_imagick() { + if [ -e "${php_install_dir}/etc/php.d/03-imagick.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/03-imagick.ini + echo; echo "${CMSG}PHP imagick module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP imagick module does not exist! ${CEND}" + fi +} diff --git a/include/ZendGuardLoader.sh b/include/ZendGuardLoader.sh new file mode 100644 index 0000000..5100e65 --- /dev/null +++ b/include/ZendGuardLoader.sh @@ -0,0 +1,70 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_ZendGuardLoader() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + phpExtensionDir=`${php_install_dir}/bin/php-config --extension-dir` + [ ! -d "${phpExtensionDir}" ] && mkdir -p ${phpExtensionDir} + if [ -n "`echo $phpExtensionDir | grep 'non-zts'`" ] && [ "${armplatform}" != 'y' ]; then + case "${PHP_main_ver}" in + 5.6) + tar xzf zend-loader-php5.6-linux-x86_64.tar.gz + /bin/mv zend-loader-php5.6-linux-x86_64/ZendGuardLoader.so ${phpExtensionDir} + rm -rf zend-loader-php5.6-linux-x86_64 + ;; + 5.5) + tar xzf zend-loader-php5.5-linux-x86_64.tar.gz + /bin/mv zend-loader-php5.5-linux-x86_64/ZendGuardLoader.so ${phpExtensionDir} + rm -rf zend-loader-php5.5-linux-x86_64 + ;; + 5.4) + tar xzf ZendGuardLoader-70429-PHP-5.4-linux-glibc23-x86_64.tar.gz + /bin/mv ZendGuardLoader-70429-PHP-5.4-linux-glibc23-x86_64/php-5.4.x/ZendGuardLoader.so ${phpExtensionDir} + rm -rf ZendGuardLoader-70429-PHP-5.4-linux-glibc23-x86_64 + ;; + 5.3) + tar xzf ZendGuardLoader-php-5.3-linux-glibc23-x86_64.tar.gz + /bin/mv ZendGuardLoader-php-5.3-linux-glibc23-x86_64/php-5.3.x/ZendGuardLoader.so ${phpExtensionDir} + rm -rf ZendGuardLoader-php-5.3-linux-glibc23-x86_64 + ;; + *) + echo "${CWARNING}Your php ${PHP_detail_ver} does not support ZendGuardLoader! ${CEND}"; + ;; + esac + + if [ -f "${phpExtensionDir}/ZendGuardLoader.so" ]; then + chmod 644 ${phpExtensionDir}/ZendGuardLoader.so + cat > ${php_install_dir}/etc/php.d/01-ZendGuardLoader.ini<< EOF +[Zend Guard Loader] +zend_extension=${phpExtensionDir}/ZendGuardLoader.so +zend_loader.enable=1 +zend_loader.disable_licensing=0 +zend_loader.obfuscation_level_support=3 +EOF + echo "${CSUCCESS}PHP ZendGuardLoader module installed successfully! ${CEND}" + fi + else + echo "Error! Your Apache's prefork or PHP already enable thread safety or platform ${TARGET_ARCH} does not support ZendGuardLoader! " + fi + popd > /dev/null + fi +} + +Uninstall_ZendGuardLoader() { + if [ -e "${php_install_dir}/etc/php.d/01-ZendGuardLoader.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/01-ZendGuardLoader.ini + echo; echo "${CMSG}PHP ZendGuardLoader module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP ZendGuardLoader module does not exist! ${CEND}" + fi +} diff --git a/include/apache.sh b/include/apache.sh new file mode 100644 index 0000000..3a11a4c --- /dev/null +++ b/include/apache.sh @@ -0,0 +1,190 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Apache() { + pushd ${oneinstack_dir}/src > /dev/null + tar xzf pcre-${pcre_ver}.tar.gz + pushd pcre-${pcre_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + tar xzf httpd-${apache_ver}.tar.gz + + # install apr + if [ ! -e "${apr_install_dir}/bin/apr-1-config" ]; then + tar xzf apr-${apr_ver}.tar.gz + pushd apr-${apr_ver} > /dev/null + ./configure --prefix=${apr_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf apr-${apr_ver} + fi + + # install apr-util + if [ ! -e "${apr_install_dir}/bin/apu-1-config" ]; then + tar xzf apr-util-${apr_util_ver}.tar.gz + pushd apr-util-${apr_util_ver} > /dev/null + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf apr-util-${apr_util_ver} + fi + + # install nghttp2 + if [ ! -e "/usr/local/lib/libnghttp2.so" ]; then + tar xzf nghttp2-${nghttp2_ver}.tar.gz + pushd nghttp2-${nghttp2_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + rm -rf nghttp2-${nghttp2_ver} + fi + + pushd httpd-${apache_ver} > /dev/null + LDFLAGS=-ldl ./configure --prefix=${apache_install_dir} --enable-mpms-shared=all --with-pcre --with-apr=${apr_install_dir} --with-apr-util=${apr_install_dir} --enable-headers --enable-mime-magic --enable-deflate --enable-proxy --enable-so --enable-dav --enable-rewrite --enable-remoteip --enable-expires --enable-static-support --enable-suexec --enable-mods-shared=most --enable-nonportable-atomics=yes --enable-ssl --with-ssl --enable-http2 --with-nghttp2=/usr/local + make -j ${THREAD} && make install + popd > /dev/null + unset LDFLAGS + if [ -e "${apache_install_dir}/bin/httpd" ]; then + echo "${CSUCCESS}Apache installed successfully! ${CEND}" + rm -rf httpd-${apache_ver} pcre-${pcre_ver} + else + rm -rf ${apache_install_dir} + echo "${CFAILURE}Apache install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${apache_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${apache_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${apache_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + /bin/cp ../init.d/httpd.service /lib/systemd/system/ + sed -i "s@/usr/local/apache@${apache_install_dir}@g" /lib/systemd/system/httpd.service + systemctl enable httpd + + sed -i "s@^User daemon@User ${run_user}@" ${apache_install_dir}/conf/httpd.conf + sed -i "s@^Group daemon@Group ${run_group}@" ${apache_install_dir}/conf/httpd.conf + if [[ ! ${nginx_option} =~ ^[1-3]$ ]] && [ ! -e "${web_install_dir}/sbin/nginx" ]; then + sed -i 's/^#ServerName www.example.com:80/ServerName 0.0.0.0:80/' ${apache_install_dir}/conf/httpd.conf + TMP_PORT=80 + elif [[ ${nginx_option} =~ ^[1-3]$ ]] || [ -e "${web_install_dir}/sbin/nginx" ]; then + sed -i 's/^#ServerName www.example.com:80/ServerName 127.0.0.1:88/' ${apache_install_dir}/conf/httpd.conf + sed -i 's@^Listen.*@Listen 127.0.0.1:88@' ${apache_install_dir}/conf/httpd.conf + TMP_PORT=88 + fi + sed -i "s@AddType\(.*\)Z@AddType\1Z\n AddType application/x-httpd-php .php .phtml\n AddType application/x-httpd-php-source .phps@" ${apache_install_dir}/conf/httpd.conf + sed -i "s@#AddHandler cgi-script .cgi@AddHandler cgi-script .cgi .pl@" ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_proxy.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_proxy_fcgi.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_suexec.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_vhost_alias.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_rewrite.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_deflate.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_expires.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_ssl.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -ri 's@^#(LoadModule.*mod_http2.so)@\1@' ${apache_install_dir}/conf/httpd.conf + sed -i 's@DirectoryIndex index.html@DirectoryIndex index.html index.php@' ${apache_install_dir}/conf/httpd.conf + sed -i "s@^DocumentRoot.*@DocumentRoot \"${wwwroot_dir}/default\"@" ${apache_install_dir}/conf/httpd.conf + sed -i "s@^@@" ${apache_install_dir}/conf/httpd.conf + sed -i "s@^#Include conf/extra/httpd-mpm.conf@Include conf/extra/httpd-mpm.conf@" ${apache_install_dir}/conf/httpd.conf + if [ "${apache_mpm_option}" == '2' ]; then + sed -ri 's@^(LoadModule.*mod_mpm_event.so)@#\1@' ${apache_install_dir}/conf/httpd.conf + sed -i 's@^#LoadModule mpm_prefork_module@LoadModule mpm_prefork_module@' ${apache_install_dir}/conf/httpd.conf + elif [ "${apache_mpm_option}" == '3' ]; then + sed -ri 's@^(LoadModule.*mod_mpm_event.so)@#\1@' ${apache_install_dir}/conf/httpd.conf + sed -i 's@^#LoadModule mpm_worker_module@LoadModule mpm_worker_module@' ${apache_install_dir}/conf/httpd.conf + fi + + #logrotate apache log + cat > /etc/logrotate.d/apache << EOF +${wwwlogs_dir}/*apache.log { + daily + rotate 5 + missingok + dateext + compress + notifempty + sharedscripts + postrotate + [ -e /var/run/httpd.pid ] && kill -USR1 \`cat /var/run/httpd.pid\` + endscript +} +EOF + + mkdir ${apache_install_dir}/conf/vhost + [ "${apache_mode_option}" != '2' ] && Apache_fcgi=$(echo -e "\n Order allow,deny\n Deny from all\n \n \n SetHandler \"proxy:unix:/dev/shm/php-cgi.sock|fcgi://localhost\"\n ") + cat > ${apache_install_dir}/conf/vhost/0.conf << EOF + + ServerAdmin admin@example.com + DocumentRoot "${wwwroot_dir}/default" + ServerName 127.0.0.1 + ErrorLog "${wwwlogs_dir}/error_apache.log" + CustomLog "${wwwlogs_dir}/access_apache.log" common + + Order allow,deny + Deny from all + + ${Apache_fcgi} + + SetOutputFilter DEFLATE + Options FollowSymLinks ExecCGI + Require all granted + AllowOverride All + Order allow,deny + Allow from all + DirectoryIndex index.html index.php + + + SetHandler server-status + Order Deny,Allow + Deny from all + Allow from 127.0.0.1 + + +EOF + + cat >> ${apache_install_dir}/conf/httpd.conf < + AddOutputFilterByType DEFLATE text/html text/plain text/css text/xml text/javascript + + RequestHeader edit "If-None-Match" "^(.*)-gzip(.*)\$" "\$1\$2" + Header edit "ETag" "^(.*)-gzip(.*)\$" "\$1\$2" + + DeflateCompressionLevel 6 + SetOutputFilter DEFLATE + + +ProtocolsHonorOrder On +PidFile /var/run/httpd.pid +ServerTokens ProductOnly +ServerSignature Off +Include conf/vhost/*.conf +EOF + [ "${nginx_option}" == '4' -a ! -e "${web_install_dir}/sbin/nginx" ] && echo 'Protocols h2 http/1.1' >> ${apache_install_dir}/conf/httpd.conf + if [ "${nginx_option}" != '4' -o -e "${web_install_dir}/sbin/nginx" ]; then + cat > ${apache_install_dir}/conf/extra/httpd-remoteip.conf << EOF +LoadModule remoteip_module modules/mod_remoteip.so +RemoteIPHeader X-Forwarded-For +RemoteIPInternalProxy 127.0.0.1 +EOF + sed -i "s@Include conf/extra/httpd-mpm.conf@Include conf/extra/httpd-mpm.conf\nInclude conf/extra/httpd-remoteip.conf@" ${apache_install_dir}/conf/httpd.conf + sed -i "s@LogFormat \"%h %l@LogFormat \"%h %a %l@g" ${apache_install_dir}/conf/httpd.conf + fi + ldconfig + [ "${with_old_openssl_flag}" == 'y' ] && sed -i "s@^export LD_LIBRARY_PATH.*@export LD_LIBRARY_PATH=${openssl_install_dir}/lib:\$LD_LIBRARY_PATH@" ${apache_install_dir}/bin/envvars + systemctl start httpd + popd > /dev/null +} diff --git a/include/apcu.sh b/include/apcu.sh new file mode 100644 index 0000000..7a4217a --- /dev/null +++ b/include/apcu.sh @@ -0,0 +1,52 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_APCU() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=`${php_install_dir}/bin/php-config --extension-dir` + if [ "`${php_install_dir}/bin/php-config --version | awk -F. '{print $1}'`" == '5' ]; then + tar xzf apcu-${apcu_oldver}.tgz + pushd apcu-${apcu_oldver} > /dev/null + else + tar xzf apcu-${apcu_ver}.tgz + pushd apcu-${apcu_ver} > /dev/null + fi + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + if [ -f "${phpExtensionDir}/apcu.so" ]; then + cat > ${php_install_dir}/etc/php.d/02-apcu.ini << EOF +[apcu] +extension=apcu.so +apc.enabled=1 +apc.shm_size=32M +apc.ttl=7200 +apc.enable_cli=1 +EOF + /bin/cp apc.php ${wwwroot_dir}/default + popd > /dev/null + echo "${CSUCCESS}PHP apcu module installed successfully! ${CEND}" + rm -rf apcu-${apcu_ver} apcu-${apcu_oldver} package.xml + else + echo "${CFAILURE}PHP apcu module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_APCU() { + if [ -e "${php_install_dir}/etc/php.d/02-apcu.ini" ]; then + rm -rf ${php_install_dir}/etc/php.d/02-apcu.ini ${wwwroot_dir}/default/apc.php + echo; echo "${CMSG}PHP apcu module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP apcu module does not exist! ${CEND}" + fi +} diff --git a/include/caddy.sh b/include/caddy.sh new file mode 100644 index 0000000..a33210d --- /dev/null +++ b/include/caddy.sh @@ -0,0 +1,55 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Caddy() { + + pushd ${oneinstack_dir}/src > /dev/null + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + #unzip caddy_${caddy_ver}_linux_amd64.zip + tar xzf caddy-${caddy_ver}.tar.gz + + #move caddy to /usr/local/caddy/bin + [ ! -d "${caddy_install_dir}/bin" ] && mkdir -p ${caddy_install_dir}/bin + /bin/cp caddy ${caddy_install_dir}/bin + + chmod +x ${caddy_install_dir}/bin/caddy + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${caddy_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${caddy_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${caddy_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + #make soft link + # [ ! -L "/usr/local/bin/caddy" ] && ln -s ${caddy_install_dir}/bin/caddy /usr/local/bin/caddy + + #move caddyfile to /usr/local/caddy/conf + [ ! -d "${caddy_install_dir}/conf" ] && mkdir -p ${caddy_install_dir}/conf + /bin/cp ../config/Caddyfile ${caddy_install_dir}/conf/ + + #move caddy.service to /lib/systemd/system + /bin/cp ../init.d/caddy.service /lib/systemd/system/ + + #modify caddy.service + sed -i "s@/usr/local/caddy@${caddy_install_dir}@g" /lib/systemd/system/caddy.service + + #设置caddy开机启动 + systemctl enable caddy + + #reload systemd + systemctl daemon-reload + + #start caddy service + systemctl start caddy + + echo "${CSUCCESS}Caddy installed successfully! ${CEND}" +} diff --git a/include/check_dir.sh b/include/check_dir.sh new file mode 100644 index 0000000..5c4e6d5 --- /dev/null +++ b/include/check_dir.sh @@ -0,0 +1,19 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +# check MySQL dir +[ -d "${mysql_install_dir}/support-files" ] && { db_install_dir=${mysql_install_dir}; db_data_dir=${mysql_data_dir}; } +[ -d "${mariadb_install_dir}/support-files" ] && { db_install_dir=${mariadb_install_dir}; db_data_dir=${mariadb_data_dir}; } +[ -d "${percona_install_dir}/support-files" ] && { db_install_dir=${percona_install_dir}; db_data_dir=${percona_data_dir}; } + +# check Nginx dir +[ -e "${nginx_install_dir}/sbin/nginx" ] && web_install_dir=${nginx_install_dir} +[ -e "${tengine_install_dir}/sbin/nginx" ] && web_install_dir=${tengine_install_dir} +[ -e "${openresty_install_dir}/nginx/sbin/nginx" ] && web_install_dir=${openresty_install_dir}/nginx diff --git a/include/check_download.sh b/include/check_download.sh new file mode 100644 index 0000000..af1d77e --- /dev/null +++ b/include/check_download.sh @@ -0,0 +1,739 @@ +#!/bin/bash +# Author: Alpha Eva +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +checkDownload() { + pushd ${oneinstack_dir}/src > /dev/null + # icu + if ! command -v icu-config >/dev/null 2>&1 || icu-config --version | grep '^3.' || [ "${Ubuntu_ver}" == "20" ]; then + echo "Download icu..." + src_url=${mirror_link}/oneinstack/src/icu4c-${icu4c_ver}-src.tgz && Download_src + fi + + # General system utils + if [ "${with_old_openssl_flag}" == 'y' ]; then + echo "Download openSSL..." + src_url=${mirror_link}/oneinstack/src/openssl-${openssl_ver}.tar.gz && Download_src + echo "Download cacert.pem..." + src_url=https://curl.se/ca/cacert.pem && Download_src + fi + + # openssl1.1 + if [[ ${nginx_option} =~ ^[1-3]$ ]]; then + echo "Download openSSL1.1..." + src_url=${mirror_link}/oneinstack/src/openssl-${openssl11_ver}.tar.gz && Download_src + fi + + # jemalloc + if [[ ${nginx_option} =~ ^[1-3]$ ]] || [[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]]; then + echo "Download jemalloc..." + src_url=${mirror_link}/oneinstack/src/jemalloc-${jemalloc_ver}.tar.bz2 && Download_src + fi + + # pcre + if [[ "${nginx_option}" =~ ^[1-3]$ ]] || [ "${apache_flag}" == 'y' ]; then + echo "Download pcre..." + src_url=${mirror_link}/oneinstack/src/pcre-${pcre_ver}.tar.gz && Download_src + fi + + # nginx/tengine/openresty + case "${nginx_option}" in + 1) + echo "Download nginx..." + src_url=${mirror_link}/oneinstack/src/nginx-${nginx_ver}.tar.gz && Download_src + ;; + 2) + echo "Download tengine..." + #src_url=http://tengine.taobao.org/download/tengine-${tengine_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/tengine-${tengine_ver}.tar.gz && Download_src + ;; + 3) + echo "Download openresty..." + src_url=${mirror_link}/oneinstack/src/openresty-${openresty_ver}.tar.gz && Download_src + ;; + esac + + # if nginx_option=4 download caddy + if [ "${nginx_option}" == '4' ]; then + echo "Download caddy ${caddy_ver}" + src_url=${mirror_link}/caddy/v${caddy_ver}/caddy-${caddy_ver}.tar.gz && Download_src + fi + + # caddy + if [ "${caddy_flag}" == 'y' ]; then + echo "Download caddy ${caddy_ver}" + src_url=${mirror_link}/caddy/v${caddy_ver}/caddy-${caddy_ver}.tar.gz && Download_src + fi + + # apache + if [ "${apache_flag}" == 'y' ]; then + echo "Download apache 2.4..." + src_url=http://archive.apache.org/dist/httpd/httpd-${apache_ver}.tar.gz && Download_src + src_url=http://archive.apache.org/dist/apr/apr-${apr_ver}.tar.gz && Download_src + src_url=http://archive.apache.org/dist/apr/apr-util-${apr_util_ver}.tar.gz && Download_src + src_url=${mirror_link}/apache/httpd/nghttp2-${nghttp2_ver}.tar.gz && Download_src + fi + + # tomcat + case "${tomcat_option}" in + 1) + echo "Download tomcat 10..." + src_url=${mirror_link}/apache/tomcat/v${tomcat10_ver}/apache-tomcat-${tomcat10_ver}.tar.gz && Download_src + ;; + 2) + echo "Download tomcat 9..." + src_url=${mirror_link}/apache/tomcat/v${tomcat9_ver}/apache-tomcat-${tomcat9_ver}.tar.gz && Download_src + ;; + 3) + echo "Download tomcat 8..." + src_url=${mirror_link}/apache/tomcat/v${tomcat8_ver}/apache-tomcat-${tomcat8_ver}.tar.gz && Download_src + ;; + 4) + echo "Download tomcat 7..." + src_url=${mirror_link}/apache/tomcat/v${tomcat7_ver}/apache-tomcat-${tomcat7_ver}.tar.gz && Download_src + src_url=${mirror_link}/apache/tomcat/v${tomcat7_ver}/catalina-jmx-remote.jar && Download_src + ;; + esac + + # jdk apr + if [[ "${jdk_option}" =~ ^[1-2]$ ]]; then + echo "Download apr..." + src_url=http://archive.apache.org/dist/apr/apr-${apr_ver}.tar.gz && Download_src + fi + + if [[ "${db_option}" =~ ^[1-9]$|^1[0-4]$ ]]; then + if [[ "${db_option}" =~ ^[1,2,5,6,7,9]$|^10$ ]] && [ "${dbinstallmethod}" == "2" ]; then + [[ "${db_option}" =~ ^[2,5,6,7]$|^10$ ]] && boost_ver=${boost_oldver} + [[ "${db_option}" =~ ^9$ ]] && boost_ver=${boost_percona_ver} + echo "Download boost..." + [ "${OUTIP_STATE}"x == "China"x ] && DOWN_ADDR_BOOST=${mirror_link}/oneinstack/src || DOWN_ADDR_BOOST=https://downloads.sourceforge.net/project/boost/boost/${boost_ver} + boostVersion2=$(echo ${boost_ver} | awk -F. '{print $1"_"$2"_"$3}') + src_url=${DOWN_ADDR_BOOST}/boost_${boostVersion2}.tar.gz && Download_src + fi + + case "${db_option}" in + 1) + # MySQL 8.0 + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_MYSQL=https://cdn.mysql.com/Downloads/MySQL-8.0 + DOWN_ADDR_MYSQL_BK=https://mirrors.aliyun.com/mysql/MySQL-8.0 + DOWN_ADDR_MYSQL_BK2=http://mirrors.tuna.tsinghua.edu.cn/mysql/downloads/MySQL-8.0 + else + DOWN_ADDR_MYSQL=https://cdn.mysql.com/Downloads/MySQL-8.0 + DOWN_ADDR_MYSQL_BK=https://mirrors.dotsrc.org/mysql/Downloads/MySQL-8.0 + fi + + if [ "${dbinstallmethod}" == '1' ]; then + echo "Download MySQL 8.0 binary package..." + FILE_NAME=mysql-${mysql80_ver}-linux-glibc2.12-x86_64.tar.xz + elif [ "${dbinstallmethod}" == '2' ]; then + echo "Download MySQL 8.0 source package..." + FILE_NAME=mysql-${mysql80_ver}.tar.gz + fi + # start download + src_url=${DOWN_ADDR_MYSQL}/${FILE_NAME} && Download_src + src_url=${DOWN_ADDR_MYSQL}/${FILE_NAME}.md5 && Download_src + # verifying download + MYSQL_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5) + [ -z "${MYSQL_TAR_MD5}" ] && MYSQL_TAR_MD5=$(curl -s ${DOWN_ADDR_MYSQL_BK}/${FILE_NAME}.md5 | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${MYSQL_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_MYSQL_BK}/${FILE_NAME};sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${MYSQL_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 2) + # MySQL 5.7 + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_MYSQL=https://cdn.mysql.com/Downloads/MySQL-5.7 + DOWN_ADDR_MYSQL_BK=https://mirrors.aliyun.com/mysql/MySQL-5.7 + DOWN_ADDR_MYSQL_BK2=http://mirrors.tuna.tsinghua.edu.cn/mysql/downloads/MySQL-5.7 + else + DOWN_ADDR_MYSQL=https://cdn.mysql.com/Downloads/MySQL-5.7 + DOWN_ADDR_MYSQL_BK=https://mirrors.dotsrc.org/mysql/Downloads/MySQL-5.7 + fi + + if [ "${dbinstallmethod}" == '1' ]; then + echo "Download MySQL 5.7 binary package..." + FILE_NAME=mysql-${mysql57_ver}-linux-glibc2.12-x86_64.tar.gz + elif [ "${dbinstallmethod}" == '2' ]; then + echo "Download MySQL 5.7 source package..." + FILE_NAME=mysql-${mysql57_ver}.tar.gz + fi + # start download + src_url=${DOWN_ADDR_MYSQL}/${FILE_NAME} && Download_src + src_url=${DOWN_ADDR_MYSQL}/${FILE_NAME}.md5 && Download_src + # verifying download + MYSQL_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5) + [ -z "${MYSQL_TAR_MD5}" ] && MYSQL_TAR_MD5=$(curl -s ${DOWN_ADDR_MYSQL_BK}/${FILE_NAME}.md5 | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${MYSQL_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_MYSQL_BK}/${FILE_NAME};sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${MYSQL_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 3) + # MySQL 5.6 + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_MYSQL=http://mirrors.aliyun.com/mysql/MySQL-5.6 + DOWN_ADDR_MYSQL_BK=http://mirrors.tuna.tsinghua.edu.cn/mysql/downloads/MySQL-5.6 + DOWN_ADDR_MYSQL_BK2=https://mirrors.aliyun.com/mysql/MySQL-5.6 + else + DOWN_ADDR_MYSQL=https://cdn.mysql.com/Downloads/MySQL-5.6 + DOWN_ADDR_MYSQL_BK=https://mirrors.dotsrc.org/mysql/Downloads/MySQL-5.6 + fi + + if [ "${dbinstallmethod}" == '1' ]; then + echo "Download MySQL 5.6 binary package..." + FILE_NAME=mysql-${mysql56_ver}-linux-glibc2.12-x86_64.tar.gz + elif [ "${dbinstallmethod}" == '2' ]; then + echo "Download MySQL 5.6 source package..." + FILE_NAME=mysql-${mysql56_ver}.tar.gz + fi + # start download + src_url=${DOWN_ADDR_MYSQL}/${FILE_NAME} && Download_src + src_url=${DOWN_ADDR_MYSQL}/${FILE_NAME}.md5 && Download_src + # verifying download + MYSQL_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5) + [ -z "${MYSQL_TAR_MD5}" ] && MYSQL_TAR_MD5=$(curl -s ${DOWN_ADDR_MYSQL_BK}/${FILE_NAME}.md5 | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${MYSQL_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_MYSQL_BK}/${FILE_NAME};sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${MYSQL_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 4) + # MySQL 5.5 + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_MYSQL=http://mirrors.aliyun.com/mysql/MySQL-5.5 + DOWN_ADDR_MYSQL_BK=http://mirrors.tuna.tsinghua.edu.cn/mysql/downloads/MySQL-5.5 + DOWN_ADDR_MYSQL_BK2=https://mirrors.aliyun.com/mysql/MySQL-5.5 + else + DOWN_ADDR_MYSQL=https://cdn.mysql.com/Downloads/MySQL-5.5 + DOWN_ADDR_MYSQL_BK=https://mirrors.dotsrc.org/mysql/Downloads/MySQL-5.5 + fi + + if [ "${dbinstallmethod}" == '1' ]; then + echo "Download MySQL 5.5 binary package..." + FILE_NAME=mysql-${mysql55_ver}-linux-glibc2.12-x86_64.tar.gz + elif [ "${dbinstallmethod}" == '2' ]; then + echo "Download MySQL 5.5 source package..." + FILE_NAME=mysql-${mysql55_ver}.tar.gz + src_url=${mirror_link}/oneinstack/src/mysql-5.5-fix-arm-client_plugin.patch && Download_src + fi + # start download + src_url=${DOWN_ADDR_MYSQL}/${FILE_NAME} && Download_src + src_url=${DOWN_ADDR_MYSQL}/${FILE_NAME}.md5 && Download_src + # verifying download + MYSQL_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5) + [ -z "${MYSQL_TAR_MD5}" ] && MYSQL_TAR_MD5=$(curl -s ${DOWN_ADDR_MYSQL_BK}/${FILE_NAME}.md5 | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${MYSQL_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_MYSQL_BK}/${FILE_NAME};sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${MYSQL_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + [5-8]) + case "${db_option}" in + 5) + mariadb_ver=${mariadb1011_ver} + ;; + 6) + mariadb_ver=${mariadb105_ver} + ;; + 7) + mariadb_ver=${mariadb104_ver} + ;; + 8) + mariadb_ver=${mariadb55_ver} + ;; + esac + + if [ "${dbinstallmethod}" == '1' ]; then + FILE_NAME=mariadb-${mariadb_ver}-linux-systemd-x86_64.tar.gz + FILE_TYPE=bintar-linux-systemd-x86_64 + elif [ "${dbinstallmethod}" == '2' ]; then + FILE_NAME=mariadb-${mariadb_ver}.tar.gz + FILE_TYPE=source + fi + + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_MARIADB=https://mirrors.xtom.com.hk/mariadb/mariadb-${mariadb_ver}/${FILE_TYPE} + DOWN_ADDR_MARIADB_BK=http://mirrors.ustc.edu.cn/mariadb/mariadb-${mariadb_ver}/${FILE_TYPE} + else + DOWN_ADDR_MARIADB=https://mirrors.xtom.com.hk/mariadb/mariadb-${mariadb_ver}/${FILE_TYPE} + DOWN_ADDR_MARIADB_BK=http://mirror.nodesdirect.com/mariadb/mariadb-${mariadb_ver}/${FILE_TYPE} + fi + + if [ "${db_option}" == '8' ]; then + DOWN_ADDR_MARIADB=https://archive.mariadb.org/mariadb-${mariadb_ver}/${FILE_TYPE} + DOWN_ADDR_MARIADB_BK=${DOWN_ADDR_MARIADB} + fi + + echo "Download MariaDB ${FILE_NAME} package..." + src_url=${DOWN_ADDR_MARIADB}/${FILE_NAME} && Download_src + wget --tries=6 -c --no-check-certificate ${DOWN_ADDR_MARIADB}/md5sums.txt -O ${FILE_NAME}.md5 + MARAIDB_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5) + [ -z "${MARAIDB_TAR_MD5}" ] && MARAIDB_TAR_MD5=$(curl -s ${DOWN_ADDR_MARIADB_BK}/md5sums.txt | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${MARAIDB_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_MARIADB_BK}/${FILE_NAME};sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${MARAIDB_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 9) + # Percona 8.0 + if [ "${dbinstallmethod}" == '1' ]; then + echo "Download Percona 8.0 binary package..." + FILE_NAME=Percona-Server-${percona80_ver}-Linux.x86_64.glibc2.28.tar.gz + DOWN_ADDR_PERCONA=https://downloads.percona.com/downloads/Percona-Server-8.0/Percona-Server-${percona80_ver}/binary/tarball + elif [ "${dbinstallmethod}" == '2' ]; then + echo "Download Percona 8.0 source package..." + FILE_NAME=percona-server-${percona80_ver}.tar.gz + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_PERCONA=${mirror_link}/oneinstack/src + else + DOWN_ADDR_PERCONA=https://downloads.percona.com/downloads/Percona-Server-8.0/Percona-Server-${percona80_ver}/source/tarball + fi + fi + # start download + src_url=${DOWN_ADDR_PERCONA}/${FILE_NAME} && Download_src + src_url=${mirror_link}/oneinstack/src/${FILE_NAME}.md5sum && Download_src + # verifying download + PERCONA_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5sum) + [ -z "${PERCONA_TAR_MD5}" ] && PERCONA_TAR_MD5=$(curl -s ${mirror_link}/oneinstack/src/${FILE_NAME}.md5sum | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${PERCONA_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_PERCONA}/${FILE_NAME}; sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${PERCONA_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 10) + # Precona 5.7 + if [ "${dbinstallmethod}" == '1' ]; then + echo "Download Percona 5.7 binary package..." + FILE_NAME=Percona-Server-${percona57_ver}-Linux.x86_64.glibc2.17.tar.gz + DOWN_ADDR_PERCONA=https://downloads.percona.com/downloads/Percona-Server-5.7/Percona-Server-${percona57_ver}/binary/tarball + elif [ "${dbinstallmethod}" == '2' ]; then + echo "Download Percona 5.7 source package..." + FILE_NAME=percona-server-${percona57_ver}.tar.gz + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_PERCONA=${mirror_link}/oneinstack/src + else + DOWN_ADDR_PERCONA=https://downloads.percona.com/downloads/Percona-Server-5.7/Percona-Server-${percona57_ver}/source/tarball + fi + fi + # start download + src_url=${DOWN_ADDR_PERCONA}/${FILE_NAME} && Download_src + src_url=${mirror_link}/oneinstack/src/${FILE_NAME}.md5sum && Download_src + # verifying download + PERCONA_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5sum) + [ -z "${PERCONA_TAR_MD5}" ] && PERCONA_TAR_MD5=$(curl -s ${mirror_link}/oneinstack/src/${FILE_NAME}.md5sum | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${PERCONA_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_PERCONA}/${FILE_NAME}; sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${PERCONA_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 11) + # Precona 5.6 + if [ "${dbinstallmethod}" == '1' ]; then + echo "Download Percona 5.6 binary package..." + perconaVerStr1=$(echo ${percona56_ver} | sed "s@-@-rel@") + FILE_NAME=Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer}.tar.gz + DOWN_ADDR_PERCONA=https://downloads.percona.com/downloads/Percona-Server-5.6/Percona-Server-${percona56_ver}/binary/tarball + elif [ "${dbinstallmethod}" == '2' ]; then + echo "Download Percona 5.6 source package..." + FILE_NAME=percona-server-${percona56_ver}.tar.gz + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_PERCONA=${mirror_link}/oneinstack/src + else + DOWN_ADDR_PERCONA=https://downloads.percona.com/downloads/Percona-Server-5.6/Percona-Server-${percona56_ver}/source/tarball + fi + fi + # start download + src_url=${DOWN_ADDR_PERCONA}/${FILE_NAME} && Download_src + src_url=${mirror_link}/oneinstack/src/${FILE_NAME}.md5sum && Download_src + # verifying download + PERCONA_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5sum) + [ -z "${PERCONA_TAR_MD5}" ] && PERCONA_TAR_MD5=$(curl -s ${mirror_link}/oneinstack/src/${FILE_NAME}.md5sum | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${PERCONA_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_PERCONA}/${FILE_NAME}; sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${PERCONA_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 12) + # Percona 5.5 + if [ "${dbinstallmethod}" == '1' ]; then + echo "Download Percona 5.5 binary package..." + perconaVerStr1=$(echo ${percona55_ver} | sed "s@-@-rel@") + FILE_NAME=Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer}.tar.gz + DOWN_ADDR_PERCONA=https://downloads.percona.com/downloads/Percona-Server-5.5/Percona-Server-${percona55_ver}/binary/tarball + elif [ "${dbinstallmethod}" == '2' ]; then + echo "Download Percona 5.5 source package..." + FILE_NAME=percona-server-${percona55_ver}.tar.gz + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_PERCONA=${mirror_link}/oneinstack/src + else + DOWN_ADDR_PERCONA=https://downloads.percona.com/downloads/Percona-Server-5.5/Percona-Server-${percona55_ver}/source/tarball + fi + fi + # start download + src_url=${DOWN_ADDR_PERCONA}/${FILE_NAME} && Download_src + src_url=${mirror_link}/oneinstack/src/${FILE_NAME}.md5sum && Download_src + # verifying download + PERCONA_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5sum) + [ -z "${PERCONA_TAR_MD5}" ] && PERCONA_TAR_MD5=$(curl -s ${mirror_link}/oneinstack/src/${FILE_NAME}.md5sum | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${PERCONA_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_PERCONA}/${FILE_NAME}; sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${PERCONA_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 13) + FILE_NAME=postgresql-${pgsql_ver}.tar.gz + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_PGSQL=https://mirrors.tuna.tsinghua.edu.cn/postgresql/source/v${pgsql_ver} + DOWN_ADDR_PGSQL_BK=https://mirrors.ustc.edu.cn/postgresql/source/v${pgsql_ver} + else + DOWN_ADDR_PGSQL=https://ftp.postgresql.org/pub/source/v${pgsql_ver} + DOWN_ADDR_PGSQL_BK=https://ftp.heanet.ie/mirrors/postgresql/source/v${pgsql_ver} + fi + src_url=${DOWN_ADDR_PGSQL}/${FILE_NAME} && Download_src + src_url=${DOWN_ADDR_PGSQL}/${FILE_NAME}.md5 && Download_src + PGSQL_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5) + [ -z "${PGSQL_TAR_MD5}" ] && PGSQL_TAR_MD5=$(curl -s ${DOWN_ADDR_PGSQL_BK}/${FILE_NAME}.md5 | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${PGSQL_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_PGSQL_BK}/${FILE_NAME};sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${PGSQL_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + 14) + # MongoDB + echo "Download MongoDB binary package..." + FILE_NAME=mongodb-linux-x86_64-${mongodb_ver}.tgz + if [ "${OUTIP_STATE}"x == "China"x ]; then + DOWN_ADDR_MongoDB=${mirror_link}/oneinstack/src + else + DOWN_ADDR_MongoDB=https://fastdl.mongodb.org/linux + fi + src_url=${DOWN_ADDR_MongoDB}/${FILE_NAME} && Download_src + src_url=${DOWN_ADDR_MongoDB}/${FILE_NAME}.md5 && Download_src + MongoDB_TAR_MD5=$(awk '{print $1}' ${FILE_NAME}.md5) + [ -z "${MongoDB_TAR_MD5}" ] && MongoDB_TAR_MD5=$(curl -s ${DOWN_ADDR_MongoDB}/${FILE_NAME}.md5 | grep ${FILE_NAME} | awk '{print $1}') + tryDlCount=0 + while [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" != "${MongoDB_TAR_MD5}" ]; do + wget -c --no-check-certificate ${DOWN_ADDR_MongoDB}/${FILE_NAME};sleep 1 + let "tryDlCount++" + [ "$(md5sum ${FILE_NAME} | awk '{print $1}')" == "${MongoDB_TAR_MD5}" -o "${tryDlCount}" == '6' ] && break || continue + done + if [ "${tryDlCount}" == '6' ]; then + echo "${CFAILURE}${FILE_NAME} download failed, Please contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + ;; + esac + fi + + # PHP + if [[ "${php_option}" =~ ^[1-9]$|^1[0-3]$ ]] || [[ "${mphp_ver}" =~ ^5[3-6]$|^7[0-4]$|^8[0-3]$ ]]; then + echo "PHP common..." + src_url=${mirror_link}/oneinstack/src/libiconv-${libiconv_ver}.tar.gz && Download_src + src_url=https://curl.haxx.se/download/curl-${curl_ver}.tar.gz && Download_src + src_url=https://downloads.sourceforge.net/project/mhash/mhash/${mhash_ver}/mhash-${mhash_ver}.tar.gz && Download_src + src_url=https://downloads.sourceforge.net/project/mcrypt/Libmcrypt/${libmcrypt_ver}/libmcrypt-${libmcrypt_ver}.tar.gz && Download_src + src_url=https://downloads.sourceforge.net/project/mcrypt/MCrypt/${mcrypt_ver}/mcrypt-${mcrypt_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/freetype-${freetype_ver}.tar.gz && Download_src + fi + + if [ "${php_option}" == '1' ] || [ "${mphp_ver}" == '53' ]; then + src_url=${mirror_link}/oneinstack/src/debian_patches_disable_SSLv2_for_openssl_1_0_0.patch && Download_src + src_url=${mirror_link}/oneinstack/src/php5.3patch && Download_src + src_url=https://secure.php.net/distributions/php-${php53_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/fpm-race-condition.patch && Download_src + elif [ "${php_option}" == '2' ] || [ "${mphp_ver}" == '54' ]; then + src_url=https://secure.php.net/distributions/php-${php54_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/fpm-race-condition.patch && Download_src + elif [ "${php_option}" == '3' ] || [ "${mphp_ver}" == '55' ]; then + src_url=https://secure.php.net/distributions/php-${php55_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/fpm-race-condition.patch && Download_src + elif [ "${php_option}" == '4' ] || [ "${mphp_ver}" == '56' ]; then + src_url=https://secure.php.net/distributions/php-${php56_ver}.tar.gz && Download_src + elif [ "${php_option}" == '5' ] || [ "${mphp_ver}" == '70' ]; then + src_url=https://secure.php.net/distributions/php-${php70_ver}.tar.gz && Download_src + elif [ "${php_option}" == '6' ] || [ "${mphp_ver}" == '71' ]; then + src_url=https://secure.php.net/distributions/php-${php71_ver}.tar.gz && Download_src + elif [ "${php_option}" == '7' ] || [ "${mphp_ver}" == '72' ]; then + src_url=${mirror_link}/oneinstack/src/php-${php72_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/argon2-${argon2_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libsodium-${libsodium_ver}.tar.gz && Download_src + elif [ "${php_option}" == '8' ] || [ "${mphp_ver}" == '73' ]; then + src_url=${mirror_link}/oneinstack/src/php-${php73_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/argon2-${argon2_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libsodium-${libsodium_ver}.tar.gz && Download_src + elif [ "${php_option}" == '9' ] || [ "${mphp_ver}" == '74' ]; then + src_url=${mirror_link}/oneinstack/src/php-${php74_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/argon2-${argon2_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libsodium-${libsodium_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libzip-${libzip_ver}.tar.gz && Download_src + elif [ "${php_option}" == '10' ] || [ "${mphp_ver}" == '80' ]; then + src_url=${mirror_link}/oneinstack/src/php-${php80_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/argon2-${argon2_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libsodium-${libsodium_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libzip-${libzip_ver}.tar.gz && Download_src + elif [ "${php_option}" == '11' ] || [ "${mphp_ver}" == '81' ]; then + src_url=${mirror_link}/oneinstack/src/php-${php81_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/argon2-${argon2_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libsodium-${libsodium_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libzip-${libzip_ver}.tar.gz && Download_src + elif [ "${php_option}" == '12' ] || [ "${mphp_ver}" == '82' ]; then + src_url=${mirror_link}/oneinstack/src/php-${php82_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/argon2-${argon2_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libsodium-${libsodium_up_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libzip-${libzip_ver}.tar.gz && Download_src + elif [ "${php_option}" == '13' ] || [ "${mphp_ver}" == '83' ]; then + src_url=${mirror_link}/oneinstack/src/php-${php83_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/argon2-${argon2_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libsodium-${libsodium_up_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/libzip-${libzip_ver}.tar.gz && Download_src + fi + + # PHP OPCache + case "${phpcache_option}" in + 1) + if [[ "${php_option}" =~ ^[1-2]$ ]]; then + # php 5.3 5.4 + echo "Download Zend OPCache..." + src_url=https://pecl.php.net/get/zendopcache-${zendopcache_ver}.tgz && Download_src + fi + ;; + 2) + echo "Download apcu..." + if [[ "${php_option}" =~ ^[1-4]$ ]]; then + src_url=https://pecl.php.net/get/apcu-${apcu_oldver}.tgz && Download_src + else + src_url=https://pecl.php.net/get/apcu-${apcu_ver}.tgz && Download_src + fi + ;; + 3) + if [[ "${php_option}" =~ ^[1-4]$ ]]; then + # php 5.3 5.4 5.5 5.6 + echo "Download xcache..." + src_url=http://xcache.lighttpd.net/pub/Releases/${xcache_ver}/xcache-${xcache_ver}.tar.gz && Download_src + fi + ;; + 4) + # php 5.3 5.4 + if [ "${php_option}" == '1' ]; then + echo "Download eaccelerator 0.9..." + src_url=https://github.com/downloads/eaccelerator/eaccelerator/eaccelerator-${eaccelerator_ver}.tar.bz2 && Download_src + elif [ "${php_option}" == '2' ]; then + echo "Download eaccelerator 1.0 dev..." + src_url=https://github.com/eaccelerator/eaccelerator/tarball/master && Download_src + fi + ;; + esac + + # Zend Guard Loader + if [ "${pecl_zendguardloader}" == '1' -a "${armplatform}" != 'y' ]; then + case "${php_option}" in + 4) + echo "Download zend loader for php 5.6..." + src_url=${mirror_link}/oneinstack/src/zend-loader-php5.6-linux-x86_64.tar.gz && Download_src + ;; + 3) + echo "Download zend loader for php 5.5..." + src_url=${mirror_link}/oneinstack/src/zend-loader-php5.5-linux-x86_64.tar.gz && Download_src + ;; + 2) + echo "Download zend loader for php 5.4..." + src_url=${mirror_link}/oneinstack/src/ZendGuardLoader-70429-PHP-5.4-linux-glibc23-x86_64.tar.gz && Download_src + ;; + 1) + echo "Download zend loader for php 5.3..." + src_url=${mirror_link}/oneinstack/src/ZendGuardLoader-php-5.3-linux-glibc23-x86_64.tar.gz && Download_src + ;; + esac + fi + + # ioncube + if [ "${pecl_ioncube}" == '1' ]; then + echo "Download ioncube..." + src_url=https://downloads.ioncube.com/loader_downloads/ioncube_loaders_lin_${SYS_ARCH_i}.tar.gz && Download_src + fi + + # SourceGuardian + if [ "${pecl_sourceguardian}" == '1' ]; then + echo "Download SourceGuardian..." + src_url=${mirror_link}/oneinstack/src/loaders.linux-${ARCH}.tar.gz && Download_src + fi + + # imageMagick + if [ "${pecl_imagick}" == '1' ]; then + echo "Download ImageMagick..." + src_url=${mirror_link}/oneinstack/src/ImageMagick-${imagemagick_ver}.tar.gz && Download_src + echo "Download imagick..." + if [[ "${php_option}" =~ ^1$ ]]; then + src_url=https://pecl.php.net/get/imagick-${imagick_oldver}.tgz && Download_src + else + src_url=https://pecl.php.net/get/imagick-${imagick_ver}.tgz && Download_src + fi + fi + + # graphicsmagick + if [ "${pecl_gmagick}" == '1' ]; then + echo "Download graphicsmagick..." + src_url=https://downloads.sourceforge.net/project/graphicsmagick/graphicsmagick/${graphicsmagick_ver}/GraphicsMagick-${graphicsmagick_ver}.tar.gz && Download_src + if [[ "${php_option}" =~ ^[1-4]$ ]]; then + echo "Download gmagick for php..." + src_url=https://pecl.php.net/get/gmagick-${gmagick_oldver}.tgz && Download_src + else + echo "Download gmagick for php 7.x..." + src_url=https://pecl.php.net/get/gmagick-${gmagick_ver}.tgz && Download_src + fi + fi + + # redis-server + if [ "${redis_flag}" == 'y' ]; then + echo "Download redis-server..." + src_url=http://download.redis.io/releases/redis-${redis_ver}.tar.gz && Download_src + fi + + # pecl_redis + if [ "${pecl_redis}" == '1' ]; then + if [[ "${php_option}" =~ ^[1-4]$ ]]; then + echo "Download pecl_redis for php 5.x..." + src_url=https://pecl.php.net/get/redis-4.3.0.tgz && Download_src + elif [[ "${php_option}" =~ ^[5-6]$ ]]; then + echo "Download pecl_redis for php 7.0~7.1..." + src_url=https://pecl.php.net/get/redis-5.3.7.tgz && Download_src + else + echo "Download pecl_redis for php 7.2+..." + src_url=https://pecl.php.net/get/redis-${pecl_redis_ver}.tgz && Download_src + fi + fi + + # memcached-server + if [ "${memcached_flag}" == 'y' ]; then + echo "Download memcached-server..." + [ "${OUTIP_STATE}"x == "China"x ] && DOWN_ADDR=${mirror_link}/oneinstack/src || DOWN_ADDR=http://www.memcached.org/files + src_url=${DOWN_ADDR}/memcached-${memcached_ver}.tar.gz && Download_src + fi + + # pecl_memcached + if [ "${pecl_memcached}" == '1' ]; then + echo "Download libmemcached..." + src_url=https://launchpad.net/libmemcached/1.0/${libmemcached_ver}/+download/libmemcached-${libmemcached_ver}.tar.gz && Download_src + if [[ "${php_option}" =~ ^[1-4]$ ]]; then + echo "Download pecl_memcached for php..." + src_url=https://pecl.php.net/get/memcached-${pecl_memcached_oldver}.tgz && Download_src + else + echo "Download pecl_memcached for php 7.x..." + src_url=https://pecl.php.net/get/memcached-${pecl_memcached_ver}.tgz && Download_src + fi + fi + + # memcached-server pecl_memcached pecl_memcache + if [ "${pecl_memcache}" == '1' ]; then + if [[ "${php_option}" =~ ^[1-4]$ ]]; then + echo "Download pecl_memcache for php 5.x..." + src_url=https://pecl.php.net/get/memcache-3.0.8.tgz && Download_src + elif [[ "${php_option}" =~ ^[5-9]$ ]]; then + echo "Download pecl_memcache for php 7.x..." + src_url=https://pecl.php.net/get/memcache-${pecl_memcache_oldver}.tgz && Download_src + else + echo "Download pecl_memcache for php 8.x..." + src_url=https://pecl.php.net/get/memcache-${pecl_memcache_ver}.tgz && Download_src + fi + fi + + # pecl_mongodb + if [ "${pecl_mongodb}" == '1' ]; then + echo "Download pecl mongo for php..." + src_url=https://pecl.php.net/get/mongo-${pecl_mongo_ver}.tgz && Download_src + echo "Download pecl mongodb for php..." + src_url=https://pecl.php.net/get/mongodb-${pecl_mongodb_ver}.tgz && Download_src + fi + + # nodejs + if [ "${nodejs_flag}" == 'y' ]; then + echo "Download Nodejs..." + [ "${OUTIP_STATE}"x == "China"x ] && DOWN_ADDR_NODE=https://mirrors.tuna.tsinghua.edu.cn/nodejs-release || DOWN_ADDR_NODE=https://nodejs.org/dist + src_url=${DOWN_ADDR_NODE}/v${nodejs_ver}/node-v${nodejs_ver}-linux-${SYS_ARCH_n}.tar.gz && Download_src + fi + + # pureftpd + if [ "${pureftpd_flag}" == 'y' ]; then + echo "Download pureftpd..." + src_url=https://download.pureftpd.org/pub/pure-ftpd/releases/pure-ftpd-${pureftpd_ver}.tar.gz && Download_src + fi + + # phpMyAdmin + if [ "${phpmyadmin_flag}" == 'y' ]; then + echo "Download phpMyAdmin..." + if [[ "${php_option}" =~ ^[1-5]$ ]] || [[ "${mphp_ver}" =~ ^5[3-6]$|^70$ ]]; then + src_url=https://files.phpmyadmin.net/phpMyAdmin/${phpmyadmin_oldver}/phpMyAdmin-${phpmyadmin_oldver}-all-languages.tar.gz && Download_src + else + src_url=https://files.phpmyadmin.net/phpMyAdmin/${phpmyadmin_ver}/phpMyAdmin-${phpmyadmin_ver}-all-languages.tar.gz && Download_src + fi + fi + + popd > /dev/null +} diff --git a/include/check_os.sh b/include/check_os.sh new file mode 100644 index 0000000..1a2b7be --- /dev/null +++ b/include/check_os.sh @@ -0,0 +1,138 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +if [ -e "/etc/os-release" ]; then + . /etc/os-release +else + echo "${CFAILURE}/etc/os-release does not exist! ${CEND}" + kill -9 $$; exit 1; +fi + +# Get OS Version +Platform=${ID,,} +VERSION_MAIN_ID=${VERSION_ID%%.*} +ARCH=$(arch) +if [[ "${Platform}" =~ ^centos$|^rhel$|^almalinux$|^rocky$|^fedora$|^amzn$|^ol$|^alinux$|^anolis$|^tencentos$|^opencloudos$|^euleros$|^openeuler$|^kylin$|^uos$|^kylinsecos$ ]]; then + PM=yum + Family=rhel + RHEL_ver=${VERSION_MAIN_ID} + if [[ "${Platform}" =~ ^centos$ ]]; then + if [ "${VERSION_MAIN_ID}" == '6' ]; then + sed -i "s@centos/\$releasever@centos-vault/6.10@g" /etc/yum.repos.d/CentOS-Base.repo + sed -i 's@centos/RPM-GPG@centos-vault/RPM-GPG@g' /etc/yum.repos.d/CentOS-Base.repo + [ -e /etc/yum.repos.d/epel.repo ] && rm -f /etc/yum.repos.d/epel.repo + fi + elif [[ "${Platform}" =~ ^fedora$ ]]; then + Fedora_ver=${VERSION_MAIN_ID} + [ ${VERSION_MAIN_ID} -ge 19 ] && [ ${VERSION_MAIN_ID} -lt 28 ] && RHEL_ver=7 + [ ${VERSION_MAIN_ID} -ge 28 ] && [ ${VERSION_MAIN_ID} -lt 34 ] && RHEL_ver=8 + [ ${VERSION_MAIN_ID} -ge 34 ] && RHEL_ver=9 + elif [[ "${Platform}" =~ ^amzn$|^alinux$|^tencentos$|^euleros$ ]]; then + [[ "${VERSION_MAIN_ID}" =~ ^2$ ]] && RHEL_ver=7 + [[ "${VERSION_MAIN_ID}" =~ ^3$ ]] && RHEL_ver=8 + elif [[ "${Platform}" =~ ^openeuler$ ]]; then + [[ "${RHEL_ver}" =~ ^20$ ]] && RHEL_ver=7 + [[ "${RHEL_ver}" =~ ^2[1,2]$ ]] && RHEL_ver=8 + elif [[ "${Platform}" =~ ^kylin$ ]]; then + [[ "${RHEL_ver}" =~ ^V10$ ]] && RHEL_ver=7 + elif [[ "${Platform}" =~ ^uos$ ]]; then + [[ "${RHEL_ver}" =~ ^20$ ]] && RHEL_ver=8 + elif [[ "${Platform}" =~ ^kylinsecos$ ]]; then + [[ "${VERSION_ID}" =~ ^3.4 ]] && RHEL_ver=7 + [[ "${VERSION_ID}" =~ ^3.5 ]] && RHEL_ver=8 + fi +elif [[ "${Platform}" =~ ^debian$|^deepin$|^kali$ ]]; then + PM=apt-get + Family=debian + Debian_ver=${VERSION_MAIN_ID} + if [[ "${Platform}" =~ ^deepin$ ]]; then + [[ "${Debian_ver}" =~ ^20$ ]] && Debian_ver=10 + [[ "${Debian_ver}" =~ ^23$ ]] && Debian_ver=11 + elif [[ "${Platform}" =~ ^kali$ ]]; then + [[ "${Debian_ver}" =~ ^202 ]] && Debian_ver=10 + fi +elif [[ "${Platform}" =~ ^ubuntu$|^linuxmint$|^elementary$ ]]; then + PM=apt-get + Family=ubuntu + Ubuntu_ver=${VERSION_MAIN_ID} + if [[ "${Platform}" =~ ^linuxmint$ ]]; then + [[ "${VERSION_MAIN_ID}" =~ ^18$ ]] && Ubuntu_ver=16 + [[ "${VERSION_MAIN_ID}" =~ ^19$ ]] && Ubuntu_ver=18 + [[ "${VERSION_MAIN_ID}" =~ ^20$ ]] && Ubuntu_ver=20 + [[ "${VERSION_MAIN_ID}" =~ ^21$ ]] && Ubuntu_ver=22 + elif [[ "${Platform}" =~ ^elementary$ ]]; then + [[ "${VERSION_MAIN_ID}" =~ ^5$ ]] && Ubuntu_ver=18 + [[ "${VERSION_MAIN_ID}" =~ ^6$ ]] && Ubuntu_ver=20 + [[ "${VERSION_MAIN_ID}" =~ ^7$ ]] && Ubuntu_ver=22 + fi +else + echo "${CFAILURE}Does not support this OS ${CEND}" + kill -9 $$; exit 1; +fi + +# Check OS Version +if [ ${RHEL_ver} -lt 7 >/dev/null 2>&1 ] || [ ${Debian_ver} -lt 9 >/dev/null 2>&1 ] || [ ${Ubuntu_ver} -lt 16 >/dev/null 2>&1 ]; then + echo "${CFAILURE}Does not support this OS, Please install CentOS 7+,Debian 9+,Ubuntu 16+ ${CEND}" + kill -9 $$; exit 1; +fi + +command -v gcc > /dev/null 2>&1 || $PM -y install gcc +gcc_ver=$(gcc -dumpversion | awk -F. '{print $1}') + +[ ${gcc_ver} -lt 5 >/dev/null 2>&1 ] && redis_ver=${redis_oldver} + +if uname -m | grep -Eqi "arm|aarch64"; then + armplatform="y" + if uname -m | grep -Eqi "armv7"; then + TARGET_ARCH="armv7" + elif uname -m | grep -Eqi "armv8"; then + TARGET_ARCH="arm64" + elif uname -m | grep -Eqi "aarch64"; then + TARGET_ARCH="aarch64" + else + TARGET_ARCH="unknown" + fi +fi + +if [ "$(uname -r | awk -F- '{print $3}' 2>/dev/null)" == "Microsoft" ]; then + Wsl=true +fi + +if [ "$(getconf WORD_BIT)" == "32" ] && [ "$(getconf LONG_BIT)" == "64" ]; then + if [ "${TARGET_ARCH}" == 'aarch64' ]; then + SYS_ARCH=arm64 + SYS_ARCH_i=aarch64 + SYS_ARCH_n=arm64 + else + SYS_ARCH=amd64 #openjdk + SYS_ARCH_i=x86-64 #ioncube + SYS_ARCH_n=x64 #nodejs + fi +else + echo "${CWARNING}32-bit OS are not supported! ${CEND}" + kill -9 $$; exit 1; +fi + +THREAD=$(grep 'processor' /proc/cpuinfo | sort -u | wc -l) + +# Percona binary: https://docs.percona.com/percona-server/5.7/installation/binary-tarball.html +if [ ${Debian_ver} -lt 9 >/dev/null 2>&1 ]; then + sslLibVer=ssl100 +elif [ "${RHEL_ver}" == '7' ] && [ "${Platform}" != 'fedora' ]; then + sslLibVer=ssl101 +elif [ ${Debian_ver} -ge 9 >/dev/null 2>&1 ] || [ ${Ubuntu_ver} -ge 16 >/dev/null 2>&1 ]; then + sslLibVer=ssl102 +elif [ ${Fedora_ver} -ge 27 >/dev/null 2>&1 ]; then + sslLibVer=ssl102 +elif [ "${RHEL_ver}" == '8' ]; then + sslLibVer=ssl1:111 +else + sslLibVer=unknown +fi diff --git a/include/check_sw.sh b/include/check_sw.sh new file mode 100644 index 0000000..36c84a9 --- /dev/null +++ b/include/check_sw.sh @@ -0,0 +1,162 @@ +#!/bin/bash +# Author: Alpha Eva +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +installDepsDebian() { + echo "${CMSG}Removing the conflicting packages...${CEND}" + if [ "${apache_flag}" == 'y' ]; then + killall apache2 + pkgList="apache2 apache2-doc apache2-utils apache2.2-common apache2.2-bin apache2-mpm-prefork apache2-doc apache2-mpm-worker php5 php5-common php5-cgi php5-cli php5-mysql php5-curl php5-gd" + for Package in ${pkgList};do + apt-get -y purge ${Package} + done + dpkg -l | grep ^rc | awk '{print $2}' | xargs dpkg -P + fi + + if [[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]]; then + pkgList="mysql-client mysql-server mysql-common mysql-server-core-5.5 mysql-client-5.5 mariadb-client mariadb-server mariadb-common" + for Package in ${pkgList};do + apt-get -y purge ${Package} + done + dpkg -l | grep ^rc | awk '{print $2}' | xargs dpkg -P + fi + + echo "${CMSG}Installing dependencies packages...${CEND}" + apt-get -y update + apt-get -y autoremove + apt-get -yf install + export DEBIAN_FRONTEND=noninteractive + + # critical security updates + grep security /etc/apt/sources.list > /tmp/security.sources.list + apt-get -y upgrade -o Dir::Etc::SourceList=/tmp/security.sources.list + + # Install needed packages + case "${Debian_ver}" in + 9|10|11|12) + pkgList="debian-keyring debian-archive-keyring build-essential gcc g++ make cmake autoconf libjpeg62-turbo-dev libjpeg-dev libpng-dev libgd-dev libxml2 libxml2-dev zlib1g zlib1g-dev libc6 libc6-dev libc-client2007e-dev libglib2.0-0 libglib2.0-dev bzip2 libzip-dev libbz2-1.0 libncurses5 libncurses5-dev libaio1 libaio-dev numactl libreadline-dev curl libcurl3-gnutls libcurl4-openssl-dev e2fsprogs libkrb5-3 libkrb5-dev libltdl-dev libidn11 libidn11-dev openssl net-tools libssl-dev libtool libevent-dev bison re2c libsasl2-dev libxslt1-dev libicu-dev locales patch vim zip unzip tmux htop bc dc expect libexpat1-dev libonig-dev libtirpc-dev rsync git lsof lrzsz rsyslog cron logrotate chrony libsqlite3-dev psmisc wget sysv-rc apt-transport-https ca-certificates software-properties-common gnupg ufw" + ;; + *) + echo "${CFAILURE}Your system Debian ${Debian_ver} are not supported!${CEND}" + kill -9 $$; exit 1; + ;; + esac + for Package in ${pkgList}; do + apt-get --no-install-recommends -y install ${Package} + done +} + +installDepsRHEL() { + [ -e '/etc/yum.conf' ] && sed -i 's@^exclude@#exclude@' /etc/yum.conf + if [ "${RHEL_ver}" == '9' ]; then + if [[ "${Platform}" =~ "rhel" ]]; then + subscription-manager repos --enable codeready-builder-for-rhel-9-${ARCH}-rpms + dnf -y install chrony oniguruma-devel rpcgen + elif [[ "${Platform}" =~ "ol" ]]; then + dnf config-manager --set-enabled ol9_codeready_builder + dnf -y install chrony oniguruma-devel rpcgen + else + dnf -y --enablerepo=crb install chrony oniguruma-devel rpcgen + fi + systemctl enable chronyd + elif [ "${RHEL_ver}" == '8' ]; then + if [[ "${Platform}" =~ "rhel" ]]; then + subscription-manager repos --enable codeready-builder-for-rhel-8-${ARCH}-rpms + dnf -y install chrony oniguruma-devel rpcgen + elif [[ "${Platform}" =~ "ol" ]]; then + dnf config-manager --set-enabled ol8_codeready_builder + dnf -y install chrony oniguruma-devel rpcgen + else + [ -z "`grep -w epel /etc/yum.repos.d/*.repo`" ] && yum -y install epel-release + if grep -qw "^\[PowerTools\]" /etc/yum.repos.d/*.repo; then + dnf -y --enablerepo=PowerTools install chrony oniguruma-devel rpcgen + elif grep -qw "^\[powertools\]" /etc/yum.repos.d/*.repo; then + dnf -y --enablerepo=powertools install chrony oniguruma-devel rpcgen + fi + fi + systemctl enable chronyd + elif [ "${RHEL_ver}" == '7' ]; then + [ -z "`grep -w epel /etc/yum.repos.d/*.repo`" ] && yum -y install epel-release + yum -y groupremove "Basic Web Server" "MySQL Database server" "MySQL Database client" + fi + + if [ "${RHEL_ver}" == '9' ]; then + [ ! -e "/usr/lib64/libtinfo.so.5" ] && ln -s /usr/lib64/libtinfo.so.6 /usr/lib64/libtinfo.so.5 + [ ! -e "/usr/lib64/libncurses.so.5" ] && ln -s /usr/lib64/libncurses.so.6 /usr/lib64/libncurses.so.5 + fi + + echo "${CMSG}Installing dependencies packages...${CEND}" + # Install needed packages + pkgList="perl-FindBin deltarpm drpm gcc gcc-c++ make cmake autoconf libjpeg libjpeg-devel libjpeg-turbo libjpeg-turbo-devel libpng libpng-devel libxml2 libxml2-devel zlib zlib-devel libzip libzip-devel glibc glibc-devel krb5-devel libc-client libc-client-devel glib2 glib2-devel bzip2 bzip2-devel ncurses ncurses-devel ncurses-compat-libs libaio numactl numactl-libs readline-devel curl curl-devel e2fsprogs e2fsprogs-devel krb5-devel libidn libidn-devel openssl openssl-devel net-tools libxslt-devel libicu-devel libevent-devel libtool libtool-ltdl bison gd-devel vim-enhanced pcre-devel libmcrypt libmcrypt-devel mhash mhash-devel mcrypt zip unzip chrony oniguruma-devel rpcgen sqlite-devel sysstat patch bc expect expat-devel perl-devel oniguruma oniguruma-devel libtirpc-devel nss libnsl rsync rsyslog git lsof lrzsz psmisc wget which libatomic tmux chkconfig firewalld" + for Package in ${pkgList}; do + yum -y install ${Package} + done + [ ${RHEL_ver} -lt 8 >/dev/null 2>&1 ] && yum -y install cmake3 + + yum -y update bash openssl glibc +} + +installDepsUbuntu() { + # Uninstall the conflicting software + echo "${CMSG}Removing the conflicting packages...${CEND}" + if [ "${apache_flag}" == 'y' ]; then + killall apache2 + pkgList="apache2 apache2-doc apache2-utils apache2.2-common apache2.2-bin apache2-mpm-prefork apache2-doc apache2-mpm-worker php5 php5-common php5-cgi php5-cli php5-mysql php5-curl php5-gd" + for Package in ${pkgList};do + apt-get -y purge ${Package} + done + dpkg -l | grep ^rc | awk '{print $2}' | xargs dpkg -P + fi + + if [[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]]; then + pkgList="mysql-client mysql-server mysql-common mysql-server-core-5.5 mysql-client-5.5 mariadb-client mariadb-server mariadb-common" + for Package in ${pkgList};do + apt-get -y purge ${Package} + done + dpkg -l | grep ^rc | awk '{print $2}' | xargs dpkg -P + fi + + echo "${CMSG}Installing dependencies packages...${CEND}" + apt-get -y update + apt-get -y autoremove + apt-get -yf install + export DEBIAN_FRONTEND=noninteractive + [[ "${Ubuntu_ver}" =~ ^22$ ]] && apt-get -y --allow-downgrades install libicu70=70.1-2 libglib2.0-0=2.72.1-1 libxml2-dev + + # critical security updates + grep security /etc/apt/sources.list > /tmp/security.sources.list + apt-get -y upgrade -o Dir::Etc::SourceList=/tmp/security.sources.list + + # Install needed packages + pkgList="libperl-dev debian-keyring debian-archive-keyring build-essential gcc g++ make cmake autoconf libjpeg8 libjpeg8-dev libpng-dev libpng12-0 libpng12-dev libpng3 libxml2 libxml2-dev zlib1g zlib1g-dev libc6 libc6-dev libc-client2007e-dev libglib2.0-0 libglib2.0-dev bzip2 libzip-dev libbz2-1.0 libncurses5 libncurses5-dev libaio1 libaio-dev numactl libreadline-dev curl libcurl3-gnutls libcurl4-gnutls-dev libcurl4-openssl-dev e2fsprogs libkrb5-3 libkrb5-dev libltdl-dev libidn11 libidn11-dev openssl net-tools libssl-dev libtool libevent-dev re2c libsasl2-dev libxslt1-dev libicu-dev libsqlite3-dev libcloog-ppl1 bison patch vim zip unzip tmux htop bc dc expect libexpat1-dev rsyslog libonig-dev libtirpc-dev libnss3 rsync git lsof lrzsz chrony psmisc wget sysv-rc apt-transport-https ca-certificates software-properties-common gnupg ufw" + export DEBIAN_FRONTEND=noninteractive + for Package in ${pkgList}; do + apt-get --no-install-recommends -y install ${Package} + done +} + +installDepsBySrc() { + pushd ${oneinstack_dir}/src > /dev/null + if ! command -v icu-config > /dev/null 2>&1 || icu-config --version | grep '^3.' || [ "${Ubuntu_ver}" == "20" ]; then + tar xzf icu4c-${icu4c_ver}-src.tgz + pushd icu/source > /dev/null + ./configure --prefix=/usr/local + make -j ${THREAD} && make install + popd > /dev/null + rm -rf icu + fi + + if command -v lsof >/dev/null 2>&1; then + echo 'already initialize' > ~/.oneinstack + else + echo "${CFAILURE}${PM} config error parsing file failed${CEND}" + kill -9 $$; exit 1; + fi + + popd > /dev/null +} diff --git a/include/color.sh b/include/color.sh new file mode 100644 index 0000000..8317379 --- /dev/null +++ b/include/color.sh @@ -0,0 +1,32 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +echo=echo +for cmd in echo /bin/echo; do + $cmd >/dev/null 2>&1 || continue + if ! $cmd -e "" | grep -qE '^-e'; then + echo=$cmd + break + fi +done +CSI=$($echo -e "\033[") +CEND="${CSI}0m" +CDGREEN="${CSI}32m" +CRED="${CSI}1;31m" +CGREEN="${CSI}1;32m" +CYELLOW="${CSI}1;33m" +CBLUE="${CSI}1;34m" +CMAGENTA="${CSI}1;35m" +CCYAN="${CSI}1;36m" +CSUCCESS="$CDGREEN" +CFAILURE="$CRED" +CQUESTION="$CMAGENTA" +CWARNING="$CYELLOW" +CMSG="$CCYAN" diff --git a/include/composer.sh b/include/composer.sh new file mode 100644 index 0000000..99d58df --- /dev/null +++ b/include/composer.sh @@ -0,0 +1,41 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_composer() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + if [ -e "/usr/local/bin/composer" ]; then + echo "${CWARNING}PHP Composer already installed! ${CEND}" + else + pushd ${oneinstack_dir}/src > /dev/null + if [ "${OUTIP_STATE}"x == "China"x ]; then + wget --no-check-certificate -c https://mirrors.aliyun.com/composer/composer.phar -O /usr/local/bin/composer > /dev/null 2>&1 + ${php_install_dir}/bin/php /usr/local/bin/composer config -g repo.packagist composer https://packagist.phpcomposer.com + else + wget --no-check-certificate -c https://getcomposer.org/composer.phar -O /usr/local/bin/composer > /dev/null 2>&1 + fi + chmod +x /usr/local/bin/composer + if [ -e "/usr/local/bin/composer" ]; then + echo; echo "${CSUCCESS}PHP Composer installed successfully! ${CEND}" + else + echo; echo "${CFAILURE}PHP Composer install failed, Please try again! ${CEND}" + fi + popd > /dev/null + fi + fi +} + +Uninstall_composer() { + if [ -e "/usr/local/bin/composer" ]; then + rm -f /usr/local/bin/composer + echo; echo "${CMSG}Composer uninstall completed${CEND}"; + else + echo; echo "${CWARNING}Composer does not exist! ${CEND}" + fi +} diff --git a/include/demo.sh b/include/demo.sh new file mode 100644 index 0000000..d1e3abc --- /dev/null +++ b/include/demo.sh @@ -0,0 +1,45 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +DEMO() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e ${wwwroot_dir}/default/index.html ]; then + [ "${OUTIP_STATE}"x == "China"x ] && /bin/cp ${oneinstack_dir}/config/index_cn.html ${wwwroot_dir}/default/index.html || /bin/cp ${oneinstack_dir}/config/index.html ${wwwroot_dir}/default + fi + + if [ -e "${php_install_dir}/bin/php" ]; then + src_url=${mirror_link}/oneinstack/src/xprober.php && Download_src + /bin/cp xprober.php ${wwwroot_dir}/default + + echo "" > ${wwwroot_dir}/default/phpinfo.php + case "${phpcache_option}" in + 1) + src_url=${mirror_link}/oneinstack/src/ocp.php && Download_src + /bin/cp ocp.php ${wwwroot_dir}/default + ;; + 2) + sed -i 's@Opcache@APC@' ${wwwroot_dir}/default/index.html + ;; + 3) + sed -i 's@Opcache@xcache@' ${wwwroot_dir}/default/index.html + ;; + 4) + /bin/cp eaccelerator-*/control.php ${wwwroot_dir}/default + sed -i 's@Opcache@eAccelerator@' ${wwwroot_dir}/default/index.html + ;; + *) + sed -i 's@Opcache@@' ${wwwroot_dir}/default/index.html + ;; + esac + fi + chown -R ${run_user}:${run_group} ${wwwroot_dir}/default + [ -e /bin/systemctl ] && systemctl daemon-reload + popd > /dev/null +} diff --git a/include/download.sh b/include/download.sh new file mode 100644 index 0000000..8167d61 --- /dev/null +++ b/include/download.sh @@ -0,0 +1,17 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Download_src() { + [ -s "${src_url##*/}" ] && echo "[${CMSG}${src_url##*/}${CEND}] found" || { wget --limit-rate=100M --tries=6 -c --no-check-certificate ${src_url}; sleep 1; } + if [ ! -e "${src_url##*/}" ]; then + echo "${CFAILURE}Auto download failed! You can manually download ${src_url} into the oneinstack/src directory.${CEND}" + kill -9 $$; exit 1; + fi +} diff --git a/include/eaccelerator.sh b/include/eaccelerator.sh new file mode 100644 index 0000000..376b38b --- /dev/null +++ b/include/eaccelerator.sh @@ -0,0 +1,73 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_eAccelerator() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + if [[ "${PHP_main_ver}" =~ ^5.[3-4]$ ]]; then + if [ "${PHP_main_ver}" == '5.3' ]; then + tar jxf eaccelerator-${eaccelerator_ver}.tar.bz2 + pushd eaccelerator-${eaccelerator_ver} > /dev/null + elif [ "${PHP_main_ver}" == '5.4' ]; then + /bin/mv master eaccelerator-eaccelerator-42067ac.tar.gz + tar xzf eaccelerator-eaccelerator-42067ac.tar.gz + pushd eaccelerator-eaccelerator-42067ac > /dev/null + fi + ${php_install_dir}/bin/phpize + ./configure --enable-eaccelerator=shared --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/eaccelerator.so" ]; then + mkdir /var/eaccelerator_cache;chown -R ${run_user}:${run_group} /var/eaccelerator_cache + cat > ${php_install_dir}/etc/php.d/02-eaccelerator.ini << EOF +[eaccelerator] +zend_extension=${phpExtensionDir}/eaccelerator.so +eaccelerator.shm_size=64 +eaccelerator.cache_dir=/var/eaccelerator_cache +eaccelerator.enable=1 +eaccelerator.optimizer=1 +eaccelerator.check_mtime=1 +eaccelerator.debug=0 +eaccelerator.filter= +eaccelerator.shm_max=0 +eaccelerator.shm_ttl=0 +eaccelerator.shm_prune_period=0 +eaccelerator.shm_only=0 +eaccelerator.compress=0 +eaccelerator.compress_level=9 +eaccelerator.keys=disk_only +eaccelerator.sessions=disk_only +eaccelerator.content=disk_only +EOF + [ -z "$(grep 'kernel.shmmax = 67108864' /etc/sysctl.conf)" ] && echo "kernel.shmmax = 67108864" >> /etc/sysctl.conf + sysctl -p + echo "${CSUCCESS}PHP eaccelerator module installed successfully! ${CEND}" + rm -rf eaccelerator-${eaccelerator_ver} eaccelerator-eaccelerator-42067ac + else + echo "${CFAILURE}PHP eaccelerator module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + else + echo; echo "${CWARNING}Your php ${PHP_detail_ver} does not support eAccelerator! ${CEND}"; + fi + popd > /dev/null + fi +} + +Uninstall_eAccelerator() { + if [ -e "${php_install_dir}/etc/php.d/02-eaccelerator.ini" ]; then + rm -rf ${php_install_dir}/etc/php.d/02-eaccelerator.ini /var/eaccelerator_cache + echo; echo "${CMSG}PHP eaccelerator module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP eaccelerator module does not exist! ${CEND}" + fi +} diff --git a/include/fail2ban.sh b/include/fail2ban.sh new file mode 100644 index 0000000..ec30c9b --- /dev/null +++ b/include/fail2ban.sh @@ -0,0 +1,96 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_fail2ban() { + pushd ${oneinstack_dir}/src > /dev/null + src_url=${mirror_link}/oneinstack/src/fail2ban-${fail2ban_ver}.tar.gz && Download_src + tar xzf fail2ban-${fail2ban_ver}.tar.gz + pushd fail2ban-${fail2ban_ver} > /dev/null + if command -v python3 > /dev/null 2>&1; then + python3 setup.py install + else + python setup.py install + fi + /bin/cp build/fail2ban.service /lib/systemd/system/ + systemctl enable fail2ban + [ -z "`grep ^Port /etc/ssh/sshd_config`" ] && now_ssh_port=22 || now_ssh_port=`grep ^Port /etc/ssh/sshd_config | awk '{print $2}' | head -1` + if [ "${PM}" == 'yum' ]; then + cat > /etc/fail2ban/jail.local << EOF +[DEFAULT] +ignoreip = 127.0.0.1/8 +bantime = 86400 +findtime = 600 +maxretry = 5 +backend = auto +banaction = firewallcmd-ipset +action = %(action_mwl)s + +[sshd] +enabled = true +filter = sshd +port = ${now_ssh_port} +action = %(action_mwl)s +logpath = /var/log/secure +bantime = 86400 +findtime = 600 +maxretry = 5 +EOF + elif [ "${PM}" == 'apt-get' ]; then + if ufw status | grep -wq inactive; then + ufw default allow incoming + ufw --force enable + fi + cat > /etc/fail2ban/jail.local << EOF +[DEFAULT] +ignoreip = 127.0.0.1/8 +bantime = 86400 +findtime = 600 +maxretry = 5 +backend = auto +banaction = ufw +action = %(action_mwl)s + +[sshd] +enabled = true +filter = sshd +port = ${now_ssh_port} +action = %(action_mwl)s +logpath = /var/log/auth.log +bantime = 86400 +findtime = 600 +maxretry = 5 +EOF + fi + cat > /etc/logrotate.d/fail2ban << EOF +/var/log/fail2ban.log { + missingok + notifempty + postrotate + /usr/local/bin/fail2ban-client flushlogs >/dev/null || true + endscript +} +EOF + kill -9 `ps -ef | grep fail2ban | grep -v grep | awk '{print $2}'` > /dev/null 2>&1 + systemctl start fail2ban + popd > /dev/null + if [ -e "/usr/local/bin/fail2ban-server" ]; then + echo; echo "${CSUCCESS}fail2ban installed successfully! ${CEND}" + else + echo; echo "${CFAILURE}fail2ban install failed, Please try again! ${CEND}" + fi + popd > /dev/null +} + +Uninstall_fail2ban() { + systemctl stop fail2ban + systemctl disable fail2ban + rm -rf /usr/local/bin/fail2ban* /etc/init.d/fail2ban /etc/fail2ban /etc/logrotate.d/fail2ban /var/log/fail2ban.* /var/run/fail2ban /lib/systemd/system/fail2ban.service + echo; echo "${CMSG}fail2ban uninstall completed${CEND}"; +} diff --git a/include/get_char.sh b/include/get_char.sh new file mode 100644 index 0000000..c14f852 --- /dev/null +++ b/include/get_char.sh @@ -0,0 +1,19 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +get_char() { + SAVEDSTTY=`stty -g` + stty -echo + stty cbreak + dd if=/dev/tty bs=1 count=1 2> /dev/null + stty -raw + stty echo + stty $SAVEDSTTY +} diff --git a/include/init_Debian.sh b/include/init_Debian.sh new file mode 100644 index 0000000..e39b624 --- /dev/null +++ b/include/init_Debian.sh @@ -0,0 +1,100 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +# Custom profile +cat > /etc/profile.d/oneinstack.sh << EOF +HISTSIZE=10000 +PS1='\${debian_chroot:+(\$debian_chroot)}\\[\\e[1;32m\\]\\u@\\h\\[\\033[00m\\]:\\[\\033[01;34m\\]\\w\\[\\033[00m\\]\\$ ' +HISTTIMEFORMAT="%F %T \$(whoami) " + +alias l='ls -AFhlt --color=auto' +alias lh='l | head' +alias ll='ls -l --color=auto' +alias ls='ls --color=auto' +alias vi=vim + +GREP_OPTIONS="--color=auto" +alias grep='grep --color' +alias egrep='egrep --color' +alias fgrep='fgrep --color' +EOF + +sed -i 's@^"syntax on@syntax on@' /etc/vim/vimrc + +# history +[ -z "$(grep history-timestamp ~/.bashrc)" ] && echo "PROMPT_COMMAND='{ msg=\$(history 1 | { read x y; echo \$y; });user=\$(whoami); echo \$(date \"+%Y-%m-%d %H:%M:%S\"):\$user:\`pwd\`/:\$msg ---- \$(who am i); } >> /tmp/\`hostname\`.\`whoami\`.history-timestamp'" >> ~/.bashrc + +# /etc/security/limits.conf +[ -e /etc/security/limits.d/*nproc.conf ] && rename nproc.conf nproc.conf_bk /etc/security/limits.d/*nproc.conf +[ -z "$(grep 'session required pam_limits.so' /etc/pam.d/common-session)" ] && echo "session required pam_limits.so" >> /etc/pam.d/common-session +sed -i '/^# End of file/,$d' /etc/security/limits.conf +cat >> /etc/security/limits.conf < /etc/resolv.conf << EOF +#nameserver 114.114.114.114 +#nameserver 8.8.8.8 +#EOF + +# /etc/sysctl.conf +[ -z "$(grep 'fs.file-max' /etc/sysctl.conf)" ] && cat >> /etc/sysctl.conf << EOF +fs.file-max = 1000000 +fs.inotify.max_user_instances = 8192 +net.ipv4.tcp_syncookies = 1 +net.ipv4.tcp_fin_timeout = 30 +net.ipv4.tcp_tw_reuse = 1 +net.ipv4.ip_local_port_range = 1024 65000 +net.ipv4.tcp_max_syn_backlog = 16384 +net.ipv4.tcp_max_tw_buckets = 6000 +net.ipv4.route.gc_timeout = 100 +net.ipv4.tcp_syn_retries = 1 +net.ipv4.tcp_synack_retries = 1 +net.core.somaxconn = 32768 +net.core.netdev_max_backlog = 32768 +net.ipv4.tcp_timestamps = 0 +net.ipv4.tcp_max_orphans = 32768 +EOF +sysctl -p + +sed -i 's@^ACTIVE_CONSOLES.*@ACTIVE_CONSOLES="/dev/tty[1-2]"@' /etc/default/console-setup +sed -i 's@^# en_US.UTF-8@en_US.UTF-8@' /etc/locale.gen +init q + +# ufw +if [ "${firewall_flag}" == 'y' ]; then + ufw allow 22/tcp + [ "${ssh_port}" != "22" ] && ufw allow ${ssh_port}/tcp + ufw allow 80/tcp + ufw allow 443/tcp + ufw --force enable +else + ufw --force disable +fi +systemctl restart rsyslog ssh + +. /etc/profile +. ~/.bashrc diff --git a/include/init_RHEL.sh b/include/init_RHEL.sh new file mode 100644 index 0000000..32d84c4 --- /dev/null +++ b/include/init_RHEL.sh @@ -0,0 +1,113 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +# Close SELINUX +setenforce 0 +sed -i 's/^SELINUX=.*$/SELINUX=disabled/' /etc/selinux/config + +# Custom profile +cat > /etc/profile.d/oneinstack.sh << EOF +HISTSIZE=10000 +PS1="\[\e[37;40m\][\[\e[32;40m\]\u\[\e[37;40m\]@\h \[\e[35;40m\]\W\[\e[0m\]]\\\\$ " +HISTTIMEFORMAT="%F %T \$(whoami) " + +alias l='ls -AFhlt' +alias lh='l | head' +alias vi=vim + +GREP_OPTIONS="--color=auto" +alias grep='grep --color' +alias egrep='egrep --color' +alias fgrep='fgrep --color' +EOF +[[ "${Platform}" =~ ^euleros$|^openeuler$ ]] && sed -i '/HISTTIMEFORMAT=/d' /etc/profile.d/oneinstack.sh + +[[ ! "${Platform}" =~ ^euleros$|^openeuler$ ]] && [ -z "$(grep ^'PROMPT_COMMAND=' /etc/bashrc)" ] && cat >> /etc/bashrc << EOF +PROMPT_COMMAND='{ msg=\$(history 1 | { read x y; echo \$y; });logger "[euid=\$(whoami)]":\$(who am i):[\`pwd\`]"\$msg"; }' +EOF + +# /etc/security/limits.conf +[ -e /etc/security/limits.d/*nproc.conf ] && rename nproc.conf nproc.conf_bk /etc/security/limits.d/*nproc.conf +sed -i '/^# End of file/,$d' /etc/security/limits.conf +cat >> /etc/security/limits.conf < /etc/sysconfig/modules/nf_conntrack.modules +chmod +x /etc/sysconfig/modules/nf_conntrack.modules +modprobe nf_conntrack +modprobe nf_conntrack_ipv4 +echo options nf_conntrack hashsize=131072 > /etc/modprobe.d/nf_conntrack.conf + +# /etc/sysctl.conf +[ ! -e "/etc/sysctl.conf_bk" ] && /bin/mv /etc/sysctl.conf{,_bk} +cat > /etc/sysctl.conf << EOF +fs.file-max=1000000 +net.ipv4.tcp_max_tw_buckets = 6000 +net.ipv4.tcp_sack = 1 +net.ipv4.tcp_window_scaling = 1 +net.ipv4.tcp_rmem = 4096 87380 4194304 +net.ipv4.tcp_wmem = 4096 16384 4194304 +net.ipv4.tcp_max_syn_backlog = 16384 +net.core.netdev_max_backlog = 32768 +net.core.somaxconn = 32768 +net.core.wmem_default = 8388608 +net.core.rmem_default = 8388608 +net.core.rmem_max = 16777216 +net.core.wmem_max = 16777216 +net.ipv4.tcp_timestamps = 0 +net.ipv4.tcp_fin_timeout = 20 +net.ipv4.tcp_synack_retries = 2 +net.ipv4.tcp_syn_retries = 2 +net.ipv4.tcp_syncookies = 1 +#net.ipv4.tcp_tw_len = 1 +net.ipv4.tcp_tw_reuse = 1 +net.ipv4.tcp_mem = 94500000 915000000 927000000 +net.ipv4.tcp_max_orphans = 3276800 +net.ipv4.ip_local_port_range = 1024 65000 +net.nf_conntrack_max = 6553500 +net.netfilter.nf_conntrack_max = 6553500 +net.netfilter.nf_conntrack_tcp_timeout_close_wait = 60 +net.netfilter.nf_conntrack_tcp_timeout_fin_wait = 120 +net.netfilter.nf_conntrack_tcp_timeout_time_wait = 120 +net.netfilter.nf_conntrack_tcp_timeout_established = 3600 +EOF +sysctl -p + +if [ ${RHEL_ver} -ge 7 >/dev/null 2>&1 ]; then + sed -i 's@LANG=.*$@LANG="en_US.UTF-8"@g' /etc/locale.conf +fi + +# firewall +if [ "${firewall_flag}" == 'y' ]; then + systemctl enable firewalld + systemctl start firewalld + firewall-cmd --permanent --zone=public --add-port={22/tcp,80/tcp,443/tcp} + [ "${ssh_port}" != "22" ] && firewall-cmd --permanent --zone=public --add-port=${ssh_port}/tcp + firewall-cmd --reload +else + systemctl stop firewalld + systemctl disable firewalld +fi +systemctl restart rsyslog sshd + +. /etc/profile diff --git a/include/init_Ubuntu.sh b/include/init_Ubuntu.sh new file mode 100644 index 0000000..904f83c --- /dev/null +++ b/include/init_Ubuntu.sh @@ -0,0 +1,100 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +# Custom profile +cat > /etc/profile.d/oneinstack.sh << EOF +HISTSIZE=10000 +HISTTIMEFORMAT="%F %T \$(whoami) " + +alias l='ls -AFhlt --color=auto' +alias lh='l | head' +alias ll='ls -l --color=auto' +alias ls='ls --color=auto' +alias vi=vim + +GREP_OPTIONS="--color=auto" +alias grep='grep --color' +alias egrep='egrep --color' +alias fgrep='fgrep --color' +EOF + +sed -i 's@^"syntax on@syntax on@' /etc/vim/vimrc + +# PS1 +[ -z "$(grep ^PS1 ~/.bashrc)" ] && echo "PS1='\${debian_chroot:+(\$debian_chroot)}\\[\\e[1;32m\\]\\u@\\h\\[\\033[00m\\]:\\[\\033[01;34m\\]\\w\\[\\033[00m\\]\\$ '" >> ~/.bashrc + +# history +[ -z "$(grep history-timestamp ~/.bashrc)" ] && echo "PROMPT_COMMAND='{ msg=\$(history 1 | { read x y; echo \$y; });user=\$(whoami); echo \$(date \"+%Y-%m-%d %H:%M:%S\"):\$user:\`pwd\`/:\$msg ---- \$(who am i); } >> /tmp/\`hostname\`.\`whoami\`.history-timestamp'" >> ~/.bashrc + +# /etc/security/limits.conf +[ -e /etc/security/limits.d/*nproc.conf ] && rename nproc.conf nproc.conf_bk /etc/security/limits.d/*nproc.conf +[ -z "$(grep 'session required pam_limits.so' /etc/pam.d/common-session)" ] && echo "session required pam_limits.so" >> /etc/pam.d/common-session +sed -i '/^# End of file/,$d' /etc/security/limits.conf +cat >> /etc/security/limits.conf <> /etc/sysctl.conf << EOF +fs.file-max = 1000000 +fs.inotify.max_user_instances = 8192 +net.ipv4.tcp_syncookies = 1 +net.ipv4.tcp_fin_timeout = 30 +net.ipv4.tcp_tw_reuse = 1 +net.ipv4.ip_local_port_range = 1024 65000 +net.ipv4.tcp_max_syn_backlog = 16384 +net.ipv4.tcp_max_tw_buckets = 6000 +net.ipv4.route.gc_timeout = 100 +net.ipv4.tcp_syn_retries = 1 +net.ipv4.tcp_synack_retries = 1 +net.core.somaxconn = 32768 +net.core.netdev_max_backlog = 32768 +net.ipv4.tcp_timestamps = 0 +net.ipv4.tcp_max_orphans = 32768 +EOF +sysctl -p + +sed -i 's@^ACTIVE_CONSOLES.*@ACTIVE_CONSOLES="/dev/tty[1-2]"@' /etc/default/console-setup +locale-gen en_US.UTF-8 +[ -d "/var/lib/locales/supported.d" ] && echo "en_US.UTF-8 UTF-8" > /var/lib/locales/supported.d/local +cat > /etc/default/locale << EOF +LANG=en_US.UTF-8 +LANGUAGE=en_US:en +EOF + +# ufw +if [ "${firewall_flag}" == 'y' ]; then + ufw allow 22/tcp + [ "${ssh_port}" != "22" ] && ufw allow ${ssh_port}/tcp + ufw allow 80/tcp + ufw allow 443/tcp + ufw --force enable +else + ufw --force disable +fi +systemctl restart rsyslog ssh + +. /etc/profile +. ~/.bashrc diff --git a/include/ioncube.sh b/include/ioncube.sh new file mode 100644 index 0000000..4228eb9 --- /dev/null +++ b/include/ioncube.sh @@ -0,0 +1,43 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_ionCube() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=`${php_install_dir}/bin/php-config --version` + PHP_main_ver=${PHP_detail_ver%.*} + phpExtensionDir=`${php_install_dir}/bin/php-config --extension-dir` + [ ! -d "${phpExtensionDir}" ] && mkdir -p ${phpExtensionDir} + [ -e "ioncube_loaders_lin_${SYS_ARCH_i}.tar.gz" ] && tar xzf ioncube_loaders_lin_${SYS_ARCH_i}.tar.gz + if [ -z "`echo ${phpExtensionDir} | grep 'non-zts'`" ]; then + /bin/mv ioncube/ioncube_loader_lin_${PHP_main_ver}_ts.so ${phpExtensionDir} + zend_extension="${phpExtensionDir}/ioncube_loader_lin_${PHP_main_ver}_ts.so" + else + /bin/mv ioncube/ioncube_loader_lin_${PHP_main_ver}.so ${phpExtensionDir} + zend_extension="${phpExtensionDir}/ioncube_loader_lin_${PHP_main_ver}.so" + fi + + if [ -f "${zend_extension}" ]; then + echo "zend_extension=${zend_extension}" > ${php_install_dir}/etc/php.d/00-ioncube.ini + echo "${CSUCCESS}PHP ionCube module installed successfully! ${CEND}" + rm -rf ioncube + fi + popd > /dev/null + fi +} + +Uninstall_ionCube() { + if [ -e "${php_install_dir}/etc/php.d/00-ioncube.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/00-ioncube.ini + echo; echo "${CMSG}PHP ionCube module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP ionCube module does not exist! ${CEND}" + fi +} diff --git a/include/jemalloc.sh b/include/jemalloc.sh new file mode 100644 index 0000000..846e71d --- /dev/null +++ b/include/jemalloc.sh @@ -0,0 +1,35 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Jemalloc() { + if [ ! -e "/usr/local/lib/libjemalloc.so" ]; then + pushd ${oneinstack_dir}/src > /dev/null + tar xjf jemalloc-${jemalloc_ver}.tar.bz2 + pushd jemalloc-${jemalloc_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "/usr/local/lib/libjemalloc.so" ]; then + if [ "${Family}" == 'rhel' ]; then + ln -s /usr/local/lib/libjemalloc.so.2 /usr/lib64/libjemalloc.so.1 + else + ln -s /usr/local/lib/libjemalloc.so.2 /usr/lib/libjemalloc.so.1 + fi + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + echo "${CSUCCESS}jemalloc module installed successfully! ${CEND}" + rm -rf jemalloc-${jemalloc_ver} + else + echo "${CFAILURE}jemalloc install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + popd > /dev/null + fi +} diff --git a/include/mariadb-10.11.sh b/include/mariadb-10.11.sh new file mode 100644 index 0000000..306d9bc --- /dev/null +++ b/include/mariadb-10.11.sh @@ -0,0 +1,215 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MariaDB1011() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mariadb_install_dir}" ] && mkdir -p ${mariadb_install_dir} + mkdir -p ${mariadb_data_dir};chown mysql:mysql -R ${mariadb_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar zxf mariadb-${mariadb1011_ver}-linux-systemd-x86_64.tar.gz + mv mariadb-${mariadb1011_ver}-linux-systemd-x86_64/* ${mariadb_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mariadb_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/mysql@${mariadb_install_dir}@g" ${mariadb_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + boostVersion2=$(echo ${boost_oldver} | awk -F. '{print $1"_"$2"_"$3}') + tar xzf boost_${boostVersion2}.tar.gz + tar xzf mariadb-${mariadb1011_ver}.tar.gz + pushd mariadb-${mariadb1011_ver} + cmake . -DCMAKE_INSTALL_PREFIX=${mariadb_install_dir} \ + -DMYSQL_DATADIR=${mariadb_data_dir} \ + -DDOWNLOAD_BOOST=1 \ + -DWITH_BOOST=../boost_${boostVersion2} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${mariadb_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MariaDB installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mariadb-${mariadb1011_ver}-linux-systemd-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mariadb-${mariadb1011_ver} boost_${boostVersion2} + fi + else + rm -rf ${mariadb_install_dir} + echo "${CFAILURE}MariaDB install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mariadb_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mariadb_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mariadb_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock +default-character-set = utf8mb4 + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${mariadb_install_dir} +datadir = ${mariadb_data_dir} +pid-file = ${mariadb_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${mariadb_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mariadb_data_dir}/mysql-slow.log + +performance_schema = 0 + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mariadb_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${mariadb_install_dir} --datadir=${mariadb_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mariadb_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mariadb_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mariadb_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mariadb_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mariadb_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${mariadb_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.user where Password='' and User not like 'mariadb.%';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.db where User='';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.proxies_priv where Host!='localhost';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + echo "${mariadb_install_dir}/lib" > /etc/ld.so.conf.d/z-mariadb.conf + ldconfig + service mysqld stop +} diff --git a/include/mariadb-10.4.sh b/include/mariadb-10.4.sh new file mode 100644 index 0000000..ad9ac74 --- /dev/null +++ b/include/mariadb-10.4.sh @@ -0,0 +1,217 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MariaDB104() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mariadb_install_dir}" ] && mkdir -p ${mariadb_install_dir} + mkdir -p ${mariadb_data_dir};chown mysql:mysql -R ${mariadb_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar zxf mariadb-${mariadb104_ver}-linux-systemd-x86_64.tar.gz + mv mariadb-${mariadb104_ver}-linux-systemd-x86_64/* ${mariadb_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mariadb_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/mysql@${mariadb_install_dir}@g" ${mariadb_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + boostVersion2=$(echo ${boost_oldver} | awk -F. '{print $1"_"$2"_"$3}') + tar xzf boost_${boostVersion2}.tar.gz + tar xzf mariadb-${mariadb104_ver}.tar.gz + pushd mariadb-${mariadb104_ver} + cmake . -DCMAKE_INSTALL_PREFIX=${mariadb_install_dir} \ + -DMYSQL_DATADIR=${mariadb_data_dir} \ + -DDOWNLOAD_BOOST=1 \ + -DWITH_BOOST=../boost_${boostVersion2} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${mariadb_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MariaDB installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mariadb-${mariadb104_ver}-linux-systemd-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mariadb-${mariadb104_ver} boost_${boostVersion2} + fi + else + rm -rf ${mariadb_install_dir} + echo "${CFAILURE}MariaDB install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mariadb_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mariadb_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mariadb_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock +default-character-set = utf8mb4 + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${mariadb_install_dir} +datadir = ${mariadb_data_dir} +pid-file = ${mariadb_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${mariadb_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mariadb_data_dir}/mysql-slow.log + +performance_schema = 0 + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mariadb_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${mariadb_install_dir} --datadir=${mariadb_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mariadb_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mariadb_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mariadb_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mariadb_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mariadb_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${mariadb_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.user where Password='' and User not like 'mariadb.%';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.db where User='';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.proxies_priv where Host!='localhost';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + echo "${mariadb_install_dir}/lib" > /etc/ld.so.conf.d/z-mariadb.conf + ldconfig + service mysqld stop +} diff --git a/include/mariadb-10.5.sh b/include/mariadb-10.5.sh new file mode 100644 index 0000000..ce1ff1e --- /dev/null +++ b/include/mariadb-10.5.sh @@ -0,0 +1,215 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MariaDB105() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mariadb_install_dir}" ] && mkdir -p ${mariadb_install_dir} + mkdir -p ${mariadb_data_dir};chown mysql:mysql -R ${mariadb_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar zxf mariadb-${mariadb105_ver}-linux-systemd-x86_64.tar.gz + mv mariadb-${mariadb105_ver}-linux-systemd-x86_64/* ${mariadb_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mariadb_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/mysql@${mariadb_install_dir}@g" ${mariadb_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + boostVersion2=$(echo ${boost_oldver} | awk -F. '{print $1"_"$2"_"$3}') + tar xzf boost_${boostVersion2}.tar.gz + tar xzf mariadb-${mariadb105_ver}.tar.gz + pushd mariadb-${mariadb105_ver} + cmake . -DCMAKE_INSTALL_PREFIX=${mariadb_install_dir} \ + -DMYSQL_DATADIR=${mariadb_data_dir} \ + -DDOWNLOAD_BOOST=1 \ + -DWITH_BOOST=../boost_${boostVersion2} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${mariadb_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MariaDB installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mariadb-${mariadb105_ver}-linux-systemd-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mariadb-${mariadb105_ver} boost_${boostVersion2} + fi + else + rm -rf ${mariadb_install_dir} + echo "${CFAILURE}MariaDB install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mariadb_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mariadb_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mariadb_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock +default-character-set = utf8mb4 + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${mariadb_install_dir} +datadir = ${mariadb_data_dir} +pid-file = ${mariadb_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${mariadb_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mariadb_data_dir}/mysql-slow.log + +performance_schema = 0 + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mariadb_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${mariadb_install_dir} --datadir=${mariadb_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mariadb_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mariadb_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mariadb_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mariadb_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mariadb_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${mariadb_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.user where Password='' and User not like 'mariadb.%';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.db where User='';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.proxies_priv where Host!='localhost';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + echo "${mariadb_install_dir}/lib" > /etc/ld.so.conf.d/z-mariadb.conf + ldconfig + service mysqld stop +} diff --git a/include/mariadb-5.5.sh b/include/mariadb-5.5.sh new file mode 100644 index 0000000..6bb71c8 --- /dev/null +++ b/include/mariadb-5.5.sh @@ -0,0 +1,216 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MariaDB55() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mariadb_install_dir}" ] && mkdir -p ${mariadb_install_dir} + mkdir -p ${mariadb_data_dir};chown mysql:mysql -R ${mariadb_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar zxf mariadb-${mariadb55_ver}-linux-systemd-x86_64.tar.gz + mv mariadb-${mariadb55_ver}-linux-systemd-x86_64/* ${mariadb_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mariadb_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/mysql@${mariadb_install_dir}@g" ${mariadb_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + tar xzf mariadb-${mariadb55_ver}.tar.gz + pushd mariadb-${mariadb55_ver} + [ "${armplatform}" == "y" ] && patch -p1 < ../mysql-5.5-fix-arm-client_plugin.patch + cmake . -DCMAKE_INSTALL_PREFIX=${mariadb_install_dir} \ + -DMYSQL_DATADIR=${mariadb_data_dir} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_READLINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${mariadb_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MariaDB installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mariadb-${mariadb55_ver}-linux-systemd-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mariadb-${mariadb55_ver} + fi + else + rm -rf ${mariadb_install_dir} + echo "${CFAILURE}MariaDB install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mariadb_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mariadb_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mariadb_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${mariadb_install_dir} +datadir = ${mariadb_data_dir} +pid-file = ${mariadb_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${mariadb_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mariadb_data_dir}/mysql-slow.log + +performance_schema = 0 + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +#default-storage-engine = MyISAM +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G +myisam_repair_threads = 1 + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mariadb_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${mariadb_install_dir} --datadir=${mariadb_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mariadb_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mariadb_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mariadb_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mariadb_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mariadb_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${mariadb_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.user where Password='' and User not like 'mariadb.%';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.db where User='';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.proxies_priv where Host!='localhost';" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + echo "${mariadb_install_dir}/lib" > /etc/ld.so.conf.d/z-mariadb.conf + ldconfig + service mysqld stop +} diff --git a/include/memcached.sh b/include/memcached.sh new file mode 100644 index 0000000..f97c96c --- /dev/null +++ b/include/memcached.sh @@ -0,0 +1,127 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_memcached_server() { + pushd ${oneinstack_dir}/src > /dev/null + # memcached server + id -u memcached >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin memcached + + tar xzf memcached-${memcached_ver}.tar.gz + pushd memcached-${memcached_ver} > /dev/null + [ ! -d "${memcached_install_dir}" ] && mkdir -p ${memcached_install_dir} + ./configure --prefix=${memcached_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${memcached_install_dir}/bin/memcached" ]; then + echo "${CSUCCESS}memcached installed successfully! ${CEND}" + rm -rf memcached-${memcached_ver} + ln -s ${memcached_install_dir}/bin/memcached /usr/bin/memcached + /bin/cp ../init.d/memcached.service /lib/systemd/system/ + systemctl enable memcached + systemctl start memcached + rm -rf memcached-${memcached_ver} + else + rm -rf ${memcached_install_dir} + echo "${CFAILURE}memcached-server install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + popd > /dev/null +} + +Install_pecl_memcache() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + if [ "$(${php_install_dir}/bin/php-config --version | awk -F. '{print $1}')" == '5' ]; then + tar xzf memcache-3.0.8.tgz + pushd memcache-3.0.8 > /dev/null + elif [ "$(${php_install_dir}/bin/php-config --version | awk -F. '{print $1}')" == '7' ]; then + tar xzf memcache-${pecl_memcache_oldver}.tgz + pushd memcache-${pecl_memcache_oldver} > /dev/null + else + #git clone https://github.com/websupport-sk/pecl-memcache.git + tar xzf memcache-${pecl_memcache_ver}.tgz + pushd memcache-${pecl_memcache_ver} > /dev/null + fi + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/memcache.so" ]; then + echo "extension=memcache.so" > ${php_install_dir}/etc/php.d/05-memcache.ini + echo "${CSUCCESS}PHP memcache module installed successfully! ${CEND}" + rm -rf memcache-${pecl_memcache_ver} memcache-${pecl_memcache_oldver} memcache-3.0.8 + else + echo "${CFAILURE}PHP memcache module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Install_pecl_memcached() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + # php memcached extension + tar xzf libmemcached-${libmemcached_ver}.tar.gz + patch -d libmemcached-${libmemcached_ver} -p0 < libmemcached-build.patch + pushd libmemcached-${libmemcached_ver} > /dev/null + [ "${PM}" == 'yum' ] && yum -y install cyrus-sasl-devel + [ "${PM}" == 'apt-get' ] && sed -i "s@lthread -pthread -pthreads@lthread -lpthread -pthreads@" ./configure + ./configure --with-memcached=${memcached_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libmemcached-${libmemcached_ver} + + if [ "$(${php_install_dir}/bin/php-config --version | awk -F. '{print $1}')" == '5' ]; then + tar xzf memcached-${pecl_memcached_oldver}.tgz + pushd memcached-${pecl_memcached_oldver} > /dev/null + else + tar xzf memcached-${pecl_memcached_ver}.tgz + pushd memcached-${pecl_memcached_ver} > /dev/null + fi + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/memcached.so" ]; then + cat > ${php_install_dir}/etc/php.d/05-memcached.ini << EOF +extension=memcached.so +memcached.use_sasl=1 +EOF + echo "${CSUCCESS}PHP memcached module installed successfully! ${CEND}" + rm -rf memcached-${pecl_memcached_oldver} memcached-${pecl_memcached_ver} + else + echo "${CFAILURE}PHP memcached module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_memcache() { + if [ -e "${php_install_dir}/etc/php.d/05-memcache.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/05-memcache.ini + echo; echo "${CMSG}PHP memcache module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP memcache module does not exist! ${CEND}" + fi +} + +Uninstall_pecl_memcached() { + if [ -e "${php_install_dir}/etc/php.d/05-memcached.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/05-memcached.ini + echo; echo "${CMSG}PHP memcached module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP memcached module does not exist! ${CEND}" + fi +} diff --git a/include/memory.sh b/include/memory.sh new file mode 100644 index 0000000..6958cc6 --- /dev/null +++ b/include/memory.sh @@ -0,0 +1,48 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export LANG=en_US.UTF-8 +export LANGUAGE=en_US:en +Mem=`free -m | awk '/Mem:/{print $2}'` +Swap=`free -m | awk '/Swap:/{print $2}'` + +if [ $Mem -le 640 ]; then + Mem_level=512M + Memory_limit=64 + THREAD=1 +elif [ $Mem -gt 640 -a $Mem -le 1280 ]; then + Mem_level=1G + Memory_limit=128 +elif [ $Mem -gt 1280 -a $Mem -le 2500 ]; then + Mem_level=2G + Memory_limit=192 +elif [ $Mem -gt 2500 -a $Mem -le 3500 ]; then + Mem_level=3G + Memory_limit=256 +elif [ $Mem -gt 3500 -a $Mem -le 4500 ]; then + Mem_level=4G + Memory_limit=320 +elif [ $Mem -gt 4500 -a $Mem -le 8000 ]; then + Mem_level=6G + Memory_limit=384 +elif [ $Mem -gt 8000 ]; then + Mem_level=8G + Memory_limit=448 +fi + +# add swapfile +if [ ! -e ~/.oneinstack ] && [ "${Swap}" == '0' ] && [ ${Mem} -le 2048 ]; then + echo "${CWARNING}Add Swap file, It may take a few minutes... ${CEND}" + dd if=/dev/zero of=/swapfile count=2048 bs=1M + mkswap /swapfile + swapon /swapfile + chmod 600 /swapfile + [ -z "`grep swapfile /etc/fstab`" ] && echo '/swapfile swap swap defaults 0 0' >> /etc/fstab +fi diff --git a/include/mongodb.sh b/include/mongodb.sh new file mode 100644 index 0000000..f56a7c3 --- /dev/null +++ b/include/mongodb.sh @@ -0,0 +1,79 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MongoDB() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mongod >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -s /sbin/nologin mongod + mkdir -p ${mongo_data_dir};chown mongod.mongod -R ${mongo_data_dir} + tar xzf mongodb-linux-x86_64-${mongodb_ver}.tgz + /bin/mv mongodb-linux-x86_64-${mongodb_ver} ${mongo_install_dir} + /bin/cp ${oneinstack_dir}/init.d/mongod.service /lib/systemd/system/ + sed -i "s@=/usr/local/mongodb@=${mongo_install_dir}@g" /lib/systemd/system/mongod.service + systemctl enable mongod + + cat > /etc/mongod.conf << EOF +# mongod.conf + +# for documentation of all options, see: +# http://docs.mongodb.org/manual/reference/configuration-options/ + +# where to write logging data. +systemLog: + destination: file + logAppend: true + path: ${mongo_data_dir}/mongod.log + +# Where and how to store data. +storage: + dbPath: ${mongo_data_dir} + journal: + enabled: true +# engine: +# mmapv1: +# wiredTiger: + +# how the process runs +processManagement: + fork: true # fork and run in background + pidFilePath: /var/run/mongodb/mongod.pid + +# network interfaces +net: + port: 27017 + bindIp: 0.0.0.0 + unixDomainSocket: + enabled: false + +#security: +# authorization: enabled + +#operationProfiling: +#replication: +#sharding: +EOF + systemctl start mongod + echo ${mongo_install_dir}/bin/mongo 127.0.0.1/admin --eval \"db.createUser\(\{user:\'root\',pwd:\'$dbmongopwd\',roles:[\'userAdminAnyDatabase\']\}\)\" | bash + sed -i 's@^#security:@security:@' /etc/mongod.conf + sed -i 's@^# authorization:@ authorization:@' /etc/mongod.conf + if [ -e "${mongo_install_dir}/bin/mongo" ]; then + sed -i "s+^dbmongopwd.*+dbmongopwd='$dbmongopwd'+" ../options.conf + echo "${CSUCCESS}MongoDB installed successfully! ${CEND}" + rm -rf mongodb-linux-x86_64-${mongodb_ver} + else + rm -rf ${mongo_install_dir} ${mongo_data_dir} + echo "${CFAILURE}MongoDB install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + popd + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mongo_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mongo_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mongo_install_dir}/bin:\1@" /etc/profile + . /etc/profile +} diff --git a/include/mphp.sh b/include/mphp.sh new file mode 100644 index 0000000..fb04e89 --- /dev/null +++ b/include/mphp.sh @@ -0,0 +1,87 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MPHP() { + if [ -e "${php_install_dir}/sbin/php-fpm" ]; then + if [ -e "${php_install_dir}${mphp_ver}/bin/phpize" ]; then + echo "${CWARNING}PHP${mphp_ver} already installed! ${CEND}" + else + [ -e "/lib/systemd/system/php-fpm.service" ] && /bin/mv /lib/systemd/system/php-fpm.service{,_bk} + php_install_dir=${php_install_dir}${mphp_ver} + case "${mphp_ver}" in + 53) + . include/php-5.3.sh + Install_PHP53 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 54) + . include/php-5.4.sh + Install_PHP54 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 55) + . include/php-5.5.sh + Install_PHP55 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 56) + . include/php-5.6.sh + Install_PHP56 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 70) + . include/php-7.0.sh + Install_PHP70 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 71) + . include/php-7.1.sh + Install_PHP71 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 72) + . include/php-7.2.sh + Install_PHP72 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 73) + . include/php-7.3.sh + Install_PHP73 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 74) + . include/php-7.4.sh + Install_PHP74 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 80) + . include/php-8.0.sh + Install_PHP80 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 81) + . include/php-8.1.sh + Install_PHP81 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 82) + . include/php-8.2.sh + Install_PHP82 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 83) + . include/php-8.3.sh + Install_PHP83 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + esac + if [ -e "${php_install_dir}/sbin/php-fpm" ]; then + systemctl stop php-fpm + sed -i "s@/dev/shm/php-cgi.sock@/dev/shm/php${mphp_ver}-cgi.sock@" ${php_install_dir}/etc/php-fpm.conf + [ -e "/lib/systemd/system/php-fpm.service" ] && /bin/mv /lib/systemd/system/php-fpm.service /lib/systemd/system/php${mphp_ver}-fpm.service + [ -e "/lib/systemd/system/php-fpm.service_bk" ] && /bin/mv /lib/systemd/system/php-fpm.service{_bk,} + systemctl enable php${mphp_ver}-fpm + systemctl enable php-fpm + systemctl start php-fpm + systemctl start php${mphp_ver}-fpm + sed -i "s@${php_install_dir}/bin:@@" /etc/profile + fi + fi + else + echo "${CWARNING}To use the multiple PHP versions, You need to use PHP-FPM! ${CEND}" + fi +} diff --git a/include/mysql-5.5.sh b/include/mysql-5.5.sh new file mode 100644 index 0000000..b15ab6f --- /dev/null +++ b/include/mysql-5.5.sh @@ -0,0 +1,220 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MySQL55() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mysql_install_dir}" ] && mkdir -p ${mysql_install_dir} + mkdir -p ${mysql_data_dir};chown mysql:mysql -R ${mysql_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar xzf mysql-${mysql55_ver}-linux-glibc2.12-x86_64.tar.gz + mv mysql-${mysql55_ver}-linux-glibc2.12-x86_64/* ${mysql_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mysql_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/mysql@${mysql_install_dir}@g" ${mysql_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + tar xzf mysql-${mysql55_ver}.tar.gz + pushd mysql-${mysql55_ver} + [ "${armplatform}" == "y" ] && patch -p1 < ../mysql-5.5-fix-arm-client_plugin.patch + cmake . -DCMAKE_INSTALL_PREFIX=${mysql_install_dir} \ + -DMYSQL_DATADIR=${mysql_data_dir} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_READLINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${mysql_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MySQL installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mysql-${mysql55_ver}-*-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mysql-${mysql55_ver} + fi + else + rm -rf ${mysql_install_dir} + echo "${CFAILURE}MySQL install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mysql_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mysql_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mysql_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock + +[mysql] +prompt="MySQL [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${mysql_install_dir} +datadir = ${mysql_data_dir} +pid-file = ${mysql_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${mysql_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mysql_data_dir}/mysql-slow.log + +performance_schema = 0 + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G +myisam_repair_threads = 1 + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mysql_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${mysql_install_dir} --datadir=${mysql_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mysql_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mysql_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mysql_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mysql_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mysql_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${mysql_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.user where Password='' and User not like 'mysql.%';" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.db where User='';" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.proxies_priv where Host!='localhost';" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + [ -e "${mysql_install_dir}/my.cnf" ] && rm -f ${mysql_install_dir}/my.cnf + echo "${mysql_install_dir}/lib" > /etc/ld.so.conf.d/z-mysql.conf + ldconfig + service mysqld stop +} diff --git a/include/mysql-5.6.sh b/include/mysql-5.6.sh new file mode 100644 index 0000000..9c8f91c --- /dev/null +++ b/include/mysql-5.6.sh @@ -0,0 +1,219 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MySQL56() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mysql_install_dir}" ] && mkdir -p ${mysql_install_dir} + mkdir -p ${mysql_data_dir};chown mysql:mysql -R ${mysql_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar xzf mysql-${mysql56_ver}-linux-glibc2.12-x86_64.tar.gz + mv mysql-${mysql56_ver}-linux-glibc2.12-x86_64/* ${mysql_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mysql_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/mysql@${mysql_install_dir}@g" ${mysql_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + tar xzf mysql-${mysql56_ver}.tar.gz + pushd mysql-${mysql56_ver} + cmake . -DCMAKE_INSTALL_PREFIX=${mysql_install_dir} \ + -DMYSQL_DATADIR=${mysql_data_dir} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${mysql_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MySQL installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mysql-${mysql56_ver}-*-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mysql-${mysql56_ver} + fi + else + rm -rf ${mysql_install_dir} + echo "${CFAILURE}MySQL install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mysql_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mysql_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mysql_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock + +[mysql] +prompt="MySQL [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${mysql_install_dir} +datadir = ${mysql_data_dir} +pid-file = ${mysql_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${mysql_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mysql_data_dir}/mysql-slow.log + +performance_schema = 0 +explicit_defaults_for_timestamp + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G +myisam_repair_threads = 1 + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mysql_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${mysql_install_dir} --datadir=${mysql_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mysql_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mysql_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mysql_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mysql_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mysql_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${mysql_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.user where Password='' and User not like 'mysql.%';" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.db where User='';" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.proxies_priv where Host!='localhost';" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + [ -e "${mysql_install_dir}/my.cnf" ] && rm -f ${mysql_install_dir}/my.cnf + echo "${mysql_install_dir}/lib" > /etc/ld.so.conf.d/z-mysql.conf + ldconfig + service mysqld stop +} diff --git a/include/mysql-5.7.sh b/include/mysql-5.7.sh new file mode 100644 index 0000000..3ea7979 --- /dev/null +++ b/include/mysql-5.7.sh @@ -0,0 +1,219 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MySQL57() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mysql_install_dir}" ] && mkdir -p ${mysql_install_dir} + mkdir -p ${mysql_data_dir};chown mysql:mysql -R ${mysql_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar xzf mysql-${mysql57_ver}-linux-glibc2.12-x86_64.tar.gz + mv mysql-${mysql57_ver}-linux-glibc2.12-x86_64/* ${mysql_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mysql_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/mysql@${mysql_install_dir}@g" ${mysql_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + boostVersion2=$(echo ${boost_oldver} | awk -F. '{print $1"_"$2"_"$3}') + tar xzf boost_${boostVersion2}.tar.gz + tar xzf mysql-${mysql57_ver}.tar.gz + pushd mysql-${mysql57_ver} + cmake . -DCMAKE_INSTALL_PREFIX=${mysql_install_dir} \ + -DMYSQL_DATADIR=${mysql_data_dir} \ + -DDOWNLOAD_BOOST=1 \ + -DWITH_BOOST=../boost_${boostVersion2} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${mysql_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MySQL installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mysql-${mysql57_ver}-*-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mysql-${mysql57_ver} boost_${boostVersion2} + fi + else + rm -rf ${mysql_install_dir} + echo "${CFAILURE}MySQL install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mysql_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mysql_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mysql_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock + +[mysql] +prompt="MySQL [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${mysql_install_dir} +datadir = ${mysql_data_dir} +pid-file = ${mysql_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${mysql_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mysql_data_dir}/mysql-slow.log + +performance_schema = 0 +explicit_defaults_for_timestamp + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +#default-storage-engine = MyISAM +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mysql_install_dir}/bin/mysqld --initialize-insecure --user=mysql --basedir=${mysql_install_dir} --datadir=${mysql_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mysql_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mysql_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mysql_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mysql_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mysql_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${mysql_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + [ -e "${mysql_install_dir}/my.cnf" ] && rm -f ${mysql_install_dir}/my.cnf + echo "${mysql_install_dir}/lib" > /etc/ld.so.conf.d/z-mysql.conf + ldconfig + service mysqld stop +} diff --git a/include/mysql-8.0.sh b/include/mysql-8.0.sh new file mode 100644 index 0000000..1174394 --- /dev/null +++ b/include/mysql-8.0.sh @@ -0,0 +1,220 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MySQL80() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mysql_install_dir}" ] && mkdir -p ${mysql_install_dir} + mkdir -p ${mysql_data_dir};chown mysql:mysql -R ${mysql_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar xJf mysql-${mysql80_ver}-linux-glibc2.12-x86_64.tar.xz + mv mysql-${mysql80_ver}-linux-glibc2.12-x86_64/* ${mysql_install_dir} + sed -i "s@/usr/local/mysql@${mysql_install_dir}@g" ${mysql_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + boostVersion2=$(echo ${boost_ver} | awk -F. '{print $1"_"$2"_"$3}') + tar xzf boost_${boostVersion2}.tar.gz + tar xzf mysql-${mysql80_ver}.tar.gz + pushd mysql-${mysql80_ver} + [ -e "/usr/bin/cmake3" ] && CMAKE=cmake3 || CMAKE=cmake + $CMAKE . -DCMAKE_INSTALL_PREFIX=${mysql_install_dir} \ + -DMYSQL_DATADIR=${mysql_data_dir} \ + -DDOWNLOAD_BOOST=1 \ + -DWITH_BOOST=../boost_${boostVersion2} \ + -DFORCE_INSOURCE_BUILD=1 \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DENABLED_LOCAL_INFILE=1 \ + -DFORCE_INSOURCE_BUILD=1 \ + -DCMAKE_C_COMPILER=/usr/bin/gcc \ + -DCMAKE_CXX_COMPILER=/usr/bin/g++ \ + -DDEFAULT_CHARSET=utf8mb4 + make -j ${THREAD} + make install + popd + fi + + # backup openssl so + #[ ! -e "${mysql_install_dir}/lib/lib_bk" ] && mkdir ${mysql_install_dir}/lib/lib_bk + #/bin/mv ${mysql_install_dir}/lib/{libssl,libcrypto}.so* ${mysql_install_dir}/lib/lib_bk/ + + if [ -d "${mysql_install_dir}/support-files" ]; then + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mysql_install_dir}/bin/mysqld_safe + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MySQL installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mysql-${mysql80_ver}-*-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mysql-${mysql80_ver} boost_${boostVersion2} + fi + else + rm -rf ${mysql_install_dir} + echo "${CFAILURE}MySQL install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mysql_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mysql_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mysql_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock +default-character-set = utf8mb4 + +[mysql] +prompt="MySQL [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock +default_authentication_plugin = mysql_native_password + +basedir = ${mysql_install_dir} +datadir = ${mysql_data_dir} +pid-file = ${mysql_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 +collation-server = utf8mb4_0900_ai_ci + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +binlog_expire_logs_seconds = 604800 + +log_error = ${mysql_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mysql_data_dir}/mysql-slow.log + +performance_schema = 0 +explicit_defaults_for_timestamp + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +#default-storage-engine = MyISAM +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mysql_install_dir}/bin/mysqld --initialize-insecure --user=mysql --basedir=${mysql_install_dir} --datadir=${mysql_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mysql_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mysql_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mysql_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mysql_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mysql_install_dir}/bin/mysql -uroot -hlocalhost -e "create user root@'127.0.0.1' identified by \"${dbrootpwd}\";" + ${mysql_install_dir}/bin/mysql -uroot -hlocalhost -e "grant all privileges on *.* to root@'127.0.0.1' with grant option;" + ${mysql_install_dir}/bin/mysql -uroot -hlocalhost -e "grant all privileges on *.* to root@'localhost' with grant option;" + ${mysql_install_dir}/bin/mysql -uroot -hlocalhost -e "alter user root@'localhost' identified by \"${dbrootpwd}\";" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + [ -e "${mysql_install_dir}/my.cnf" ] && rm -f ${mysql_install_dir}/my.cnf + echo "${mysql_install_dir}/lib" > /etc/ld.so.conf.d/z-mysql.conf + ldconfig + service mysqld stop +} diff --git a/include/mysql-8.2.sh b/include/mysql-8.2.sh new file mode 100644 index 0000000..7c8c919 --- /dev/null +++ b/include/mysql-8.2.sh @@ -0,0 +1,220 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_MySQL82() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${mysql_install_dir}" ] && mkdir -p ${mysql_install_dir} + mkdir -p ${mysql_data_dir};chown mysql:mysql -R ${mysql_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar xJf mysql-${mysql82_ver}-linux-glibc2.17-x86_64.tar.xz + mv mysql-${mysql82_ver}-linux-glibc2.17-x86_64/* ${mysql_install_dir} + sed -i "s@/usr/local/mysql@${mysql_install_dir}@g" ${mysql_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + boostVersion2=$(echo ${boost_ver} | awk -F. '{print $1"_"$2"_"$3}') + tar xzf boost_${boostVersion2}.tar.gz + tar xzf mysql-${mysql82_ver}.tar.gz + pushd mysql-${mysql82_ver} + [ -e "/usr/bin/cmake3" ] && CMAKE=cmake3 || CMAKE=cmake + $CMAKE . -DCMAKE_INSTALL_PREFIX=${mysql_install_dir} \ + -DMYSQL_DATADIR=${mysql_data_dir} \ + -DDOWNLOAD_BOOST=1 \ + -DWITH_BOOST=../boost_${boostVersion2} \ + -DFORCE_INSOURCE_BUILD=1 \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DENABLED_LOCAL_INFILE=1 \ + -DFORCE_INSOURCE_BUILD=1 \ + -DCMAKE_C_COMPILER=/usr/bin/gcc \ + -DCMAKE_CXX_COMPILER=/usr/bin/g++ \ + -DDEFAULT_CHARSET=utf8mb4 + make -j ${THREAD} + make install + popd + fi + + # backup openssl so + #[ ! -e "${mysql_install_dir}/lib/lib_bk" ] && mkdir ${mysql_install_dir}/lib/lib_bk + #/bin/mv ${mysql_install_dir}/lib/{libssl,libcrypto}.so* ${mysql_install_dir}/lib/lib_bk/ + + if [ -d "${mysql_install_dir}/support-files" ]; then + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mysql_install_dir}/bin/mysqld_safe + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}MySQL installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf mysql-${mysql82_ver}-*-x86_64 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf mysql-${mysql82_ver} boost_${boostVersion2} + fi + else + rm -rf ${mysql_install_dir} + echo "${CFAILURE}MySQL install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${mysql_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${mysql_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${mysql_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock +default-character-set = utf8mb4 + +[mysql] +prompt="MySQL [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock +default_authentication_plugin = mysql_native_password + +basedir = ${mysql_install_dir} +datadir = ${mysql_data_dir} +pid-file = ${mysql_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 +collation-server = utf8mb4_0900_ai_ci + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +binlog_expire_logs_seconds = 604800 + +log_error = ${mysql_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${mysql_data_dir}/mysql-slow.log + +performance_schema = 0 +explicit_defaults_for_timestamp + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +#default-storage-engine = MyISAM +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${mysql_install_dir}/bin/mysqld --initialize-insecure --user=mysql --basedir=${mysql_install_dir} --datadir=${mysql_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${mysql_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${mysql_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${mysql_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${mysql_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${mysql_install_dir}/bin/mysql -uroot -hlocalhost -e "create user root@'127.0.0.1' identified by \"${dbrootpwd}\";" + ${mysql_install_dir}/bin/mysql -uroot -hlocalhost -e "grant all privileges on *.* to root@'127.0.0.1' with grant option;" + ${mysql_install_dir}/bin/mysql -uroot -hlocalhost -e "grant all privileges on *.* to root@'localhost' with grant option;" + ${mysql_install_dir}/bin/mysql -uroot -hlocalhost -e "alter user root@'localhost' identified by \"${dbrootpwd}\";" + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + [ -e "${mysql_install_dir}/my.cnf" ] && rm -f ${mysql_install_dir}/my.cnf + echo "${mysql_install_dir}/lib" > /etc/ld.so.conf.d/z-mysql.conf + ldconfig + service mysqld stop +} diff --git a/include/nginx.sh b/include/nginx.sh new file mode 100644 index 0000000..a69444f --- /dev/null +++ b/include/nginx.sh @@ -0,0 +1,99 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Nginx() { + pushd ${oneinstack_dir}/src > /dev/null + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf pcre-${pcre_ver}.tar.gz + tar xzf nginx-${nginx_ver}.tar.gz + tar xzf openssl-${openssl11_ver}.tar.gz + pushd nginx-${nginx_ver} > /dev/null + # Modify Nginx version + #sed -i 's@#define NGINX_VERSION.*$@#define NGINX_VERSION "1.2"@' src/core/nginx.h + #sed -i 's@#define NGINX_VER.*NGINX_VERSION$@#define NGINX_VER "Linuxeye/" NGINX_VERSION@' src/core/nginx.h + #sed -i 's@Server: nginx@Server: linuxeye@' src/http/ngx_http_header_filter_module.c + + # close debug + sed -i 's@CFLAGS="$CFLAGS -g"@#CFLAGS="$CFLAGS -g"@' auto/cc/gcc + + [ ! -d "${nginx_install_dir}" ] && mkdir -p ${nginx_install_dir} + ./configure --prefix=${nginx_install_dir} --user=${run_user} --group=${run_group} --with-http_stub_status_module --with-http_sub_module --with-http_v2_module --with-http_ssl_module --with-stream --with-stream_ssl_preread_module --with-stream_ssl_module --with-http_gzip_static_module --with-http_realip_module --with-http_flv_module --with-http_mp4_module --with-openssl=../openssl-${openssl11_ver} --with-pcre=../pcre-${pcre_ver} --with-pcre-jit --with-ld-opt='-ljemalloc' ${nginx_modules_options} + make -j ${THREAD} && make install + if [ -e "${nginx_install_dir}/conf/nginx.conf" ]; then + popd > /dev/null + #rm -rf pcre-${pcre_ver}* openssl-${openssl11_ver}* nginx-${nginx_ver}* ${nginx_install_dir}* + echo "${CSUCCESS}Nginx installed successfully! ${CEND}" + else + rm -rf pcre-${pcre_ver}* openssl-${openssl11_ver}* nginx-${nginx_ver}* ${nginx_install_dir}* + echo "${CFAILURE}Nginx install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${nginx_install_dir}/sbin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${nginx_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${nginx_install_dir}/sbin:\1@" /etc/profile + . /etc/profile + + /bin/cp ../init.d/nginx.service /lib/systemd/system/ + sed -i "s@/usr/local/nginx@${nginx_install_dir}@g" /lib/systemd/system/nginx.service + systemctl enable nginx + + mv ${nginx_install_dir}/conf/nginx.conf{,_bk} + if [ "${apache_flag}" == 'y' ] || [ -e "${apache_install_dir}/bin/httpd" ]; then + /bin/cp ../config/nginx_apache.conf ${nginx_install_dir}/conf/nginx.conf + elif { [[ ${tomcat_option} =~ ^[1-4]$ ]] || [ -e "${tomcat_install_dir}/conf/server.xml" ]; } && { [[ ! ${php_option} =~ ^[1-9]$|^1[0-1]$ ]] && [ ! -e "${php_install_dir}/bin/php" ]; }; then + /bin/cp ../config/nginx_tomcat.conf ${nginx_install_dir}/conf/nginx.conf + else + /bin/cp ../config/nginx.conf ${nginx_install_dir}/conf/nginx.conf + [[ "${php_option}" =~ ^[1-9]$|^1[0-1]$ ]] && [ -z "`grep '/php-fpm_status' ${nginx_install_dir}/conf/nginx.conf`" ] && sed -i "s@index index.html index.php;@index index.html index.php;\n location ~ /php-fpm_status {\n #fastcgi_pass remote_php_ip:9000;\n fastcgi_pass unix:/dev/shm/php-cgi.sock;\n fastcgi_index index.php;\n include fastcgi.conf;\n allow 127.0.0.1;\n deny all;\n }@" ${nginx_install_dir}/conf/nginx.conf + fi + cat > ${nginx_install_dir}/conf/proxy.conf << EOF +proxy_connect_timeout 300s; +proxy_send_timeout 900; +proxy_read_timeout 900; +proxy_buffer_size 32k; +proxy_buffers 4 64k; +proxy_busy_buffers_size 128k; +proxy_redirect off; +proxy_hide_header Vary; +proxy_set_header Accept-Encoding ''; +proxy_set_header Referer \$http_referer; +proxy_set_header Cookie \$http_cookie; +proxy_set_header Host \$host; +proxy_set_header X-Real-IP \$remote_addr; +proxy_set_header X-Forwarded-For \$proxy_add_x_forwarded_for; +proxy_set_header X-Forwarded-Proto \$scheme; +EOF + sed -i "s@/data/wwwroot/default@${wwwroot_dir}/default@" ${nginx_install_dir}/conf/nginx.conf + sed -i "s@/data/wwwlogs@${wwwlogs_dir}@g" ${nginx_install_dir}/conf/nginx.conf + sed -i "s@^user www www@user ${run_user} ${run_group}@" ${nginx_install_dir}/conf/nginx.conf + + # logrotate nginx log + cat > /etc/logrotate.d/nginx << EOF +${wwwlogs_dir}/*nginx.log { + daily + rotate 5 + missingok + dateext + compress + notifempty + sharedscripts + postrotate + [ -e /var/run/nginx.pid ] && kill -USR1 \`cat /var/run/nginx.pid\` + endscript +} +EOF + popd > /dev/null + ldconfig + systemctl start nginx +} diff --git a/include/ngx_lua_waf.sh b/include/ngx_lua_waf.sh new file mode 100644 index 0000000..942fb95 --- /dev/null +++ b/include/ngx_lua_waf.sh @@ -0,0 +1,187 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Nginx_lua_waf() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${nginx_install_dir}/sbin/nginx" ] && echo "${CWARNING}Nginx is not installed on your system! ${CEND}" && exit 1 + if [ ! -e "/usr/local/lib/libluajit-5.1.so.2.1.0" ]; then + [ -e "/usr/local/lib/libluajit-5.1.so.2.0.5" ] && find /usr/local -name *luajit* | xargs rm -rf + src_url=${mirror_link}/oneinstack/src/luajit2-${luajit2_ver}.tar.gz && Download_src + tar xzf luajit2-${luajit2_ver}.tar.gz + pushd luajit2-${luajit2_ver} + make && make install + [ ! -e "/usr/local/lib/libluajit-5.1.so.2.1.0" ] && { echo "${CFAILURE}LuaJIT install failed! ${CEND}"; kill -9 $$; exit 1; } + popd > /dev/null + rm -rf luajit2-${luajit2_ver} + fi + + src_url=${mirror_link}/oneinstack/src/lua-resty-core-${lua_resty_core_ver}.tar.gz && Download_src + tar xzf lua-resty-core-${lua_resty_core_ver}.tar.gz + pushd lua-resty-core-${lua_resty_core_ver} + make install + popd > /dev/null + rm -rf lua-resty-core-${lua_resty_core_ver} + + src_url=${mirror_link}/oneinstack/src/lua-resty-lrucache-${lua_resty_lrucache_ver}.tar.gz && Download_src + tar xzf lua-resty-lrucache-${lua_resty_lrucache_ver}.tar.gz + pushd lua-resty-lrucache-${lua_resty_lrucache_ver} + make install + popd > /dev/null + rm -rf lua-resty-lrucache-${lua_resty_lrucache_ver} + + [ ! -h "/usr/local/share/lua/5.1" ] && { rm -rf /usr/local/share/lua/5.1 ; ln -s /usr/local/lib/lua /usr/local/share/lua/5.1; } + if [ ! -e "/usr/local/lib/lua/5.1/cjson.so" ]; then + src_url=${mirror_link}/oneinstack/src/lua-cjson-${lua_cjson_ver}.tar.gz && Download_src + tar xzf lua-cjson-${lua_cjson_ver}.tar.gz + pushd lua-cjson-${lua_cjson_ver} + sed -i 's@^LUA_INCLUDE_DIR.*@&/luajit-2.1@' Makefile + make && make install + [ ! -e "/usr/local/lib/lua/5.1/cjson.so" ] && { echo "${CFAILURE}lua-cjson install failed! ${CEND}"; kill -9 $$; exit 1; } + popd > /dev/null + fi + ${nginx_install_dir}/sbin/nginx -V &> $$ + nginx_configure_args_tmp=`cat $$ | grep 'configure arguments:' | awk -F: '{print $2}'` + rm -rf $$ + nginx_configure_args=`echo ${nginx_configure_args_tmp} | sed "s@--with-openssl=../openssl-\w.\w.\w\+ @--with-openssl=../openssl-${openssl11_ver} @" | sed "s@--with-pcre=../pcre-\w.\w\+ @--with-pcre=../pcre-${pcre_ver} @"` + if [ -z "`echo ${nginx_configure_args} | grep lua-nginx-module`" ]; then + src_url=http://nginx.org/download/nginx-${nginx_ver}.tar.gz && Download_src + src_url=https://www.openssl.org/source/openssl-${openssl11_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/pcre-${pcre_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/ngx_devel_kit.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/lua-nginx-module-${lua_nginx_module_ver}.tar.gz && Download_src + tar xzf nginx-${nginx_ver}.tar.gz + tar xzf openssl-${openssl11_ver}.tar.gz + tar xzf pcre-${pcre_ver}.tar.gz + tar xzf ngx_devel_kit.tar.gz + tar xzf lua-nginx-module-${lua_nginx_module_ver}.tar.gz + pushd nginx-${nginx_ver} + make clean + sed -i 's@CFLAGS="$CFLAGS -g"@#CFLAGS="$CFLAGS -g"@' auto/cc/gcc # close debug + export LUAJIT_LIB=/usr/local/lib + export LUAJIT_INC=/usr/local/include/luajit-2.1 + ./configure ${nginx_configure_args} --with-ld-opt="-Wl,-rpath,/usr/local/lib" --add-module=../lua-nginx-module-${lua_nginx_module_ver} --add-module=../ngx_devel_kit + make -j ${THREAD} + if [ -f "objs/nginx" ]; then + /bin/mv ${nginx_install_dir}/sbin/nginx{,`date +%m%d`} + /bin/cp objs/nginx ${nginx_install_dir}/sbin/nginx + kill -USR2 `cat /var/run/nginx.pid` + sleep 1 + kill -QUIT `cat /var/run/nginx.pid.oldbin` + popd > /dev/null + echo "${CSUCCESS}lua-nginx-module installed successfully! ${CEND}" + sed -i "s@^nginx_modules_options='\(.*\)'@nginx_modules_options=\'\1 --with-ld-opt=\"-Wl,-rpath,/usr/local/lib\" --add-module=../lua-nginx-module-${lua_nginx_module_ver} --add-module=../ngx_devel_kit\'@" ../options.conf + rm -rf nginx-${nginx_ver} + else + echo "${CFAILURE}lua-nginx-module install failed! ${CEND}" + kill -9 $$; exit 1; + fi + fi + popd > /dev/null +} + +Tengine_lua_waf() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${tengine_install_dir}/sbin/nginx" ] && echo "${CWARNING}Tengine is not installed on your system! ${CEND}" && exit 1 + if [ ! -e "/usr/local/lib/libluajit-5.1.so.2.1.0" ]; then + [ -e "/usr/local/lib/libluajit-5.1.so.2.0.5" ] && find /usr/local -name *luajit* | xargs rm -rf + src_url=${mirror_link}/oneinstack/src/luajit2-${luajit2_ver}.tar.gz && Download_src + tar xzf luajit2-${luajit2_ver}.tar.gz + pushd luajit2-${luajit2_ver} + make && make install + [ ! -e "/usr/local/lib/libluajit-5.1.so.2.1.0" ] && { echo "${CFAILURE}LuaJIT install failed! ${CEND}"; kill -9 $$; exit 1; } + popd > /dev/null + fi + if [ ! -e "/usr/local/lib/lua/5.1/cjson.so" ]; then + src_url=${mirror_link}/oneinstack/src/lua-cjson-${lua_cjson_ver}.tar.gz && Download_src + tar xzf lua-cjson-${lua_cjson_ver}.tar.gz + pushd lua-cjson-${lua_cjson_ver} + sed -i 's@^LUA_INCLUDE_DIR.*@&/luajit-2.1@' Makefile + make && make install + [ ! -e "/usr/local/lib/lua/5.1/cjson.so" ] && { echo "${CFAILURE}lua-cjson install failed! ${CEND}"; kill -9 $$; exit 1; } + popd > /dev/null + fi + ${tengine_install_dir}/sbin/nginx -V &> $$ + tengine_configure_args_tmp=`cat $$ | grep 'configure arguments:' | awk -F: '{print $2}'` + rm -rf $$ + tengine_configure_args=`echo ${tengine_configure_args_tmp} | sed "s@--with-openssl=../openssl-\w.\w.\w\+ @--with-openssl=../openssl-${openssl11_ver} @" | sed "s@--with-pcre=../pcre-\w.\w\+ @--with-pcre=../pcre-${pcre_ver} @"` + if [ -z "`echo ${tengine_configure_args} | grep lua`" ]; then + src_url=http://tengine.taobao.org/download/tengine-${tengine_ver}.tar.gz && Download_src + src_url=https://www.openssl.org/source/openssl-${openssl11_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/pcre-${pcre_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/ngx_devel_kit.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/lua-nginx-module.tar.gz && Download_src + tar xzf tengine-${tengine_ver}.tar.gz + tar xzf openssl-${openssl11_ver}.tar.gz + tar xzf pcre-${pcre_ver}.tar.gz + tar xzf ngx_devel_kit.tar.gz + tar xzf lua-nginx-module.tar.gz + pushd tengine-${tengine_ver} + make clean + export LUAJIT_LIB=/usr/local/lib + export LUAJIT_INC=/usr/local/include/luajit-2.1 + ./configure ${tengine_configure_args} --with-ld-opt="-Wl,-rpath,/usr/local/lib" --add-module=../lua-nginx-module --add-module=../ngx_devel_kit + make -j ${THREAD} + if [ -f "objs/nginx" ]; then + /bin/mv ${tengine_install_dir}/sbin/nginx{,`date +%m%d`} + /bin/mv ${tengine_install_dir}/modules{,`date +%m%d`} + /bin/cp objs/nginx ${tengine_install_dir}/sbin/nginx + chmod +x ${tengine_install_dir}/sbin/* + make install + kill -USR2 `cat /var/run/nginx.pid` + sleep 1 + kill -QUIT `cat /var/run/nginx.pid.oldbin` + popd > /dev/null + sed -i "s@^nginx_modules_options='\(.*\)'@nginx_modules_options=\'\1 --with-ld-opt=\"-Wl,-rpath,/usr/local/lib\" --add-module=../lua-nginx-module --add-module=../ngx_devel_kit\'@" ../options.conf + echo "${CSUCCESS}lua_module installed successfully! ${CEND}" + rm -rf tengine-${tengine_ver} + else + echo "${CFAILURE}lua_module install failed! ${CEND}" + kill -9 $$; exit 1; + fi + fi + popd > /dev/null +} + +enable_lua_waf() { + pushd ${oneinstack_dir}/src > /dev/null + . ../include/check_dir.sh + rm -f ngx_lua_waf.tar.gz + src_url=${mirror_link}/oneinstack/src/ngx_lua_waf.tar.gz && Download_src + tar xzf ngx_lua_waf.tar.gz -C ${web_install_dir}/conf + [ -e "${web_install_dir}/conf/resty" ] && /bin/mv ${web_install_dir}/conf/resty{,_bak} + sed -i "s@/usr/local/nginx@${web_install_dir}@g" ${web_install_dir}/conf/waf.conf + sed -i "s@/usr/local/nginx@${web_install_dir}@" ${web_install_dir}/conf/waf/config.lua + sed -i "s@/data/wwwlogs@${wwwlogs_dir}@" ${web_install_dir}/conf/waf/config.lua + [ -z "`grep 'include waf.conf;' ${web_install_dir}/conf/nginx.conf`" ] && sed -i "s@ vhost/\*.conf;@&\n include waf.conf;@" ${web_install_dir}/conf/nginx.conf + ${web_install_dir}/sbin/nginx -t + if [ $? -eq 0 ]; then + service nginx reload + echo "${CSUCCESS}ngx_lua_waf enabled successfully! ${CEND}" + chown ${run_user}:${run_group} ${wwwlogs_dir} + else + echo "${CFAILURE}ngx_lua_waf enable failed! ${CEND}" + fi + popd > /dev/null +} + +disable_lua_waf() { + pushd ${oneinstack_dir}/src > /dev/null + . ../include/check_dir.sh + sed -i '/include waf.conf;/d' ${web_install_dir}/conf/nginx.conf + ${web_install_dir}/sbin/nginx -t + if [ $? -eq 0 ]; then + rm -rf ${web_install_dir}/conf/{waf,waf.conf} + service nginx reload + echo "${CSUCCESS}ngx_lua_waf disabled successfully! ${CEND}" + else + echo "${CFAILURE}ngx_lua_waf disable failed! ${CEND}" + fi + popd > /dev/null +} diff --git a/include/nodejs.sh b/include/nodejs.sh new file mode 100644 index 0000000..e55b5f9 --- /dev/null +++ b/include/nodejs.sh @@ -0,0 +1,35 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Nodejs() { + pushd ${oneinstack_dir}/src > /dev/null + tar xzf node-v${nodejs_ver}-linux-${SYS_ARCH_n}.tar.gz + /bin/mv node-v${nodejs_ver}-linux-${SYS_ARCH_n} ${nodejs_install_dir} + if [ -e "${nodejs_install_dir}/bin/node" ]; then + cat > /etc/profile.d/nodejs.sh << EOF +export NODE_HOME=${nodejs_install_dir} +export PATH=\$NODE_HOME/bin:\$PATH +EOF + . /etc/profile + echo "${CSUCCESS}Nodejs installed successfully! ${CEND}" + else + echo "${CFAILURE}Nodejs install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + popd > /dev/null +} + +Uninstall_Nodejs() { + if [ -e "${nodejs_install_dir}" ]; then + rm -rf ${nodejs_install_dir} /etc/profile.d/nodejs.sh + echo "${CMSG}Nodejs uninstall completed! ${CEND}" + fi +} + diff --git a/include/ois.aarch64 b/include/ois.aarch64 new file mode 100644 index 0000000..48720a1 Binary files /dev/null and b/include/ois.aarch64 differ diff --git a/include/ois.x86_64 b/include/ois.x86_64 new file mode 100644 index 0000000..38aeca7 Binary files /dev/null and b/include/ois.x86_64 differ diff --git a/include/openjdk-11.sh b/include/openjdk-11.sh new file mode 100644 index 0000000..6dcae2b --- /dev/null +++ b/include/openjdk-11.sh @@ -0,0 +1,41 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_OpenJDK11() { + if [ "${Family}" == 'rhel' ]; then + yum -y install java-11-openjdk-devel + JAVA_HOME=/usr/lib/jvm/java-11-openjdk + elif [ "${Family}" == 'debian' ]; then + apt-get --no-install-recommends -y install openjdk-11-jdk + JAVA_HOME=/usr/lib/jvm/java-11-openjdk-${SYS_ARCH} + elif [ "${Family}" == 'ubuntu' ]; then + if [[ "${Ubuntu_ver}" =~ ^16$ ]]; then + cat ${oneinstack_dir}/src/adoptium.key | sudo apt-key add - + apt-add-repository --yes https://mirrors.tuna.tsinghua.edu.cn/Adoptium/deb + apt -y update + apt-get --no-install-recommends -y install temurin-11-jdk + JAVA_HOME=/usr/lib/jvm/temurin-11-jdk-${SYS_ARCH} + else + apt-get --no-install-recommends -y install openjdk-11-jdk + JAVA_HOME=/usr/lib/jvm/java-11-openjdk-${SYS_ARCH} + fi + fi + if [ -e "${JAVA_HOME}/bin/java" ]; then + cat > /etc/profile.d/openjdk.sh << EOF +export JAVA_HOME=${JAVA_HOME} +export CLASSPATH=\$JAVA_HOME/lib/tools.jar:\$JAVA_HOME/lib/dt.jar:\$JAVA_HOME/lib +EOF + . /etc/profile.d/openjdk.sh + echo "${CSUCCESS}OpenJDK11 installed successfully! ${CEND}" + else + echo "${CFAILURE}OpenJDK11 install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi +} diff --git a/include/openjdk-17.sh b/include/openjdk-17.sh new file mode 100644 index 0000000..9750422 --- /dev/null +++ b/include/openjdk-17.sh @@ -0,0 +1,62 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_OpenJDK17() { + if [ "${Family}" == 'rhel' ]; then + if [[ "${RHEL_ver}" =~ ^7$ ]]; then + cat > /etc/yum.repos.d/adoptium.repo << EOF +[Adoptium] +name=Adoptium +baseurl=https://mirrors.tuna.tsinghua.edu.cn/Adoptium/rpm/rhel\$releasever-\$basearch/ +enabled=1 +gpgcheck=0 +EOF + yum -y install temurin-17-jdk + JAVA_HOME=/usr/lib/jvm/temurin-17-jdk + else + yum -y install java-17-openjdk-devel + JAVA_HOME=/usr/lib/jvm/java-17-openjdk + fi + elif [ "${Family}" == 'debian' ]; then + if [[ "${Debian_ver}" =~ ^9$|^10$ ]]; then + #wget -qO - https://packages.adoptium.net/artifactory/api/gpg/key/public | apt-key add - + cat ${oneinstack_dir}/src/adoptium.key | sudo apt-key add - + apt-add-repository --yes https://mirrors.tuna.tsinghua.edu.cn/Adoptium/deb + apt -y update + apt-get --no-install-recommends -y install temurin-17-jdk + JAVA_HOME=/usr/lib/jvm/temurin-17-jdk-${SYS_ARCH} + else + apt-get --no-install-recommends -y install openjdk-17-jdk + JAVA_HOME=/usr/lib/jvm/java-17-openjdk-${SYS_ARCH} + fi + elif [ "${Family}" == 'ubuntu' ]; then + if [[ "${Ubuntu_ver}" =~ ^16$ ]]; then + cat ${oneinstack_dir}/src/adoptium.key | sudo apt-key add - + apt-add-repository --yes https://mirrors.tuna.tsinghua.edu.cn/Adoptium/deb + apt -y update + apt-get --no-install-recommends -y install temurin-17-jdk + JAVA_HOME=/usr/lib/jvm/temurin-17-jdk-${SYS_ARCH} + else + apt-get --no-install-recommends -y install openjdk-17-jdk + JAVA_HOME=/usr/lib/jvm/java-17-openjdk-${SYS_ARCH} + fi + fi + if [ -e "${JAVA_HOME}/bin/java" ]; then + cat > /etc/profile.d/openjdk.sh << EOF +export JAVA_HOME=${JAVA_HOME} +export CLASSPATH=\$JAVA_HOME/lib/tools.jar:\$JAVA_HOME/lib/dt.jar:\$JAVA_HOME/lib +EOF + . /etc/profile.d/openjdk.sh + echo "${CSUCCESS}OpenJDK17 installed successfully! ${CEND}" + else + echo "${CFAILURE}OpenJDK17 install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi +} diff --git a/include/openjdk-8.sh b/include/openjdk-8.sh new file mode 100644 index 0000000..a778e8d --- /dev/null +++ b/include/openjdk-8.sh @@ -0,0 +1,42 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_OpenJDK8() { + if [ "${Family}" == 'rhel' ]; then + yum -y install java-1.8.0-openjdk-devel + JAVA_HOME=/usr/lib/jvm/java-1.8.0-openjdk + elif [ "${Family}" == 'debian' ]; then + if [[ "${Debian_ver}" =~ ^10$|^11$|^12$ ]]; then + #wget -qO - https://packages.adoptium.net/artifactory/api/gpg/key/public | apt-key add - + cat ${oneinstack_dir}/src/adoptium.key | sudo apt-key add - + apt-add-repository --yes https://mirrors.tuna.tsinghua.edu.cn/Adoptium/deb + apt -y update + apt-get --no-install-recommends -y install temurin-8-jdk + JAVA_HOME=/usr/lib/jvm/temurin-8-jdk-${SYS_ARCH} + elif [[ "${Debian_ver}" =~ ^9$ ]]; then + apt-get --no-install-recommends -y install openjdk-8-jdk + JAVA_HOME=/usr/lib/jvm/java-8-openjdk-${SYS_ARCH} + fi + elif [ "${Family}" == 'ubuntu' ]; then + apt-get --no-install-recommends -y install openjdk-8-jdk + JAVA_HOME=/usr/lib/jvm/java-8-openjdk-${SYS_ARCH} + fi + if [ -e "${JAVA_HOME}/bin/java" ]; then + cat > /etc/profile.d/openjdk.sh << EOF +export JAVA_HOME=${JAVA_HOME} +export CLASSPATH=\$JAVA_HOME/lib/tools.jar:\$JAVA_HOME/lib/dt.jar:\$JAVA_HOME/lib +EOF + . /etc/profile.d/openjdk.sh + echo "${CSUCCESS}OpenJDK8 installed successfully! ${CEND}" + else + echo "${CFAILURE}OpenJDK8 install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi +} diff --git a/include/openresty.sh b/include/openresty.sh new file mode 100644 index 0000000..3d9612a --- /dev/null +++ b/include/openresty.sh @@ -0,0 +1,95 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_OpenResty() { + pushd ${oneinstack_dir}/src > /dev/null + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf pcre-${pcre_ver}.tar.gz + tar xzf openresty-${openresty_ver}.tar.gz + tar xzf openssl-${openssl11_ver}.tar.gz + pushd openresty-${openresty_ver} > /dev/null + + # close debug + sed -i 's@CFLAGS="$CFLAGS -g"@#CFLAGS="$CFLAGS -g"@' bundle/nginx-${openresty_ver%.*}/auto/cc/gcc # close debug + + [ ! -d "${openresty_install_dir}" ] && mkdir -p ${openresty_install_dir} + ./configure --prefix=${openresty_install_dir} --user=${run_user} --group=${run_group} --with-http_stub_status_module --with-http_sub_module --with-http_v2_module --with-http_ssl_module --with-http_gzip_static_module --with-http_realip_module --with-http_flv_module --with-http_mp4_module --with-openssl=../openssl-${openssl11_ver} --with-pcre=../pcre-${pcre_ver} --with-pcre-jit --with-ld-opt='-ljemalloc -Wl,-u,pcre_version' ${nginx_modules_options} + make -j ${THREAD} && make install + if [ -e "${openresty_install_dir}/nginx/conf/nginx.conf" ]; then + popd > /dev/null + rm -rf pcre-${pcre_ver}* openssl-${openssl11_ver}* openresty-${openresty_ver}* ${openresty_install_dir}* + echo "${CSUCCESS}OpenResty installed successfully! ${CEND}" + else + rm -rf pcre-${pcre_ver}* openssl-${openssl11_ver}* openresty-${openresty_ver}* ${openresty_install_dir}* + echo "${CFAILURE}OpenResty install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${openresty_install_dir}/nginx/sbin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${openresty_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${openresty_install_dir}/nginx/sbin:\1@" /etc/profile + . /etc/profile + + /bin/cp ../init.d/nginx.service /lib/systemd/system/ + sed -i "s@/usr/local/nginx@${openresty_install_dir}/nginx@g" /lib/systemd/system/nginx.service + systemctl enable nginx + + mv ${openresty_install_dir}/nginx/conf/nginx.conf{,_bk} + if [ "${apache_flag}" == 'y' ] || [ -e "${apache_install_dir}/bin/httpd" ]; then + /bin/cp ../config/nginx_apache.conf ${openresty_install_dir}/nginx/conf/nginx.conf + elif { [[ ${tomcat_option} =~ ^[1-4]$ ]] || [ -e "${tomcat_install_dir}/conf/server.xml" ]; } && { [[ ! ${php_option} =~ ^[1-9]$|^1[0-1]$ ]] && [ ! -e "${php_install_dir}/bin/php" ]; }; then + /bin/cp ../config/nginx_tomcat.conf ${openresty_install_dir}/nginx/conf/nginx.conf + else + /bin/cp ../config/nginx.conf ${openresty_install_dir}/nginx/conf/nginx.conf + [[ "${php_option}" =~ ^[1-9]$|^1[0-1]$ ]] && [ -z "`grep '/php-fpm_status' ${openresty_install_dir}/nginx/conf/nginx.conf`" ] && sed -i "s@index index.html index.php;@index index.html index.php;\n location ~ /php-fpm_status {\n #fastcgi_pass remote_php_ip:9000;\n fastcgi_pass unix:/dev/shm/php-cgi.sock;\n fastcgi_index index.php;\n include fastcgi.conf;\n allow 127.0.0.1;\n deny all;\n }@" ${openresty_install_dir}/nginx/conf/nginx.conf + fi + cat > ${openresty_install_dir}/nginx/conf/proxy.conf << EOF +proxy_connect_timeout 300s; +proxy_send_timeout 900; +proxy_read_timeout 900; +proxy_buffer_size 32k; +proxy_buffers 4 64k; +proxy_busy_buffers_size 128k; +proxy_redirect off; +proxy_hide_header Vary; +proxy_set_header Accept-Encoding ''; +proxy_set_header Referer \$http_referer; +proxy_set_header Cookie \$http_cookie; +proxy_set_header Host \$host; +proxy_set_header X-Real-IP \$remote_addr; +proxy_set_header X-Forwarded-For \$proxy_add_x_forwarded_for; +proxy_set_header X-Forwarded-Proto \$scheme; +EOF + sed -i "s@/data/wwwroot/default@${wwwroot_dir}/default@" ${openresty_install_dir}/nginx/conf/nginx.conf + sed -i "s@/data/wwwlogs@${wwwlogs_dir}@g" ${openresty_install_dir}/nginx/conf/nginx.conf + sed -i "s@^user www www@user ${run_user} ${run_group}@" ${openresty_install_dir}/nginx/conf/nginx.conf + + # logrotate nginx log + cat > /etc/logrotate.d/nginx << EOF +${wwwlogs_dir}/*nginx.log { + daily + rotate 5 + missingok + dateext + compress + notifempty + sharedscripts + postrotate + [ -e /var/run/nginx.pid ] && kill -USR1 \`cat /var/run/nginx.pid\` + endscript +} +EOF + popd > /dev/null + ldconfig + systemctl start nginx +} diff --git a/include/openssl.sh b/include/openssl.sh new file mode 100644 index 0000000..70a8469 --- /dev/null +++ b/include/openssl.sh @@ -0,0 +1,170 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +if openssl version | grep -Eqi 'OpenSSL 1.0.2*'; then + php5_with_openssl="--with-openssl" + php70_with_openssl="--with-openssl" + php71_with_openssl="--with-openssl" + php72_with_openssl="--with-openssl" + php73_with_openssl="--with-openssl" + php74_with_openssl="--with-openssl" + php80_with_openssl="--with-openssl" + php81_with_openssl="--with-openssl" + php82_with_openssl="--with-openssl" + php83_with_openssl="--with-openssl" + + php5_with_ssl="--with-ssl" + php70_with_ssl="--with-ssl" + php71_with_ssl="--with-ssl" + php72_with_ssl="--with-ssl" + php73_with_ssl="--with-ssl" + php74_with_ssl="--with-ssl" + php80_with_ssl="--with-ssl" + php81_with_ssl="--with-ssl" + php82_with_ssl="--with-ssl" + php83_with_ssl="--with-ssl" + + php5_with_curl="--with-curl" + php70_with_curl="--with-curl" + php71_with_curl="--with-curl" + php72_with_curl="--with-curl" + php73_with_curl="--with-curl" + php74_with_curl="--with-curl" + php80_with_curl="--with-curl" + php81_with_curl="--with-curl" + php82_with_curl="--with-curl" + php83_with_curl="--with-curl" +elif openssl version | grep -Eqi 'OpenSSL 1.1.*'; then + php5_with_openssl="--with-openssl=${openssl_install_dir}" + php70_with_openssl="--with-openssl" + php71_with_openssl="--with-openssl" + php72_with_openssl="--with-openssl" + php73_with_openssl="--with-openssl" + php74_with_openssl="--with-openssl" + php80_with_openssl="--with-openssl" + php81_with_openssl="--with-openssl" + php82_with_openssl="--with-openssl" + php83_with_openssl="--with-openssl" + + php5_with_ssl="--with-ssl=${openssl_install_dir}" + php70_with_ssl="--with-ssl" + php71_with_ssl="--with-ssl" + php72_with_ssl="--with-ssl" + php73_with_ssl="--with-ssl" + php74_with_ssl="--with-ssl" + php80_with_ssl="--with-ssl" + php81_with_ssl="--with-ssl" + php82_with_ssl="--with-ssl" + php83_with_ssl="--with-ssl" + + php5_with_curl="--with-curl=${curl_install_dir}" + php70_with_curl="--with-curl" + php71_with_curl="--with-curl" + php72_with_curl="--with-curl" + php73_with_curl="--with-curl" + php74_with_curl="--with-curl" + php80_with_curl="--with-curl" + php81_with_curl="--with-curl" + php82_with_curl="--with-curl" + php83_with_curl="--with-curl" + [[ ${php_option} =~ ^[1-4]$ ]] || [[ "${mphp_ver}" =~ ^5[3-6]$ ]] && with_old_openssl_flag=y +elif openssl version | grep -Eqi 'OpenSSL 3.*'; then + php5_with_openssl="--with-openssl=${openssl_install_dir}" + php70_with_openssl="--with-openssl=${openssl_install_dir}" + php71_with_openssl="--with-openssl" + php72_with_openssl="--with-openssl" + php73_with_openssl="--with-openssl" + php74_with_openssl="--with-openssl" + php80_with_openssl="--with-openssl" + php81_with_openssl="--with-openssl" + php82_with_openssl="--with-openssl" + php83_with_openssl="--with-openssl" + + php5_with_ssl="--with-ssl=${openssl_install_dir}" + php70_with_ssl="--with-ssl=${openssl_install_dir}" + php71_with_ssl="--with-ssl" + php72_with_ssl="--with-ssl" + php73_with_ssl="--with-ssl" + php74_with_ssl="--with-ssl" + php80_with_ssl="--with-ssl" + php81_with_ssl="--with-ssl" + php82_with_ssl="--with-ssl" + php83_with_ssl="--with-ssl" + + php5_with_curl="--with-curl=${curl_install_dir}" + php70_with_curl="--with-curl=${curl_install_dir}" + php71_with_curl="--with-curl" + php72_with_curl="--with-curl" + php73_with_curl="--with-curl" + php74_with_curl="--with-curl" + php80_with_curl="--with-curl" + php81_with_curl="--with-curl" + php82_with_curl="--with-curl" + php83_with_curl="--with-curl" + [[ ${php_option} =~ ^[1-5]$ ]] || [[ "${mphp_ver}" =~ ^5[3-6]$|^70$ ]] && with_old_openssl_flag=y +else + php5_with_openssl="--with-openssl=${openssl_install_dir}" + php70_with_openssl="--with-openssl=${openssl_install_dir}" + php71_with_openssl="--with-openssl=${openssl_install_dir}" + php72_with_openssl="--with-openssl=${openssl_install_dir}" + php73_with_openssl="--with-openssl=${openssl_install_dir}" + php74_with_openssl="--with-openssl=${openssl_install_dir} --with-openssl-dir=${openssl_install_dir}" + php80_with_openssl="--with-openssl=${openssl_install_dir} --with-openssl-dir=${openssl_install_dir}" + php81_with_openssl="--with-openssl=${openssl_install_dir} --with-openssl-dir=${openssl_install_dir}" + php82_with_openssl="--with-openssl=${openssl_install_dir} --with-openssl-dir=${openssl_install_dir}" + php83_with_openssl="--with-openssl=${openssl_install_dir} --with-openssl-dir=${openssl_install_dir}" + + php5_with_ssl="--with-ssl=${openssl_install_dir}" + php70_with_ssl="--with-ssl=${openssl_install_dir}" + php71_with_ssl="--with-ssl=${openssl_install_dir}" + php72_with_ssl="--with-ssl=${openssl_install_dir}" + php73_with_ssl="--with-ssl=${openssl_install_dir}" + php74_with_ssl="--with-ssl=${openssl_install_dir}" + php80_with_ssl="--with-ssl=${openssl_install_dir}" + php81_with_ssl="--with-ssl=${openssl_install_dir}" + php82_with_ssl="--with-ssl=${openssl_install_dir}" + php83_with_ssl="--with-ssl=${openssl_install_dir}" + + php5_with_curl="--with-curl=${curl_install_dir}" + php70_with_curl="--with-curl=${curl_install_dir}" + php71_with_curl="--with-curl=${curl_install_dir}" + php72_with_curl="--with-curl=${curl_install_dir}" + php73_with_curl="--with-curl=${curl_install_dir}" + php74_with_curl="--with-curl=${curl_install_dir}" + php80_with_curl="--with-curl=${curl_install_dir}" + php81_with_curl="--with-curl=${curl_install_dir}" + php82_with_curl="--with-curl=${curl_install_dir}" + php83_with_curl="--with-curl=${curl_install_dir}" + with_old_openssl_flag=y +fi + +Install_openSSL() { + if [ "${with_old_openssl_flag}" == 'y' ]; then + if [ ! -e "${openssl_install_dir}/lib/libssl.a" ]; then + pushd ${oneinstack_dir}/src > /dev/null + tar xzf openssl-${openssl_ver}.tar.gz + pushd openssl-${openssl_ver} > /dev/null + make clean + ./config -Wl,-rpath=${openssl_install_dir}/lib -fPIC --prefix=${openssl_install_dir} --openssldir=${openssl_install_dir} + make depend + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${openssl_install_dir}/lib/libcrypto.a" ]; then + echo "${CSUCCESS}openSSL installed successfully! ${CEND}" + /bin/cp cacert.pem ${openssl_install_dir}/cert.pem + rm -rf openssl-${openssl_ver} + else + echo "${CFAILURE}openSSL install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + popd > /dev/null + fi + fi +} diff --git a/include/pecl_calendar.sh b/include/pecl_calendar.sh new file mode 100644 index 0000000..932be4f --- /dev/null +++ b/include/pecl_calendar.sh @@ -0,0 +1,41 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_calendar() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + src_url=https://secure.php.net/distributions/php-${PHP_detail_ver}.tar.gz && Download_src + tar xzf php-${PHP_detail_ver}.tar.gz + pushd php-${PHP_detail_ver}/ext/calendar > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/calendar.so" ]; then + echo 'extension=calendar.so' > ${php_install_dir}/etc/php.d/04-calendar.ini + echo "${CSUCCESS}PHP calendar module installed successfully! ${CEND}" + rm -rf php-${PHP_detail_ver} + else + echo "${CFAILURE}PHP calendar module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_calendar() { + if [ -e "${php_install_dir}/etc/php.d/04-calendar.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/04-calendar.ini + echo; echo "${CMSG}PHP calendar module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP calendar module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_fileinfo.sh b/include/pecl_fileinfo.sh new file mode 100644 index 0000000..12b3c23 --- /dev/null +++ b/include/pecl_fileinfo.sh @@ -0,0 +1,42 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_fileinfo() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + src_url=https://secure.php.net/distributions/php-${PHP_detail_ver}.tar.gz && Download_src + tar xzf php-${PHP_detail_ver}.tar.gz + pushd php-${PHP_detail_ver}/ext/fileinfo > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + sed -i 's@^CFLAGS =.*@CFLAGS = -std=c99 -g@' Makefile + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/fileinfo.so" ]; then + echo 'extension=fileinfo.so' > ${php_install_dir}/etc/php.d/04-fileinfo.ini + echo "${CSUCCESS}PHP fileinfo module installed successfully! ${CEND}" + rm -rf php-${PHP_detail_ver} + else + echo "${CFAILURE}PHP fileinfo module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_fileinfo() { + if [ -e "${php_install_dir}/etc/php.d/04-fileinfo.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/04-fileinfo.ini + echo; echo "${CMSG}PHP fileinfo module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP fileinfo module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_imap.sh b/include/pecl_imap.sh new file mode 100644 index 0000000..bccf187 --- /dev/null +++ b/include/pecl_imap.sh @@ -0,0 +1,58 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_imap() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + if [ "${PM}" == 'yum' ]; then + if [ "${RHEL_ver}" == '9' ]; then + cat > /etc/yum.repos.d/remi.repo << EOF +[remi] +name=Remi's RPM repository for Enterprise Linux 9 - \$basearch +mirrorlist=http://cdn.remirepo.net/enterprise/9/remi/\$basearch/mirror +enabled=0 +gpgcheck=0 +EOF + dnf -y --enablerepo=remi install uw-imap-devel + else + yum -y install libc-client-devel + [ ! -e /usr/lib/libc-client.so ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + else + apt-get -y install libc-client2007e-dev + fi + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + src_url=https://secure.php.net/distributions/php-${PHP_detail_ver}.tar.gz && Download_src + tar xzf php-${PHP_detail_ver}.tar.gz + pushd php-${PHP_detail_ver}/ext/imap > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config --with-kerberos --with-imap --with-imap-ssl + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/imap.so" ]; then + echo 'extension=imap.so' > ${php_install_dir}/etc/php.d/04-imap.ini + echo "${CSUCCESS}PHP imap module installed successfully! ${CEND}" + rm -rf php-${PHP_detail_ver} + else + echo "${CFAILURE}PHP imap module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_imap() { + if [ -e "${php_install_dir}/etc/php.d/04-imap.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/04-imap.ini + echo; echo "${CMSG}PHP imap module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP imap module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_ldap.sh b/include/pecl_ldap.sh new file mode 100644 index 0000000..d2a12f9 --- /dev/null +++ b/include/pecl_ldap.sh @@ -0,0 +1,52 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_ldap() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + src_url=https://secure.php.net/distributions/php-${PHP_detail_ver}.tar.gz && Download_src + tar xzf php-${PHP_detail_ver}.tar.gz + pushd php-${PHP_detail_ver}/ext/ldap > /dev/null + if [ "${PM}" == 'yum' ]; then + yum -y install openldap-devel + else + apt-get -y install libldap2-dev + ln -s /usr/lib/${ARCH}-linux-gnu/libldap.so /usr/lib/ + ln -s /usr/lib/${ARCH}-linux-gnu/liblber.so /usr/lib/ + fi + ${php_install_dir}/bin/phpize + if [ "${PM}" == 'yum' ]; then + ./configure --with-php-config=${php_install_dir}/bin/php-config --with-ldap --with-libdir=lib64 + else + ./configure --with-php-config=${php_install_dir}/bin/php-config --with-ldap --with-libdir=lib/x86_64-linux-gnu + fi + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/ldap.so" ]; then + echo 'extension=ldap.so' > ${php_install_dir}/etc/php.d/04-ldap.ini + echo "${CSUCCESS}PHP ldap module installed successfully! ${CEND}" + rm -rf php-${PHP_detail_ver} + else + echo "${CFAILURE}PHP ldap module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_ldap() { + if [ -e "${php_install_dir}/etc/php.d/04-ldap.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/04-ldap.ini + echo; echo "${CMSG}PHP ldap module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP ldap module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_mongodb.sh b/include/pecl_mongodb.sh new file mode 100644 index 0000000..52ec2ee --- /dev/null +++ b/include/pecl_mongodb.sh @@ -0,0 +1,69 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_mongodb() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + if [[ "$(${php_install_dir}/bin/php-config --version | awk -F. '{print $1$2}')" =~ ^5[3-4]$ ]]; then + src_url=https://pecl.php.net/get/mongo-${pecl_mongo_ver}.tgz && Download_src + tar xzf mongo-${pecl_mongo_ver}.tgz + pushd mongo-${pecl_mongo_ver} > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/mongo.so" ]; then + echo 'extension=mongo.so' > ${php_install_dir}/etc/php.d/07-mongo.ini + rm -rf mongo-${pecl_mongo_ver} + echo "${CSUCCESS}PHP mongo module installed successfully! ${CEND}" + else + echo "${CFAILURE}PHP mongo module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + else + if [[ "$(${php_install_dir}/bin/php-config --version | awk -F. '{print $1$2}')" =~ ^7[0-2]$ ]]; then + src_url=https://pecl.php.net/get/mongodb-${pecl_mongodb_oldver}.tgz && Download_src + tar xzf mongodb-${pecl_mongodb_oldver}.tgz + pushd mongodb-${pecl_mongodb_oldver} > /dev/null + else + src_url=https://pecl.php.net/get/mongodb-${pecl_mongodb_ver}.tgz && Download_src + tar xzf mongodb-${pecl_mongodb_ver}.tgz + pushd mongodb-${pecl_mongodb_ver} > /dev/null + fi + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/mongodb.so" ]; then + echo 'extension=mongodb.so' > ${php_install_dir}/etc/php.d/07-mongodb.ini + echo "${CSUCCESS}PHP mongodb module installed successfully! ${CEND}" + rm -rf mongodb-${pecl_mongodb_oldver} mongodb-${pecl_mongodb_ver} + else + echo "${CFAILURE}PHP mongodb module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + fi + popd > /dev/null + fi +} + +Uninstall_pecl_mongodb() { + if [ -e "${php_install_dir}/etc/php.d/07-mongo.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/07-mongo.ini + echo; echo "${CMSG}PHP mongo module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP mongo module does not exist! ${CEND}" + fi + if [ -e "${php_install_dir}/etc/php.d/07-mongodb.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/07-mongodb.ini + echo; echo "${CMSG}PHP mongodb module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP mongodb module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_pgsql.sh b/include/pecl_pgsql.sh new file mode 100644 index 0000000..bed52d1 --- /dev/null +++ b/include/pecl_pgsql.sh @@ -0,0 +1,46 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_pgsql() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=`${php_install_dir}/bin/php-config --extension-dir` + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + tar xzf php-${PHP_detail_ver}.tar.gz + pushd php-${PHP_detail_ver}/ext/pgsql > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-pgsql=${pgsql_install_dir} --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + pushd php-${PHP_detail_ver}/ext/pdo_pgsql > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-pdo-pgsql=${pgsql_install_dir} --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/pgsql.so" -a -f "${phpExtensionDir}/pdo_pgsql.so" ]; then + echo 'extension=pgsql.so' > ${php_install_dir}/etc/php.d/07-pgsql.ini + echo 'extension=pdo_pgsql.so' >> ${php_install_dir}/etc/php.d/07-pgsql.ini + echo "${CSUCCESS}PHP pgsql module installed successfully! ${CEND}" + rm -rf php-${PHP_detail_ver} + else + echo "${CFAILURE}PHP pgsql module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_pgsql() { + if [ -e "${php_install_dir}/etc/php.d/07-pgsql.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/07-pgsql.ini + echo; echo "${CMSG}PHP pgsql module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP pgsql module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_phalcon.sh b/include/pecl_phalcon.sh new file mode 100644 index 0000000..8b5ae09 --- /dev/null +++ b/include/pecl_phalcon.sh @@ -0,0 +1,54 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_phalcon() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + if [[ "${PHP_main_ver}" =~ ^7.[2-4]$|^8.3$ ]]; then + src_url=https://pecl.php.net/get/phalcon-${phalcon_ver}.tgz && Download_src + tar xzf phalcon-${phalcon_ver}.tgz + pushd phalcon-${phalcon_ver} > /dev/null + ${php_install_dir}/bin/phpize + echo "${CMSG}It may take a few minutes... ${CEND}" + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + elif [[ "${PHP_main_ver}" =~ ^5.[5-6]$|^7.[0-1]$ ]]; then + src_url=${mirror_link}/oneinstack/src/cphalcon-${phalcon_oldver}.tar.gz && Download_src + tar xzf cphalcon-${phalcon_oldver}.tar.gz + pushd cphalcon-${phalcon_oldver}/build > /dev/null + echo "${CMSG}It may take a few minutes... ${CEND}" + ./install --phpize ${php_install_dir}/bin/phpize --php-config ${php_install_dir}/bin/php-config --arch 64bits + popd > /dev/null + else + echo "${CWARNING}Your php ${PHP_detail_ver} does not support phalcon! ${CEND}" + fi + if [ -f "${phpExtensionDir}/phalcon.so" ]; then + echo 'extension=phalcon.so' > ${php_install_dir}/etc/php.d/04-phalcon.ini + echo "${CSUCCESS}PHP phalcon module installed successfully! ${CEND}" + rm -rf cphalcon-${phalcon_oldver} phalcon-${phalcon_ver} + else + echo "${CFAILURE}PHP phalcon module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_phalcon() { + if [ -e "${php_install_dir}/etc/php.d/04-phalcon.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/04-phalcon.ini + echo; echo "${CMSG}PHP phalcon module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP phalcon module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_swoole.sh b/include/pecl_swoole.sh new file mode 100644 index 0000000..b9cc258 --- /dev/null +++ b/include/pecl_swoole.sh @@ -0,0 +1,62 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_swoole() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + if [[ "${PHP_main_ver}" =~ ^5.[3-6]$ ]]; then + src_url=https://pecl.php.net/get/swoole-1.10.5.tgz && Download_src + tar xzf swoole-1.10.5.tgz + pushd swoole-1.10.5 > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config --enable-openssl --with-openssl-dir=${openssl_install_dir} + elif [[ "${PHP_main_ver}" =~ ^7.[0-1]$ ]]; then + src_url=https://pecl.php.net/get/swoole-4.5.2.tgz && Download_src + tar xzf swoole-4.5.2.tgz + pushd swoole-4.5.2 > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config --enable-openssl --with-openssl-dir=${openssl_install_dir} + elif [[ "${PHP_main_ver}" =~ ^7.[2-4]$ ]]; then + src_url=https://pecl.php.net/get/swoole-${swoole_oldver}.tgz && Download_src + tar xzf swoole-${swoole_oldver}.tgz + pushd swoole-${swoole_oldver} > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config --enable-openssl --with-openssl-dir=${openssl_install_dir} --enable-http2 --enable-swoole-json --enable-swoole-curl + else + src_url=https://pecl.php.net/get/swoole-${swoole_ver}.tgz && Download_src + tar xzf swoole-${swoole_ver}.tgz + pushd swoole-${swoole_ver} > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config --enable-openssl --with-openssl-dir=${openssl_install_dir} --enable-http2 --enable-swoole-json --enable-swoole-curl + fi + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/swoole.so" ]; then + echo 'extension=swoole.so' > ${php_install_dir}/etc/php.d/06-swoole.ini + echo "${CSUCCESS}PHP swoole module installed successfully! ${CEND}" + rm -rf swoole-${swoole_ver} swoole-${swoole_oldver} swoole-1.10.5 swoole-4.5.2 + else + echo "${CFAILURE}PHP swoole module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_swoole() { + if [ -e "${php_install_dir}/etc/php.d/06-swoole.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/06-swoole.ini + echo; echo "${CMSG}PHP swoole module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP swoole module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_xdebug.sh b/include/pecl_xdebug.sh new file mode 100644 index 0000000..c957b8c --- /dev/null +++ b/include/pecl_xdebug.sh @@ -0,0 +1,68 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_xdebug() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + if [[ "${PHP_main_ver}" =~ ^7.[0-4]$|^80$ ]]; then + if [[ "${PHP_main_ver}" =~ ^7.[0-1]$ ]]; then + src_url=https://pecl.php.net/get/xdebug-${xdebug_oldver}.tgz && Download_src + tar xzf xdebug-${xdebug_oldver}.tgz + pushd xdebug-${xdebug_oldver} > /dev/null + else + src_url=https://pecl.php.net/get/xdebug-${xdebug_ver}.tgz && Download_src + tar xzf xdebug-${xdebug_ver}.tgz + pushd xdebug-${xdebug_ver} > /dev/null + fi + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/xdebug.so" ]; then + src_url=${mirror_link}/oneinstack/src/webgrind-master.zip && Download_src + unzip -q webgrind-master.zip + /bin/mv webgrind-master ${wwwroot_dir}/default/webgrind + [ ! -e /tmp/xdebug ] && { mkdir /tmp/xdebug; chown ${run_user}:${run_group} /tmp/xdebug; } + [ ! -e /tmp/webgrind ] && { mkdir /tmp/webgrind; chown ${run_user}:${run_group} /tmp/webgrind; } + chown -R ${run_user}:${run_group} ${wwwroot_dir}/default/webgrind + sed -i 's@static $storageDir.*@static $storageDir = "/tmp/webgrind";@' ${wwwroot_dir}/default/webgrind/config.php + sed -i 's@static $profilerDir.*@static $profilerDir = "/tmp/xdebug";@' ${wwwroot_dir}/default/webgrind/config.php + cat > ${php_install_dir}/etc/php.d/08-xdebug.ini << EOF +[xdebug] +zend_extension=xdebug.so +xdebug.trace_output_dir=/tmp/xdebug +xdebug.profiler_output_dir = /tmp/xdebug +xdebug.profiler_enable = On +xdebug.profiler_enable_trigger = 1 +EOF + echo "${CSUCCESS}PHP xdebug module installed successfully! ${CEND}" + echo; echo "Webgrind URL: ${CMSG}http://{Public IP}/webgrind ${CEND}" + rm -rf xdebug-${xdebug_ver} xdebug-${xdebug_oldver} + else + echo "${CFAILURE}PHP xdebug module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + else + echo "${CWARNING}Your php ${PHP_detail_ver} does not support xdebug! ${CEND}"; + fi + popd > /dev/null + fi +} + +Uninstall_pecl_xdebug() { + if [ -e "${php_install_dir}/etc/php.d/08-xdebug.ini" ]; then + rm -rf ${php_install_dir}/etc/php.d/08-xdebug.ini /tmp/{xdebug,webgrind} ${wwwroot_dir}/default/webgrind + echo; echo "${CMSG}PHP xdebug module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP xdebug module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_yaf.sh b/include/pecl_yaf.sh new file mode 100644 index 0000000..dcbb50e --- /dev/null +++ b/include/pecl_yaf.sh @@ -0,0 +1,46 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_yaf() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + if [[ "${PHP_main_ver}" =~ ^7.[0-4]$|^8.0$ ]]; then + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + src_url=https://pecl.php.net/get/yaf-${yaf_ver}.tgz && Download_src + tar xzf yaf-${yaf_ver}.tgz + pushd yaf-${yaf_ver} > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/yaf.so" ]; then + echo 'extension=yaf.so' > ${php_install_dir}/etc/php.d/04-yaf.ini + echo "${CSUCCESS}PHP yaf module installed successfully! ${CEND}" + rm -rf yaf-${yaf_ver} + else + echo "${CFAILURE}PHP yaf module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + else + echo "${CWARNING}Your php ${PHP_detail_ver} does not support yaf! ${CEND}"; + fi + popd > /dev/null + fi +} + +Uninstall_pecl_yaf() { + if [ -e "${php_install_dir}/etc/php.d/04-yaf.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/04-yaf.ini + echo; echo "${CMSG}PHP yaf module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP yaf module does not exist! ${CEND}" + fi +} diff --git a/include/pecl_yar.sh b/include/pecl_yar.sh new file mode 100644 index 0000000..3de0674 --- /dev/null +++ b/include/pecl_yar.sh @@ -0,0 +1,46 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_pecl_yar() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + if [[ "${PHP_main_ver}" =~ ^7.[0-4]$|^8.0$ ]]; then + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + src_url=https://pecl.php.net/get/yar-${yar_ver}.tgz && Download_src + tar xzf yar-${yar_ver}.tgz + pushd yar-${yar_ver} > /dev/null + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config --with-curl=${curl_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/yar.so" ]; then + echo 'extension=yar.so' > ${php_install_dir}/etc/php.d/04-yar.ini + echo "${CSUCCESS}PHP yar module installed successfully! ${CEND}" + rm -rf yar-${yar_ver} + else + echo "${CFAILURE}PHP yar module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + else + echo "${CWARNING}Your php ${PHP_detail_ver} does not support yar! ${CEND}"; + fi + popd > /dev/null + fi +} + +Uninstall_pecl_yar() { + if [ -e "${php_install_dir}/etc/php.d/04-yar.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/04-yar.ini + echo; echo "${CMSG}PHP yar module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP yar module does not exist! ${CEND}" + fi +} diff --git a/include/percona-5.5.sh b/include/percona-5.5.sh new file mode 100644 index 0000000..a85f760 --- /dev/null +++ b/include/percona-5.5.sh @@ -0,0 +1,220 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Percona55() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${percona_install_dir}" ] && mkdir -p ${percona_install_dir} + mkdir -p ${percona_data_dir};chown mysql:mysql -R ${percona_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + perconaVerStr1=$(echo ${percona55_ver} | sed "s@-@-rel@") + tar xzf ./Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer}.tar.gz + mv Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer}/* ${percona_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${percona_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer}@${percona_install_dir}@g" ${percona_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + tar xzf percona-server-${percona55_ver}.tar.gz + pushd percona-server-${percona55_ver} + [ "${armplatform}" == "y" ] && patch -p1 < ../mysql-5.5-fix-arm-client_plugin.patch + cmake . -DCMAKE_INSTALL_PREFIX=${percona_install_dir} \ + -DMYSQL_DATADIR=${percona_data_dir} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_ARCHIVE_STORAGE_ENGINE=1 \ + -DWITH_READLINE=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${percona_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}Percona installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer} + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf percona-server-${percona55_ver} + fi + else + rm -rf ${percona_install_dir} + echo "${CFAILURE}Percona install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${percona_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${percona_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${percona_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock + +[mysql] +prompt="Percona [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${percona_install_dir} +datadir = ${percona_data_dir} +pid-file = ${percona_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${percona_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${percona_data_dir}/mysql-slow.log + +performance_schema = 0 + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G +myisam_repair_threads = 1 + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${percona_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${percona_install_dir} --datadir=${percona_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${percona_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${percona_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${percona_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${percona_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${percona_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${percona_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.user where Password='' and User not like 'mysql.%';" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.db where User='';" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.proxies_priv where Host!='localhost';" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + echo "${percona_install_dir}/lib" > /etc/ld.so.conf.d/z-percona.conf + ldconfig + service mysqld stop +} diff --git a/include/percona-5.6.sh b/include/percona-5.6.sh new file mode 100644 index 0000000..0557c9b --- /dev/null +++ b/include/percona-5.6.sh @@ -0,0 +1,220 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Percona56() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${percona_install_dir}" ] && mkdir -p ${percona_install_dir} + mkdir -p ${percona_data_dir};chown mysql:mysql -R ${percona_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + perconaVerStr1=$(echo ${percona56_ver} | sed "s@-@-rel@") + tar xzf ./Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer}.tar.gz + mv Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer}/* ${percona_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${percona_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer}@${percona_install_dir}@g" ${percona_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + tar xzf percona-server-${percona56_ver}.tar.gz + pushd percona-server-${percona56_ver} + cmake . -DCMAKE_INSTALL_PREFIX=${percona_install_dir} \ + -DMYSQL_DATADIR=${percona_data_dir} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_ARCHIVE_STORAGE_ENGINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${percona_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}Percona installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer} + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf percona-server-${percona56_ver} + fi + else + rm -rf ${percona_install_dir} + echo "${CFAILURE}Percona install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${percona_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${percona_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${percona_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock + +[mysql] +prompt="Percona [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${percona_install_dir} +datadir = ${percona_data_dir} +pid-file = ${percona_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${percona_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${percona_data_dir}/mysql-slow.log + +performance_schema = 0 +explicit_defaults_for_timestamp + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G +myisam_repair_threads = 1 + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${percona_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${percona_install_dir} --datadir=${percona_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${percona_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${percona_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${percona_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${percona_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${percona_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${percona_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.user where Password='' and User not like 'mysql.%';" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.db where User='';" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "delete from mysql.proxies_priv where Host!='localhost';" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + echo "${percona_install_dir}/lib" > /etc/ld.so.conf.d/z-percona.conf + ldconfig + service mysqld stop +} diff --git a/include/percona-5.7.sh b/include/percona-5.7.sh new file mode 100644 index 0000000..dae2844 --- /dev/null +++ b/include/percona-5.7.sh @@ -0,0 +1,220 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Percona57() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${percona_install_dir}" ] && mkdir -p ${percona_install_dir} + mkdir -p ${percona_data_dir};chown mysql:mysql -R ${percona_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar xzf Percona-Server-${percona57_ver}-Linux.x86_64.glibc2.17.tar.gz + mv Percona-Server-${percona57_ver}-Linux.x86_64.glibc2.17/* ${percona_install_dir} + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${percona_install_dir}/bin/mysqld_safe + sed -i "s@Percona-Server-${percona57_ver}-Linux.x86_64.glibc2.17@${percona_install_dir}@g" ${percona_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + boostVersion2=$(echo ${boost_oldver} | awk -F. '{print $1"_"$2"_"$3}') + tar xzf boost_${boostVersion2}.tar.gz + tar xzf percona-server-${percona57_ver}.tar.gz + pushd percona-server-${percona57_ver} + cmake . -DCMAKE_INSTALL_PREFIX=${percona_install_dir} \ + -DMYSQL_DATADIR=${percona_data_dir} \ + -DDOWNLOAD_BOOST=1 \ + -DWITH_BOOST=../boost_${boostVersion2} \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DWITH_ARCHIVE_STORAGE_ENGINE=1 \ + -DWITH_ZLIB=system \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DDEFAULT_COLLATION=utf8mb4_general_ci \ + -DEXTRA_CHARSETS=all \ + -DCMAKE_EXE_LINKER_FLAGS='-ljemalloc' + make -j ${THREAD} + make install + popd + fi + + if [ -d "${percona_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}Percona installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf Percona-Server-${percona57_ver}-Linux.x86_64.${sslLibVer} + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf percona-server-${percona57_ver} boost_${boostVersion2} + fi + else + rm -rf ${percona_install_dir} + echo "${CFAILURE}Percona install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${percona_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${percona_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${percona_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock + +[mysql] +prompt="Percona [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock + +basedir = ${percona_install_dir} +datadir = ${percona_data_dir} +pid-file = ${percona_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +query_cache_type = 1 +query_cache_size = 8M +query_cache_limit = 2M + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +expire_logs_days = 7 + +log_error = ${percona_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${percona_data_dir}/mysql-slow.log + +performance_schema = 0 +explicit_defaults_for_timestamp + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 16M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 32M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^query_cache_size.*@query_cache_size = 64M@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${percona_install_dir}/bin/mysqld --initialize-insecure --user=mysql --basedir=${percona_install_dir} --datadir=${percona_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${percona_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${percona_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${percona_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${percona_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${percona_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'127.0.0.1' identified by \"${dbrootpwd}\" with grant option;" + ${percona_install_dir}/bin/mysql -e "grant all privileges on *.* to root@'localhost' identified by \"${dbrootpwd}\" with grant option;" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + [ -e "${percona_install_dir}/my.cnf" ] && rm -rf ${percona_install_dir}/my.cnf + echo "${percona_install_dir}/lib" > /etc/ld.so.conf.d/z-percona.conf + ldconfig + service mysqld stop +} diff --git a/include/percona-8.0.sh b/include/percona-8.0.sh new file mode 100644 index 0000000..1231da9 --- /dev/null +++ b/include/percona-8.0.sh @@ -0,0 +1,221 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Percona80() { + pushd ${oneinstack_dir}/src > /dev/null + id -u mysql >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin mysql + + [ ! -d "${percona_install_dir}" ] && mkdir -p ${percona_install_dir} + mkdir -p ${percona_data_dir};chown mysql:mysql -R ${percona_data_dir} + + if [ "${dbinstallmethod}" == "1" ]; then + tar xzf ./Percona-Server-${percona80_ver}-Linux.x86_64.glibc2.28.tar.gz + mv Percona-Server-${percona80_ver}-Linux.x86_64.glibc2.28/* ${percona_install_dir} + #sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${percona_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/Percona-Server-${percona80_ver}-Linux.x86_64.glibc2.28@${percona_install_dir}@g" ${percona_install_dir}/bin/mysqld_safe + elif [ "${dbinstallmethod}" == "2" ]; then + boostVersion2=$(echo ${boost_percona_ver} | awk -F. '{print $1"_"$2"_"$3}') + tar xzf boost_${boostVersion2}.tar.gz + tar xzf percona-server-${percona80_ver}.tar.gz + pushd percona-server-${percona80_ver} + cmake . -DCMAKE_INSTALL_PREFIX=${percona_install_dir} \ + -DMYSQL_DATADIR=${percona_data_dir} \ + -DDOWNLOAD_BOOST=1 \ + -DWITH_BOOST=../boost_${boostVersion2} \ + -DFORCE_INSOURCE_BUILD=1 \ + -DSYSCONFDIR=/etc \ + -DWITH_INNOBASE_STORAGE_ENGINE=1 \ + -DWITH_PARTITION_STORAGE_ENGINE=1 \ + -DWITH_FEDERATED_STORAGE_ENGINE=1 \ + -DWITH_BLACKHOLE_STORAGE_ENGINE=1 \ + -DWITH_MYISAM_STORAGE_ENGINE=1 \ + -DWITH_EMBEDDED_SERVER=1 \ + -DENABLE_DTRACE=0 \ + -DENABLED_LOCAL_INFILE=1 \ + -DDEFAULT_CHARSET=utf8mb4 \ + -DEXTRA_CHARSETS=all + make -j ${THREAD} + make install + sed -i 's@^load_jemalloc=1@load_jemalloc=0@' ${percona_install_dir}/bin/mysqld_safe + popd + fi + + # backup openssl so + #[ ! -e "${percona_install_dir}/lib/lib_bk" ] && mkdir ${percona_install_dir}/lib/lib_bk + #/bin/mv ${percona_install_dir}/lib/{libssl,libcrypto}.so* ${percona_install_dir}/lib/lib_bk/ + + if [ -d "${percona_install_dir}/support-files" ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${dbrootpwd}'+" ../options.conf + echo "${CSUCCESS}Percona installed successfully! ${CEND}" + if [ "${dbinstallmethod}" == "1" ]; then + rm -rf Percona-Server-${percona80_ver}-Linux.x86_64.glibc2.28 + elif [ "${dbinstallmethod}" == "2" ]; then + rm -rf percona-server-${percona80_ver} boost_${boostVersion2} + fi + else + rm -rf ${percona_install_dir} + echo "${CFAILURE}Percona install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp ${percona_install_dir}/support-files/mysql.server /etc/init.d/mysqld + sed -i "s@^basedir=.*@basedir=${percona_install_dir}@" /etc/init.d/mysqld + sed -i "s@^datadir=.*@datadir=${percona_data_dir}@" /etc/init.d/mysqld + chmod +x /etc/init.d/mysqld + [ "${PM}" == 'yum' ] && { chkconfig --add mysqld; chkconfig mysqld on; } + [ "${PM}" == 'apt-get' ] && update-rc.d mysqld defaults + popd + + # my.cnf + cat > /etc/my.cnf << EOF +[client] +port = 3306 +socket = /tmp/mysql.sock +default-character-set = utf8mb4 + +[mysql] +prompt="Percona [\\d]> " +no-auto-rehash + +[mysqld] +port = 3306 +socket = /tmp/mysql.sock +default_authentication_plugin = mysql_native_password + +basedir = ${percona_install_dir} +datadir = ${percona_data_dir} +pid-file = ${percona_data_dir}/mysql.pid +user = mysql +bind-address = 0.0.0.0 +server-id = 1 + +init-connect = 'SET NAMES utf8mb4' +character-set-server = utf8mb4 +collation-server = utf8mb4_0900_ai_ci + +skip-name-resolve +#skip-networking +back_log = 300 + +max_connections = 1000 +max_connect_errors = 6000 +open_files_limit = 65535 +table_open_cache = 128 +max_allowed_packet = 500M +binlog_cache_size = 1M +max_heap_table_size = 8M +tmp_table_size = 16M + +read_buffer_size = 2M +read_rnd_buffer_size = 8M +sort_buffer_size = 8M +join_buffer_size = 8M +key_buffer_size = 4M + +thread_cache_size = 8 + +ft_min_word_len = 4 + +log_bin = mysql-bin +binlog_format = mixed +binlog_expire_logs_seconds = 604800 + +log_error = ${percona_data_dir}/mysql-error.log +slow_query_log = 1 +long_query_time = 1 +slow_query_log_file = ${percona_data_dir}/mysql-slow.log + +performance_schema = 0 +explicit_defaults_for_timestamp + +#lower_case_table_names = 1 + +skip-external-locking + +default_storage_engine = InnoDB +#default-storage-engine = MyISAM +innodb_file_per_table = 1 +innodb_open_files = 500 +innodb_buffer_pool_size = 64M +innodb_write_io_threads = 4 +innodb_read_io_threads = 4 +innodb_thread_concurrency = 0 +innodb_purge_threads = 1 +innodb_flush_log_at_trx_commit = 2 +innodb_log_buffer_size = 2M +innodb_log_file_size = 32M +innodb_log_files_in_group = 3 +innodb_max_dirty_pages_pct = 90 +innodb_lock_wait_timeout = 120 + +bulk_insert_buffer_size = 8M +myisam_sort_buffer_size = 8M +myisam_max_sort_file_size = 10G + +interactive_timeout = 28800 +wait_timeout = 28800 + +[mysqldump] +quick +max_allowed_packet = 500M + +[myisamchk] +key_buffer_size = 8M +sort_buffer_size = 8M +read_buffer = 4M +write_buffer = 4M +EOF + + sed -i "s@max_connections.*@max_connections = $((${Mem}/3))@" /etc/my.cnf + if [ ${Mem} -gt 1500 -a ${Mem} -le 2500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 16@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 16M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 128M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 32M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 256@' /etc/my.cnf + elif [ ${Mem} -gt 2500 -a ${Mem} -le 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 32@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 32M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 512M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 64M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 512@' /etc/my.cnf + elif [ ${Mem} -gt 3500 ]; then + sed -i 's@^thread_cache_size.*@thread_cache_size = 64@' /etc/my.cnf + sed -i 's@^myisam_sort_buffer_size.*@myisam_sort_buffer_size = 64M@' /etc/my.cnf + sed -i 's@^key_buffer_size.*@key_buffer_size = 256M@' /etc/my.cnf + sed -i 's@^innodb_buffer_pool_size.*@innodb_buffer_pool_size = 1024M@' /etc/my.cnf + sed -i 's@^tmp_table_size.*@tmp_table_size = 128M@' /etc/my.cnf + sed -i 's@^table_open_cache.*@table_open_cache = 1024@' /etc/my.cnf + fi + + ${percona_install_dir}/bin/mysqld --initialize-insecure --user=mysql --basedir=${percona_install_dir} --datadir=${percona_data_dir} + + [ "${Wsl}" == true ] && chmod 600 /etc/my.cnf + chown mysql:mysql -R ${percona_data_dir} + [ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} + service mysqld start + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${percona_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${percona_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${percona_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + ${percona_install_dir}/bin/mysql -uroot -hlocalhost -e "create user root@'127.0.0.1' identified by \"${dbrootpwd}\";" + ${percona_install_dir}/bin/mysql -uroot -hlocalhost -e "grant all privileges on *.* to root@'127.0.0.1' with grant option;" + ${percona_install_dir}/bin/mysql -uroot -hlocalhost -e "grant all privileges on *.* to root@'localhost' with grant option;" + ${percona_install_dir}/bin/mysql -uroot -hlocalhost -e "alter user root@'localhost' identified by \"${dbrootpwd}\";" + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" + rm -rf /etc/ld.so.conf.d/{mysql,mariadb,percona}*.conf + [ -e "${percona_install_dir}/my.cnf" ] && rm -f ${percona_install_dir}/my.cnf + echo "${percona_install_dir}/lib" > /etc/ld.so.conf.d/z-percona.conf + ldconfig + service mysqld stop +} diff --git a/include/php-5.3.sh b/include/php-5.3.sh new file mode 100644 index 0000000..73d48b1 --- /dev/null +++ b/include/php-5.3.sh @@ -0,0 +1,253 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP53() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php5_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/bin/libmcrypt-config" -a ! -e "/usr/bin/libmcrypt-config" ]; then + tar xzf libmcrypt-${libmcrypt_ver}.tar.gz + pushd libmcrypt-${libmcrypt_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + ldconfig + pushd libltdl > /dev/null + ./configure --enable-ltdl-install + make -j ${THREAD} && make install + popd > /dev/null + popd > /dev/null + rm -rf libmcrypt-${libmcrypt_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/usr/bin/libmcrypt-config" ] && ln -s /usr/local/bin/libmcrypt-config /usr/bin/libmcrypt-config + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + if [ ! -e "/usr/local/bin/mcrypt" -a ! -e "/usr/bin/mcrypt" ]; then + tar xzf mcrypt-${mcrypt_ver}.tar.gz + pushd mcrypt-${mcrypt_ver} > /dev/null + ldconfig + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mcrypt-${mcrypt_ver} + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php53_ver}.tar.gz + patch -d php-${php53_ver} -p0 < fpm-race-condition.patch + pushd php-${php53_ver} > /dev/null + patch -p1 < ../php5.3patch + patch -p1 < ../debian_patches_disable_SSLv2_for_openssl_1_0_0.patch + make clean + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + { [ ${RHEL_ver} -ge 9 >/dev/null 2>&1 ] || [ ${Debian_ver} -ge 10 >/dev/null 2>&1 ] || [ ${Ubuntu_ver} -ge 19 >/dev/null 2>&1 ]; } || intl_modules_options='--enable-intl' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs --disable-fileinfo \ + --with-mysql=mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php5_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php5_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm --disable-fileinfo \ + --with-mysql=mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php5_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php5_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + fi + { [ ${RHEL_ver} -ge 9 >/dev/null 2>&1 ] || [ ${Debian_ver} -ge 10 >/dev/null 2>&1 ] || [ ${Ubuntu_ver} -ge 19 >/dev/null 2>&1 ]; } || sed -i '/^BUILD_/ s/\$(CC)/\$(CXX)/g' Makefile + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 5@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php53_ver} + popd > /dev/null +} diff --git a/include/php-5.4.sh b/include/php-5.4.sh new file mode 100644 index 0000000..6e4f100 --- /dev/null +++ b/include/php-5.4.sh @@ -0,0 +1,250 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP54() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php5_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/bin/libmcrypt-config" -a ! -e "/usr/bin/libmcrypt-config" ]; then + tar xzf libmcrypt-${libmcrypt_ver}.tar.gz + pushd libmcrypt-${libmcrypt_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + ldconfig + pushd libltdl > /dev/null + ./configure --enable-ltdl-install + make -j ${THREAD} && make install + popd > /dev/null + popd > /dev/null + rm -rf libmcrypt-${libmcrypt_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/usr/bin/libmcrypt-config" ] && ln -s /usr/local/bin/libmcrypt-config /usr/bin/libmcrypt-config + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + if [ ! -e "/usr/local/bin/mcrypt" -a ! -e "/usr/bin/mcrypt" ]; then + tar xzf mcrypt-${mcrypt_ver}.tar.gz + pushd mcrypt-${mcrypt_ver} > /dev/null + ldconfig + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mcrypt-${mcrypt_ver} + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php54_ver}.tar.gz + patch -d php-${php54_ver} -p0 < fpm-race-condition.patch + pushd php-${php54_ver} > /dev/null + make clean + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + { [ ${RHEL_ver} -ge 9 >/dev/null 2>&1 ] || [ ${Debian_ver} -ge 10 >/dev/null 2>&1 ] || [ ${Ubuntu_ver} -ge 19 >/dev/null 2>&1 ]; } || intl_modules_options='--enable-intl' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs --disable-fileinfo \ + --with-mysql=mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php5_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php5_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm --disable-fileinfo \ + --with-mysql=mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php5_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php5_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 5@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php54_ver} + popd > /dev/null +} diff --git a/include/php-5.5.sh b/include/php-5.5.sh new file mode 100644 index 0000000..87e9ee8 --- /dev/null +++ b/include/php-5.5.sh @@ -0,0 +1,263 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP55() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php5_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/bin/libmcrypt-config" -a ! -e "/usr/bin/libmcrypt-config" ]; then + tar xzf libmcrypt-${libmcrypt_ver}.tar.gz + pushd libmcrypt-${libmcrypt_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + ldconfig + pushd libltdl > /dev/null + ./configure --enable-ltdl-install + make -j ${THREAD} && make install + popd > /dev/null + popd > /dev/null + rm -rf libmcrypt-${libmcrypt_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/usr/bin/libmcrypt-config" ] && ln -s /usr/local/bin/libmcrypt-config /usr/bin/libmcrypt-config + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + if [ ! -e "/usr/local/bin/mcrypt" -a ! -e "/usr/bin/mcrypt" ]; then + tar xzf mcrypt-${mcrypt_ver}.tar.gz + pushd mcrypt-${mcrypt_ver} > /dev/null + ldconfig + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mcrypt-${mcrypt_ver} + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + tar xzf php-${php55_ver}.tar.gz + patch -d php-${php55_ver} -p0 < fpm-race-condition.patch + pushd php-${php55_ver} > /dev/null + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + { [ ${RHEL_ver} -ge 9 >/dev/null 2>&1 ] || [ ${Debian_ver} -ge 10 >/dev/null 2>&1 ] || [ ${Ubuntu_ver} -ge 19 >/dev/null 2>&1 ]; } || intl_modules_options='--enable-intl' + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --with-mysql=mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php5_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php5_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --with-mysql=mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php5_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php5_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 5@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=4000 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.fast_shutdown=1 +opcache.enable_cli=1 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php55_ver} + popd > /dev/null +} diff --git a/include/php-5.6.sh b/include/php-5.6.sh new file mode 100644 index 0000000..5125171 --- /dev/null +++ b/include/php-5.6.sh @@ -0,0 +1,269 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP56() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php5_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/bin/libmcrypt-config" -a ! -e "/usr/bin/libmcrypt-config" ]; then + tar xzf libmcrypt-${libmcrypt_ver}.tar.gz + pushd libmcrypt-${libmcrypt_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + ldconfig + pushd libltdl > /dev/null + ./configure --enable-ltdl-install + make -j ${THREAD} && make install + popd > /dev/null + popd > /dev/null + rm -rf libmcrypt-${libmcrypt_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/usr/bin/libmcrypt-config" ] && ln -s /usr/local/bin/libmcrypt-config /usr/bin/libmcrypt-config + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + if [ ! -e "/usr/local/bin/mcrypt" -a ! -e "/usr/bin/mcrypt" ]; then + tar xzf mcrypt-${mcrypt_ver}.tar.gz + pushd mcrypt-${mcrypt_ver} > /dev/null + ldconfig + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mcrypt-${mcrypt_ver} + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php56_ver}.tar.gz + pushd php-${php56_ver} > /dev/null + make clean + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + { [ ${RHEL_ver} -ge 9 >/dev/null 2>&1 ] || [ ${Debian_ver} -ge 10 >/dev/null 2>&1 ] || [ ${Ubuntu_ver} -ge 19 >/dev/null 2>&1 ]; } || intl_modules_options='--enable-intl' + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --with-mysql=mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php5_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php5_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --with-mysql=mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php5_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php5_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 5@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=4000 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.fast_shutdown=1 +opcache.enable_cli=1 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php56_ver} + popd > /dev/null +} diff --git a/include/php-7.0.sh b/include/php-7.0.sh new file mode 100644 index 0000000..11f54ff --- /dev/null +++ b/include/php-7.0.sh @@ -0,0 +1,274 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP70() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php70_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/bin/libmcrypt-config" -a ! -e "/usr/bin/libmcrypt-config" ]; then + tar xzf libmcrypt-${libmcrypt_ver}.tar.gz + pushd libmcrypt-${libmcrypt_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + ldconfig + pushd libltdl > /dev/null + ./configure --enable-ltdl-install + make -j ${THREAD} && make install + popd > /dev/null + popd > /dev/null + rm -rf libmcrypt-${libmcrypt_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/usr/bin/libmcrypt-config" ] && ln -s /usr/local/bin/libmcrypt-config /usr/bin/libmcrypt-config + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + if [ ! -e "/usr/local/bin/mcrypt" -a ! -e "/usr/bin/mcrypt" ]; then + tar xzf mcrypt-${mcrypt_ver}.tar.gz + pushd mcrypt-${mcrypt_ver} > /dev/null + ldconfig + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mcrypt-${mcrypt_ver} + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php70_ver}.tar.gz + pushd php-${php70_ver} + make clean + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + { [ ${Debian_ver} -ge 10 >/dev/null 2>&1 ] || [ ${Ubuntu_ver} -ge 19 >/dev/null 2>&1 ]; } || intl_modules_options='--enable-intl' + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php70_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php70_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php70_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php70_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --with-xsl ${intl_modules_options} \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.fast_shutdown=1 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php70_ver} + popd > /dev/null +} diff --git a/include/php-7.1.sh b/include/php-7.1.sh new file mode 100644 index 0000000..05e6702 --- /dev/null +++ b/include/php-7.1.sh @@ -0,0 +1,277 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP71() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php71_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/bin/libmcrypt-config" -a ! -e "/usr/bin/libmcrypt-config" ]; then + tar xzf libmcrypt-${libmcrypt_ver}.tar.gz + pushd libmcrypt-${libmcrypt_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + ldconfig + pushd libltdl > /dev/null + ./configure --enable-ltdl-install + make -j ${THREAD} && make install + popd > /dev/null + popd > /dev/null + rm -rf libmcrypt-${libmcrypt_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/usr/bin/libmcrypt-config" ] && ln -s /usr/local/bin/libmcrypt-config /usr/bin/libmcrypt-config + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + if [ ! -e "/usr/local/bin/mcrypt" -a ! -e "/usr/bin/mcrypt" ]; then + tar xzf mcrypt-${mcrypt_ver}.tar.gz + pushd mcrypt-${mcrypt_ver} > /dev/null + ldconfig + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mcrypt-${mcrypt_ver} + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php71_ver}.tar.gz + pushd php-${php71_ver} > /dev/null + if [ -e ext/openssl/openssl.c ] && ! grep -Eqi '^#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c; then + sed -i '/OPENSSL_SSLV23_PADDING/i#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c + sed -i '/OPENSSL_SSLV23_PADDING/a#endif' ext/openssl/openssl.c + fi + make clean + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php71_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php71_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --enable-intl --with-xsl \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php71_with_curl} --enable-mbregex \ + --enable-mbstring --with-mcrypt --with-gd --enable-gd-native-ttf ${php71_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --enable-intl --with-xsl \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.fast_shutdown=1 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php71_ver} + popd > /dev/null +} diff --git a/include/php-7.2.sh b/include/php-7.2.sh new file mode 100644 index 0000000..53b2a76 --- /dev/null +++ b/include/php-7.2.sh @@ -0,0 +1,270 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP72() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php72_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/lib/pkgconfig/libargon2.pc" ]; then + tar xzf argon2-${argon2_ver}.tar.gz + pushd argon2-${argon2_ver} > /dev/null + make -j ${THREAD} && make install + [ ! -d /usr/local/lib/pkgconfig ] && mkdir -p /usr/local/lib/pkgconfig + /bin/cp libargon2.pc /usr/local/lib/pkgconfig/ + popd > /dev/null + rm -rf argon2-${argon2_ver} + fi + + if [ ! -e "/usr/local/lib/libsodium.la" ]; then + tar xzf libsodium-${libsodium_ver}.tar.gz + pushd libsodium-${libsodium_ver} > /dev/null + ./configure --disable-dependency-tracking --enable-minimal + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libsodium-${libsodium_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php72_ver}.tar.gz + pushd php-${php72_ver} > /dev/null + if [ -e ext/openssl/openssl.c ] && ! grep -Eqi '^#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c; then + sed -i '/OPENSSL_SSLV23_PADDING/i#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c + sed -i '/OPENSSL_SSLV23_PADDING/a#endif' ext/openssl/openssl.c + fi + make clean + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php72_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --with-gd ${php72_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --enable-intl --with-xsl \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php72_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --with-gd ${php72_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --enable-intl --with-xsl \ + --with-gettext --enable-zip --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php72_ver} + popd > /dev/null +} diff --git a/include/php-7.3.sh b/include/php-7.3.sh new file mode 100644 index 0000000..91348af --- /dev/null +++ b/include/php-7.3.sh @@ -0,0 +1,270 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP73() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php73_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/lib/pkgconfig/libargon2.pc" ]; then + tar xzf argon2-${argon2_ver}.tar.gz + pushd argon2-${argon2_ver} > /dev/null + make -j ${THREAD} && make install + [ ! -d /usr/local/lib/pkgconfig ] && mkdir -p /usr/local/lib/pkgconfig + /bin/cp libargon2.pc /usr/local/lib/pkgconfig/ + popd > /dev/null + rm -rf argon2-${argon2_ver} + fi + + if [ ! -e "/usr/local/lib/libsodium.la" ]; then + tar xzf libsodium-${libsodium_ver}.tar.gz + pushd libsodium-${libsodium_ver} > /dev/null + ./configure --disable-dependency-tracking --enable-minimal + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libsodium-${libsodium_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php73_ver}.tar.gz + pushd php-${php73_ver} > /dev/null + if [ -e ext/openssl/openssl.c ] && ! grep -Eqi '^#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c; then + sed -i '/OPENSSL_SSLV23_PADDING/i#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c + sed -i '/OPENSSL_SSLV23_PADDING/a#endif' ext/openssl/openssl.c + fi + make clean + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php73_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --with-gd ${php73_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --enable-intl --with-xsl \ + --with-gettext --enable-zip --without-libzip --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype-dir=${freetype_install_dir} --with-jpeg-dir --with-png-dir --with-zlib \ + --with-libxml-dir=/usr --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php73_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --with-gd ${php73_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --enable-intl --with-xsl \ + --with-gettext --enable-zip --without-libzip --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php73_ver} + popd > /dev/null +} diff --git a/include/php-7.4.sh b/include/php-7.4.sh new file mode 100644 index 0000000..fd94d62 --- /dev/null +++ b/include/php-7.4.sh @@ -0,0 +1,280 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP74() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php74_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/lib/pkgconfig/libargon2.pc" ]; then + tar xzf argon2-${argon2_ver}.tar.gz + pushd argon2-${argon2_ver} > /dev/null + make -j ${THREAD} && make install + [ ! -d /usr/local/lib/pkgconfig ] && mkdir -p /usr/local/lib/pkgconfig + /bin/cp libargon2.pc /usr/local/lib/pkgconfig/ + popd > /dev/null + rm -rf argon2-${argon2_ver} + fi + + if [ ! -e "/usr/local/lib/libsodium.la" ]; then + tar xzf libsodium-${libsodium_ver}.tar.gz + pushd libsodium-${libsodium_ver} > /dev/null + ./configure --disable-dependency-tracking --enable-minimal + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libsodium-${libsodium_ver} + fi + + if [ ! -e "/usr/local/lib/libzip.la" ]; then + tar xzf libzip-${libzip_ver}.tar.gz + pushd libzip-${libzip_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libzip-${libzip_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php74_ver}.tar.gz + pushd php-${php74_ver} > /dev/null + if [ -e ext/openssl/openssl.c ] && ! grep -Eqi '^#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c; then + sed -i '/OPENSSL_SSLV23_PADDING/i#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c + sed -i '/OPENSSL_SSLV23_PADDING/a#endif' ext/openssl/openssl.c + fi + make clean + export PKG_CONFIG_PATH=/usr/local/lib/pkgconfig/:$PKG_CONFIG_PATH + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php74_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php74_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv-dir=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem --enable-inline-optimization ${php74_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php74_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --with-xmlrpc --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php74_ver} + popd > /dev/null +} diff --git a/include/php-8.0.sh b/include/php-8.0.sh new file mode 100644 index 0000000..cee042e --- /dev/null +++ b/include/php-8.0.sh @@ -0,0 +1,280 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP80() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php80_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/lib/pkgconfig/libargon2.pc" ]; then + tar xzf argon2-${argon2_ver}.tar.gz + pushd argon2-${argon2_ver} > /dev/null + make -j ${THREAD} && make install + [ ! -d /usr/local/lib/pkgconfig ] && mkdir -p /usr/local/lib/pkgconfig + /bin/cp libargon2.pc /usr/local/lib/pkgconfig/ + popd > /dev/null + rm -rf argon2-${argon2_ver} + fi + + if [ ! -e "/usr/local/lib/libsodium.la" ]; then + tar xzf libsodium-${libsodium_ver}.tar.gz + pushd libsodium-${libsodium_ver} > /dev/null + ./configure --disable-dependency-tracking --enable-minimal + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libsodium-${libsodium_ver} + fi + + if [ ! -e "/usr/local/lib/libzip.la" ]; then + tar xzf libzip-${libzip_ver}.tar.gz + pushd libzip-${libzip_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libzip-${libzip_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php80_ver}.tar.gz + pushd php-${php80_ver} > /dev/null + if [ -e ext/openssl/openssl.c ] && ! grep -Eqi '^#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c; then + sed -i '/OPENSSL_SSLV23_PADDING/i#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c + sed -i '/OPENSSL_SSLV23_PADDING/a#endif' ext/openssl/openssl.c + fi + make clean + export PKG_CONFIG_PATH=/usr/local/lib/pkgconfig/:$PKG_CONFIG_PATH + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem ${php80_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php80_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem ${php80_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php80_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php80_ver} + popd > /dev/null +} diff --git a/include/php-8.1.sh b/include/php-8.1.sh new file mode 100644 index 0000000..b25c8fb --- /dev/null +++ b/include/php-8.1.sh @@ -0,0 +1,276 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP81() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php81_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/lib/pkgconfig/libargon2.pc" ]; then + tar xzf argon2-${argon2_ver}.tar.gz + pushd argon2-${argon2_ver} > /dev/null + make -j ${THREAD} && make install + [ ! -d /usr/local/lib/pkgconfig ] && mkdir -p /usr/local/lib/pkgconfig + /bin/cp libargon2.pc /usr/local/lib/pkgconfig/ + popd > /dev/null + rm -rf argon2-${argon2_ver} + fi + + if [ ! -e "/usr/local/lib/libsodium.la" ]; then + tar xzf libsodium-${libsodium_ver}.tar.gz + pushd libsodium-${libsodium_ver} > /dev/null + ./configure --disable-dependency-tracking --enable-minimal + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libsodium-${libsodium_ver} + fi + + if [ ! -e "/usr/local/lib/libzip.la" ]; then + tar xzf libzip-${libzip_ver}.tar.gz + pushd libzip-${libzip_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libzip-${libzip_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php81_ver}.tar.gz + pushd php-${php81_ver} > /dev/null + make clean + export PKG_CONFIG_PATH=/usr/local/lib/pkgconfig/:$PKG_CONFIG_PATH + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem ${php81_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php81_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem ${php81_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php81_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php81_ver} + popd > /dev/null +} diff --git a/include/php-8.2.sh b/include/php-8.2.sh new file mode 100644 index 0000000..d5ae197 --- /dev/null +++ b/include/php-8.2.sh @@ -0,0 +1,276 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP82() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php82_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/lib/pkgconfig/libargon2.pc" ]; then + tar xzf argon2-${argon2_ver}.tar.gz + pushd argon2-${argon2_ver} > /dev/null + make -j ${THREAD} && make install + [ ! -d /usr/local/lib/pkgconfig ] && mkdir -p /usr/local/lib/pkgconfig + /bin/cp libargon2.pc /usr/local/lib/pkgconfig/ + popd > /dev/null + rm -rf argon2-${argon2_ver} + fi + + if [ ! -e "/usr/local/lib/libsodium.la" ]; then + tar xzf libsodium-${libsodium_up_ver}.tar.gz + pushd libsodium-${libsodium_up_ver} > /dev/null + ./configure --disable-dependency-tracking --enable-minimal + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libsodium-${libsodium_up_ver} + fi + + if [ ! -e "/usr/local/lib/libzip.la" ]; then + tar xzf libzip-${libzip_ver}.tar.gz + pushd libzip-${libzip_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libzip-${libzip_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php82_ver}.tar.gz + pushd php-${php82_ver} > /dev/null + make clean + export PKG_CONFIG_PATH=/usr/local/lib/pkgconfig/:$PKG_CONFIG_PATH + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem ${php82_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php82_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem ${php82_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php82_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php82_ver} + popd > /dev/null +} diff --git a/include/php-8.3.sh b/include/php-8.3.sh new file mode 100644 index 0000000..4ae0f50 --- /dev/null +++ b/include/php-8.3.sh @@ -0,0 +1,276 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PHP83() { + pushd ${oneinstack_dir}/src > /dev/null + if [ ! -e "/usr/local/lib/libiconv.la" ]; then + tar xzf libiconv-${libiconv_ver}.tar.gz + pushd libiconv-${libiconv_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libiconv-${libiconv_ver} + fi + + if [ ! -e "${curl_install_dir}/lib/libcurl.la" ]; then + tar xzf curl-${curl_ver}.tar.gz + pushd curl-${curl_ver} > /dev/null + [ -e "/usr/local/lib/libnghttp2.so" ] && with_nghttp2='--with-nghttp2=/usr/local' + ./configure --prefix=${curl_install_dir} ${php83_with_ssl} ${with_nghttp2} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf curl-${curl_ver} + fi + + if [ ! -e "${freetype_install_dir}/lib/libfreetype.la" ]; then + tar xzf freetype-${freetype_ver}.tar.gz + pushd freetype-${freetype_ver} > /dev/null + ./configure --prefix=${freetype_install_dir} --enable-freetype-config + make -j ${THREAD} && make install + ln -sf ${freetype_install_dir}/include/freetype2/* /usr/include/ + [ -d /usr/lib/pkgconfig ] && /bin/cp ${freetype_install_dir}/lib/pkgconfig/freetype2.pc /usr/lib/pkgconfig/ + popd > /dev/null + rm -rf freetype-${freetype_ver} + fi + + if [ ! -e "/usr/local/lib/pkgconfig/libargon2.pc" ]; then + tar xzf argon2-${argon2_ver}.tar.gz + pushd argon2-${argon2_ver} > /dev/null + make -j ${THREAD} && make install + [ ! -d /usr/local/lib/pkgconfig ] && mkdir -p /usr/local/lib/pkgconfig + /bin/cp libargon2.pc /usr/local/lib/pkgconfig/ + popd > /dev/null + rm -rf argon2-${argon2_ver} + fi + + if [ ! -e "/usr/local/lib/libsodium.la" ]; then + tar xzf libsodium-${libsodium_up_ver}.tar.gz + pushd libsodium-${libsodium_up_ver} > /dev/null + ./configure --disable-dependency-tracking --enable-minimal + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libsodium-${libsodium_up_ver} + fi + + if [ ! -e "/usr/local/lib/libzip.la" ]; then + tar xzf libzip-${libzip_ver}.tar.gz + pushd libzip-${libzip_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf libzip-${libzip_ver} + fi + + if [ ! -e "/usr/local/include/mhash.h" -a ! -e "/usr/include/mhash.h" ]; then + tar xzf mhash-${mhash_ver}.tar.gz + pushd mhash-${mhash_ver} > /dev/null + ./configure + make -j ${THREAD} && make install + popd > /dev/null + rm -rf mhash-${mhash_ver} + fi + + [ -z "`grep /usr/local/lib /etc/ld.so.conf.d/*.conf`" ] && echo '/usr/local/lib' > /etc/ld.so.conf.d/local.conf + ldconfig + + if [ "${PM}" == 'yum' ]; then + [ ! -e "/lib64/libpcre.so.1" ] && ln -s /lib64/libpcre.so.0.0.1 /lib64/libpcre.so.1 + [ ! -e "/usr/lib/libc-client.so" ] && ln -s /usr/lib64/libc-client.so /usr/lib/libc-client.so + fi + + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf php-${php83_ver}.tar.gz + pushd php-${php83_ver} > /dev/null + make clean + export PKG_CONFIG_PATH=/usr/local/lib/pkgconfig/:$PKG_CONFIG_PATH + [ ! -d "${php_install_dir}" ] && mkdir -p ${php_install_dir} + [ "${phpcache_option}" == '1' ] && phpcache_arg='--enable-opcache' || phpcache_arg='--disable-opcache' + if [ "${apache_mode_option}" == '2' ]; then + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-apxs2=${apache_install_dir}/bin/apxs ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem ${php83_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php83_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + else + ./configure --prefix=${php_install_dir} --with-config-file-path=${php_install_dir}/etc \ + --with-config-file-scan-dir=${php_install_dir}/etc/php.d \ + --with-fpm-user=${run_user} --with-fpm-group=${run_group} --enable-fpm ${phpcache_arg} --disable-fileinfo \ + --enable-mysqlnd --with-mysqli=mysqlnd --with-pdo-mysql=mysqlnd \ + --with-iconv=/usr/local --with-freetype --with-jpeg --with-zlib \ + --enable-xml --disable-rpath --enable-bcmath --enable-shmop --enable-exif \ + --enable-sysvsem ${php83_with_curl} --enable-mbregex \ + --enable-mbstring --with-password-argon2 --with-sodium=/usr/local --enable-gd ${php83_with_openssl} \ + --with-mhash --enable-pcntl --enable-sockets --enable-ftp --enable-intl --with-xsl \ + --with-gettext --with-zip=/usr/local --enable-soap --disable-debug ${php_modules_options} + fi + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + make install + + if [ -e "${php_install_dir}/bin/phpize" ]; then + [ ! -e "${php_install_dir}/etc/php.d" ] && mkdir -p ${php_install_dir}/etc/php.d + echo "${CSUCCESS}PHP installed successfully! ${CEND}" + else + rm -rf ${php_install_dir} + echo "${CFAILURE}PHP install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${php_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${php_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${php_install_dir}/bin:\1@" /etc/profile + . /etc/profile + + # wget -c http://pear.php.net/go-pear.phar + # ${php_install_dir}/bin/php go-pear.phar + + /bin/cp php.ini-production ${php_install_dir}/etc/php.ini + + sed -i "s@^memory_limit.*@memory_limit = ${Memory_limit}M@" ${php_install_dir}/etc/php.ini + sed -i 's@^output_buffering =@output_buffering = On\noutput_buffering =@' ${php_install_dir}/etc/php.ini + #sed -i 's@^;cgi.fix_pathinfo.*@cgi.fix_pathinfo=0@' ${php_install_dir}/etc/php.ini + sed -i 's@^short_open_tag = Off@short_open_tag = On@' ${php_install_dir}/etc/php.ini + sed -i 's@^expose_php = On@expose_php = Off@' ${php_install_dir}/etc/php.ini + sed -i 's@^request_order.*@request_order = "CGP"@' ${php_install_dir}/etc/php.ini + sed -i "s@^;date.timezone.*@date.timezone = ${timezone}@" ${php_install_dir}/etc/php.ini + sed -i 's@^post_max_size.*@post_max_size = 100M@' ${php_install_dir}/etc/php.ini + sed -i 's@^upload_max_filesize.*@upload_max_filesize = 50M@' ${php_install_dir}/etc/php.ini + sed -i 's@^max_execution_time.*@max_execution_time = 600@' ${php_install_dir}/etc/php.ini + sed -i 's@^;realpath_cache_size.*@realpath_cache_size = 2M@' ${php_install_dir}/etc/php.ini + sed -i 's@^disable_functions.*@disable_functions = passthru,exec,system,chroot,chgrp,chown,shell_exec,proc_open,proc_get_status,ini_alter,ini_restore,dl,readlink,symlink,popepassthru,stream_socket_server,fsocket,popen@' ${php_install_dir}/etc/php.ini + [ -e /usr/sbin/sendmail ] && sed -i 's@^;sendmail_path.*@sendmail_path = /usr/sbin/sendmail -t -i@' ${php_install_dir}/etc/php.ini + if [ "${with_old_openssl_flag}" = 'y' ]; then + sed -i "s@^;curl.cainfo.*@curl.cainfo = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.cafile.*@openssl.cafile = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + sed -i "s@^;openssl.capath.*@openssl.capath = \"${openssl_install_dir}/cert.pem\"@" ${php_install_dir}/etc/php.ini + fi + + [ "${phpcache_option}" == '1' ] && cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + + if [ "${apache_mode_option}" != '2' ]; then + # php-fpm Init Script + /bin/cp ${oneinstack_dir}/init.d/php-fpm.service /lib/systemd/system/ + sed -i "s@/usr/local/php@${php_install_dir}@g" /lib/systemd/system/php-fpm.service + systemctl enable php-fpm + + cat > ${php_install_dir}/etc/php-fpm.conf < /dev/null + [ -e "${php_install_dir}/bin/phpize" ] && rm -rf php-${php83_ver} + popd > /dev/null +} diff --git a/include/phpmyadmin.sh b/include/phpmyadmin.sh new file mode 100644 index 0000000..ff56a86 --- /dev/null +++ b/include/phpmyadmin.sh @@ -0,0 +1,32 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_phpMyAdmin() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=`${php_install_dir}/bin/php-config --version` + PHP_main_ver=${PHP_detail_ver%.*} + if [[ "${PHP_main_ver}" =~ ^5.[3-6]$|^7.[0-1]$ ]]; then + tar xzf phpMyAdmin-${phpmyadmin_oldver}-all-languages.tar.gz + /bin/mv phpMyAdmin-${phpmyadmin_oldver}-all-languages ${wwwroot_dir}/default/phpMyAdmin + else + tar xzf phpMyAdmin-${phpmyadmin_ver}-all-languages.tar.gz + /bin/mv phpMyAdmin-${phpmyadmin_ver}-all-languages ${wwwroot_dir}/default/phpMyAdmin + fi + /bin/cp ${wwwroot_dir}/default/phpMyAdmin/{config.sample.inc.php,config.inc.php} + mkdir ${wwwroot_dir}/default/phpMyAdmin/{upload,save} + sed -i "s@UploadDir.*@UploadDir'\] = 'upload';@" ${wwwroot_dir}/default/phpMyAdmin/config.inc.php + sed -i "s@SaveDir.*@SaveDir'\] = 'save';@" ${wwwroot_dir}/default/phpMyAdmin/config.inc.php + sed -i "s@host'\].*@host'\] = '127.0.0.1';@" ${wwwroot_dir}/default/phpMyAdmin/config.inc.php + sed -i "s@blowfish_secret.*;@blowfish_secret\'\] = \'$(cat /dev/urandom | head -1 | base64 | head -c 32)\';@" ${wwwroot_dir}/default/phpMyAdmin/config.inc.php + chown -R ${run_user}:${run_group} ${wwwroot_dir}/default/phpMyAdmin + popd > /dev/null + fi +} diff --git a/include/postgresql.sh b/include/postgresql.sh new file mode 100644 index 0000000..3df686c --- /dev/null +++ b/include/postgresql.sh @@ -0,0 +1,51 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PostgreSQL() { + pushd ${oneinstack_dir}/src > /dev/null + id -u postgres >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -d ${pgsql_install_dir} -s /bin/bash postgres + mkdir -p ${pgsql_data_dir};chown postgres.postgres -R ${pgsql_data_dir} + tar xzf postgresql-${pgsql_ver}.tar.gz + pushd postgresql-${pgsql_ver} + ./configure --prefix=$pgsql_install_dir + make -j ${THREAD} + make install + chmod 755 ${pgsql_install_dir} + chown -R postgres.postgres ${pgsql_install_dir} + /bin/cp ${oneinstack_dir}/init.d/postgresql.service /lib/systemd/system/ + sed -i "s@=/usr/local/pgsql@=${pgsql_install_dir}@g" /lib/systemd/system/postgresql.service + sed -i "s@PGDATA=.*@PGDATA=${pgsql_data_dir}@" /lib/systemd/system/postgresql.service + systemctl enable postgresql + popd + su - postgres -c "${pgsql_install_dir}/bin/initdb -D ${pgsql_data_dir}" + systemctl start postgresql + sleep 5 + su - postgres -c "${pgsql_install_dir}/bin/psql -c \"alter user postgres with password '$dbpostgrespwd';\"" + sed -i 's@^host.*@#&@g' ${pgsql_data_dir}/pg_hba.conf + sed -i 's@^local.*@#&@g' ${pgsql_data_dir}/pg_hba.conf + echo 'local all all md5' >> ${pgsql_data_dir}/pg_hba.conf + echo 'host all all 0.0.0.0/0 md5' >> ${pgsql_data_dir}/pg_hba.conf + sed -i "s@^#listen_addresses.*@listen_addresses = '*'@" ${pgsql_data_dir}/postgresql.conf + systemctl reload postgresql + + if [ -e "${pgsql_install_dir}/bin/psql" ]; then + sed -i "s+^dbpostgrespwd.*+dbpostgrespwd='$dbpostgrespwd'+" ../options.conf + echo "${CSUCCESS}PostgreSQL installed successfully! ${CEND}" + else + rm -rf ${pgsql_install_dir} ${pgsql_data_dir} + echo "${CFAILURE}PostgreSQL install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + popd + [ -z "$(grep ^'export PATH=' /etc/profile)" ] && echo "export PATH=${pgsql_install_dir}/bin:\$PATH" >> /etc/profile + [ -n "$(grep ^'export PATH=' /etc/profile)" -a -z "$(grep ${pgsql_install_dir} /etc/profile)" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${pgsql_install_dir}/bin:\1@" /etc/profile + . /etc/profile +} diff --git a/include/pureftpd.sh b/include/pureftpd.sh new file mode 100644 index 0000000..03ae346 --- /dev/null +++ b/include/pureftpd.sh @@ -0,0 +1,65 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_PureFTPd() { + pushd ${oneinstack_dir}/src > /dev/null + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf pure-ftpd-${pureftpd_ver}.tar.gz + pushd pure-ftpd-${pureftpd_ver} > /dev/null + [ ! -d "${pureftpd_install_dir}" ] && mkdir -p ${pureftpd_install_dir} + ./configure --prefix=${pureftpd_install_dir} CFLAGS=-O2 --with-puredb --with-quotas --with-cookie --with-virtualhosts --with-virtualchroot --with-diraliases --with-sysquotas --with-ratios --with-altlog --with-paranoidmsg --with-shadow --with-welcomemsg --with-throttling --with-uploadscript --with-language=english --with-tls + make -j ${THREAD} && make install + popd > /dev/null + if [ -e "${pureftpd_install_dir}/sbin/pure-ftpwho" ]; then + /bin/cp ../init.d/pureftpd.service /lib/systemd/system/ + sed -i "s@/usr/local/pureftpd@${pureftpd_install_dir}@g" /lib/systemd/system/pureftpd.service + systemctl enable pureftpd + + [ ! -e "${pureftpd_install_dir}/etc" ] && mkdir ${pureftpd_install_dir}/etc + /bin/cp ../config/pure-ftpd.conf ${pureftpd_install_dir}/etc + sed -i "s@^PureDB.*@PureDB ${pureftpd_install_dir}/etc/pureftpd.pdb@" ${pureftpd_install_dir}/etc/pure-ftpd.conf + sed -i "s@^LimitRecursion.*@LimitRecursion 65535 8@" ${pureftpd_install_dir}/etc/pure-ftpd.conf + IPADDR=${IPADDR:-127.0.0.1} + [ ! -d /etc/ssl/private ] && mkdir -p /etc/ssl/private + openssl dhparam -out /etc/ssl/private/pure-ftpd-dhparams.pem 2048 + openssl req -x509 -days 7300 -sha256 -nodes -subj "/C=CN/ST=Shanghai/L=Shanghai/O=OneinStack/CN=${IPADDR}" -newkey rsa:2048 -keyout /etc/ssl/private/pure-ftpd.pem -out /etc/ssl/private/pure-ftpd.pem + chmod 600 /etc/ssl/private/pure-ftpd*.pem + sed -i "s@^# TLS.*@&\nCertFile /etc/ssl/private/pure-ftpd.pem@" ${pureftpd_install_dir}/etc/pure-ftpd.conf + sed -i "s@^# TLS.*@&\nTLSCipherSuite HIGH:MEDIUM:+TLSv1:\!SSLv2:\!SSLv3@" ${pureftpd_install_dir}/etc/pure-ftpd.conf + sed -i "s@^# TLS.*@TLS 1@" ${pureftpd_install_dir}/etc/pure-ftpd.conf + ulimit -s unlimited + systemctl start pureftpd + + # Firewall Ftp + if [ "${PM}" == 'yum' ]; then + if [ "`firewall-cmd --state`" == "running" ]; then + firewall-cmd --permanent --zone=public --add-port={21/tcp,20000-30000/tcp} + firewall-cmd --reload + fi + elif [ "${PM}" == 'apt-get' ]; then + if ufw status | grep -wq active; then + ufw allow 21/tcp + ufw allow 20000:30000/tcp + fi + fi + + echo "${CSUCCESS}Pure-Ftp installed successfully! ${CEND}" + rm -rf pure-ftpd-${pureftpd_ver} + else + rm -rf ${pureftpd_install_dir} + echo "${CFAILURE}Pure-Ftpd install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + popd > /dev/null +} diff --git a/include/redis.sh b/include/redis.sh new file mode 100644 index 0000000..1e21b9e --- /dev/null +++ b/include/redis.sh @@ -0,0 +1,85 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_redis_server() { + pushd ${oneinstack_dir}/src > /dev/null + tar xzf redis-${redis_ver}.tar.gz + pushd redis-${redis_ver} > /dev/null + make -j ${THREAD} + if [ -f "src/redis-server" ]; then + mkdir -p ${redis_install_dir}/{bin,etc,var} + /bin/cp src/{redis-benchmark,redis-check-aof,redis-check-rdb,redis-cli,redis-sentinel,redis-server} ${redis_install_dir}/bin/ + /bin/cp redis.conf ${redis_install_dir}/etc/ + ln -s ${redis_install_dir}/bin/* /usr/local/bin/ + sed -i 's@pidfile.*@pidfile /var/run/redis/redis.pid@' ${redis_install_dir}/etc/redis.conf + sed -i "s@logfile.*@logfile ${redis_install_dir}/var/redis.log@" ${redis_install_dir}/etc/redis.conf + sed -i "s@^dir.*@dir ${redis_install_dir}/var@" ${redis_install_dir}/etc/redis.conf + sed -i 's@daemonize no@daemonize yes@' ${redis_install_dir}/etc/redis.conf + sed -i "s@^# bind 127.0.0.1@bind 127.0.0.1@" ${redis_install_dir}/etc/redis.conf + redis_maxmemory=`expr $Mem / 8`000000 + [ -z "`grep ^maxmemory ${redis_install_dir}/etc/redis.conf`" ] && sed -i "s@maxmemory @maxmemory \nmaxmemory `expr $Mem / 8`000000@" ${redis_install_dir}/etc/redis.conf + echo "${CSUCCESS}Redis-server installed successfully! ${CEND}" + popd > /dev/null + rm -rf redis-${redis_ver} + id -u redis >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -M -s /sbin/nologin redis + chown -R redis:redis ${redis_install_dir}/{var,etc} + + /bin/cp ../init.d/redis-server.service /lib/systemd/system/ + sed -i "s@/usr/local/redis@${redis_install_dir}@g" /lib/systemd/system/redis-server.service + systemctl enable redis-server + #[ -z "`grep 'vm.overcommit_memory' /etc/sysctl.conf`" ] && echo 'vm.overcommit_memory = 1' >> /etc/sysctl.conf + #sysctl -p + systemctl start redis-server + else + rm -rf ${redis_install_dir} + echo "${CFAILURE}Redis-server install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + popd > /dev/null +} + +Install_pecl_redis() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=`${php_install_dir}/bin/php-config --extension-dir` + if [ "$(${php_install_dir}/bin/php-config --version | awk -F. '{print $1}')" == '5' ]; then + tar xzf redis-4.3.0.tgz + pushd redis-4.3.0 > /dev/null + elif [[ "$(${php_install_dir}/bin/php-config --version | awk -F. '{print $1$2}')" =~ ^7[0-1]$ ]]; then + tar xzf redis-5.3.7.tgz + pushd redis-5.3.7 > /dev/null + else + tar xzf redis-${pecl_redis_ver}.tgz + pushd redis-${pecl_redis_ver} > /dev/null + fi + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/redis.so" ]; then + echo 'extension=redis.so' > ${php_install_dir}/etc/php.d/05-redis.ini + echo "${CSUCCESS}PHP Redis module installed successfully! ${CEND}" + rm -rf redis-${pecl_redis_ver} redis-4.3.0 redis-5.3.7 + else + echo "${CFAILURE}PHP Redis module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_pecl_redis() { + if [ -e "${php_install_dir}/etc/php.d/05-redis.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/05-redis.ini + echo; echo "${CMSG}PHP redis module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP redis module does not exist! ${CEND}" + fi +} diff --git a/include/sourceguardian.sh b/include/sourceguardian.sh new file mode 100644 index 0000000..06ea553 --- /dev/null +++ b/include/sourceguardian.sh @@ -0,0 +1,49 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_SourceGuardian() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + PHP_detail_ver=`${php_install_dir}/bin/php-config --version` + PHP_main_ver=${PHP_detail_ver%.*} + phpExtensionDir=`${php_install_dir}/bin/php-config --extension-dir` + [ ! -e sourceguardian ] && mkdir sourceguardian + [ -e "loaders.linux-${ARCH}.tar.gz" ] && tar xzf loaders.linux-${ARCH}.tar.gz -C sourceguardian + + if [ -e "sourceguardian/ixed.${PHP_main_ver}.lin" ]; then + [ ! -d "${phpExtensionDir}" ] && mkdir -p ${phpExtensionDir} + if [ -z "`echo ${phpExtensionDir} | grep 'non-zts'`" ]; then + /bin/mv sourceguardian/ixed.${PHP_main_ver}ts.lin ${phpExtensionDir} + extension="ixed.${PHP_main_ver}ts.lin" + else + /bin/mv sourceguardian/ixed.${PHP_main_ver}.lin ${phpExtensionDir} + extension="ixed.${PHP_main_ver}.lin" + fi + + if [ -f "${phpExtensionDir}/ixed.${PHP_main_ver}.lin" ]; then + echo "extension=${extension}" > ${php_install_dir}/etc/php.d/02-sourceguardian.ini + echo "${CSUCCESS}PHP SourceGuardian module installed successfully! ${CEND}" + rm -rf sourceguardian + fi + else + echo; echo "${CWARNING}Your php ${PHP_detail_ver} or platform ${TARGET_ARCH} does not support SourceGuardian! ${CEND}"; + fi + popd > /dev/null + fi +} + +Uninstall_SourceGuardian() { + if [ -e "${php_install_dir}/etc/php.d/02-sourceguardian.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/02-sourceguardian.ini + echo; echo "${CMSG}PHP SourceGuardian module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP SourceGuardian module does not exist! ${CEND}" + fi +} diff --git a/include/tengine.sh b/include/tengine.sh new file mode 100644 index 0000000..ca0318e --- /dev/null +++ b/include/tengine.sh @@ -0,0 +1,94 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Tengine() { + pushd ${oneinstack_dir}/src > /dev/null + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /sbin/nologin ${run_user} + + tar xzf pcre-${pcre_ver}.tar.gz + tar xzf tengine-${tengine_ver}.tar.gz + tar xzf openssl-${openssl11_ver}.tar.gz + pushd tengine-${tengine_ver} > /dev/null + # Modify Tengine version + #sed -i 's@TENGINE "/" TENGINE_VERSION@"Tengine/unknown"@' src/core/nginx.h + + [ ! -d "${tengine_install_dir}" ] && mkdir -p ${tengine_install_dir} + ./configure --prefix=${tengine_install_dir} --user=${run_user} --group=${run_group} --with-http_v2_module --with-http_ssl_module --with-stream --with-stream_ssl_preread_module --with-stream_ssl_module --with-http_gzip_static_module --with-http_realip_module --with-http_flv_module --with-http_mp4_module --with-openssl=../openssl-${openssl11_ver} --with-pcre=../pcre-${pcre_ver} --with-pcre-jit --with-jemalloc ${nginx_modules_options} + make && make install + if [ -e "${tengine_install_dir}/conf/nginx.conf" ]; then + popd > /dev/null + rm -rf pcre-${pcre_ver}* openssl-${openssl11_ver}* tengine-${tengine_ver}* rm -rf ${tengine_install_dir}* + echo "${CSUCCESS}Tengine installed successfully! ${CEND}" + else + rm -rf pcre-${pcre_ver}* openssl-${openssl11_ver}* tengine-${tengine_ver}* rm -rf ${tengine_install_dir}* + echo "${CFAILURE}Tengine install failed, Please Contact the author! ${CEND}" + kill -9 $$; exit 1; + fi + + [ -z "`grep ^'export PATH=' /etc/profile`" ] && echo "export PATH=${tengine_install_dir}/sbin:\$PATH" >> /etc/profile + [ -n "`grep ^'export PATH=' /etc/profile`" -a -z "`grep ${tengine_install_dir} /etc/profile`" ] && sed -i "s@^export PATH=\(.*\)@export PATH=${tengine_install_dir}/sbin:\1@" /etc/profile + . /etc/profile + + /bin/cp ../init.d/nginx.service /lib/systemd/system/ + sed -i "s@/usr/local/nginx@${tengine_install_dir}@g" /lib/systemd/system/nginx.service + systemctl enable nginx + + mv ${tengine_install_dir}/conf/nginx.conf{,_bk} + if [ "${apache_flag}" == 'y' ] || [ -e "${apache_install_dir}/bin/httpd" ]; then + /bin/cp ../config/nginx_apache.conf ${tengine_install_dir}/conf/nginx.conf + elif { [[ ${tomcat_option} =~ ^[1-4]$ ]] || [ -e "${tomcat_install_dir}/conf/server.xml" ]; } && { [[ ! ${php_option} =~ ^[1-9]$|^1[0-1]$ ]] && [ ! -e "${php_install_dir}/bin/php" ]; }; then + /bin/cp ../config/nginx_tomcat.conf ${tengine_install_dir}/conf/nginx.conf + else + /bin/cp ../config/nginx.conf ${tengine_install_dir}/conf/nginx.conf + [[ "${php_option}" =~ ^[1-9]$|^1[0-1]$ ]] && [ -z "`grep '/php-fpm_status' ${tengine_install_dir}/conf/nginx.conf`" ] && sed -i "s@index index.html index.php;@index index.html index.php;\n location ~ /php-fpm_status {\n #fastcgi_pass remote_php_ip:9000;\n fastcgi_pass unix:/dev/shm/php-cgi.sock;\n fastcgi_index index.php;\n include fastcgi.conf;\n allow 127.0.0.1;\n deny all;\n }@" ${tengine_install_dir}/conf/nginx.conf + fi + cat > ${tengine_install_dir}/conf/proxy.conf << EOF +proxy_connect_timeout 300s; +proxy_send_timeout 900; +proxy_read_timeout 900; +proxy_buffer_size 32k; +proxy_buffers 4 64k; +proxy_busy_buffers_size 128k; +proxy_redirect off; +proxy_hide_header Vary; +proxy_set_header Accept-Encoding ''; +proxy_set_header Referer \$http_referer; +proxy_set_header Cookie \$http_cookie; +proxy_set_header Host \$host; +proxy_set_header X-Real-IP \$remote_addr; +proxy_set_header X-Forwarded-For \$proxy_add_x_forwarded_for; +proxy_set_header X-Forwarded-Proto \$scheme; +EOF + sed -i "s@/data/wwwroot/default@${wwwroot_dir}/default@" ${tengine_install_dir}/conf/nginx.conf + sed -i "s@/data/wwwlogs@${wwwlogs_dir}@g" ${tengine_install_dir}/conf/nginx.conf + sed -i "s@^user www www@user ${run_user} ${run_group}@" ${tengine_install_dir}/conf/nginx.conf + + # logrotate nginx log + cat > /etc/logrotate.d/nginx << EOF +${wwwlogs_dir}/*nginx.log { + daily + rotate 5 + missingok + dateext + compress + notifempty + sharedscripts + postrotate + [ -e /var/run/nginx.pid ] && kill -USR1 \`cat /var/run/nginx.pid\` + endscript +} +EOF + popd > /dev/null + ldconfig + systemctl start nginx +} diff --git a/include/tomcat-10.sh b/include/tomcat-10.sh new file mode 100644 index 0000000..51ace21 --- /dev/null +++ b/include/tomcat-10.sh @@ -0,0 +1,129 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Tomcat10() { + pushd ${oneinstack_dir}/src > /dev/null + . /etc/profile + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /bin/bash ${run_user} || { [ -z "$(grep ^${run_user} /etc/passwd | grep '/bin/bash')" ] && usermod -g ${run_group} -s /bin/bash ${run_user}; } + + # install apr + if [ ! -e "${apr_install_dir}/bin/apr-1-config" ]; then + tar xzf apr-${apr_ver}.tar.gz + pushd apr-${apr_ver} > /dev/null + ./configure --prefix=${apr_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf apr-${apr_ver} + fi + + tar xzf apache-tomcat-${tomcat10_ver}.tar.gz + [ ! -d "${tomcat_install_dir}" ] && mkdir -p ${tomcat_install_dir} + /bin/cp -R apache-tomcat-${tomcat10_ver}/* ${tomcat_install_dir} + rm -rf ${tomcat_install_dir}/webapps/{docs,examples,host-manager,manager,ROOT/*} + + if [ ! -e "${tomcat_install_dir}/conf/server.xml" ]; then + rm -rf ${tomcat_install_dir} + echo "${CFAILURE}Tomcat install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + pushd ${tomcat_install_dir}/bin > /dev/null + tar xzf tomcat-native.tar.gz + pushd tomcat-native-*-src/native > /dev/null + if [ "${armplatform}" == "y" ]; then + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} + else + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} --with-ssl=${openssl_install_dir} + fi + make -j ${THREAD} && make install + popd > /dev/null + rm -rf tomcat-native-* + if [ -e "${apr_install_dir}/lib/libtcnative-1.la" ]; then + [ ${Mem} -le 768 ] && let Xms_Mem="${Mem}/3" || Xms_Mem=256 + let XmxMem="${Mem}/2" + cat > ${tomcat_install_dir}/bin/setenv.sh << EOF +JAVA_OPTS='-Djava.security.egd=file:/dev/./urandom -server -Xms${Xms_Mem}m -Xmx${XmxMem}m -Dfile.encoding=UTF-8' +CATALINA_OPTS="-Djava.library.path=${apr_install_dir}/lib" +# -Djava.rmi.server.hostname=$IPADDR +# -Dcom.sun.management.jmxremote.password.file=\$CATALINA_BASE/conf/jmxremote.password +# -Dcom.sun.management.jmxremote.access.file=\$CATALINA_BASE/conf/jmxremote.access +# -Dcom.sun.management.jmxremote.ssl=false" +EOF + chmod +x ./*.sh + /bin/mv ${tomcat_install_dir}/conf/server.xml{,_bk} + popd # goto ${oneinstack_dir}/src + /bin/cp ${oneinstack_dir}/config/server.xml ${tomcat_install_dir}/conf + sed -i "s@/usr/local/tomcat@${tomcat_install_dir}@g" ${tomcat_install_dir}/conf/server.xml + + if [ ! -e "${nginx_install_dir}/sbin/nginx" -a ! -e "${tengine_install_dir}/sbin/nginx" -a ! -e "${openresty_install_dir}/nginx/sbin/nginx" -a ! -e "${apache_install_dir}/bin/httpd" ]; then + if [ "${PM}" == 'yum' ]; then + if [ "`firewall-cmd --state`" == "running" ]; then + firewall-cmd --permanent --zone=public --add-port=8080/tcp + firewall-cmd --reload + fi + elif [ "${PM}" == 'apt-get' ]; then + if ufw status | grep -wq active; then + ufw allow 8080/tcp + fi + fi + fi + + [ ! -d "${tomcat_install_dir}/conf/vhost" ] && mkdir ${tomcat_install_dir}/conf/vhost + cat > ${tomcat_install_dir}/conf/vhost/localhost.xml << EOF + + + + + +EOF + # logrotate tomcat catalina.out + cat > /etc/logrotate.d/tomcat << EOF +${tomcat_install_dir}/logs/catalina.out { + daily + rotate 5 + missingok + dateext + compress + notifempty + copytruncate +} +EOF + [ -z "$(grep ' /dev/null + echo "${CFAILURE}Tomcat install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + service tomcat start + popd > /dev/null +} diff --git a/include/tomcat-7.sh b/include/tomcat-7.sh new file mode 100644 index 0000000..dc94bff --- /dev/null +++ b/include/tomcat-7.sh @@ -0,0 +1,131 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Tomcat7() { + pushd ${oneinstack_dir}/src > /dev/null + . /etc/profile + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /bin/bash ${run_user} || { [ -z "$(grep ^${run_user} /etc/passwd | grep '/bin/bash')" ] && usermod -g ${run_group} -s /bin/bash ${run_user}; } + + # install apr + if [ ! -e "${apr_install_dir}/bin/apr-1-config" ]; then + tar xzf apr-${apr_ver}.tar.gz + pushd apr-${apr_ver} > /dev/null + ./configure --prefix=${apr_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf apr-${apr_ver} + fi + + tar xzf apache-tomcat-${tomcat7_ver}.tar.gz + [ ! -d "${tomcat_install_dir}" ] && mkdir -p ${tomcat_install_dir} + /bin/cp -R apache-tomcat-${tomcat7_ver}/* ${tomcat_install_dir} + rm -rf ${tomcat_install_dir}/webapps/{docs,examples,host-manager,manager,ROOT/*} + + if [ ! -e "${tomcat_install_dir}/conf/server.xml" ]; then + rm -rf ${tomcat_install_dir} + echo "${CFAILURE}Tomcat install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + /bin/cp catalina-jmx-remote.jar ${tomcat_install_dir}/lib + + pushd ${tomcat_install_dir}/bin > /dev/null + tar xzf tomcat-native.tar.gz + pushd tomcat-native-*-src/native > /dev/null + if [ "${armplatform}" == "y" ]; then + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} + else + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} --with-ssl=${openssl_install_dir} + fi + make -j ${THREAD} && make install + popd > /dev/null + rm -rf tomcat-native-* + if [ -e "${apr_install_dir}/lib/libtcnative-1.la" ]; then + [ ${Mem} -le 768 ] && let Xms_Mem="${Mem}/3" || Xms_Mem=256 + let XmxMem="${Mem}/2" + cat > ${tomcat_install_dir}/bin/setenv.sh << EOF +JAVA_OPTS='-Djava.security.egd=file:/dev/./urandom -server -Xms${Xms_Mem}m -Xmx${XmxMem}m -Dfile.encoding=UTF-8' +CATALINA_OPTS="-Djava.library.path=${apr_install_dir}/lib" +# -Djava.rmi.server.hostname=$IPADDR +# -Dcom.sun.management.jmxremote.password.file=\$CATALINA_BASE/conf/jmxremote.password +# -Dcom.sun.management.jmxremote.access.file=\$CATALINA_BASE/conf/jmxremote.access +# -Dcom.sun.management.jmxremote.ssl=false" +EOF + chmod +x ./*.sh + /bin/mv ${tomcat_install_dir}/conf/server.xml{,_bk} + popd # goto ${oneinstack_dir}/src + /bin/cp ${oneinstack_dir}/config/server.xml ${tomcat_install_dir}/conf + sed -i "s@/usr/local/tomcat@${tomcat_install_dir}@g" ${tomcat_install_dir}/conf/server.xml + + if [ ! -e "${nginx_install_dir}/sbin/nginx" -a ! -e "${tengine_install_dir}/sbin/nginx" -a ! -e "${openresty_install_dir}/nginx/sbin/nginx" -a ! -e "${apache_install_dir}/bin/httpd" ]; then + if [ "${PM}" == 'yum' ]; then + if [ "`firewall-cmd --state`" == "running" ]; then + firewall-cmd --permanent --zone=public --add-port=8080/tcp + firewall-cmd --reload + fi + elif [ "${PM}" == 'apt-get' ]; then + if ufw status | grep -wq active; then + ufw allow 8080/tcp + fi + fi + fi + + [ ! -d "${tomcat_install_dir}/conf/vhost" ] && mkdir ${tomcat_install_dir}/conf/vhost + cat > ${tomcat_install_dir}/conf/vhost/localhost.xml << EOF + + + + + +EOF + # logrotate tomcat catalina.out + cat > /etc/logrotate.d/tomcat << EOF +${tomcat_install_dir}/logs/catalina.out { + daily + rotate 5 + missingok + dateext + compress + notifempty + copytruncate +} +EOF + [ -z "$(grep ' /dev/null + echo "${CFAILURE}Tomcat install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + service tomcat start + popd > /dev/null +} diff --git a/include/tomcat-8.sh b/include/tomcat-8.sh new file mode 100644 index 0000000..3efd28d --- /dev/null +++ b/include/tomcat-8.sh @@ -0,0 +1,129 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Tomcat8() { + pushd ${oneinstack_dir}/src > /dev/null + . /etc/profile + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /bin/bash ${run_user} || { [ -z "$(grep ^${run_user} /etc/passwd | grep '/bin/bash')" ] && usermod -g ${run_group} -s /bin/bash ${run_user}; } + + # install apr + if [ ! -e "${apr_install_dir}/bin/apr-1-config" ]; then + tar xzf apr-${apr_ver}.tar.gz + pushd apr-${apr_ver} > /dev/null + ./configure --prefix=${apr_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf apr-${apr_ver} + fi + + tar xzf apache-tomcat-${tomcat8_ver}.tar.gz + [ ! -d "${tomcat_install_dir}" ] && mkdir -p ${tomcat_install_dir} + /bin/cp -R apache-tomcat-${tomcat8_ver}/* ${tomcat_install_dir} + rm -rf ${tomcat_install_dir}/webapps/{docs,examples,host-manager,manager,ROOT/*} + + if [ ! -e "${tomcat_install_dir}/conf/server.xml" ]; then + rm -rf ${tomcat_install_dir} + echo "${CFAILURE}Tomcat install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + pushd ${tomcat_install_dir}/bin > /dev/null + tar xzf tomcat-native.tar.gz + pushd tomcat-native-*-src/native > /dev/null + if [ "${armplatform}" == "y" ]; then + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} + else + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} --with-ssl=${openssl_install_dir} + fi + make -j ${THREAD} && make install + popd > /dev/null + rm -rf tomcat-native-* + if [ -e "${apr_install_dir}/lib/libtcnative-1.la" ]; then + [ ${Mem} -le 768 ] && let Xms_Mem="${Mem}/3" || Xms_Mem=256 + let XmxMem="${Mem}/2" + cat > ${tomcat_install_dir}/bin/setenv.sh << EOF +JAVA_OPTS='-Djava.security.egd=file:/dev/./urandom -server -Xms${Xms_Mem}m -Xmx${XmxMem}m -Dfile.encoding=UTF-8' +CATALINA_OPTS="-Djava.library.path=${apr_install_dir}/lib" +# -Djava.rmi.server.hostname=$IPADDR +# -Dcom.sun.management.jmxremote.password.file=\$CATALINA_BASE/conf/jmxremote.password +# -Dcom.sun.management.jmxremote.access.file=\$CATALINA_BASE/conf/jmxremote.access +# -Dcom.sun.management.jmxremote.ssl=false" +EOF + chmod +x ./*.sh + /bin/mv ${tomcat_install_dir}/conf/server.xml{,_bk} + popd # goto ${oneinstack_dir}/src + /bin/cp ${oneinstack_dir}/config/server.xml ${tomcat_install_dir}/conf + sed -i "s@/usr/local/tomcat@${tomcat_install_dir}@g" ${tomcat_install_dir}/conf/server.xml + + if [ ! -e "${nginx_install_dir}/sbin/nginx" -a ! -e "${tengine_install_dir}/sbin/nginx" -a ! -e "${openresty_install_dir}/nginx/sbin/nginx" -a ! -e "${apache_install_dir}/bin/httpd" ]; then + if [ "${PM}" == 'yum' ]; then + if [ "`firewall-cmd --state`" == "running" ]; then + firewall-cmd --permanent --zone=public --add-port=8080/tcp + firewall-cmd --reload + fi + elif [ "${PM}" == 'apt-get' ]; then + if ufw status | grep -wq active; then + ufw allow 8080/tcp + fi + fi + fi + + [ ! -d "${tomcat_install_dir}/conf/vhost" ] && mkdir ${tomcat_install_dir}/conf/vhost + cat > ${tomcat_install_dir}/conf/vhost/localhost.xml << EOF + + + + + +EOF + # logrotate tomcat catalina.out + cat > /etc/logrotate.d/tomcat << EOF +${tomcat_install_dir}/logs/catalina.out { + daily + rotate 5 + missingok + dateext + compress + notifempty + copytruncate +} +EOF + [ -z "$(grep ' /dev/null + echo "${CFAILURE}Tomcat install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + service tomcat start + popd > /dev/null +} diff --git a/include/tomcat-9.sh b/include/tomcat-9.sh new file mode 100644 index 0000000..82ef4d1 --- /dev/null +++ b/include/tomcat-9.sh @@ -0,0 +1,129 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_Tomcat9() { + pushd ${oneinstack_dir}/src > /dev/null + . /etc/profile + id -g ${run_group} >/dev/null 2>&1 + [ $? -ne 0 ] && groupadd ${run_group} + id -u ${run_user} >/dev/null 2>&1 + [ $? -ne 0 ] && useradd -g ${run_group} -M -s /bin/bash ${run_user} || { [ -z "$(grep ^${run_user} /etc/passwd | grep '/bin/bash')" ] && usermod -g ${run_group} -s /bin/bash ${run_user}; } + + # install apr + if [ ! -e "${apr_install_dir}/bin/apr-1-config" ]; then + tar xzf apr-${apr_ver}.tar.gz + pushd apr-${apr_ver} > /dev/null + ./configure --prefix=${apr_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf apr-${apr_ver} + fi + + tar xzf apache-tomcat-${tomcat9_ver}.tar.gz + [ ! -d "${tomcat_install_dir}" ] && mkdir -p ${tomcat_install_dir} + /bin/cp -R apache-tomcat-${tomcat9_ver}/* ${tomcat_install_dir} + rm -rf ${tomcat_install_dir}/webapps/{docs,examples,host-manager,manager,ROOT/*} + + if [ ! -e "${tomcat_install_dir}/conf/server.xml" ]; then + rm -rf ${tomcat_install_dir} + echo "${CFAILURE}Tomcat install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + kill -9 $$; exit 1; + fi + + pushd ${tomcat_install_dir}/bin > /dev/null + tar xzf tomcat-native.tar.gz + pushd tomcat-native-*-src/native > /dev/null + if [ "${armplatform}" == "y" ]; then + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} + else + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} --with-ssl=${openssl_install_dir} + fi + make -j ${THREAD} && make install + popd > /dev/null + rm -rf tomcat-native-* + if [ -e "${apr_install_dir}/lib/libtcnative-1.la" ]; then + [ ${Mem} -le 768 ] && let Xms_Mem="${Mem}/3" || Xms_Mem=256 + let XmxMem="${Mem}/2" + cat > ${tomcat_install_dir}/bin/setenv.sh << EOF +JAVA_OPTS='-Djava.security.egd=file:/dev/./urandom -server -Xms${Xms_Mem}m -Xmx${XmxMem}m -Dfile.encoding=UTF-8' +CATALINA_OPTS="-Djava.library.path=${apr_install_dir}/lib" +# -Djava.rmi.server.hostname=$IPADDR +# -Dcom.sun.management.jmxremote.password.file=\$CATALINA_BASE/conf/jmxremote.password +# -Dcom.sun.management.jmxremote.access.file=\$CATALINA_BASE/conf/jmxremote.access +# -Dcom.sun.management.jmxremote.ssl=false" +EOF + chmod +x ./*.sh + /bin/mv ${tomcat_install_dir}/conf/server.xml{,_bk} + popd # goto ${oneinstack_dir}/src + /bin/cp ${oneinstack_dir}/config/server.xml ${tomcat_install_dir}/conf + sed -i "s@/usr/local/tomcat@${tomcat_install_dir}@g" ${tomcat_install_dir}/conf/server.xml + + if [ ! -e "${nginx_install_dir}/sbin/nginx" -a ! -e "${tengine_install_dir}/sbin/nginx" -a ! -e "${openresty_install_dir}/nginx/sbin/nginx" -a ! -e "${apache_install_dir}/bin/httpd" ]; then + if [ "${PM}" == 'yum' ]; then + if [ "`firewall-cmd --state`" == "running" ]; then + firewall-cmd --permanent --zone=public --add-port=8080/tcp + firewall-cmd --reload + fi + elif [ "${PM}" == 'apt-get' ]; then + if ufw status | grep -wq active; then + ufw allow 8080/tcp + fi + fi + fi + + [ ! -d "${tomcat_install_dir}/conf/vhost" ] && mkdir ${tomcat_install_dir}/conf/vhost + cat > ${tomcat_install_dir}/conf/vhost/localhost.xml << EOF + + + + + +EOF + # logrotate tomcat catalina.out + cat > /etc/logrotate.d/tomcat << EOF +${tomcat_install_dir}/logs/catalina.out { + daily + rotate 5 + missingok + dateext + compress + notifempty + copytruncate +} +EOF + [ -z "$(grep ' /dev/null + echo "${CFAILURE}Tomcat install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + service tomcat start + popd > /dev/null +} diff --git a/include/upgrade_db.sh b/include/upgrade_db.sh new file mode 100644 index 0000000..ec4e526 --- /dev/null +++ b/include/upgrade_db.sh @@ -0,0 +1,179 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Upgrade_DB() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${db_install_dir}/bin/mysql" ] && echo "${CWARNING}MySQL/MariaDB/Percona is not installed on your system! ${CEND}" && exit 1 + [ "${armplatform}" == 'y' ] && echo "${CWARNING}The arm architecture operating system does not support upgrading MySQL/MariaDB/Percona! ${CEND}" && exit 1 + + # check db passwd + while :; do + ${db_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "quit" > /dev/null 2>&1 + if [ $? -eq 0 ]; then + break + else + echo + read -e -p "Please input the root password of database: " NEW_dbrootpwd + ${db_install_dir}/bin/mysql -uroot -p${NEW_dbrootpwd} -e "quit" >/dev/null 2>&1 + if [ $? -eq 0 ]; then + dbrootpwd=${NEW_dbrootpwd} + sed -i "s+^dbrootpwd.*+dbrootpwd='$dbrootpwd'+" ../options.conf + break + else + echo "${CFAILURE}${DB} root password incorrect,Please enter again! ${CEND}" + fi + fi + done + + OLD_db_ver_tmp=`${db_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e 'select version()\G;' | grep version | awk '{print $2}'` + if [ -n "`${db_install_dir}/bin/mysql -V | grep -o MariaDB`" ]; then + [ "${OUTIP_STATE}"x == "China"x ] && DOWN_ADDR=https://mirrors.tuna.tsinghua.edu.cn/mariadb || DOWN_ADDR=https://archive.mariadb.org + DB=MariaDB + OLD_db_ver=`echo ${OLD_db_ver_tmp} | awk -F'-' '{print $1}'` + elif [ -n "`${db_install_dir}/bin/mysql -V | grep -o Percona`" ]; then + DB=Percona + OLD_db_ver=${OLD_db_ver_tmp} + else + #[ "${OUTIP_STATE}"x == "China"x ] && DOWN_ADDR=http://mirrors.ustc.edu.cn/mysql-ftp/Downloads || DOWN_ADDR=http://cdn.mysql.com/Downloads + DOWN_ADDR=http://cdn.mysql.com/Downloads + DB=MySQL + OLD_db_ver=${OLD_db_ver_tmp%%-log} + fi + + #backup + echo + echo "${CSUCCESS}Starting ${DB} backup${CEND}......" + ${db_install_dir}/bin/mysqldump -uroot -p${dbrootpwd} --opt --all-databases > DB_all_backup_$(date +"%Y%m%d").sql + [ -f "DB_all_backup_$(date +"%Y%m%d").sql" ] && echo "${DB} backup success, Backup file: ${MSG}`pwd`/DB_all_backup_$(date +"%Y%m%d").sql${CEND}" + + #upgrade + echo + echo "Current ${DB} Version: ${CMSG}${OLD_db_ver}${CEND}" + while :; do echo + [ "${db_flag}" != 'y' ] && read -e -p "Please input upgrade ${DB} Version(example: ${OLD_db_ver}): " NEW_db_ver + if [ `echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'` == `echo ${OLD_db_ver} | awk -F. '{print $1"."$2}'` ]; then + if [ "${DB}" == 'MariaDB' ]; then + DB_filename=mariadb-${NEW_db_ver}-linux-systemd-x86_64 + DB_URL=${DOWN_ADDR}/mariadb-${NEW_db_ver}/bintar-linux-systemd-x86_64/${DB_filename}.tar.gz + elif [ "${DB}" == 'Percona' ]; then + if [[ "`echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'`" =~ ^5.[5-6]$ ]]; then + perconaVerStr1=$(echo ${NEW_db_ver} | sed "s@-@-rel@") + else + perconaVerStr1=${NEW_db_ver} + fi + if [[ "`echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'`" =~ ^8.0$ ]]; then + DB_filename=Percona-Server-${perconaVerStr1}-Linux.x86_64.glibc2.28 + elif [[ "`echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'`" =~ ^5.7$ ]]; then + DB_filename=Percona-Server-${perconaVerStr1}-Linux.x86_64.glibc2.17 + else + DB_filename=Percona-Server-${perconaVerStr1}-Linux.x86_64.${sslLibVer} + fi + DB_URL=https://www.percona.com/downloads/Percona-Server-`echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'`/Percona-Server-${NEW_db_ver}/binary/tarball/${DB_filename}.tar.gz + elif [ "${DB}" == 'MySQL' ]; then + DB_filename=mysql-${NEW_db_ver}-linux-glibc2.12-x86_64 + if [ `echo ${OLD_db_ver} | awk -F. '{print $1"."$2}'` == '8.0' ]; then + DB_URL=${DOWN_ADDR}/MySQL-`echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'`/${DB_filename}.tar.xz + else + DB_URL=${DOWN_ADDR}/MySQL-`echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'`/${DB_filename}.tar.gz + fi + fi + [ ! -e "`ls ${DB_filename}.tar.?z 2>/dev/null`" ] && wget --no-check-certificate -c ${DB_URL} > /dev/null 2>&1 + if [ -e "`ls ${DB_filename}.tar.?z 2>/dev/null`" ]; then + echo "Download [${CMSG}`ls ${DB_filename}.tar.?z 2>/dev/null`${CEND}] successfully! " + else + echo "${CWARNING}${DB} version does not exist! ${CEND}" + fi + break + else + echo "${CWARNING}input error! ${CEND}Please only input '${CMSG}${OLD_db_ver%.*}.xx${CEND}'" + [ "${db_flag}" == 'y' ] && exit + fi + done + + if [ -e "`ls ${DB_filename}.tar.?z 2>/dev/null`" ]; then + echo "[${CMSG}`ls ${DB_filename}.tar.?z 2>/dev/null`${CEND}] found" + if [ "${db_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + if [ "${DB}" == 'MariaDB' ]; then + tar xzf ${DB_filename}.tar.gz + service mysqld stop + mv ${mariadb_install_dir}{,_old_`date +"%Y%m%d_%H%M%S"`} + mv ${mariadb_data_dir}{,_old_`date +"%Y%m%d_%H%M%S"`} + [ ! -d "${mariadb_install_dir}" ] && mkdir -p ${mariadb_install_dir} + mkdir -p ${mariadb_data_dir};chown mysql:mysql -R ${mariadb_data_dir} + mv ${DB_filename}/* ${mariadb_install_dir}/ + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mariadb_install_dir}/bin/mysqld_safe + ${mariadb_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${mariadb_install_dir} --datadir=${mariadb_data_dir} + chown mysql:mysql -R ${mariadb_data_dir} + service mysqld start + ${mariadb_install_dir}/bin/mysql < DB_all_backup_$(date +"%Y%m%d").sql + service mysqld restart + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" >/dev/null 2>&1 + ${mariadb_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" >/dev/null 2>&1 + ${mariadb_install_dir}/bin/mysql_upgrade -uroot -p${dbrootpwd} >/dev/null 2>&1 + [ $? -eq 0 ] && echo "You have ${CMSG}successfully${CEND} upgrade from ${CMSG}${OLD_db_ver}${CEND} to ${CMSG}${NEW_db_ver}${CEND}" + elif [ "${DB}" == 'Percona' ]; then + tar xzf ${DB_filename}.tar.gz + service mysqld stop + mv ${percona_install_dir}{,_old_`date +"%Y%m%d_%H%M%S"`} + mv ${percona_data_dir}{,_old_`date +"%Y%m%d_%H%M%S"`} + [ ! -d "${percona_install_dir}" ] && mkdir -p ${percona_install_dir} + mkdir -p ${percona_data_dir};chown mysql:mysql -R ${percona_data_dir} + mv ${DB_filename}/* ${percona_install_dir}/ + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${percona_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/${DB_filename}@${percona_install_dir}@g" ${percona_install_dir}/bin/mysqld_safe + if [[ "`echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'`" =~ ^5.[5-6]$ ]]; then + ${percona_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${percona_install_dir} --datadir=${percona_data_dir} + else + ${percona_install_dir}/bin/mysqld --initialize-insecure --user=mysql --basedir=${percona_install_dir} --datadir=${percona_data_dir} + fi + chown mysql:mysql -R ${percona_data_dir} + service mysqld start + ${percona_install_dir}/bin/mysql < DB_all_backup_$(date +"%Y%m%d").sql + service mysqld restart + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" >/dev/null 2>&1 + ${percona_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" >/dev/null 2>&1 + ${percona_install_dir}/bin/mysql_upgrade -uroot -p${dbrootpwd} >/dev/null 2>&1 + [ $? -eq 0 ] && echo "You have ${CMSG}successfully${CEND} upgrade from ${CMSG}${OLD_db_ver}${CEND} to ${CMSG}${NEW_db_ver}${CEND}" + elif [ "${DB}" == 'MySQL' ]; then + if [ `echo ${OLD_db_ver} | awk -F. '{print $1"."$2}'` == '8.0' ]; then + tar xJf ${DB_filename}.tar.xz + else + tar xzf ${DB_filename}.tar.gz + fi + service mysqld stop + mv ${mysql_install_dir}{,_old_`date +"%Y%m%d_%H%M%S"`} + mv ${mysql_data_dir}{,_old_`date +"%Y%m%d_%H%M%S"`} + [ ! -d "${mysql_install_dir}" ] && mkdir -p ${mysql_install_dir} + mkdir -p ${mysql_data_dir};chown mysql:mysql -R ${mysql_data_dir} + mv ${DB_filename}/* ${mysql_install_dir}/ + sed -i 's@executing mysqld_safe@executing mysqld_safe\nexport LD_PRELOAD=/usr/local/lib/libjemalloc.so@' ${mysql_install_dir}/bin/mysqld_safe + sed -i "s@/usr/local/mysql@${mysql_install_dir}@g" ${mysql_install_dir}/bin/mysqld_safe + if [[ "`echo ${NEW_db_ver} | awk -F. '{print $1"."$2}'`" =~ ^5.[5-6]$ ]]; then + ${mysql_install_dir}/scripts/mysql_install_db --user=mysql --basedir=${mysql_install_dir} --datadir=${mysql_data_dir} + else + ${mysql_install_dir}/bin/mysqld --initialize-insecure --user=mysql --basedir=${mysql_install_dir} --datadir=${mysql_data_dir} + fi + + chown mysql:mysql -R ${mysql_data_dir} + [ -e "${mysql_install_dir}/my.cnf" ] && rm -rf ${mysql_install_dir}/my.cnf + sed -i '/myisam_repair_threads/d' /etc/my.cnf + service mysqld start + ${mysql_install_dir}/bin/mysql < DB_all_backup_$(date +"%Y%m%d").sql + service mysqld restart + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "drop database test;" >/dev/null 2>&1 + ${mysql_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "reset master;" >/dev/null 2>&1 + ${mysql_install_dir}/bin/mysql_upgrade -uroot -p${dbrootpwd} >/dev/null 2>&1 + [ $? -eq 0 ] && echo "You have ${CMSG}successfully${CEND} upgrade from ${CMSG}${OLD_db_ver}${CEND} to ${CMSG}${NEW_db_ver}${CEND}" + fi + fi +} diff --git a/include/upgrade_memcached.sh b/include/upgrade_memcached.sh new file mode 100644 index 0000000..4bb48ff --- /dev/null +++ b/include/upgrade_memcached.sh @@ -0,0 +1,61 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Upgrade_Memcached() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${memcached_install_dir}/bin/memcached" ] && echo "${CWARNING}Memcached is not installed on your system! ${CEND}" && exit 1 + OLD_memcached_ver=`${memcached_install_dir}/bin/memcached -V | awk '{print $2}'` + Latest_memcached_ver=`curl --connect-timeout 2 -m 3 -s https://github.com/memcached/memcached/wiki/ReleaseNotes | grep 'internal present.*ReleaseNotes' | grep -oE "[0-9]\.[0-9]\.[0-9]+" | head -1` + Latest_memcached_ver=${Latest_memcached_ver:-1.5.12} + echo "Current Memcached Version: ${CMSG}${OLD_memcached_ver}${CEND}" + while :; do echo + [ "${memcached_flag}" != 'y' ] && read -e -p "Please input upgrade Memcached Version(default: ${Latest_memcached_ver}): " NEW_memcached_ver + NEW_memcached_ver=${NEW_memcached_ver:-${Latest_memcached_ver}} + if [ "${NEW_memcached_ver}" != "${OLD_memcached_ver}" ]; then + [ "${OUTIP_STATE}"x == "China"x ] && DOWN_ADDR=${mirror_link}/oneinstack/src || DOWN_ADDR=http://www.memcached.org/files + [ ! -e "memcached-${NEW_memcached_ver}.tar.gz" ] && wget --no-check-certificate -c ${DOWN_ADDR}/memcached-${NEW_memcached_ver}.tar.gz > /dev/null 2>&1 + if [ -e "memcached-${NEW_memcached_ver}.tar.gz" ]; then + echo "Download [${CMSG}memcached-${NEW_memcached_ver}.tar.gz${CEND}] successfully! " + break + else + echo "${CWARNING}Memcached version does not exist! ${CEND}" + fi + else + echo "${CWARNING}input error! Upgrade Memcached version is the same as the old version${CEND}" + exit + fi + done + + if [ -e "memcached-${NEW_memcached_ver}.tar.gz" ]; then + echo "[${CMSG}memcached-${NEW_memcached_ver}.tar.gz${CEND}] found" + if [ "${memcached_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + tar xzf memcached-${NEW_memcached_ver}.tar.gz + pushd memcached-${NEW_memcached_ver} + make clean + ./configure --prefix=${memcached_install_dir} + make -j ${THREAD} + + if [ -e "memcached" ]; then + echo "Restarting Memcached..." + service memcached stop + make install + service memcached start + popd > /dev/null + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}${OLD_memcached_ver}${CEND} to ${CWARNING}${NEW_memcached_ver}${CEND}" + rm -rf memcached-${NEW_memcached_ver} + else + echo "${CFAILURE}Upgrade Memcached failed! ${CEND}" + fi + fi + popd > /dev/null +} diff --git a/include/upgrade_oneinstack.sh b/include/upgrade_oneinstack.sh new file mode 100644 index 0000000..45d7aad --- /dev/null +++ b/include/upgrade_oneinstack.sh @@ -0,0 +1,67 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Upgrade_OneinStack() { + pushd ${oneinstack_dir} > /dev/null + Latest_OneinStack_MD5=$(curl --connect-timeout 3 -m 5 -s ${mirror_link}/md5sum.txt | grep oneinstack.tar.gz | awk '{print $1}') + [ ! -e README.md ] && ois_flag=n + if [ "${oneinstack_md5}" != "${Latest_OneinStack_MD5}" ]; then + /bin/mv options.conf /tmp + sed -i '/oneinstack_dir=/d' /tmp/options.conf + [ -e /tmp/oneinstack.tar.gz ] && rm -rf /tmp/oneinstack.tar.gz + wget --no-check-certificate -qc ${mirror_link}/oneinstack.tar.gz -O /tmp/oneinstack.tar.gz + if [ -n "`echo ${oneinstack_dir} | grep lnmp`" ]; then + tar xzf /tmp/oneinstack.tar.gz -C /tmp + /bin/cp -R /tmp/oneinstack/* ${oneinstack_dir}/ + /bin/rm -rf /tmp/oneinstack + else + tar xzf /tmp/oneinstack.tar.gz -C ../ + fi + IFS=$'\n' + for L in `grep -vE '^#|^$' /tmp/options.conf` + do + IFS=$IFS_old + Key="`echo ${L%%=*}`" + Value="`echo ${L#*=}`" + sed -i "s|^${Key}=.*|${Key}=${Value}|" ./options.conf + done + rm -rf /tmp/{oneinstack.tar.gz,options.conf} + [ "${ois_flag}" == "n" ] && rm -f ss.sh LICENSE README.md + sed -i "s@^oneinstack_md5=.*@oneinstack_md5=${Latest_OneinStack_MD5}@" ./options.conf + if [ -e "change_jdk_version.sh" ]; then + rm -f change_jdk_version.sh + wget -qc ${mirror_link}/scripts/change_jdk_version.sh + chmod +x change_jdk_version.sh + fi + if [ -e "${php_install_dir}/sbin/php-fpm" ]; then + [ -n "`grep ^cgi.fix_pathinfo=0 ${php_install_dir}/etc/php.ini`" ] && sed -i 's@^cgi.fix_pathinfo.*@;&@' ${php_install_dir}/etc/php.ini + [ -e "/usr/local/php53/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php53/etc/php.ini 2>/dev/null + [ -e "/usr/local/php54/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php54/etc/php.ini 2>/dev/null + [ -e "/usr/local/php55/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php55/etc/php.ini 2>/dev/null + [ -e "/usr/local/php56/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php56/etc/php.ini 2>/dev/null + [ -e "/usr/local/php70/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php70/etc/php.ini 2>/dev/null + [ -e "/usr/local/php71/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php71/etc/php.ini 2>/dev/null + [ -e "/usr/local/php72/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php72/etc/php.ini 2>/dev/null + [ -e "/usr/local/php73/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php73/etc/php.ini 2>/dev/null + [ -e "/usr/local/php74/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php74/etc/php.ini 2>/dev/null + [ -e "/usr/local/php80/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php80/etc/php.ini 2>/dev/null + [ -e "/usr/local/php81/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php81/etc/php.ini 2>/dev/null + [ -e "/usr/local/php82/etc/php.ini" ] && sed -i 's@^cgi.fix_pathinfo=0@;&@' /usr/local/php82/etc/php.ini 2>/dev/null + fi + [ -e "/lib/systemd/system/php-fpm.service" ] && { sed -i 's@^PrivateTmp.*@#&@g' /lib/systemd/system/php-fpm.service; systemctl daemon-reload; } + echo + echo "${CSUCCESS}Congratulations! OneinStack upgrade successful! ${CEND}" + echo + else + echo "${CWARNING}Your OneinStack already has the latest version or does not need to be upgraded! ${CEND}" + fi + [ ! -e "${oneinstack_dir}/options.conf" ] && [ -e "/tmp/options.conf" ] && /bin/cp /tmp/options.conf ${oneinstack_dir}/options.conf + popd > /dev/null +} diff --git a/include/upgrade_php.sh b/include/upgrade_php.sh new file mode 100644 index 0000000..7c14b9d --- /dev/null +++ b/include/upgrade_php.sh @@ -0,0 +1,74 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Upgrade_PHP() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${php_install_dir}" ] && echo "${CWARNING}PHP is not installed on your system! ${CEND}" && exit 1 + OLD_php_ver=`${php_install_dir}/bin/php-config --version` + pythonCtl=python + command -v python3 > /dev/null 2>&1 && pythonCtl=python3 + Latest_php_ver=`curl --connect-timeout 2 -m 3 -s https://www.php.net/releases/active.php | ${pythonCtl} -mjson.tool | awk '/version/{print $2}' | sed 's/"//g' | grep "${OLD_php_ver%.*}"` + Latest_php_ver=${Latest_php_ver:-5.5.38} + echo + echo "Current PHP Version: ${CMSG}$OLD_php_ver${CEND}" + while :; do echo + [ "${php_flag}" != 'y' ] && read -e -p "Please input upgrade PHP Version(Default: $Latest_php_ver): " NEW_php_ver + NEW_php_ver=${NEW_php_ver:-${Latest_php_ver}} + if [ "${NEW_php_ver%.*}" == "${OLD_php_ver%.*}" ]; then + [ ! -e "php-${NEW_php_ver}.tar.gz" ] && wget --no-check-certificate -c https://secure.php.net/distributions/php-${NEW_php_ver}.tar.gz > /dev/null 2>&1 + if [ -e "php-${NEW_php_ver}.tar.gz" ]; then + echo "Download [${CMSG}php-${NEW_php_ver}.tar.gz${CEND}] successfully! " + else + echo "${CWARNING}PHP version does not exist! ${CEND}" + fi + break + else + echo "${CWARNING}input error! ${CEND}Please only input '${CMSG}${OLD_php_ver%.*}.xx${CEND}'" + [ "${php_flag}" == 'y' ] && exit + fi + done + + if [ -e "php-${NEW_php_ver}.tar.gz" ]; then + echo "[${CMSG}php-${NEW_php_ver}.tar.gz${CEND}] found" + if [ "${php_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + tar xzf php-${NEW_php_ver}.tar.gz + src_url=${mirror_link}/oneinstack/src/fpm-race-condition.patch && Download_src + patch -d php-${NEW_php_ver} -p0 < fpm-race-condition.patch + pushd php-${NEW_php_ver} + if [[ "${OLD_php_ver%.*}" =~ ^7.[1-4]$|^8.[0-1]$ ]] && [ -e ext/openssl/openssl.c ] && ! grep -Eqi '^#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c; then + sed -i '/OPENSSL_SSLV23_PADDING/i#ifdef RSA_SSLV23_PADDING' ext/openssl/openssl.c + sed -i '/OPENSSL_SSLV23_PADDING/a#endif' ext/openssl/openssl.c + fi + make clean + export PKG_CONFIG_PATH=/usr/local/lib/pkgconfig/:$PKG_CONFIG_PATH + ${php_install_dir}/bin/php -i |grep 'Configure Command' | awk -F'=>' '{print $2}' | bash + make ZEND_EXTRA_LIBS='-liconv' -j ${THREAD} + if [ -e "${apache_install_dir}/bin/httpd" ]; then + echo "Stoping apache..." + service httpd stop + make install + echo "Starting apache..." + service httpd start + else + echo "Stoping php-fpm..." + service php-fpm stop + make install + echo "Starting php-fpm..." + service php-fpm start + fi + popd > /dev/null + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}$OLD_php_ver${CEND} to ${CWARNING}${NEW_php_ver}${CEND}" + rm -rf php-${NEW_php_ver} + fi + popd > /dev/null +} diff --git a/include/upgrade_phpmyadmin.sh b/include/upgrade_phpmyadmin.sh new file mode 100644 index 0000000..7461dbe --- /dev/null +++ b/include/upgrade_phpmyadmin.sh @@ -0,0 +1,54 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Upgrade_phpMyAdmin() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${wwwroot_dir}/default/phpMyAdmin" ] && echo "${CWARNING}phpMyAdmin is not installed on your system! ${CEND}" && exit 1 + OLD_phpmyadmin_ver=`grep Version ${wwwroot_dir}/default/phpMyAdmin/README | awk '{print $2}'` + Latest_phpmyadmin_ver=`curl --connect-timeout 2 -m 3 -s https://www.phpmyadmin.net/files/ | awk -F'>|<' '/\/files\/[0-9]/{print $5}' | head -1` + Latest_phpmyadmin_ver=${Latest_phpmyadmin_ver:-5.0.4} + echo "Current phpMyAdmin Version: ${CMSG}${OLD_phpmyadmin_ver}${CEND}" + while :; do echo + [ "${phpmyadmin_flag}" != 'y' ] && read -e -p "Please input upgrade phpMyAdmin Version(default: ${Latest_phpmyadmin_ver}): " NEW_phpmyadmin_ver + NEW_phpmyadmin_ver=${NEW_phpmyadmin_ver:-${Latest_phpmyadmin_ver}} + if [ "${NEW_phpmyadmin_ver}" != "${OLD_phpmyadmin_ver}" ]; then + [ ! -e "phpMyAdmin-${NEW_phpmyadmin_ver}-all-languages.tar.gz" ] && wget --no-check-certificate -c https://files.phpmyadmin.net/phpMyAdmin/${NEW_phpmyadmin_ver}/phpMyAdmin-${NEW_phpmyadmin_ver}-all-languages.tar.gz > /dev/null 2>&1 + if [ -e "phpMyAdmin-${NEW_phpmyadmin_ver}-all-languages.tar.gz" ]; then + echo "Download [${CMSG}phpMyAdmin-${NEW_phpmyadmin_ver}-all-languages.tar.gz${CEND}] successfully! " + break + else + echo "${CWARNING}phpMyAdmin version does not exist! ${CEND}" + fi + else + echo "${CWARNING}input error! Upgrade phpMyAdmin version is the same as the old version${CEND}" + exit + fi + done + + if [ -e "phpMyAdmin-${NEW_phpmyadmin_ver}-all-languages.tar.gz" ]; then + echo "[${CMSG}phpMyAdmin-${NEW_phpmyadmin_ver}-all-languages.tar.gz${CEND}] found" + if [ "${phpmyadmin_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + tar xzf phpMyAdmin-${NEW_phpmyadmin_ver}-all-languages.tar.gz + rm -rf ${wwwroot_dir}/default/phpMyAdmin + /bin/mv phpMyAdmin-${NEW_phpmyadmin_ver}-all-languages ${wwwroot_dir}/default/phpMyAdmin + /bin/cp ${wwwroot_dir}/default/phpMyAdmin/{config.sample.inc.php,config.inc.php} + mkdir ${wwwroot_dir}/default/phpMyAdmin/{upload,save} + sed -i "s@UploadDir.*@UploadDir'\] = 'upload';@" ${wwwroot_dir}/default/phpMyAdmin/config.inc.php + sed -i "s@SaveDir.*@SaveDir'\] = 'save';@" ${wwwroot_dir}/default/phpMyAdmin/config.inc.php + sed -i "s@host'\].*@host'\] = '127.0.0.1';@" ${wwwroot_dir}/default/phpMyAdmin/config.inc.php + sed -i "s@blowfish_secret.*;@blowfish_secret\'\] = \'$(cat /dev/urandom | head -1 | base64 | head -c 45)\';@" ${wwwroot_dir}/default/phpMyAdmin/config.inc.php + chown -R ${run_user}:${run_group} ${wwwroot_dir}/default/phpMyAdmin + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}$OLD_phpmyadmin_ver${CEND} to ${CWARNING}$NEW_phpmyadmin_ver${CEND}" + fi + popd > /dev/null +} diff --git a/include/upgrade_redis.sh b/include/upgrade_redis.sh new file mode 100644 index 0000000..333afa0 --- /dev/null +++ b/include/upgrade_redis.sh @@ -0,0 +1,59 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Upgrade_Redis() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -d "$redis_install_dir" ] && echo "${CWARNING}Redis is not installed on your system! ${CEND}" && exit 1 + OLD_redis_ver=`$redis_install_dir/bin/redis-cli --version | awk '{print $2}'` + Latest_redis_ver=`curl --connect-timeout 2 -m 3 -s http://download.redis.io/redis-stable/00-RELEASENOTES | awk '/Released/{print $2}' | head -1` + Latest_redis_ver=${Latest_redis_ver:-6.0.4} + echo "Current Redis Version: ${CMSG}$OLD_redis_ver${CEND}" + while :; do echo + [ "${redis_flag}" != 'y' ] && read -e -p "Please input upgrade Redis Version(default: ${Latest_redis_ver}): " NEW_redis_ver + NEW_redis_ver=${NEW_redis_ver:-${Latest_redis_ver}} + if [ "$NEW_redis_ver" != "$OLD_redis_ver" ]; then + [ ! -e "redis-$NEW_redis_ver.tar.gz" ] && wget --no-check-certificate -c http://download.redis.io/releases/redis-$NEW_redis_ver.tar.gz > /dev/null 2>&1 + if [ -e "redis-$NEW_redis_ver.tar.gz" ]; then + echo "Download [${CMSG}redis-$NEW_redis_ver.tar.gz${CEND}] successfully! " + break + else + echo "${CWARNING}Redis version does not exist! ${CEND}" + fi + else + echo "${CWARNING}input error! Upgrade Redis version is the same as the old version${CEND}" + exit + fi + done + + if [ -e "redis-$NEW_redis_ver.tar.gz" ]; then + echo "[${CMSG}redis-$NEW_redis_ver.tar.gz${CEND}] found" + if [ "${redis_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + tar xzf redis-$NEW_redis_ver.tar.gz + pushd redis-$NEW_redis_ver + make clean + make -j ${THREAD} + + if [ -f "src/redis-server" ]; then + echo "Restarting Redis..." + service redis-server stop + /bin/cp src/{redis-benchmark,redis-check-aof,redis-check-rdb,redis-cli,redis-sentinel,redis-server} $redis_install_dir/bin/ + service redis-server start + popd > /dev/null + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}$OLD_redis_ver${CEND} to ${CWARNING}$NEW_redis_ver${CEND}" + rm -rf redis-$NEW_redis_ver + else + echo "${CFAILURE}Upgrade Redis failed! ${CEND}" + fi + fi + popd > /dev/null +} diff --git a/include/upgrade_web.sh b/include/upgrade_web.sh new file mode 100644 index 0000000..5ec1f65 --- /dev/null +++ b/include/upgrade_web.sh @@ -0,0 +1,360 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Upgrade_Nginx() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${nginx_install_dir}/sbin/nginx" ] && echo "${CWARNING}Nginx is not installed on your system! ${CEND}" && exit 1 + OLD_nginx_ver_tmp=`${nginx_install_dir}/sbin/nginx -v 2>&1` + OLD_nginx_ver=${OLD_nginx_ver_tmp##*/} + Latest_nginx_ver=`curl --connect-timeout 2 -m 3 -s http://nginx.org/en/CHANGES-1.22 | awk '/Changes with nginx/{print$0}' | awk '{print $4}' | head -1` + [ -z "${Latest_nginx_ver}" ] && Latest_nginx_ver=`curl --connect-timeout 2 -m 3 -s http://nginx.org/en/CHANGES | awk '/Changes with nginx/{print$0}' | awk '{print $4}' | head -1` + echo + echo "Current Nginx Version: ${CMSG}${OLD_nginx_ver}${CEND}" + while :; do echo + [ "${nginx_flag}" != 'y' ] && read -e -p "Please input upgrade Nginx Version(default: ${Latest_nginx_ver}): " NEW_nginx_ver + NEW_nginx_ver=${NEW_nginx_ver:-${Latest_nginx_ver}} + if [ "${NEW_nginx_ver}" != "${OLD_nginx_ver}" ]; then + [ ! -e "nginx-${NEW_nginx_ver}.tar.gz" ] && wget --no-check-certificate -c http://nginx.org/download/nginx-${NEW_nginx_ver}.tar.gz > /dev/null 2>&1 + if [ -e "nginx-${NEW_nginx_ver}.tar.gz" ]; then + src_url=https://www.openssl.org/source/openssl-${openssl11_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/pcre-${pcre_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/ngx_devel_kit.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/lua-nginx-module-${lua_nginx_module_ver}.tar.gz && Download_src + tar xzf openssl-${openssl11_ver}.tar.gz + tar xzf pcre-${pcre_ver}.tar.gz + tar xzf ngx_devel_kit.tar.gz + tar xzf lua-nginx-module-${lua_nginx_module_ver}.tar.gz + echo "Download [${CMSG}nginx-${NEW_nginx_ver}.tar.gz${CEND}] successfully! " + break + else + echo "${CWARNING}Nginx version does not exist! ${CEND}" + fi + else + echo "${CWARNING}input error! Upgrade Nginx version is the same as the old version${CEND}" + exit + fi + done + + if [ -e "nginx-${NEW_nginx_ver}.tar.gz" ]; then + echo "[${CMSG}nginx-${NEW_nginx_ver}.tar.gz${CEND}] found" + if [ "${nginx_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + ${nginx_install_dir}/sbin/nginx -V &> $$ + nginx_configure_args_tmp=`cat $$ | grep 'configure arguments:' | awk -F: '{print $2}'` + rm -rf $$ + nginx_configure_args=`echo ${nginx_configure_args_tmp} | sed "s@lua-nginx-module-\w.\w\+.\w\+ @lua-nginx-module-${lua_nginx_module_ver} @" | sed "s@lua-nginx-module @lua-nginx-module-${lua_nginx_module_ver} @" | sed "s@--with-openssl=../openssl-\w.\w.\w\+ @--with-openssl=../openssl-${openssl11_ver} @" | sed "s@--with-pcre=../pcre-\w.\w\+ @--with-pcre=../pcre-${pcre_ver} @"` + if [ -n "`echo $nginx_configure_args | grep lua-nginx-module`" ]; then + ${oneinstack_dir}/upgrade.sh --oneinstack > /dev/null + src_url=${mirror_link}/oneinstack/src/luajit2-${luajit2_ver}.tar.gz && Download_src + tar xzf luajit2-${luajit2_ver}.tar.gz + pushd luajit2-${luajit2_ver} + make && make install + popd > /dev/null + rm -rf luajit2-${luajit2_ver} + + src_url=${mirror_link}/oneinstack/src/lua-resty-core-${lua_resty_core_ver}.tar.gz && Download_src + tar xzf lua-resty-core-${lua_resty_core_ver}.tar.gz + pushd lua-resty-core-${lua_resty_core_ver} + make install + popd > /dev/null + rm -rf lua-resty-core-${lua_resty_core_ver} + + src_url=${mirror_link}/oneinstack/src/lua-resty-lrucache-${lua_resty_lrucache_ver}.tar.gz && Download_src + tar xzf lua-resty-lrucache-${lua_resty_lrucache_ver}.tar.gz + pushd lua-resty-lrucache-${lua_resty_lrucache_ver} + make install + popd > /dev/null + rm -rf lua-resty-lrucache-${lua_resty_lrucache_ver} + fi + + tar xzf nginx-${NEW_nginx_ver}.tar.gz + pushd nginx-${NEW_nginx_ver} + make clean + sed -i 's@CFLAGS="$CFLAGS -g"@#CFLAGS="$CFLAGS -g"@' auto/cc/gcc # close debug + export LUAJIT_LIB=/usr/local/lib + export LUAJIT_INC=/usr/local/include/luajit-2.1 + ./configure ${nginx_configure_args} + make -j ${THREAD} + if [ -f "objs/nginx" ]; then + /bin/mv ${nginx_install_dir}/sbin/nginx{,`date +%m%d`} + /bin/cp objs/nginx ${nginx_install_dir}/sbin/nginx + kill -USR2 `cat /var/run/nginx.pid` + sleep 1 + kill -QUIT `cat /var/run/nginx.pid.oldbin` + popd > /dev/null + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}${OLD_nginx_ver}${CEND} to ${CWARNING}${NEW_nginx_ver}${CEND}" + rm -rf nginx-${NEW_nginx_ver} + else + echo "${CFAILURE}Upgrade Nginx failed! ${CEND}" + fi + fi + popd > /dev/null +} + +Upgrade_Tengine() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${tengine_install_dir}/sbin/nginx" ] && echo "${CWARNING}Tengine is not installed on your system! ${CEND}" && exit 1 + OLD_tengine_ver_tmp=`${tengine_install_dir}/sbin/nginx -v 2>&1` + OLD_tengine_ver="`echo ${OLD_tengine_ver_tmp#*/} | awk '{print $1}'`" + Latest_tengine_ver=`curl --connect-timeout 2 -m 3 -s http://tengine.taobao.org/changelog.html | grep -v generator | grep -oE "[0-9]\.[0-9]\.[0-9]+" | head -1` + echo + echo "Current Tengine Version: ${CMSG}${OLD_tengine_ver}${CEND}" + while :; do echo + [ "${tengine_flag}" != 'y' ] && read -e -p "Please input upgrade Tengine Version(default: ${Latest_tengine_ver}): " NEW_tengine_ver + NEW_tengine_ver=${NEW_tengine_ver:-${Latest_tengine_ver}} + if [ "${NEW_tengine_ver}" != "${OLD_tengine_ver}" ]; then + [ ! -e "tengine-${NEW_tengine_ver}.tar.gz" ] && wget --no-check-certificate -c http://tengine.taobao.org/download/tengine-${NEW_tengine_ver}.tar.gz > /dev/null 2>&1 + if [ -e "tengine-${NEW_tengine_ver}.tar.gz" ]; then + src_url=https://www.openssl.org/source/openssl-${openssl11_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/pcre-${pcre_ver}.tar.gz && Download_src + tar xzf openssl-${openssl11_ver}.tar.gz + tar xzf pcre-${pcre_ver}.tar.gz + echo "Download [${CMSG}tengine-${NEW_tengine_ver}.tar.gz${CEND}] successfully! " + break + else + echo "${CWARNING}Tengine version does not exist! ${CEND}" + fi + else + echo "${CWARNING}input error! Upgrade Tengine version is the same as the old version${CEND}" + exit + fi + done + + if [ -e "tengine-${NEW_tengine_ver}.tar.gz" ]; then + echo "[${CMSG}tengine-${NEW_tengine_ver}.tar.gz${CEND}] found" + if [ "${tengine_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + tar xzf tengine-${NEW_tengine_ver}.tar.gz + pushd tengine-${NEW_tengine_ver} + make clean + ${tengine_install_dir}/sbin/nginx -V &> $$ + tengine_configure_args_tmp=`cat $$ | grep 'configure arguments:' | awk -F: '{print $2}'` + rm -rf $$ + tengine_configure_args=`echo ${tengine_configure_args_tmp} | sed "s@--with-openssl=../openssl-\w.\w.\w\+ @--with-openssl=../openssl-${openssl11_ver} @" | sed "s@--with-pcre=../pcre-\w.\w\+ @--with-pcre=../pcre-${pcre_ver} @"` + export LUAJIT_LIB=/usr/local/lib + export LUAJIT_INC=/usr/local/include/luajit-2.1 + ./configure ${tengine_configure_args} + make + if [ -f "objs/nginx" ]; then + /bin/mv ${tengine_install_dir}/sbin/nginx{,`date +%m%d`} + /bin/mv ${tengine_install_dir}/modules{,`date +%m%d`} + /bin/cp objs/nginx ${tengine_install_dir}/sbin/nginx + chmod +x ${tengine_install_dir}/sbin/* + make install + kill -USR2 `cat /var/run/nginx.pid` + sleep 1 + kill -QUIT `cat /var/run/nginx.pid.oldbin` + popd > /dev/null + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}$OLD_tengine_ver${CEND} to ${CWARNING}${NEW_tengine_ver}${CEND}" + rm -rf tengine-${NEW_tengine_ver} + else + echo "${CFAILURE}Upgrade Tengine failed! ${CEND}" + fi + fi + popd > /dev/null +} + +Upgrade_OpenResty() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${openresty_install_dir}/nginx/sbin/nginx" ] && echo "${CWARNING}OpenResty is not installed on your system! ${CEND}" && exit 1 + OLD_openresy_ver_tmp=`${openresty_install_dir}/nginx/sbin/nginx -v 2>&1` + OLD_openresy_ver="`echo ${OLD_openresy_ver_tmp#*/} | awk '{print $1}'`" + Latest_openresy_ver=`curl --connect-timeout 2 -m 3 -s https://openresty.org/en/download.html | awk '/download\/openresty-/{print $0}' | grep -oE "[0-9]+\.[0-9]+\.[0-9]+\.[0-9]+" | head -1` + echo + echo "Current OpenResty Version: ${CMSG}${OLD_openresy_ver}${CEND}" + while :; do echo + [ "${openresty_flag}" != 'y' ] && read -e -p "Please input upgrade OpenResty Version(default: ${Latest_openresy_ver}): " NEW_openresy_ver + NEW_openresy_ver=${NEW_openresy_ver:-${Latest_openresy_ver}} + if [ "${NEW_openresy_ver}" != "${OLD_openresy_ver}" ]; then + [ ! -e "openresty-${NEW_openresy_ver}.tar.gz" ] && wget --no-check-certificate -c https://openresty.org/download/openresty-${NEW_openresy_ver}.tar.gz > /dev/null 2>&1 + if [ -e "openresty-${NEW_openresy_ver}.tar.gz" ]; then + src_url=https://www.openssl.org/source/openssl-${openssl11_ver}.tar.gz && Download_src + src_url=${mirror_link}/oneinstack/src/pcre-${pcre_ver}.tar.gz && Download_src + tar xzf openssl-${openssl11_ver}.tar.gz + tar xzf pcre-${pcre_ver}.tar.gz + echo "Download [${CMSG}openresty-${NEW_openresy_ver}.tar.gz${CEND}] successfully! " + break + else + echo "${CWARNING}OpenResty version does not exist! ${CEND}" + fi + else + echo "${CWARNING}input error! Upgrade OpenResty version is the same as the old version${CEND}" + exit + fi + done + + if [ -e "openresty-${NEW_openresy_ver}.tar.gz" ]; then + echo "[${CMSG}openresty-${NEW_openresy_ver}.tar.gz${CEND}] found" + if [ "${openresty_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + tar xzf openresty-${NEW_openresy_ver}.tar.gz + pushd openresty-${NEW_openresy_ver} + make clean + sed -i 's@CFLAGS="$CFLAGS -g"@#CFLAGS="$CFLAGS -g"@' bundle/nginx-${NEW_openresy_ver%.*}/auto/cc/gcc # close debug + ${openresty_install_dir}/nginx/sbin/nginx -V &> $$ + ./configure --prefix=${openresty_install_dir} --user=${run_user} --group=${run_user} --with-http_stub_status_module --with-http_sub_module --with-http_v2_module --with-http_ssl_module --with-http_gzip_static_module --with-http_realip_module --with-http_flv_module --with-http_mp4_module --with-openssl=../openssl-${openssl11_ver} --with-pcre=../pcre-${pcre_ver} --with-pcre-jit --with-ld-opt='-ljemalloc -Wl,-u,pcre_version' ${nginx_modules_options} + make -j ${THREAD} + if [ -f "build/nginx-${NEW_openresy_ver%.*}/objs/nginx" ]; then + /bin/mv ${openresty_install_dir}/nginx/sbin/nginx{,`date +%m%d`} + make install + kill -USR2 `cat /var/run/nginx.pid` + sleep 1 + kill -QUIT `cat /var/run/nginx.pid.oldbin` + popd > /dev/null + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}${OLD_openresy_ver}${CEND} to ${CWARNING}${NEW_openresy_ver}${CEND}" + rm -rf openresty-${NEW_openresy_ver} + else + echo "${CFAILURE}Upgrade OpenResty failed! ${CEND}" + fi + fi + popd > /dev/null +} + +Upgrade_Apache() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${apache_install_dir}/bin/httpd" ] && echo "${CWARNING}Apache is not installed on your system! ${CEND}" && exit 1 + OLD_apache_ver="`${apache_install_dir}/bin/httpd -v | grep version | awk -F'/| ' '{print $4}'`" + Latest_apache_ver=`curl --connect-timeout 2 -m 3 -s http://httpd.apache.org/download.cgi | awk "/#apache24/{print $2}" | head -1 | grep -oE "2\.[24]\.[0-9]+"` + Latest_apache_ver=${Latest_apache_ver:-${apache22_ver}} + echo + echo "Current Apache Version: ${CMSG}${OLD_apache_ver}${CEND}" + while :; do echo + [ "${apache_flag}" != 'y' ] && read -e -p "Please input upgrade Apache Version(Default: ${Latest_apache_ver}): " NEW_apache_ver + NEW_apache_ver=${NEW_apache_ver:-${Latest_apache_ver}} + if [ `echo ${NEW_apache_ver} | awk -F. '{print $1$2}'` == "24" ]; then + if [ "${NEW_apache_ver}" != "${OLD_apache_ver}" ]; then + src_url=http://archive.apache.org/dist/apr/apr-${apr_ver}.tar.gz && Download_src + src_url=http://archive.apache.org/dist/apr/apr-util-${apr_util_ver}.tar.gz && Download_src + [ ! -e "httpd-${NEW_apache_ver}.tar.gz" ] && wget --no-check-certificate -c http://archive.apache.org/dist/httpd/httpd-${NEW_apache_ver}.tar.gz > /dev/null 2>&1 + if [ -e "httpd-${NEW_apache_ver}.tar.gz" ]; then + echo "Download [${CMSG}apache-${NEW_apache_ver}.tar.gz${CEND}] successfully! " + break + else + echo "${CWARNING}Apache version does not exist! ${CEND}" + fi + else + echo "${CWARNING}input error! Upgrade Apache version is the same as the old version${CEND}" + exit + fi + else + echo "${CWARNING}input error! ${CEND}Please only input '${CMSG}${OLD_apache_ver%.*}.xx${CEND}'" + [ "${apache_flag}" == 'y' ] && exit + fi + done + + if [ -e "httpd-${NEW_apache_ver}.tar.gz" ]; then + echo "[${CMSG}httpd-${NEW_apache_ver}.tar.gz${CEND}] found" + if [ "${apache_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + # install apr + if [ ! -e "${apr_install_dir}/bin/apr-1-config" ]; then + tar xzf apr-${apr_ver}.tar.gz + pushd apr-${apr_ver} > /dev/null + ./configure --prefix=${apr_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf apr-${apr_ver} + fi + # install apr-util + if [ ! -e "${apr_install_dir}/bin/apu-1-config" ]; then + tar xzf apr-util-${apr_util_ver}.tar.gz + pushd apr-util-${apr_util_ver} > /dev/null + ./configure --prefix=${apr_install_dir} --with-apr=${apr_install_dir} + make -j ${THREAD} && make install + popd > /dev/null + rm -rf apr-util-${apr_util_ver} + fi + tar xzf httpd-${NEW_apache_ver}.tar.gz + pushd httpd-${NEW_apache_ver} + make clean + LDFLAGS=-ldl ./configure --prefix=${apache_install_dir} --enable-mpms-shared=all --with-pcre --with-apr=${apr_install_dir} --with-apr-util=${apr_install_dir} --enable-headers --enable-mime-magic --enable-deflate --enable-proxy --enable-so --enable-dav --enable-rewrite --enable-remoteip --enable-expires --enable-static-support --enable-suexec --enable-mods-shared=most --enable-nonportable-atomics=yes --enable-ssl --with-ssl=${openssl_install_dir} --enable-http2 --with-nghttp2=/usr/local + make -j ${THREAD} + if [ -e 'httpd' ]; then + [[ -d ${apache_install_dir}_bak && -d ${apache_install_dir} ]] && rm -rf ${apache_install_dir}_bak + service httpd stop + /bin/cp -R ${apache_install_dir}{,_bak} + make install && unset LDFLAGS + service httpd start + popd > /dev/null + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}${OLD_apache_ver}${CEND} to ${CWARNING}${NEW_apache_ver}${CEND}" + rm -rf httpd-${NEW_apache_ver} + else + echo "${CFAILURE}Upgrade Apache failed! ${CEND}" + fi + fi + popd > /dev/null +} + +Upgrade_Tomcat() { + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e "${tomcat_install_dir}/conf/server.xml" ] && echo "${CWARNING}Tomcat is not installed on your system! ${CEND}" && exit 1 + OLD_tomcat_ver="`${tomcat_install_dir}/bin/version.sh | awk '/Server number/{print $3}' | awk -F. '{print $1"."$2"."$3}'`" + Tomcat_flag="`echo ${OLD_tomcat_ver} | awk -F. '{print $1}'`" + Latest_tomcat_ver=`curl --connect-timeout 2 -m 3 -s https://tomcat.apache.org/download-${Tomcat_flag}0.cgi | grep "README" | head -1 | grep -oE "[6-9]\.[0-9]\.[0-9]+"` + Latest_tomcat_ver=${Latest_tomcat_ver:-${tomcat10_ver}} + echo + echo "Current Tomcat Version: ${CMSG}${OLD_tomcat_ver}${CEND}" + while :; do echo + [ "${tomcat_flag}" != 'y' ] && read -e -p "Please input upgrade Tomcat Version(Default: ${Latest_tomcat_ver}): " NEW_tomcat_ver + NEW_tomcat_ver=${NEW_tomcat_ver:-${Latest_tomcat_ver}} + if [ "`echo ${NEW_tomcat_ver} | awk -F. '{print $1}'`" == "${Tomcat_flag}" ]; then + rm -f catalina-jmx-remote.jar + echo "Download tomcat-${NEW_tomcat_ver}..." + src_url=${mirror_link}/apache/tomcat/v${NEW_tomcat_ver}/apache-tomcat-${NEW_tomcat_ver}.tar.gz && Download_src + [ ! -e "apache-tomcat-${NEW_tomcat_ver}.tar.gz" ] && wget --no-check-certificate -c https://archive.apache.org/dist/tomcat-${OLD_tomcat_ver}/v${NEW_tomcat_ver}/bin/apache-tomcat-${NEW_tomcat_ver}.tar.gz > /dev/null 2>&1 + if [ -e "${tomcat_install_dir}/lib/catalina-jmx-remote.jar" ]; then + src_url=${mirror_link}/apache/tomcat/v${NEW_tomcat_ver}/catalina-jmx-remote.jar && Download_src + [ ! -e "catalina-jmx-remote.jar" ] && wget --no-check-certificate -c https://archive.apache.org/dist/tomcat-${OLD_tomcat_ver}/v${NEW_tomcat_ver}/bin/extras/catalina-jmx-remote.jar > /dev/null 2>&1 + fi + if [ -e "apache-tomcat-${NEW_tomcat_ver}.tar.gz" ]; then + echo "Download [${CMSG}apache-tomcat-${NEW_tomcat_ver}.tar.gz${CEND}] successfully! " + break + else + echo "${CWARNING}Tomcat version does not exist! ${CEND}" + fi + else + echo "${CWARNING}input error! ${CEND}Please only input '${CMSG}${Tomcat_flag}.xx${CEND}'" + fi + done + + if [ -e "apache-tomcat-${NEW_tomcat_ver}.tar.gz" ]; then + echo "[${CMSG}apache-tomcat-${NEW_tomcat_ver}.tar.gz${CEND}] found" + if [ "${tomcat_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=`get_char` + fi + tar xzf apache-tomcat-${NEW_tomcat_ver}.tar.gz + /bin/mv apache-tomcat-${NEW_tomcat_ver}/conf/server.xml{,_bk} + /bin/cp ${tomcat_install_dir}/conf/{server.xml,jmxremote.access,jmxremote.password,tomcat-users.xml} apache-tomcat-${NEW_tomcat_ver}/conf/ + [ -e "${tomcat_install_dir}/lib/catalina-jmx-remote.jar" ] && /bin/cp catalina-jmx-remote.jar apache-tomcat-${NEW_tomcat_ver}/lib + /bin/cp ${tomcat_install_dir}/bin/setenv.sh apache-tomcat-${NEW_tomcat_ver}/bin/ + /bin/cp -R ${tomcat_install_dir}/conf/vhost apache-tomcat-${NEW_tomcat_ver}/conf/ + chmod +x apache-tomcat-${NEW_tomcat_ver}/bin/*.sh + [[ -d ${tomcat_install_dir}_bak && -d ${tomcat_install_dir} ]] && rm -rf ${tomcat_install_dir}._bak + service tomcat stop + /bin/mv ${tomcat_install_dir}{,_bak} + /bin/mv apache-tomcat-${NEW_tomcat_ver} ${tomcat_install_dir} && chown -R ${run_user}:${run_group} ${tomcat_install_dir} + if [ -e "${tomcat_install_dir}/conf/server.xml" ]; then + service tomcat start + echo "You have ${CMSG}successfully${CEND} upgrade from ${CWARNING}${OLD_tomcat_ver}${CEND} to ${CWARNING}${NEW_tomcat_ver}${CEND}" + else + echo "${CFAILURE}Upgrade Tomcat failed! ${CEND}" + fi + fi + popd > /dev/null +} diff --git a/include/xcache.sh b/include/xcache.sh new file mode 100644 index 0000000..09e0390 --- /dev/null +++ b/include/xcache.sh @@ -0,0 +1,86 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_XCache() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + if [[ "${PHP_main_ver}" =~ ^5.[3-6]$ ]]; then + tar xzf xcache-${xcache_ver}.tar.gz + pushd xcache-${xcache_ver} > /dev/null + ${php_install_dir}/bin/phpize + ./configure --enable-xcache --enable-xcache-coverager --enable-xcache-optimizer --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + if [ -f "${phpExtensionDir}/xcache.so" ]; then + /bin/cp -R htdocs ${wwwroot_dir}/default/xcache + popd > /dev/null + chown -R ${run_user}:${run_group} ${wwwroot_dir}/default/xcache + touch /tmp/xcache;chown ${run_user}:${run_group} /tmp/xcache + let xcacheCount="${CPU}+1" + let xcacheSize="${Memory_limit}/2" + cat > ${php_install_dir}/etc/php.d/04-xcache.ini << EOF +[xcache-common] +extension=xcache.so +[xcache.admin] +xcache.admin.enable_auth=On +xcache.admin.user=admin +xcache.admin.pass="${xcachepwd_md5}" + +[xcache] +xcache.size=${xcacheSize}M +xcache.count=${xcacheCount} +xcache.slots=8K +xcache.ttl=3600 +xcache.gc_interval=300 +xcache.var_size=4M +xcache.var_count=${xcacheCount} +xcache.var_slots=8K +xcache.var_ttl=0 +xcache.var_maxttl=0 +xcache.var_gc_interval=300 +xcache.test=Off +xcache.readonly_protection=Off +xcache.shm_scheme=mmap +xcache.mmap_path=/tmp/xcache +xcache.coredump_directory= +xcache.cacher=On +xcache.stat=On +xcache.optimizer=Off + +[xcache.coverager] +; enabling this feature will impact performance +; enable only if xcache.coverager == On && xcache.coveragedump_directory == "non-empty-value" +; enable coverage data collecting and xcache_coverager_start/stop/get/clean() functions +xcache.coverager = Off +xcache.coverager_autostart = On +xcache.coveragedump_directory = "" +EOF + echo "${CSUCCESS}PHP xcache module installed successfully! ${CEND}" + rm -rf xcache-${xcache_ver} + else + echo "${CFAILURE}PHP xcache module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + else + echo; echo "${CWARNING}Your php ${PHP_detail_ver} does not support XCache! ${CEND}"; + fi + popd > /dev/null + fi +} + +Uninstall_XCache() { + if [ -e "${php_install_dir}/etc/php.d/04-xcache.ini" ]; then + rm -rf ${php_install_dir}/etc/php.d/04-xcache.ini ${wwwroot_dir}/default/xcache /tmp/xcache + echo; echo "${CMSG}PHP xcache module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP xcache module does not exist! ${CEND}" + fi +} diff --git a/include/zendopcache.sh b/include/zendopcache.sh new file mode 100644 index 0000000..fbb26e6 --- /dev/null +++ b/include/zendopcache.sh @@ -0,0 +1,85 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +Install_ZendOPcache() { + if [ -e "${php_install_dir}/bin/phpize" ]; then + pushd ${oneinstack_dir}/src > /dev/null + phpExtensionDir=$(${php_install_dir}/bin/php-config --extension-dir) + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + if [[ "${PHP_main_ver}" =~ ^5.[3-4]$ ]]; then + tar xzf zendopcache-${zendopcache_ver}.tgz + pushd zendopcache-${zendopcache_ver} > /dev/null + else + src_url=https://secure.php.net/distributions/php-${PHP_detail_ver}.tar.gz && Download_src + tar xzf php-${PHP_detail_ver}.tar.gz + pushd php-${PHP_detail_ver}/ext/opcache > /dev/null + fi + + ${php_install_dir}/bin/phpize + ./configure --with-php-config=${php_install_dir}/bin/php-config + make -j ${THREAD} && make install + popd > /dev/null + if [ -f "${phpExtensionDir}/opcache.so" ]; then + # write opcache configs + if [[ "${PHP_main_ver}" =~ ^5.[3-4]$ ]]; then + # For php 5.3 5.4 + cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=${phpExtensionDir}/opcache.so +opcache.enable=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=4000 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.fast_shutdown=1 +opcache.enable_cli=1 +;opcache.optimization_level=0 +EOF + rm -rf zendopcache-${zendopcache_ver} + else + # For php 5.5+ + cat > ${php_install_dir}/etc/php.d/02-opcache.ini << EOF +[opcache] +zend_extension=opcache.so +opcache.enable=1 +opcache.enable_cli=1 +opcache.memory_consumption=${Memory_limit} +opcache.interned_strings_buffer=8 +opcache.max_accelerated_files=100000 +opcache.max_wasted_percentage=5 +opcache.use_cwd=1 +opcache.validate_timestamps=1 +opcache.revalidate_freq=60 +;opcache.save_comments=0 +opcache.fast_shutdown=1 +opcache.consistency_checks=0 +;opcache.optimization_level=0 +EOF + fi + + echo "${CSUCCESS}PHP opcache module installed successfully! ${CEND}" + rm -rf php-${PHP_detail_ver} + else + echo "${CFAILURE}PHP opcache module install failed, Please contact the author! ${CEND}" && grep -Ew 'NAME|ID|ID_LIKE|VERSION_ID|PRETTY_NAME' /etc/os-release + fi + popd > /dev/null + fi +} + +Uninstall_ZendOPcache() { + if [ -e "${php_install_dir}/etc/php.d/02-opcache.ini" ]; then + rm -f ${php_install_dir}/etc/php.d/02-opcache.ini + echo; echo "${CMSG}PHP opcache module uninstall completed${CEND}" + else + echo; echo "${CWARNING}PHP opcache module does not exist! ${CEND}" + fi +} diff --git a/init.d/Tomcat-init b/init.d/Tomcat-init new file mode 100644 index 0000000..19f6a16 --- /dev/null +++ b/init.d/Tomcat-init @@ -0,0 +1,119 @@ +#!/bin/bash +### BEGIN INIT INFO +# Provides: tomcat +# Required-Start: $remote_fs $syslog +# Required-Stop: $remote_fs $syslog +# Default-Start: 2 3 4 5 +# Default-Stop: 0 1 6 +# Short-Description: tomcat-server daemon +# Description: tomcat-server daemon +### END INIT INFO +# +# chkconfig: - 95 15 +# description: Tomcat start/stop/status script + +#Location of JAVA_HOME (bin files) +export JAVA_HOME= + +#Add Java binary files to PATH +export PATH=$JAVA_HOME/bin:$PATH + +#CATALINA_HOME is the location of the configuration files of this instance of Tomcat +CATALINA_HOME=/usr/local/tomcat + +#TOMCAT_USER is the default user of tomcat +TOMCAT_USER=www + +#TOMCAT_USAGE is the message if this script is called without any options +TOMCAT_USAGE="Usage: $0 {\e[00;32mstart\e[00m|\e[00;31mstop\e[00m|\e[00;32mstatus\e[00m|\e[00;31mrestart\e[00m}" + +#SHUTDOWN_WAIT is wait time in seconds for java proccess to stop +SHUTDOWN_WAIT=20 + +tomcat_pid() { + echo `ps -ef | grep java | grep $CATALINA_HOME/ | grep -v grep | tr -s " "|cut -d" " -f2` +} + +start() { + pid=$(tomcat_pid) + if [ -n "$pid" ]; then + echo -e "\e[00;31mTomcat is already running (pid: $pid)\e[00m" + else + echo -e "\e[00;32mStarting tomcat\e[00m" + if [ `user_exists $TOMCAT_USER` = "1" ]; then + su $TOMCAT_USER -c $CATALINA_HOME/bin/startup.sh + else + $CATALINA_HOME/bin/startup.sh + fi + status + fi + return 0 +} + +status() { + pid=$(tomcat_pid) + if [ -n "$pid" ]; then + echo -e "\e[00;32mTomcat is running with pid: $pid\e[00m" + else + echo -e "\e[00;31mTomcat is not running\e[00m" + fi +} + +stop() { + pid=$(tomcat_pid) + if [ -n "$pid" ]; then + echo -e "\e[00;31mStoping Tomcat\e[00m" + $CATALINA_HOME/bin/shutdown.sh + + let kwait=$SHUTDOWN_WAIT + count=0; + until [ `ps -p $pid | grep -c $pid` = '0' ] || [ $count -gt $kwait ] + do + echo -n -e "\e[00;31mwaiting for processes to exit\e[00m\n"; + sleep 1 + let count=$count+1; + done + + if [ $count -gt $kwait ]; then + echo -n -e "\n\e[00;31mkilling processes which didn't stop after $SHUTDOWN_WAIT seconds\e[00m" + kill -9 $pid + fi + else + echo -e "\e[00;31mTomcat is not running\e[00m" + fi + + return 0 +} + +user_exists() { + if id -u $1 >/dev/null 2>&1; then + islogin=`cat /etc/passwd | grep ^${TOMCAT_USER}: | grep nologin$` + if [ "${islogin: -7}" = "nologin" ]; then + echo "0" + else + echo "1" + fi + else + echo "0" + fi +} + +case $1 in + start) + start + ;; + stop) + stop + ;; + restart) + stop + start + ;; + status) + status + ;; + *) + echo -e $TOMCAT_USAGE + ;; +esac +exit 0 diff --git a/init.d/caddy.service b/init.d/caddy.service new file mode 100644 index 0000000..e43e528 --- /dev/null +++ b/init.d/caddy.service @@ -0,0 +1,19 @@ +[Unit] +Description=Caddy +After=network.target network-online.target +Requires=network-online.target + +[Service] +Type=notify +User=caddy +Group=caddy +ExecStart=/usr/local/caddy/bin/caddy run --environ --config /usr/local/caddy/conf/Caddyfile +ExecReload=/usr/local/caddy/bin/caddy reload --config /usr/local/caddy/conf/Caddyfile --force +TimeoutStopSec=5s +LimitNOFILE=1048576 +PrivateTmp=true +ProtectSystem=full +AmbientCapabilities=CAP_NET_ADMIN CAP_NET_BIND_SERVICE + +[Install] +WantedBy=multi-user.target \ No newline at end of file diff --git a/init.d/httpd.service b/init.d/httpd.service new file mode 100644 index 0000000..cfd0dcf --- /dev/null +++ b/init.d/httpd.service @@ -0,0 +1,18 @@ +[Unit] +Description=The Apache HTTP Server +After=network.target + +[Service] +Type=forking +PIDFile=/var/run/httpd.pid +ExecStartPre=/usr/local/apache/bin/apachectl -t +ExecStart=/usr/local/apache/bin/apachectl -k start +ExecReload=/usr/local/apache/bin/apachectl -k graceful +ExecStop=/usr/local/apache/bin/apachectl -k graceful-stop +PrivateTmp=true +LimitNOFILE=1000000 +LimitNPROC=1000000 +LimitCORE=1000000 + +[Install] +WantedBy=multi-user.target diff --git a/init.d/memcached.service b/init.d/memcached.service new file mode 100644 index 0000000..e8c3ec4 --- /dev/null +++ b/init.d/memcached.service @@ -0,0 +1,88 @@ +# It's not recommended to modify this file in-place, because it will be +# overwritten during upgrades. If you want to customize, the best +# way is to use the "systemctl edit" command to create an override unit. +# +# For example, to pass additional options, create an override unit +# (as is done by systemctl edit) and enter the following: +# +# [Service] +# Environment=OPTIONS="-l 127.0.0.1,::1" + + +[Unit] +Description=memcached daemon +After=network.target + +[Service] +Environment=PORT=11211 +Environment=USER=memcached +Environment=MAXCONN=1024 +Environment=CACHESIZE=256 +Environment="OPTIONS=-l 127.0.0.1" +ExecStart=/usr/bin/memcached -p ${PORT} -u ${USER} -m ${CACHESIZE} -c ${MAXCONN} $OPTIONS + +# Set up a new file system namespace and mounts private /tmp and /var/tmp +# directories so this service cannot access the global directories and +# other processes cannot access this service's directories. +PrivateTmp=true + +# Mounts the /usr, /boot, and /etc directories read-only for processes +# invoked by this unit. +ProtectSystem=full + +# Ensures that the service process and all its children can never gain new +# privileges +NoNewPrivileges=true + +# Sets up a new /dev namespace for the executed processes and only adds API +# pseudo devices such as /dev/null, /dev/zero or /dev/random (as well as +# the pseudo TTY subsystem) to it, but no physical devices such as /dev/sda. +PrivateDevices=true + +# Required for dropping privileges and running as a different user +CapabilityBoundingSet=CAP_SETGID CAP_SETUID CAP_SYS_RESOURCE + +# Restricts the set of socket address families accessible to the processes +# of this unit. Protects against vulnerabilities such as CVE-2016-8655 +RestrictAddressFamilies=AF_INET AF_INET6 AF_UNIX + + +# Some security features are not in the older versions of systemd used by +# e.g. RHEL7/CentOS 7. The below settings are automatically edited at package +# build time to uncomment them if the target platform supports them. + +# Attempts to create memory mappings that are writable and executable at +# the same time, or to change existing memory mappings to become executable +# are prohibited. +##safer##MemoryDenyWriteExecute=true + +# Explicit module loading will be denied. This allows to turn off module +# load and unload operations on modular kernels. It is recommended to turn +# this on for most services that do not need special file systems or extra +# kernel modules to work. +##safer##ProtectKernelModules=true + +# Kernel variables accessible through /proc/sys, /sys, /proc/sysrq-trigger, +# /proc/latency_stats, /proc/acpi, /proc/timer_stats, /proc/fs and /proc/irq +# will be made read-only to all processes of the unit. Usually, tunable +# kernel variables should only be written at boot-time, with the sysctl.d(5) +# mechanism. Almost no services need to write to these at runtime; it is hence +# recommended to turn this on for most services. +##safer##ProtectKernelTunables=true + +# The Linux Control Groups (cgroups(7)) hierarchies accessible through +# /sys/fs/cgroup will be made read-only to all processes of the unit. +# Except for container managers no services should require write access +# to the control groups hierarchies; it is hence recommended to turn this +# on for most services +##safer##ProtectControlGroups=true + +# Any attempts to enable realtime scheduling in a process of the unit are +# refused. +##safer##RestrictRealtime=true + +# Takes away the ability to create or manage any kind of namespace +##safer##RestrictNamespaces=true + +[Install] +WantedBy=multi-user.target diff --git a/init.d/mongod.service b/init.d/mongod.service new file mode 100644 index 0000000..02bfe72 --- /dev/null +++ b/init.d/mongod.service @@ -0,0 +1,37 @@ +[Unit] +Description=MongoDB Database Server +After=multi-user.target +Documentation=https://docs.mongodb.org/manual + +[Service] +User=mongod +Group=mongod +Environment="OPTIONS=-f /etc/mongod.conf" +EnvironmentFile=-/etc/sysconfig/mongod +ExecStart=/usr/local/mongodb/bin/mongod $OPTIONS +ExecStartPre=/bin/mkdir -p /var/run/mongodb +ExecStartPre=/bin/chown mongod:mongod /var/run/mongodb +ExecStartPre=/bin/chmod 0755 /var/run/mongodb +PermissionsStartOnly=true +PIDFile=/var/run/mongodb/mongod.pid +Type=forking +# file size +LimitFSIZE=infinity +# cpu time +LimitCPU=infinity +# virtual memory size +LimitAS=infinity +# open files +LimitNOFILE=64000 +# processes/threads +LimitNPROC=64000 +# locked memory +LimitMEMLOCK=infinity +# total threads (user+kernel) +TasksMax=infinity +TasksAccounting=false +# Recommended limits for for mongod as specified in +# http://docs.mongodb.org/manual/reference/ulimit/#recommended-settings + +[Install] +WantedBy=multi-user.target diff --git a/init.d/nginx.service b/init.d/nginx.service new file mode 100644 index 0000000..79e3988 --- /dev/null +++ b/init.d/nginx.service @@ -0,0 +1,20 @@ +[Unit] +Description=nginx - high performance web server +Documentation=http://nginx.org/en/docs/ +After=network.target + +[Service] +Type=forking +PIDFile=/var/run/nginx.pid +ExecStartPost=/bin/sleep 0.1 +ExecStartPre=/usr/local/nginx/sbin/nginx -t -c /usr/local/nginx/conf/nginx.conf +ExecStart=/usr/local/nginx/sbin/nginx -c /usr/local/nginx/conf/nginx.conf +ExecReload=/bin/kill -s HUP $MAINPID +ExecStop=/bin/kill -s QUIT $MAINPID +TimeoutStartSec=120 +LimitNOFILE=1000000 +LimitNPROC=1000000 +LimitCORE=1000000 + +[Install] +WantedBy=multi-user.target diff --git a/init.d/php-fpm.service b/init.d/php-fpm.service new file mode 100644 index 0000000..6538a50 --- /dev/null +++ b/init.d/php-fpm.service @@ -0,0 +1,16 @@ +[Unit] +Description=The PHP FastCGI Process Manager +Documentation=http://php.net/docs.php +After=network.target + +[Service] +Type=simple +PIDFile=/usr/local/php/var/run/php-fpm.pid +ExecStart=/usr/local/php/sbin/php-fpm --nodaemonize --fpm-config /usr/local/php/etc/php-fpm.conf +ExecReload=/bin/kill -USR2 $MAINPID +LimitNOFILE=1000000 +LimitNPROC=1000000 +LimitCORE=1000000 + +[Install] +WantedBy=multi-user.target diff --git a/init.d/postgresql.service b/init.d/postgresql.service new file mode 100644 index 0000000..107ff5f --- /dev/null +++ b/init.d/postgresql.service @@ -0,0 +1,39 @@ +[Unit] +Description=PostgreSQL database server +After=network.target + +[Service] +Type=forking + +User=postgres +Group=postgres + +# Where to send early-startup messages from the server (before the logging +# options of postgresql.conf take effect) +# This is normally controlled by the global default set by systemd +# StandardOutput=syslog + +# Disable OOM kill on the postmaster +OOMScoreAdjust=-1000 +# ... but allow it still to be effective for child processes +# (note that these settings are ignored by Postgres releases before 9.5) +Environment=PG_OOM_ADJUST_FILE=/proc/self/oom_score_adj +Environment=PG_OOM_ADJUST_VALUE=0 + +# Maximum number of seconds pg_ctl will wait for postgres to start. Note that +# PGSTARTTIMEOUT should be less than TimeoutSec value. +Environment=PGSTARTTIMEOUT=270 + +Environment=PGDATA=/data/pgsql + +ExecStart=/usr/local/pgsql/bin/pg_ctl start -D ${PGDATA} -s -w -t ${PGSTARTTIMEOUT} +ExecStop=/usr/local/pgsql/bin/pg_ctl stop -D ${PGDATA} -s -m fast +ExecReload=/usr/local/pgsql/bin/pg_ctl reload -D ${PGDATA} -s + +# Give a reasonable amount of time for the server to start up/shut down. +# Ideally, the timeout for starting PostgreSQL server should be handled more +# nicely by pg_ctl in ExecStart, so keep its timeout smaller than this value. +TimeoutSec=300 + +[Install] +WantedBy=multi-user.target diff --git a/init.d/pureftpd.service b/init.d/pureftpd.service new file mode 100644 index 0000000..31bb779 --- /dev/null +++ b/init.d/pureftpd.service @@ -0,0 +1,11 @@ +[Unit] +Description=Pure-FTPd FTP server +After=network.target + +[Service] +Type=forking +PIDFile=/var/run/pure-ftpd.pid +ExecStart=/usr/local/pureftpd/sbin/pure-ftpd /usr/local/pureftpd/etc/pure-ftpd.conf + +[Install] +WantedBy=multi-user.target diff --git a/init.d/redis-server.service b/init.d/redis-server.service new file mode 100644 index 0000000..cf67b4c --- /dev/null +++ b/init.d/redis-server.service @@ -0,0 +1,23 @@ +[Unit] +Description=Redis In-Memory Data Store +After=network.target + +[Service] +Type=forking +PIDFile=/var/run/redis/redis.pid +User=redis +Group=redis + +Environment=statedir=/var/run/redis +PermissionsStartOnly=true +ExecStartPre=/bin/mkdir -p ${statedir} +ExecStartPre=/bin/chown -R redis:redis ${statedir} +ExecStart=/usr/local/redis/bin/redis-server /usr/local/redis/etc/redis.conf +ExecStop=/bin/kill -s TERM $MAINPID +Restart=always +LimitNOFILE=1000000 +LimitNPROC=1000000 +LimitCORE=1000000 + +[Install] +WantedBy=multi-user.target diff --git a/install.sh b/install.sh new file mode 100644 index 0000000..4bebfef --- /dev/null +++ b/install.sh @@ -0,0 +1,1367 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin +clear +printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# For more information please visit https://oneinstack.com # +####################################################################### +" +# Check if user is root +[ $(id -u) != "0" ] && { echo "${CFAILURE}Error: You must be root to run this script${CEND}"; exit 1; } + +oneinstack_dir=$(dirname "`readlink -f $0`") +pushd ${oneinstack_dir} > /dev/null +. ./versions.txt +. ./options.conf +. ./include/color.sh +. ./include/check_os.sh +. ./include/check_dir.sh +. ./include/download.sh +. ./include/get_char.sh + +dbrootpwd=`< /dev/urandom tr -dc A-Za-z0-9 | head -c8` +dbpostgrespwd=`< /dev/urandom tr -dc A-Za-z0-9 | head -c8` +dbmongopwd=`< /dev/urandom tr -dc A-Za-z0-9 | head -c8` +xcachepwd=`< /dev/urandom tr -dc A-Za-z0-9 | head -c8` +dbinstallmethod=1 + +version() { + echo "version: 2.6" + echo "updated date: 2023-02-04" +} + +Show_Help() { + version + echo "Usage: $0 command ...[parameters].... + --help, -h Show this help message, More: https://oneinstack.com/auto + --version, -v Show version info + --nginx_option [1-4] Install Nginx server version + --apache Install Apache + --apache_mode_option [1-2] Apache2.4 mode, 1(default): php-fpm, 2: mod_php + --apache_mpm_option [1-3] Apache2.4 MPM, 1(default): event, 2: prefork, 3: worker + --php_option [1-13] Install PHP version + --mphp_ver [53~83] Install another PHP version (PATH: ${php_install_dir}\${mphp_ver}) + --mphp_addons Only install another PHP addons + --phpcache_option [1-4] Install PHP opcode cache, default: 1 opcache + --php_extensions [ext name] Install PHP extensions, include zendguardloader,ioncube, + sourceguardian,imagick,gmagick,fileinfo,imap,ldap,calendar,phalcon, + yaf,yar,redis,memcached,memcache,mongodb,swoole,xdebug + --nodejs Install Nodejs + --tomcat_option [1-4] Install Tomcat version + --jdk_option [1-3] Install JDK version + --db_option [1-14] Install DB version + --dbinstallmethod [1-2] DB install method, default: 1 binary install + --dbrootpwd [password] DB super password + --pureftpd Install Pure-Ftpd + --redis Install Redis + --memcached Install Memcached + --phpmyadmin Install phpMyAdmin + --ssh_port [No.] SSH port + --firewall Enable firewall + --md5sum Check md5sum + --reboot Restart the server after installation + " +} +ARG_NUM=$# +TEMP=`getopt -o hvV --long help,version,nginx_option:,apache,apache_mode_option:,apache_mpm_option:,php_option:,mphp_ver:,mphp_addons,phpcache_option:,php_extensions:,nodejs,tomcat_option:,jdk_option:,db_option:,dbrootpwd:,dbinstallmethod:,pureftpd,redis,memcached,phpmyadmin,ssh_port:,firewall,md5sum,reboot -- "$@" 2>/dev/null` +[ $? != 0 ] && echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 +eval set -- "${TEMP}" +while :; do + [ -z "$1" ] && break; + case "$1" in + -h | --help) + Show_Help + exit 0 + ;; + -v | -V | --version) + version + exit 0 + ;; + --nginx_option) + nginx_option=$2 + shift 2 + [[ ! ${nginx_option} =~ ^[1-4]$ ]] && { + echo "${CWARNING}nginx_option input error! Please only input number 1~5${CEND}" + exit 1 + } + [ -e "${nginx_install_dir}/sbin/nginx" ] && { + echo "${CWARNING}Nginx already installed! ${CEND}" + unset nginx_option + } + [ -e "${tengine_install_dir}/sbin/nginx" ] && { + echo "${CWARNING}Tengine already installed! ${CEND}" + unset nginx_option + } + [ -e "${openresty_install_dir}/nginx/sbin/nginx" ] && { + echo "${CWARNING}OpenResty already installed! ${CEND}" + unset nginx_option + } + [ -e "${caddy_install_dir}/bin/caddy" ] && { + echo "${CWARNING}Caddy already installed! ${CEND}" + unset nginx_option + } + ;; + --apache) + apache_flag=y + shift 1 + [ -e "${apache_install_dir}/bin/httpd" ] && { + echo "${CWARNING}Aapche already installed! ${CEND}" + unset apache_flag + } + ;; + --apache_mode_option) + apache_mode_option=$2 + shift 2 + [[ ! ${apache_mode_option} =~ ^[1-2]$ ]] && { + echo "${CWARNING}apache_mode_option input error! Please only input number 1~2${CEND}" + exit 1 + } + ;; + --apache_mpm_option) + apache_mpm_option=$2 + shift 2 + [[ ! ${apache_mpm_option} =~ ^[1-3]$ ]] && { + echo "${CWARNING}apache_mpm_option input error! Please only input number 1~3${CEND}" + exit 1 + } + ;; + --php_option) + php_option=$2 + shift 2 + [[ ! ${php_option} =~ ^[1-9]$|^1[0-3]$ ]] && { + echo "${CWARNING}php_option input error! Please only input number 1~12${CEND}" + exit 1 + } + [ -e "${php_install_dir}/bin/phpize" ] && { + echo "${CWARNING}PHP already installed! ${CEND}" + unset php_option + } + ;; + --mphp_ver) + mphp_ver=$2 + mphp_flag=y + shift 2 + [[ ! "${mphp_ver}" =~ ^5[3-6]$|^7[0-4]$|^8[0-3]$ ]] && { + echo "${CWARNING}mphp_ver input error! Please only input number 53~82${CEND}" + exit 1 + } + ;; + --mphp_addons) + mphp_addons_flag=y + shift 1 + ;; + --phpcache_option) + phpcache_option=$2 + shift 2 + ;; + --php_extensions) + php_extensions=$2 + shift 2 + [ -n "$(echo ${php_extensions} | grep -w zendguardloader)" ] && pecl_zendguardloader=1 + [ -n "$(echo ${php_extensions} | grep -w ioncube)" ] && pecl_ioncube=1 + [ -n "$(echo ${php_extensions} | grep -w sourceguardian)" ] && pecl_sourceguardian=1 + [ -n "$(echo ${php_extensions} | grep -w imagick)" ] && pecl_imagick=1 + [ -n "$(echo ${php_extensions} | grep -w gmagick)" ] && pecl_gmagick=1 + [ -n "$(echo ${php_extensions} | grep -w fileinfo)" ] && pecl_fileinfo=1 + [ -n "$(echo ${php_extensions} | grep -w imap)" ] && pecl_imap=1 + [ -n "$(echo ${php_extensions} | grep -w ldap)" ] && pecl_ldap=1 + [ -n "$(echo ${php_extensions} | grep -w calendar)" ] && pecl_calendar=1 + [ -n "$(echo ${php_extensions} | grep -w phalcon)" ] && pecl_phalcon=1 + [ -n "$(echo ${php_extensions} | grep -w yaf)" ] && pecl_yaf=1 + [ -n "$(echo ${php_extensions} | grep -w yar)" ] && pecl_yar=1 + [ -n "$(echo ${php_extensions} | grep -w redis)" ] && pecl_redis=1 + [ -n "$(echo ${php_extensions} | grep -w memcached)" ] && pecl_memcached=1 + [ -n "$(echo ${php_extensions} | grep -w memcache)" ] && pecl_memcache=1 + [ -n "$(echo ${php_extensions} | grep -w mongodb)" ] && pecl_mongodb=1 + [ -n "$(echo ${php_extensions} | grep -w swoole)" ] && pecl_swoole=1 + [ -n "$(echo ${php_extensions} | grep -w xdebug)" ] && pecl_xdebug=1 + ;; + --nodejs) + nodejs_flag=y + shift 1 + [ -e "${nodejs_install_dir}/bin/node" ] && { + echo "${CWARNING}Nodejs already installed! ${CEND}" + unset nodejs_flag + } + ;; + --tomcat_option) + tomcat_option=$2 + shift 2 + [[ ! ${tomcat_option} =~ ^[1-4]$ ]] && { + echo "${CWARNING}tomcat_option input error! Please only input number 1~4${CEND}" + exit 1 + } + [ -e "$tomcat_install_dir/conf/server.xml" ] && { + echo "${CWARNING}Tomcat already installed! ${CEND}" + unset tomcat_option + } + ;; + --jdk_option) + jdk_option=$2 + shift 2 + [[ ! ${jdk_option} =~ ^[1-3]$ ]] && { + echo "${CWARNING}jdk_option input error! Please only input number 1~3${CEND}" + exit 1 + } + ;; + --db_option) + db_option=$2 + shift 2 + if [[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]]; then + [ -d "${db_install_dir}/support-files" ] && { + echo "${CWARNING}MySQL already installed! ${CEND}" + unset db_option + } + elif [ "${db_option}" == '13' ]; then + [ -e "${pgsql_install_dir}/bin/psql" ] && { + echo "${CWARNING}PostgreSQL already installed! ${CEND}" + unset db_option + } + elif [ "${db_option}" == '14' ]; then + [ -e "${mongo_install_dir}/bin/mongo" ] && { + echo "${CWARNING}MongoDB already installed! ${CEND}" + unset db_option + } + else + echo "${CWARNING}db_option input error! Please only input number 1~14${CEND}" + exit 1 + fi + ;; + --dbrootpwd) + dbrootpwd=$2 + shift 2 + dbpostgrespwd="${dbrootpwd}" + dbmongopwd="${dbrootpwd}" + ;; + --dbinstallmethod) + dbinstallmethod=$2 + shift 2 + [[ ! ${dbinstallmethod} =~ ^[1-2]$ ]] && { + echo "${CWARNING}dbinstallmethod input error! Please only input number 1~2${CEND}" + exit 1 + } + ;; + --pureftpd) + pureftpd_flag=y + shift 1 + [ -e "${pureftpd_install_dir}/sbin/pure-ftpwho" ] && { + echo "${CWARNING}Pure-FTPd already installed! ${CEND}" + unset pureftpd_flag + } + ;; + --redis) + redis_flag=y + shift 1 + [ -e "${redis_install_dir}/bin/redis-server" ] && { + echo "${CWARNING}redis-server already installed! ${CEND}" + unset redis_flag + } + ;; + --memcached) + memcached_flag=y + shift 1 + [ -e "${memcached_install_dir}/bin/memcached" ] && { + echo "${CWARNING}memcached-server already installed! ${CEND}" + unset memcached_flag + } + ;; + --phpmyadmin) + phpmyadmin_flag=y + shift 1 + [ -d "${wwwroot_dir}/default/phpMyAdmin" ] && { + echo "${CWARNING}phpMyAdmin already installed! ${CEND}" + unset phpmyadmin_flag + } + ;; + --ssh_port) + ssh_port=$2 + shift 2 + ;; + --firewall) + firewall_flag=y + shift 1 + ;; + --md5sum) + md5sum_flag=y; shift 1 + ;; + --reboot) + reboot_flag=y + shift 1 + ;; + --) + shift + ;; + *) + echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 + ;; + esac +done + +# Check md5sum +if [ ${ARG_NUM} == 0 ] && [ ! -e ~/.oneinstack ]; then + # Check md5sum + while :; do echo + read -e -p "Do you want to check md5sum? [y/n]: " md5sum_flag + if [[ ! ${md5sum_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done +fi +if [ "${md5sum_flag}" == 'y' ]; then + [ -e "${oneinstack_dir}.tar.gz" ] && oneinstack_file=${oneinstack_dir}.tar.gz + [ -e "${oneinstack_dir}-full.tar.gz" ] && oneinstack_file=${oneinstack_dir}-full.tar.gz + oneinstack_tgz=${oneinstack_file##*/} + if [ -e "${oneinstack_file}" ]; then + now_oneinstack_md5=$(md5sum ${oneinstack_file} | awk '{print $1}') + latest_oneinStack_md5=$(curl --connect-timeout 3 -m 5 -s ${mirror_link}/md5sum.txt | grep ${oneinstack_tgz} | awk '{print $1}') + if [ "${now_oneinstack_md5}" != "${latest_oneinStack_md5}" ]; then + echo "${CFAILURE}Error: The md5 value of the installation package does not match the official website, please download again, url: ${mirror_link}/${oneinstack_tgz}${CEND}" + exit 1 + fi + else + echo "${CFAILURE}Error: ${oneinstack_file} does not exist${CEND}" + exit 1 + fi +fi + +# Use default SSH port 22. If you use another SSH port on your server +if [ -e "/etc/ssh/sshd_config" ]; then + [ -z "`grep ^Port /etc/ssh/sshd_config`" ] && now_ssh_port=22 || now_ssh_port=`grep ^Port /etc/ssh/sshd_config | awk '{print $2}' | head -1` + while :; do echo + [ ${ARG_NUM} == 0 ] && read -e -p "Please input SSH port(Default: ${now_ssh_port}): " ssh_port + ssh_port=${ssh_port:-${now_ssh_port}} + if [ ${ssh_port} -eq 22 >/dev/null 2>&1 -o ${ssh_port} -gt 1024 >/dev/null 2>&1 -a ${ssh_port} -lt 65535 >/dev/null 2>&1 ]; then + break + else + echo "${CWARNING}input error! Input range: 22,1025~65534${CEND}" + exit 1 + fi + done + + if [ -z "`grep ^Port /etc/ssh/sshd_config`" -a "${ssh_port}" != '22' ]; then + sed -i "s@^#Port.*@&\nPort ${ssh_port}@" /etc/ssh/sshd_config + elif [ -n "`grep ^Port /etc/ssh/sshd_config`" ]; then + sed -i "s@^Port.*@Port ${ssh_port}@" /etc/ssh/sshd_config + fi +fi + +if [ ${ARG_NUM} == 0 ]; then + if [ ! -e ~/.oneinstack ]; then + # check firewall + while :; do echo + read -e -p "Do you want to enable firewall? [y/n]: " firewall_flag + if [[ ! ${firewall_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + fi + + # check Web server + while :; do echo + read -e -p "Do you want to install Web server? [y/n]: " web_flag + if [[ ! ${web_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + if [ "${web_flag}" == 'y' ]; then + # Nginx/Tegine/OpenResty + while :; do + echo + echo 'Please select Web server type:' + echo -e "\t${CMSG}1${CEND}. Install Nginx" + echo -e "\t${CMSG}2${CEND}. Install Tengine" + echo -e "\t${CMSG}3${CEND}. Install OpenResty" + echo -e "\t${CMSG}4${CEND}. Install Caddy" + echo -e "\t${CMSG}5${CEND}. Do not install" + read -e -p "Please input a number:(Default 1 press Enter) " nginx_option + nginx_option=${nginx_option:-1} + if [[ ! ${nginx_option} =~ ^[1-5]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~5${CEND}" + else + [ "${nginx_option}" != '5' -a -e "${nginx_install_dir}/sbin/nginx" ] && { + echo "${CWARNING}Nginx already installed! ${CEND}" + unset nginx_option + } + [ "${nginx_option}" != '5' -a -e "${tengine_install_dir}/sbin/nginx" ] && { + echo "${CWARNING}Tengine already installed! ${CEND}" + unset nginx_option + } + [ "${nginx_option}" != '5' -a -e "${openresty_install_dir}/nginx/sbin/nginx" ] && { + echo "${CWARNING}OpenResty already installed! ${CEND}" + unset nginx_option + } + [ "${nginx_option}" != '5' -a -e "${caddy_install_dir}/nginx/sbin/nginx" ] && { + echo "${CWARNING}Caddy already installed! ${CEND}" + unset nginx_option + } + break + fi + done + if [[ ${nginx_option} =~ ^[1-3]$ ]]; then + # Apache + while :; do + echo + read -e -p "Do you want to install Apache? [y/n]: " apache_flag + if [[ ! ${apache_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + [ "${apache_flag}" == 'y' -a -e "${apache_install_dir}/bin/httpd" ] && { + echo "${CWARNING}Aapche already installed! ${CEND}" + unset apache_flag + } + break + fi + done + # Apache2.4 mode and Apache2.4 MPM + if [ "${apache_flag}" == 'y' -o -e "${apache_install_dir}/bin/httpd" ]; then + while :; do + echo + echo 'Please select Apache mode:' + echo -e "\t${CMSG}1${CEND}. php-fpm" + echo -e "\t${CMSG}2${CEND}. mod_php" + read -e -p "Please input a number:(Default 1 press Enter) " apache_mode_option + apache_mode_option=${apache_mode_option:-1} + if [[ ! ${apache_mode_option} =~ ^[1-2]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~2${CEND}" + else + break + fi + done + while :; do + echo + echo 'Please select Apache MPM:' + echo -e "\t${CMSG}1${CEND}. event" + echo -e "\t${CMSG}2${CEND}. prefork" + echo -e "\t${CMSG}3${CEND}. worker" + read -e -p "Please input a number:(Default 1 press Enter) " apache_mpm_option + apache_mpm_option=${apache_mpm_option:-1} + if [[ ! ${apache_mpm_option} =~ ^[1-3]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~3${CEND}" + else + break + fi + done + fi + # Tomcat + while :; do + echo + echo 'Please select tomcat server:' + echo -e "\t${CMSG}1${CEND}. Install Tomcat-10" + echo -e "\t${CMSG}2${CEND}. Install Tomcat-9" + echo -e "\t${CMSG}3${CEND}. Install Tomcat-8" + echo -e "\t${CMSG}4${CEND}. Install Tomcat-7" + echo -e "\t${CMSG}5${CEND}. Do not install" + read -e -p "Please input a number:(Default 5 press Enter) " tomcat_option + tomcat_option=${tomcat_option:-5} + if [[ ! ${tomcat_option} =~ ^[1-5]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~5${CEND}" + else + [ "${tomcat_option}" != '5' -a -e "$tomcat_install_dir/conf/server.xml" ] && { + echo "${CWARNING}Tomcat already installed! ${CEND}" + unset tomcat_option + } + if [[ "${tomcat_option}" =~ ^1$ ]]; then + while :; do + echo + echo 'Please select JDK version:' + echo -e "\t${CMSG}2${CEND}. Install openjdk-11-jdk" + echo -e "\t${CMSG}3${CEND}. Install openjdk-17-jdk" + read -e -p "Please input a number:(Default 1 press Enter) " jdk_option + jdk_option=${jdk_option:-2} + if [[ ! ${jdk_option} =~ ^[2-3]$ ]]; then + echo "${CWARNING}input error! Please only input number 2~3${CEND}" + else + break + fi + done + elif [[ "${tomcat_option}" =~ ^[2-3]$ ]]; then + while :; do + echo + echo 'Please select JDK version:' + echo -e "\t${CMSG}1${CEND}. Install openjdk-8-jdk" + echo -e "\t${CMSG}2${CEND}. Install openjdk-11-jdk" + echo -e "\t${CMSG}3${CEND}. Install openjdk-17-jdk" + read -e -p "Please input a number:(Default 1 press Enter) " jdk_option + jdk_option=${jdk_option:-1} + if [[ ! ${jdk_option} =~ ^[1-3]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~3${CEND}" + else + break + fi + done + elif [ "${tomcat_option}" == '4' ]; then + while :; do + echo + echo 'Please select JDK version:' + echo -e "\t${CMSG}1${CEND}. Install openjdk-8-jdk" + read -e -p "Please input a number:(Default 1 press Enter) " jdk_option + jdk_option=${jdk_option:-1} + if [[ ! ${jdk_option} =~ ^1$ ]]; then + echo "${CWARNING}input error! Please only input number 1${CEND}" + else + break + fi + done + fi + break + fi + done + elif [ "${nginx_option}" == '4' ]; then + # Caddy + while :; do + echo + read -e -p "Do you want to install Caddy? [y/n]: " caddy_flag + if [[ ! ${caddy_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + [ "${caddy_flag}" == 'y' -a -e "${caddy_install_dir}/bin/caddy" ] && { + echo "${CWARNING}Caddy already installed! ${CEND}" + unset caddy_flag + } + break + fi + done + fi + fi + break + fi + done + + # choice database + while :; do + echo + read -e -p "Do you want to install Database? [y/n]: " db_flag + if [[ ! ${db_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + if [ "${db_flag}" == 'y' ]; then + while :; do + echo + echo 'Please select a version of the Database:' + echo -e "\t${CMSG} 1${CEND}. Install MySQL-8.0" + echo -e "\t${CMSG} 2${CEND}. Install MySQL-5.7" + echo -e "\t${CMSG} 3${CEND}. Install MySQL-5.6" + echo -e "\t${CMSG} 4${CEND}. Install MySQL-5.5" + echo -e "\t${CMSG} 5${CEND}. Install MariaDB-10.11" + echo -e "\t${CMSG} 6${CEND}. Install MariaDB-10.5" + echo -e "\t${CMSG} 7${CEND}. Install MariaDB-10.4" + echo -e "\t${CMSG} 8${CEND}. Install MariaDB-5.5" + echo -e "\t${CMSG} 9${CEND}. Install Percona-8.0" + echo -e "\t${CMSG}10${CEND}. Install Percona-5.7" + echo -e "\t${CMSG}11${CEND}. Install Percona-5.6" + echo -e "\t${CMSG}12${CEND}. Install Percona-5.5" + echo -e "\t${CMSG}13${CEND}. Install PostgreSQL" + echo -e "\t${CMSG}14${CEND}. Install MongoDB" + read -e -p "Please input a number:(Default 2 press Enter) " db_option + db_option=${db_option:-2} + if [[ "${db_option}" =~ ^[1-9]$|^1[0-4]$ ]]; then + if [ "${db_option}" == '13' ]; then + [ -e "${pgsql_install_dir}/bin/psql" ] && { echo "${CWARNING}PostgreSQL already installed! ${CEND}"; unset db_option; break; } + elif [ "${db_option}" == '14' ]; then + [ -e "${mongo_install_dir}/bin/mongo" ] && { echo "${CWARNING}MongoDB already installed! ${CEND}"; unset db_option; break; } + else + [ -d "${db_install_dir}/support-files" ] && { echo "${CWARNING}MySQL already installed! ${CEND}"; unset db_option; break; } + fi + while :; do + if [ "${db_option}" == '13' ]; then + read -e -p "Please input the postgres password of PostgreSQL(default: ${dbpostgrespwd}): " dbpwd + dbpwd=${dbpwd:-${dbpostgrespwd}} + elif [ "${db_option}" == '14' ]; then + read -e -p "Please input the root password of MongoDB(default: ${dbmongopwd}): " dbpwd + dbpwd=${dbpwd:-${dbmongopwd}} + else + read -e -p "Please input the root password of MySQL(default: ${dbrootpwd}): " dbpwd + dbpwd=${dbpwd:-${dbrootpwd}} + fi + [ -n "`echo ${dbpwd} | grep '[+|&]'`" ] && { echo "${CWARNING}input error,not contain a plus sign (+) and & ${CEND}"; continue; } + if (( ${#dbpwd} >= 5 )); then + if [ "${db_option}" == '13' ]; then + dbpostgrespwd=${dbpwd} + elif [ "${db_option}" == '14' ]; then + dbmongopwd=${dbpwd} + else + dbrootpwd=${dbpwd} + fi + break + else + echo "${CWARNING}password least 5 characters! ${CEND}" + fi + done + # choose install methods + if [[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]]; then + while :; do echo + echo "Please choose installation of the database:" + echo -e "\t${CMSG}1${CEND}. Install database from binary package." + echo -e "\t${CMSG}2${CEND}. Install database from source package." + read -e -p "Please input a number:(Default 1 press Enter) " dbinstallmethod + dbinstallmethod=${dbinstallmethod:-1} + if [[ ! ${dbinstallmethod} =~ ^[1-2]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~2${CEND}" + else + break + fi + done + fi + break + else + echo "${CWARNING}input error! Please only input number 1~14${CEND}" + fi + done + fi + break + fi + done + + # choice php + while :; do echo + read -e -p "Do you want to install PHP? [y/n]: " php_flag + if [[ ! ${php_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + if [ "${php_flag}" == 'y' ]; then + [ -e "${php_install_dir}/bin/phpize" ] && { echo "${CWARNING}PHP already installed! ${CEND}"; unset php_option; break; } + while :; do echo + echo 'Please select a version of the PHP:' + echo -e "\t${CMSG} 1${CEND}. Install php-5.3" + echo -e "\t${CMSG} 2${CEND}. Install php-5.4" + echo -e "\t${CMSG} 3${CEND}. Install php-5.5" + echo -e "\t${CMSG} 4${CEND}. Install php-5.6" + echo -e "\t${CMSG} 5${CEND}. Install php-7.0" + echo -e "\t${CMSG} 6${CEND}. Install php-7.1" + echo -e "\t${CMSG} 7${CEND}. Install php-7.2" + echo -e "\t${CMSG} 8${CEND}. Install php-7.3" + echo -e "\t${CMSG} 9${CEND}. Install php-7.4" + echo -e "\t${CMSG}10${CEND}. Install php-8.0" + echo -e "\t${CMSG}11${CEND}. Install php-8.1" + echo -e "\t${CMSG}12${CEND}. Install php-8.2" + echo -e "\t${CMSG}13${CEND}. Install php-8.3" + read -e -p "Please input a number:(Default 7 press Enter) " php_option + php_option=${php_option:-7} + if [[ ! ${php_option} =~ ^[1-9]$|^1[0-3]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~13${CEND}" + else + break + fi + done + fi + break + fi + done + + # check php ver + if [ -e "${php_install_dir}/bin/phpize" ]; then + PHP_detail_ver=$(${php_install_dir}/bin/php-config --version) + PHP_main_ver=${PHP_detail_ver%.*} + fi + + # PHP opcode cache and extensions + if [[ ${php_option} =~ ^[1-9]$|^1[0-3]$ ]] || [ -e "${php_install_dir}/bin/phpize" ]; then + while :; do echo + read -e -p "Do you want to install opcode cache of the PHP? [y/n]: " phpcache_flag + if [[ ! ${phpcache_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + if [ "${phpcache_flag}" == 'y' ]; then + if [ "${php_option}" == '1' -o "${PHP_main_ver}" == '5.3' ]; then + while :; do + echo 'Please select a opcode cache of the PHP:' + echo -e "\t${CMSG}1${CEND}. Install Zend OPcache" + echo -e "\t${CMSG}2${CEND}. Install APCU" + echo -e "\t${CMSG}3${CEND}. Install XCache" + echo -e "\t${CMSG}4${CEND}. Install eAccelerator-0.9" + read -e -p "Please input a number:(Default 1 press Enter) " phpcache_option + phpcache_option=${phpcache_option:-1} + if [[ ! ${phpcache_option} =~ ^[1-4]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~4${CEND}" + else + break + fi + done + fi + if [ "${php_option}" == '2' -o "${PHP_main_ver}" == '5.4' ]; then + while :; do + echo 'Please select a opcode cache of the PHP:' + echo -e "\t${CMSG}1${CEND}. Install Zend OPcache" + echo -e "\t${CMSG}2${CEND}. Install APCU" + echo -e "\t${CMSG}3${CEND}. Install XCache" + echo -e "\t${CMSG}4${CEND}. Install eAccelerator-1.0-dev" + read -e -p "Please input a number:(Default 1 press Enter) " phpcache_option + phpcache_option=${phpcache_option:-1} + if [[ ! ${phpcache_option} =~ ^[1-4]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~4${CEND}" + else + break + fi + done + fi + if [ "${php_option}" == '3' -o "${PHP_main_ver}" == '5.5' ]; then + while :; do + echo 'Please select a opcode cache of the PHP:' + echo -e "\t${CMSG}1${CEND}. Install Zend OPcache" + echo -e "\t${CMSG}2${CEND}. Install APCU" + echo -e "\t${CMSG}3${CEND}. Install XCache" + read -e -p "Please input a number:(Default 1 press Enter) " phpcache_option + phpcache_option=${phpcache_option:-1} + if [[ ! ${phpcache_option} =~ ^[1-3]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~3${CEND}" + else + break + fi + done + fi + if [ "${php_option}" == '4' -o "${PHP_main_ver}" == '5.6' ]; then + while :; do + echo 'Please select a opcode cache of the PHP:' + echo -e "\t${CMSG}1${CEND}. Install Zend OPcache" + echo -e "\t${CMSG}2${CEND}. Install APCU" + echo -e "\t${CMSG}3${CEND}. Install XCache" + read -e -p "Please input a number:(Default 1 press Enter) " phpcache_option + phpcache_option=${phpcache_option:-1} + if [[ ! ${phpcache_option} =~ ^[1-3]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~3${CEND}" + else + break + fi + done + fi + if [[ ${php_option} =~ ^[5-9]$|^1[0-3]$ ]] || [[ "${PHP_main_ver}" =~ ^7.[0-4]$|^8.[0-3]$ ]]; then + while :; do + echo 'Please select a opcode cache of the PHP:' + echo -e "\t${CMSG}1${CEND}. Install Zend OPcache" + echo -e "\t${CMSG}2${CEND}. Install APCU" + read -e -p "Please input a number:(Default 1 press Enter) " phpcache_option + phpcache_option=${phpcache_option:-1} + if [[ ! ${phpcache_option} =~ ^[1-2]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~2${CEND}" + else + break + fi + done + fi + fi + break + fi + done + # set xcache passwd + if [ "${phpcache_option}" == '3' ]; then + while :; do + read -e -p "Please input xcache admin password: " xcachepwd + (( ${#xcachepwd} >= 5 )) && { xcachepwd_md5=$(echo -n "${xcachepwd}" | md5sum | awk '{print $1}') ; break ; } || echo "${CFAILURE}xcache admin password least 5 characters! ${CEND}" + done + fi + # PHP extension + while :; do + echo + echo 'Please select PHP extensions:' + echo -e "\t${CMSG} 0${CEND}. Do not install" + echo -e "\t${CMSG} 1${CEND}. Install zendguardloader(PHP<=5.6)" + echo -e "\t${CMSG} 2${CEND}. Install ioncube" + echo -e "\t${CMSG} 3${CEND}. Install sourceguardian(PHP<=7.2)" + echo -e "\t${CMSG} 4${CEND}. Install imagick" + echo -e "\t${CMSG} 5${CEND}. Install gmagick" + echo -e "\t${CMSG} 6${CEND}. Install fileinfo" + echo -e "\t${CMSG} 7${CEND}. Install imap" + echo -e "\t${CMSG} 8${CEND}. Install ldap" + echo -e "\t${CMSG} 9${CEND}. Install phalcon(PHP>=5.5)" + echo -e "\t${CMSG}10${CEND}. Install yaf(PHP>=7.0)" + echo -e "\t${CMSG}11${CEND}. Install redis" + echo -e "\t${CMSG}12${CEND}. Install memcached" + echo -e "\t${CMSG}13${CEND}. Install memcache" + echo -e "\t${CMSG}14${CEND}. Install mongodb" + echo -e "\t${CMSG}15${CEND}. Install swoole" + echo -e "\t${CMSG}16${CEND}. Install xdebug(PHP>=5.5)" + read -e -p "Please input numbers:(Default '4 11 12' press Enter) " phpext_option + phpext_option=${phpext_option:-'4 11 12'} + [ "${phpext_option}" == '0' ] && break + array_phpext=(${phpext_option}) + array_all=(1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16) + for v in ${array_phpext[@]} + do + [ -z "`echo ${array_all[@]} | grep -w ${v}`" ] && phpext_flag=1 + done + if [ "${phpext_flag}" == '1' ]; then + unset phpext_flag + echo; echo "${CWARNING}input error! Please only input number 4 11 12 and so on${CEND}"; echo + continue + else + [ -n "`echo ${array_phpext[@]} | grep -w 1`" ] && pecl_zendguardloader=1 + [ -n "`echo ${array_phpext[@]} | grep -w 2`" ] && pecl_ioncube=1 + [ -n "`echo ${array_phpext[@]} | grep -w 3`" ] && pecl_sourceguardian=1 + [ -n "`echo ${array_phpext[@]} | grep -w 4`" ] && pecl_imagick=1 + [ -n "`echo ${array_phpext[@]} | grep -w 5`" ] && pecl_gmagick=1 + [ -n "`echo ${array_phpext[@]} | grep -w 6`" ] && pecl_fileinfo=1 + [ -n "`echo ${array_phpext[@]} | grep -w 7`" ] && pecl_imap=1 + [ -n "`echo ${array_phpext[@]} | grep -w 8`" ] && pecl_ldap=1 + [ -n "`echo ${array_phpext[@]} | grep -w 9`" ] && pecl_phalcon=1 + [ -n "`echo ${array_phpext[@]} | grep -w 10`" ] && pecl_yaf=1 + [ -n "`echo ${array_phpext[@]} | grep -w 11`" ] && pecl_redis=1 + [ -n "`echo ${array_phpext[@]} | grep -w 12`" ] && pecl_memcached=1 + [ -n "`echo ${array_phpext[@]} | grep -w 13`" ] && pecl_memcache=1 + [ -n "`echo ${array_phpext[@]} | grep -w 14`" ] && pecl_mongodb=1 + [ -n "`echo ${array_phpext[@]} | grep -w 15`" ] && pecl_swoole=1 + [ -n "`echo ${array_phpext[@]} | grep -w 16`" ] && pecl_xdebug=1 + break + fi + done + fi + + # check Nodejs + while :; do echo + read -e -p "Do you want to install Nodejs? [y/n]: " nodejs_flag + if [[ ! ${nodejs_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + [ "${nodejs_flag}" == 'y' -a -e "${nodejs_install_dir}/bin/node" ] && { echo "${CWARNING}Nodejs already installed! ${CEND}"; unset nodejs_flag; } + break + fi + done + + # check Pureftpd + while :; do echo + read -e -p "Do you want to install Pure-FTPd? [y/n]: " pureftpd_flag + if [[ ! ${pureftpd_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + [ "${pureftpd_flag}" == 'y' -a -e "${pureftpd_install_dir}/sbin/pure-ftpwho" ] && { echo "${CWARNING}Pure-FTPd already installed! ${CEND}"; unset pureftpd_flag; } + break + fi + done + + # check phpMyAdmin + if [[ ${php_option} =~ ^[1-9]$|^1[0-3]$ ]] || [ -e "${php_install_dir}/bin/phpize" ]; then + while :; do echo + read -e -p "Do you want to install phpMyAdmin? [y/n]: " phpmyadmin_flag + if [[ ! ${phpmyadmin_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + [ "${phpmyadmin_flag}" == 'y' -a -d "${wwwroot_dir}/default/phpMyAdmin" ] && { echo "${CWARNING}phpMyAdmin already installed! ${CEND}"; unset phpmyadmin_flag; } + break + fi + done + fi + + # check redis + while :; do echo + read -e -p "Do you want to install redis-server? [y/n]: " redis_flag + if [[ ! ${redis_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + [ "${redis_flag}" == 'y' -a -e "${redis_install_dir}/bin/redis-server" ] && { echo "${CWARNING}redis-server already installed! ${CEND}"; unset redis_flag; } + break + fi + done + + # check memcached + while :; do echo + read -e -p "Do you want to install memcached-server? [y/n]: " memcached_flag + if [[ ! ${memcached_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + [ "${memcached_flag}" == 'y' -a -e "${memcached_install_dir}/bin/memcached" ] && { echo "${CWARNING}memcached-server already installed! ${CEND}"; unset memcached_flag; } + break + fi + done +fi + +if [[ ${nginx_option} =~ ^[1-4]$ ]] || [ "${apache_flag}" == 'y' ] || [ "${caddy_flag}" == 'y' ] || [[ ${tomcat_option} =~ ^[1-4]$ ]]; then + [ ! -d ${wwwroot_dir}/default ] && mkdir -p ${wwwroot_dir}/default + [ ! -d ${wwwlogs_dir} ] && mkdir -p ${wwwlogs_dir} +fi +[ -d /data ] && chmod 755 /data + +# install wget gcc curl +if [ ! -e ~/.oneinstack ]; then + downloadDepsSrc=1 + [ "${PM}" == 'apt-get' ] && apt-get -y update > /dev/null + [ "${PM}" == 'yum' ] && yum clean all > /dev/null + ${PM} -y install wget gcc curl > /dev/null +fi + +# get the IP information +IPADDR=$(./include/ois.${ARCH} ip_local) +OUTIP_STATE=$(./include/ois.${ARCH} ip_state) + +# openSSL +. ./include/openssl.sh + +# Check download source packages +. ./include/check_download.sh + +[ "${armplatform}" == "y" ] && dbinstallmethod=2 +checkDownload 2>&1 | tee -a ${oneinstack_dir}/install.log + +# get OS Memory +. ./include/memory.sh + +if [ ! -e ~/.oneinstack ]; then + # Check binary dependencies packages + . ./include/check_sw.sh + case "${Family}" in + "rhel") + installDepsRHEL 2>&1 | tee ${oneinstack_dir}/install.log + . include/init_RHEL.sh 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + "debian") + installDepsDebian 2>&1 | tee ${oneinstack_dir}/install.log + . include/init_Debian.sh 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + "ubuntu") + installDepsUbuntu 2>&1 | tee ${oneinstack_dir}/install.log + . include/init_Ubuntu.sh 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + esac + # Install dependencies from source package + installDepsBySrc 2>&1 | tee -a ${oneinstack_dir}/install.log +fi + +# start Time +startTime=`date +%s` + +# openSSL +Install_openSSL | tee -a ${oneinstack_dir}/install.log + +# Jemalloc +if [[ ${nginx_option} =~ ^[1-3]$ ]] || [[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]]; then + . include/jemalloc.sh + Install_Jemalloc | tee -a ${oneinstack_dir}/install.log +fi + +# Database +case "${db_option}" in + 1) + . include/mysql-8.0.sh + Install_MySQL80 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 2) + . include/mysql-5.7.sh + Install_MySQL57 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 3) + . include/mysql-5.6.sh + Install_MySQL56 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 4) + . include/mysql-5.5.sh + Install_MySQL55 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 5) + . include/mariadb-10.11.sh + Install_MariaDB1011 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 6) + . include/mariadb-10.5.sh + Install_MariaDB105 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 7) + . include/mariadb-10.4.sh + Install_MariaDB104 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 8) + . include/mariadb-5.5.sh + Install_MariaDB55 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 9) + [ "${Family}" == 'rhel' ] && [ "${RHEL_ver}" == '8' ] && dbinstallmethod=2 && checkDownload + . include/percona-8.0.sh + Install_Percona80 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 10) + . include/percona-5.7.sh + Install_Percona57 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 11) + . include/percona-5.6.sh + Install_Percona56 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 12) + . include/percona-5.5.sh + Install_Percona55 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 13) + . include/postgresql.sh + Install_PostgreSQL 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 14) + . include/mongodb.sh + Install_MongoDB 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; +esac + +# Nginx server +case "${nginx_option}" in +1) + . include/nginx.sh + Install_Nginx 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; +2) + . include/tengine.sh + Install_Tengine 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; +3) + . include/openresty.sh + Install_OpenResty 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; +4) + . include/caddy.sh + Install_Caddy 2>&1 | tee -a ${oneinstack_dir}/install.log + caddy_flag='y' + ;; +esac + +# Apache +if [ "${apache_flag}" == 'y' ]; then + apache_mode_option=${apache_mode_option:-1} + apache_mpm_option=${apache_mpm_option:-1} + . include/apache.sh + Install_Apache 2>&1 | tee -a ${oneinstack_dir}/install.log +fi + +# PHP +case "${php_option}" in + 1) + . include/php-5.3.sh + Install_PHP53 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 2) + . include/php-5.4.sh + Install_PHP54 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 3) + . include/php-5.5.sh + Install_PHP55 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 4) + . include/php-5.6.sh + Install_PHP56 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 5) + . include/php-7.0.sh + Install_PHP70 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 6) + . include/php-7.1.sh + Install_PHP71 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 7) + . include/php-7.2.sh + Install_PHP72 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 8) + . include/php-7.3.sh + Install_PHP73 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 9) + . include/php-7.4.sh + Install_PHP74 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 10) + . include/php-8.0.sh + Install_PHP80 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 11) + . include/php-8.1.sh + Install_PHP81 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 12) + . include/php-8.2.sh + Install_PHP82 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 13) + . include/php-8.3.sh + Install_PHP83 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; +esac + +PHP_addons() { + # PHP opcode cache + case "${phpcache_option}" in + 1) + . include/zendopcache.sh + Install_ZendOPcache 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 2) + . include/apcu.sh + Install_APCU 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 3) + . include/xcache.sh + Install_XCache 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 4) + . include/eaccelerator.sh + Install_eAccelerator 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + esac + + # ZendGuardLoader + if [ "${pecl_zendguardloader}" == '1' ]; then + . include/ZendGuardLoader.sh + Install_ZendGuardLoader 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # ioncube + if [ "${pecl_ioncube}" == '1' ]; then + . include/ioncube.sh + Install_ionCube 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # SourceGuardian + if [ "${pecl_sourceguardian}" == '1' ]; then + . include/sourceguardian.sh + Install_SourceGuardian 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # imagick + if [ "${pecl_imagick}" == '1' ]; then + . include/ImageMagick.sh + Install_ImageMagick 2>&1 | tee -a ${oneinstack_dir}/install.log + Install_pecl_imagick 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # gmagick + if [ "${pecl_gmagick}" == '1' ]; then + . include/GraphicsMagick.sh + Install_GraphicsMagick 2>&1 | tee -a ${oneinstack_dir}/install.log + Install_pecl_gmagick 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # fileinfo + if [ "${pecl_fileinfo}" == '1' ]; then + . include/pecl_fileinfo.sh + Install_pecl_fileinfo 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # imap + if [ "${pecl_imap}" == '1' ]; then + . include/pecl_imap.sh + Install_pecl_imap 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # ldap + if [ "${pecl_ldap}" == '1' ]; then + . include/pecl_ldap.sh + Install_pecl_ldap 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # calendar + if [ "${pecl_calendar}" == '1' ]; then + . include/pecl_calendar.sh + Install_pecl_calendar 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # phalcon + if [ "${pecl_phalcon}" == '1' ]; then + . include/pecl_phalcon.sh + Install_pecl_phalcon 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # yaf + if [ "${pecl_yaf}" == '1' ]; then + . include/pecl_yaf.sh + Install_pecl_yaf 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # yar + if [ "${pecl_yar}" == '1' ]; then + . include/pecl_yar.sh + Install_pecl_yar 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # pecl_memcached + if [ "${pecl_memcached}" == '1' ]; then + . include/memcached.sh + Install_pecl_memcached 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # pecl_memcache + if [ "${pecl_memcache}" == '1' ]; then + . include/memcached.sh + Install_pecl_memcache 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # pecl_redis + if [ "${pecl_redis}" == '1' ]; then + . include/redis.sh + Install_pecl_redis 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # pecl_mongodb + if [ "${pecl_mongodb}" == '1' ]; then + . include/pecl_mongodb.sh + Install_pecl_mongodb 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # swoole + if [ "${pecl_swoole}" == '1' ]; then + . include/pecl_swoole.sh + Install_pecl_swoole 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # xdebug + if [ "${pecl_xdebug}" == '1' ]; then + . include/pecl_xdebug.sh + Install_pecl_xdebug 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # pecl_pgsql + if [ -e "${pgsql_install_dir}/bin/psql" ]; then + . include/pecl_pgsql.sh + Install_pecl_pgsql 2>&1 | tee -a ${oneinstack_dir}/install.log + fi +} + +[ "${mphp_addons_flag}" != 'y' ] && PHP_addons + +if [ "${mphp_flag}" == 'y' ]; then + . include/mphp.sh + Install_MPHP 2>&1 | tee -a ${oneinstack_dir}/install.log + php_install_dir=${php_install_dir}${mphp_ver} + PHP_addons +fi + +# JDK +case "${jdk_option}" in + 1) + . include/openjdk-8.sh + Install_OpenJDK8 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 2) + . include/openjdk-11.sh + Install_OpenJDK11 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 3) + . include/openjdk-17.sh + Install_OpenJDK17 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; +esac + +case "${tomcat_option}" in + 1) + . include/tomcat-10.sh + Install_Tomcat10 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 2) + . include/tomcat-9.sh + Install_Tomcat9 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 3) + . include/tomcat-8.sh + Install_Tomcat8 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; + 4) + . include/tomcat-7.sh + Install_Tomcat7 2>&1 | tee -a ${oneinstack_dir}/install.log + ;; +esac + +# Nodejs +if [ "${nodejs_flag}" == 'y' ]; then + . include/nodejs.sh + Install_Nodejs 2>&1 | tee -a ${oneinstack_dir}/install.log +fi + +# Pure-FTPd +if [ "${pureftpd_flag}" == 'y' ]; then + . include/pureftpd.sh + Install_PureFTPd 2>&1 | tee -a ${oneinstack_dir}/install.log +fi + +# phpMyAdmin +if [ "${phpmyadmin_flag}" == 'y' ]; then + . include/phpmyadmin.sh + Install_phpMyAdmin 2>&1 | tee -a ${oneinstack_dir}/install.log +fi + +# redis +if [ "${redis_flag}" == 'y' ]; then + . include/redis.sh + Install_redis_server 2>&1 | tee -a ${oneinstack_dir}/install.log +fi + +# memcached +if [ "${memcached_flag}" == 'y' ]; then + . include/memcached.sh + Install_memcached_server 2>&1 | tee -a ${oneinstack_dir}/install.log +fi + +# index example +if [ -d "${wwwroot_dir}/default" ]; then + . include/demo.sh + DEMO 2>&1 | tee -a ${oneinstack_dir}/install.log +fi + +# get web_install_dir and db_install_dir +. include/check_dir.sh + +# Starting DB +[ -d "/etc/mysql" ] && /bin/mv /etc/mysql{,_bk} +[ -d "${db_install_dir}/support-files" ] && [ -z "`ps -ef | grep mysqld_safe | grep -v grep`" ] && service mysqld start + +# reload php +[ -e "${php_install_dir}/sbin/php-fpm" ] && { [ -e "/bin/systemctl" ] && systemctl reload php-fpm || service php-fpm reload; } +[ -n "${mphp_ver}" -a -e "${php_install_dir}${mphp_ver}/sbin/php-fpm" ] && { [ -e "/bin/systemctl" ] && systemctl reload php${mphp_ver}-fpm || service php${mphp_ver}-fpm reload; } +[ -e "${apache_install_dir}/bin/apachectl" ] && ${apache_install_dir}/bin/apachectl -k graceful + +endTime=`date +%s` +((installTime=($endTime-$startTime)/60)) +echo "####################Congratulations########################" +echo "Total OneinStack Install Time: ${CQUESTION}${installTime}${CEND} minutes" +[[ "${nginx_option}" =~ ^[1-3]$ ]] && echo -e "\n$(printf "%-32s" "Nginx install dir":)${CMSG}${web_install_dir}${CEND}" +[ "${apache_flag}" == 'y' ] && echo -e "\n$(printf "%-32s" "Apache install dir":)${CMSG}${apache_install_dir}${CEND}" +[ "${caddy_flag}" == 'y' ] && echo -e "\n$(printf "%-32s" "Caddy install dir":)${CMSG}${caddy_install_dir}${CEND}" +[[ "${tomcat_option}" =~ ^[1-4]$ ]] && echo -e "\n$(printf "%-32s" "Tomcat install dir":)${CMSG}${tomcat_install_dir}${CEND}" +[[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]] && echo -e "\n$(printf "%-32s" "Database install dir:")${CMSG}${db_install_dir}${CEND}" +[[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]] && echo "$(printf "%-32s" "Database data dir:")${CMSG}${db_data_dir}${CEND}" +[[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]] && echo "$(printf "%-32s" "Database user:")${CMSG}root${CEND}" +[[ "${db_option}" =~ ^[1-9]$|^1[0-2]$ ]] && echo "$(printf "%-32s" "Database password:")${CMSG}${dbrootpwd}${CEND}" +[ "${db_option}" == '13' ] && echo -e "\n$(printf "%-32s" "PostgreSQL install dir:")${CMSG}${pgsql_install_dir}${CEND}" +[ "${db_option}" == '13' ] && echo "$(printf "%-32s" "PostgreSQL data dir:")${CMSG}${pgsql_data_dir}${CEND}" +[ "${db_option}" == '13' ] && echo "$(printf "%-32s" "PostgreSQL user:")${CMSG}postgres${CEND}" +[ "${db_option}" == '13' ] && echo "$(printf "%-32s" "postgres password:")${CMSG}${dbpostgrespwd}${CEND}" +[ "${db_option}" == '14' ] && echo -e "\n$(printf "%-32s" "MongoDB install dir:")${CMSG}${mongo_install_dir}${CEND}" +[ "${db_option}" == '14' ] && echo "$(printf "%-32s" "MongoDB data dir:")${CMSG}${mongo_data_dir}${CEND}" +[ "${db_option}" == '14' ] && echo "$(printf "%-32s" "MongoDB user:")${CMSG}root${CEND}" +[ "${db_option}" == '14' ] && echo "$(printf "%-32s" "MongoDB password:")${CMSG}${dbmongopwd}${CEND}" +[[ "${php_option}" =~ ^[1-9]$|^1[0-2]$ ]] && echo -e "\n$(printf "%-32s" "PHP install dir:")${CMSG}${php_install_dir}${CEND}" +[ "${phpcache_option}" == '1' ] && echo "$(printf "%-32s" "Opcache Control Panel URL:")${CMSG}http://${IPADDR}/ocp.php${CEND}" +[ "${phpcache_option}" == '2' ] && echo "$(printf "%-32s" "APC Control Panel URL:")${CMSG}http://${IPADDR}/apc.php${CEND}" +[ "${phpcache_option}" == '3' -a -e "${php_install_dir}/etc/php.d/04-xcache.ini" ] && echo "$(printf "%-32s" "xcache Control Panel URL:")${CMSG}http://${IPADDR}/xcache${CEND}" +[ "${phpcache_option}" == '3' -a -e "${php_install_dir}/etc/php.d/04-xcache.ini" ] && echo "$(printf "%-32s" "xcache user:")${CMSG}admin${CEND}" +[ "${phpcache_option}" == '3' -a -e "${php_install_dir}/etc/php.d/04-xcache.ini" ] && echo "$(printf "%-32s" "xcache password:")${CMSG}${xcachepwd}${CEND}" +[ "${phpcache_option}" == '4' -a -e "${php_install_dir}/etc/php.d/02-eaccelerator.ini" ] && echo "$(printf "%-32s" "eAccelerator Control Panel URL:")${CMSG}http://${IPADDR}/control.php${CEND}" +[ "${phpcache_option}" == '4' -a -e "${php_install_dir}/etc/php.d/02-eaccelerator.ini" ] && echo "$(printf "%-32s" "eAccelerator user:")${CMSG}admin${CEND}" +[ "${phpcache_option}" == '4' -a -e "${php_install_dir}/etc/php.d/02-eaccelerator.ini" ] && echo "$(printf "%-32s" "eAccelerator password:")${CMSG}eAccelerator${CEND}" +[ "${pureftpd_flag}" == 'y' ] && echo -e "\n$(printf "%-32s" "Pure-FTPd install dir:")${CMSG}${pureftpd_install_dir}${CEND}" +[ "${pureftpd_flag}" == 'y' ] && echo "$(printf "%-32s" "Create FTP virtual script:")${CMSG}./pureftpd_vhost.sh${CEND}" +[ "${phpmyadmin_flag}" == 'y' ] && echo -e "\n$(printf "%-32s" "phpMyAdmin dir:")${CMSG}${wwwroot_dir}/default/phpMyAdmin${CEND}" +[ "${phpmyadmin_flag}" == 'y' ] && echo "$(printf "%-32s" "phpMyAdmin Control Panel URL:")${CMSG}http://${IPADDR}/phpMyAdmin${CEND}" +[ "${redis_flag}" == 'y' ] && echo -e "\n$(printf "%-32s" "redis install dir:")${CMSG}${redis_install_dir}${CEND}" +[ "${memcached_flag}" == 'y' ] && echo -e "\n$(printf "%-32s" "memcached install dir:")${CMSG}${memcached_install_dir}${CEND}" +if [[ ${nginx_option} =~ ^[1-4]$ ]] || [ "${apache_flag}" == 'y' ] || [[ ${tomcat_option} =~ ^[1-4]$ ]]; then + echo -e "\n$(printf "%-32s" "Index URL:")${CMSG}http://${IPADDR}/${CEND}" +fi +if [ ${ARG_NUM} == 0 ]; then + while :; do echo + echo "${CMSG}Please restart the server and see if the services start up fine.${CEND}" + read -e -p "Do you want to restart OS ? [y/n]: " reboot_flag + if [[ ! "${reboot_flag}" =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done +fi +[ "${reboot_flag}" == 'y' ] && reboot diff --git a/options.conf b/options.conf new file mode 100644 index 0000000..adf8e1a --- /dev/null +++ b/options.conf @@ -0,0 +1,104 @@ +# mirror link +mirror_link=https://mirrors.oneinstack.com + +# set the default timezone +timezone=Asia/Shanghai + +# Nginx Apache and PHP-FPM process is run as $run_user(Default "www"), you can freely specify +run_user=www +# Nginx Apache and PHP-FPM process is run as $run_group(Default "www"), you can freely specify +run_group=www + +# set the default install path, you can freely specify +nginx_install_dir=/usr/local/nginx +tengine_install_dir=/usr/local/tengine +openresty_install_dir=/usr/local/openresty +caddy_install_dir=/usr/local/caddy +apache_install_dir=/usr/local/apache +tomcat_install_dir=/usr/local/tomcat + +mysql_install_dir=/usr/local/mysql +mariadb_install_dir=/usr/local/mariadb +percona_install_dir=/usr/local/percona +pgsql_install_dir=/usr/local/pgsql +mongo_install_dir=/usr/local/mongodb + +php_install_dir=/usr/local/php + +nodejs_install_dir=/usr/local/node + +pureftpd_install_dir=/usr/local/pureftpd + +memcached_install_dir=/usr/local/memcached + +redis_install_dir=/usr/local/redis + +openssl_install_dir=/usr/local/openssl +imagick_install_dir=/usr/local/imagemagick +gmagick_install_dir=/usr/local/graphicsmagick +curl_install_dir=/usr/local/curl +freetype_install_dir=/usr/local/freetype + +apr_install_dir=/usr/local/apr + +# Add modules +nginx_modules_options='' +php_modules_options='' + +######################################################################### +# database data storage directory, you can freely specify +mysql_data_dir=/data/mysql +mariadb_data_dir=/data/mariadb +percona_data_dir=/data/percona +pgsql_data_dir=/data/pgsql +mongo_data_dir=/data/mongodb + +# web directory, you can customize +wwwroot_dir=/data/wwwroot + +# nginx Generate a log storage directory, you can freely specify. +wwwlogs_dir=/data/wwwlogs + +######################################################################### +# [MySQL/MariaDB/Percona] automatically generated, You can't change +dbrootpwd= + +# [PostgreSQL] automatically generated, You can't change +dbpostgrespwd= + +# [MongoDB] automatically generated, You can't change +dbmongopwd= + +######################################################################### +# Backup Dest directory, change this if you have someother location +backup_dir=/data/backup + +# How many days before the backup directory will be removed +expired_days=5 + +# local,remote,oss,cos,upyun,qiniu,s3,gdrive,dropbox +backup_destination= + +# db ; web, You can't change +backup_content= + +# aliyun OSS Bucket, You can't change +oss_bucket= + +# qcloud OSS Bucket, You can't change +cos_bucket= + +# qiniu Bucket, You can't change +qiniu_bucket= + +# Amazon S3 Bucket, You can't change +s3_bucket= + +# The backup of the database, You can't change +db_name= + +# The backup of the website, You can't change +website_name= + +# oneinstack.tar.gz md5, You can't change +oneinstack_md5= diff --git a/pureftpd_vhost.sh b/pureftpd_vhost.sh new file mode 100644 index 0000000..09d7a59 --- /dev/null +++ b/pureftpd_vhost.sh @@ -0,0 +1,271 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin +clear +printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# FTP virtual user account management # +# For more information please visit https://oneinstack.com # +####################################################################### +" +# Check if user is root +[ $(id -u) != "0" ] && { echo "${CFAILURE}Error: You must be root to run this script${CEND}"; exit 1; } + +oneinstack_dir=$(dirname "`readlink -f $0`") +pushd ${oneinstack_dir} > /dev/null +. ./options.conf +. ./include/color.sh + +[ ! -d "${pureftpd_install_dir}" ] && { echo "${CFAILURE}FTP server does not exist! ${CEND}"; exit 1; } + +FTP_conf=${pureftpd_install_dir}/etc/pure-ftpd.conf +FTP_tmp_passfile=${pureftpd_install_dir}/etc/pureftpd_psss.tmp +Puredbfile=${pureftpd_install_dir}/etc/pureftpd.pdb +Passwdfile=${pureftpd_install_dir}/etc/pureftpd.passwd +FTP_bin=${pureftpd_install_dir}/bin/pure-pw +[ -z "`grep ^PureDB ${FTP_conf}`" ] && { echo "${CFAILURE}pure-ftpd is not own password database${CEND}" ; exit 1; } + +ARG_NUM=$# +Show_Help() { + echo + echo "Usage: $0 command ...[parameters].... + --help, -h Show this help message + --useradd,--add Add username + --usermod Modify directory + --passwd Modify password + --userdel,--delete Delete User + --listalluser,--list List all User + --showuser List User details + --username,-u [ftp username] Ftp username + --password,-p [ftp password] Ftp password + --directory,-d,-D [ftp directory] Ftp home directory + " +} + +TEMP=`getopt -o hu:p:d:D: --long help,useradd,add,usermod,passwd,userdel,delete,listalluser,list,showuser,username:,password:,directory: -- "$@" 2>/dev/null` +[ $? != 0 ] && echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 +eval set -- "${TEMP}" +while :; do + [ -z "$1" ] && break; + case "$1" in + -h|--help) + Show_Help; exit 0 + ;; + --add|--useradd) + useradd_flag=y; shift 1 + ;; + --usermod) + usermod_flag=y; shift 1 + ;; + --passwd) + passwd_flag=y; shift 1 + ;; + --delete|--userdel) + userdel_flag=y; shift 1 + ;; + --list|--listalluser) + listalluser_flag=y; shift 1 + ;; + --showuser) + showuser_flag=y; shift 1 + ;; + -u|--username) + username_flag=y; User=$2; shift 2 + ;; + -p|--password) + password_flag=y; Password=$2; shift 2 + ;; + -d|-D|--directory) + directory_flag=y; Directory=$2; shift 2 + ;; + --) + shift + ;; + *) + echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 + ;; + esac +done + +USER() { + while :; do + if [ "${username_flag}" != 'y' ]; then + echo + read -e -p "Please input a username: " User + fi + if [ -z "${User}" ]; then + echo "${CWARNING}username can't be NULL! ${CEND}" + else + break + fi + done +} + +PASSWORD() { + while :; do + if [ "${password_flag}" != 'y' ]; then + echo + read -e -p "Please input the password: " Password + fi + [ -n "`echo ${Password} | grep '[+|&]'`" ] && { echo "${CWARNING}input error,not contain a plus sign (+) and &${CEND}"; continue; } + if (( ${#Password} >= 5 )); then + echo -e "${Password}\n${Password}" > ${FTP_tmp_passfile} + break + else + echo "${CWARNING}Ftp password least 5 characters! ${CEND}" + fi + done +} + +DIRECTORY() { + while :; do + if [ "${directory_flag}" != 'y' ]; then + echo + read -e -p "Please input the directory(Default directory: ${wwwroot_dir}): " Directory + fi + Directory=${Directory:-${wwwroot_dir}} + if [ ! -d "${Directory}" ]; then + echo "${CWARNING}The directory does not exist${CEND}" + else + break + fi + done +} + +UserAdd() { + USER + [ -e "${Passwdfile}" ] && [ -n "`grep ^${User}: ${Passwdfile}`" ] && { echo "${CQUESTION}[${User}] is already existed! ${CEND}"; exit 1; } + PASSWORD;DIRECTORY + ${FTP_bin} useradd ${User} -f ${Passwdfile} -u ${run_user} -g ${run_group} -d ${Directory} -m < ${FTP_tmp_passfile} + ${FTP_bin} mkdb ${Puredbfile} -f ${Passwdfile} > /dev/null 2>&1 + echo "#####################################" + echo + echo "[${User}] create successful! " + echo + echo "You user name is : ${CMSG}${User}${CEND}" + echo "You Password is : ${CMSG}${Password}${CEND}" + echo "You directory is : ${CMSG}${Directory}${CEND}" + echo +} + +UserMod() { + USER + [ -e "${Passwdfile}" ] && [ -z "`grep ^${User}: ${Passwdfile}`" ] && { echo "${CQUESTION}[${User}] was not existed! ${CEND}"; exit 1; } + DIRECTORY + ${FTP_bin} usermod ${User} -f ${Passwdfile} -d ${Directory} -m + ${FTP_bin} mkdb ${Puredbfile} -f ${Passwdfile} > /dev/null 2>&1 + echo "#####################################" + echo + echo "[${User}] modify a successful! " + echo + echo "You user name is : ${CMSG}${User}${CEND}" + echo "You new directory is : ${CMSG}${Directory}${CEND}" + echo +} + +UserPasswd() { + USER + [ -e "${Passwdfile}" ] && [ -z "`grep ^${User}: ${Passwdfile}`" ] && { echo "${CQUESTION}[${User}] was not existed! ${CEND}"; exit 1; } + PASSWORD + ${FTP_bin} passwd ${User} -f ${Passwdfile} -m < ${FTP_tmp_passfile} + ${FTP_bin} mkdb ${Puredbfile} -f ${Passwdfile} > /dev/null 2>&1 + echo "#####################################" + echo + echo "[${User}] Password changed successfully! " + echo + echo "You user name is : ${CMSG}${User}${CEND}" + echo "You new password is : ${CMSG}${Password}${CEND}" + echo +} + +UserDel() { + if [ ! -e "${Passwdfile}" ]; then + echo "${CQUESTION}User was not existed! ${CEND}" + else + ${FTP_bin} list + fi + + USER + [ -e "${Passwdfile}" ] && [ -z "`grep ^${User}: ${Passwdfile}`" ] && { echo "${CQUESTION}[${User}] was not existed! ${CEND}"; exit 1; } + ${FTP_bin} userdel ${User} -f ${Passwdfile} -m + ${FTP_bin} mkdb ${Puredbfile} -f ${Passwdfile} > /dev/null 2>&1 + echo + echo "[${User}] have been deleted! " +} + +ListAllUser() { + if [ ! -e "${Passwdfile}" ]; then + echo "${CQUESTION}User was not existed! ${CEND}" + else + ${FTP_bin} list + fi +} + +ShowUser() { + USER + [ -e "${Passwdfile}" ] && [ -z "`grep ^${User}: ${Passwdfile}`" ] && { echo "${CQUESTION}[${User}] was not existed! ${CEND}"; exit 1; } + ${FTP_bin} show ${User} +} + +Menu() { + while :; do + printf " +What Are You Doing? +\t${CMSG}1${CEND}. UserAdd +\t${CMSG}2${CEND}. UserMod +\t${CMSG}3${CEND}. UserPasswd +\t${CMSG}4${CEND}. UserDel +\t${CMSG}5${CEND}. ListAllUser +\t${CMSG}6${CEND}. ShowUser +\t${CMSG}q${CEND}. Exit +" + read -e -p "Please input the correct option: " Number + if [[ ! ${Number} =~ ^[1-6,q]$ ]]; then + echo "${CFAILURE}input error! Please only input 1~6 and q${CEND}" + else + case "${Number}" in + 1) + UserAdd + ;; + 2) + UserMod + ;; + 3) + UserPasswd + ;; + 4) + UserDel + ;; + 5) + ListAllUser + ;; + 6) + ShowUser + ;; + q) + exit + ;; + esac + fi + done +} + +if [ ${ARG_NUM} == 0 ]; then + Menu +else + [ "${useradd_flag}" == 'y' ] && UserAdd + [ "${usermod_flag}" == 'y' ] && UserMod + [ "${passwd_flag}" == 'y' ] && UserPasswd + [ "${userdel_flag}" == 'y' ] && UserDel + [ "${listalluser_flag}" == 'y' ] && ListAllUser + [ "${showuser_flag}" == 'y' ] && ShowUser +fi diff --git a/reset_db_root_password.sh b/reset_db_root_password.sh new file mode 100644 index 0000000..ef86110 --- /dev/null +++ b/reset_db_root_password.sh @@ -0,0 +1,145 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin +clear +printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# Reset Database root password for OneinStack # +# For more information please visit https://oneinstack.com # +####################################################################### +" +oneinstack_dir=$(dirname "`readlink -f $0`") +pushd ${oneinstack_dir} > /dev/null +. ./options.conf +. ./include/color.sh +. ./include/check_dir.sh +[ ! -d "${db_install_dir}" ] && { echo "${CFAILURE}Database is not installed on your system! ${CEND}"; exit 1; } + +Show_Help() { + echo "Usage: $0 command ...[parameters].... + -h, --help print this help. + -q, --quiet quiet operation. + -f, --force Lost Database Password? Forced reset password. + -p, --password [pass] DB super password. + " +} + +New_dbrootpwd="`< /dev/urandom tr -dc A-Za-z0-9 | head -c8`" +TEMP=`getopt -o hqfp: --long help,quiet,force,password: -- "$@" 2>/dev/null` +[ $? != 0 ] && echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 +eval set -- "${TEMP}" +while :; do + [ -z "$1" ] && break; + case "$1" in + -h|--help) + Show_Help; exit 0 + ;; + -q|--quiet) + quiet_flag=y; shift 1 + ;; + -f|--force) + force_flag=y; shift 1 + ;; + -p|--password) + New_dbrootpwd=$2; shift 2 + password_flag=y + ;; + --) + shift + ;; + *) + echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 + ;; + esac +done + +Input_dbrootpwd() { + while :; do echo + read -e -p "Please input the root password of database: " New_dbrootpwd + [ -n "`echo ${New_dbrootpwd} | grep '[+|&]'`" ] && { echo "${CWARNING}input error,not contain a plus sign (+) and &${CEND}"; continue; } + (( ${#New_dbrootpwd} >= 5 )) && break || echo "${CWARNING}database root password least 5 characters! ${CEND}" + done +} + +Reset_Interaction_dbrootpwd() { + ${db_install_dir}/bin/mysqladmin -uroot -p"${dbrootpwd}" password "${New_dbrootpwd}" -h localhost > /dev/null 2>&1 + status_Localhost=`echo $?` + ${db_install_dir}/bin/mysqladmin -uroot -p"${dbrootpwd}" password "${New_dbrootpwd}" -h 127.0.0.1 > /dev/null 2>&1 + status_127=`echo $?` + if [ ${status_Localhost} == '0' -a ${status_127} == '0' ]; then + sed -i "s+^dbrootpwd.*+dbrootpwd='${New_dbrootpwd}'+" ./options.conf + echo + echo "Password reset succesfully! " + echo "The new password: ${CMSG}${New_dbrootpwd}${CEND}" + echo + else + echo "${CFAILURE}Reset Database root password failed! ${CEND}" + fi +} + +Reset_force_dbrootpwd() { + DB_Ver="`${db_install_dir}/bin/mysql_config --version`" + echo "${CMSG}Stopping MySQL...${CEND}" + service mysqld stop > /dev/null 2>&1 + while [ -n "`ps -ef | grep mysqld | grep -v grep | awk '{print $2}'`" ]; do + sleep 1 + done + echo "${CMSG}skip grant tables...${CEND}" + sed -i '/\[mysqld\]/a\skip-grant-tables' /etc/my.cnf + service mysqld start > /dev/null 2>&1 + sed -i '/^skip-grant-tables/d' /etc/my.cnf + while [ -z "`ps -ef | grep 'mysqld ' | grep -v grep | awk '{print $2}'`" ]; do + sleep 1 + done + if echo "${DB_Ver}" | grep -Eqi '^8.0.|^5.7.|^10.[4-5].|^10.11.'; then + ${db_install_dir}/bin/mysql -uroot -hlocalhost << EOF +update mysql.user set authentication_string=password("${New_dbrootpwd}") where user="root"; +flush privileges; +EOF + else + ${db_install_dir}/bin/mysql -uroot -hlocalhost << EOF +update mysql.user set password = Password("${New_dbrootpwd}") where User = 'root'; +EOF + fi + if [ $? -eq 0 ]; then + killall mysqld + while [ -n "`ps -ef | grep mysqld | grep -v grep | awk '{print $2}'`" ]; do + sleep 1 + done + [ -n "`ps -ef | grep mysqld | grep -v grep | awk '{print $2}'`" ] && ps -ef | grep mysqld | grep -v grep | awk '{print $2}' | xargs kill -9 > /dev/null 2>&1 + service mysqld start > /dev/null 2>&1 + sed -i "s+^dbrootpwd.*+dbrootpwd='${New_dbrootpwd}'+" ./options.conf + [ -e ~/ReadMe ] && sed -i "s+^MySQL root password:.*+MySQL root password: ${New_dbrootpwd}+" ~/ReadMe + echo + echo "Password reset succesfully! " + echo "The new password: ${CMSG}${New_dbrootpwd}${CEND}" + echo + fi +} + +[ "${password_flag}" == 'y' ] && quiet_flag=y +if [ "${quiet_flag}" == 'y' ]; then + if [ "${force_flag}" == 'y' ]; then + Reset_force_dbrootpwd + else + sleep 2 && [ ! -e /tmp/mysql.sock ] && service mysqld start + Reset_Interaction_dbrootpwd + fi +else + Input_dbrootpwd + if [ "${force_flag}" == 'y' ]; then + Reset_force_dbrootpwd + else + Reset_Interaction_dbrootpwd + fi +fi +popd > /dev/null diff --git a/src/adoptium.key b/src/adoptium.key new file mode 100644 index 0000000..7d76f7a --- /dev/null +++ b/src/adoptium.key @@ -0,0 +1,31 @@ +-----BEGIN PGP PUBLIC KEY BLOCK----- + +mQENBGGTvTQBCAC6ey144n7CG8foafF6mwgIBN1fIm1ILZDuGS4tMr0/XI8pgJnT +QvsPxZWEvtSm7bEMObzEoZJcXwjBcJl1B0ui8k5kHMTI75gCmZPsoKLFWIEpuRBQ +PBocusw80apDmLnNDQLVQvDFtEua5gaNa/fRw9YsmBoXBqvgrjFUIdGyWoQvH5+a +9OYlWD9n5VV0gnVMb+aclwVzB/zJw3kHGSgzuMtlAHeQiah7Y8yomQn/UIX8yqDf ++11sP3+c87YcjkRqImRTtmKEDcEtGPAIXC6SYA+uEEkbYE0Fy0chkvtnVWJ597fa +Epai4rnICU8zoJ6X5z3v1aM2WerhX9oq9X8PABEBAAG0QEFkb3B0aXVtIEdQRyBL +ZXkgKERFQi9SUE0gU2lnbmluZyBLZXkpIDx0ZW11cmluLWRldkBlY2xpcHNlLm9y +Zz6JAVIEEwEIADwWIQQ7BNdTyQUNml00PzmEPEilZfjwSwUCYZO9NAIbAwULCQgH +AgMiAgEGFQoJCAsCBBYCAwECHgcCF4AACgkQhDxIpWX48Et4AggAjjJzYWuKV3nG +7ngInngl8G/m9JoHr7BmwgcQXYhdy5hVkMcUx5JLeXz2LMBUH/F2nD595hgjMabk +kVib20X8lq9RsNbdfc2hBcWU6qyHKxsIqT4boI2/XDyEzzMyyZWWNGo/27Ci7Xmj +pWu31nh0pDdPqdyWDIKojbVVnxlCRY8as8Sm+1ufi709KCi4MuwHNsUlCSwb/fju +NKeHkrHbLcHKUUIEcmTSKRWrpMYBzm1HYOGBz4xPuELwUfUp71ehfoyBZlp6RDRf +l5TYI1FmCyHuvjNhrJgWv7bOTcf8yObGY+TEUhzc4xQqCrF4ur9d3opvsuPBQsv+ +Klqi5KSZgrkBDQRhk700AQgAq14okly8cFrpYVenEQPiB75AUZfKRpMduiR6IxAj +SKcH7aSoFZ9AubUEBVpZsyT5svxoEPe1i4TdbF+m9FGy42EcOlLa3ArLTj5H8FRl +UdGZB9I5mk4GptOzPM+aHMMu92vW/ZwjuS8DvOiQSp+cUmG1EqOMJSM7e/4BM71z +E+OKaVJCj79pEzhG3SK/IC/OlxxyETT66NSfYJd7Sw5R6Vr19am/uNU690W0CJ+q +VQeFpmDMr7LnfdFRIh+lJe05+PvWXeidkGjox5cbG52wf8aRIR/FgkfcFvqRMN1f +B+dVOWueloUeVAnzcUznOKmUEs7LP9ObJhYHHgup4IAU2wARAQABiQE2BBgBCAAg +FiEEOwTXU8kFDZpdND85hDxIpWX48EsFAmGTvTQCGwwACgkQhDxIpWX48EvXHQf/ +Q0nZsGDXnZHiBoojeSdpkO7WBjMIP3w1GdLvRpPQrS8TfOPbZuoevzCNh38Y3gwF +yelJspvzDQrBXhgkzAGlucYg8Y7KHa5Ebm7iDgMzc37L1hYSZTYCqwd7aowfgy34 +hOk3B67LffkJpIh738Oa9CtlwxQ9xcytmBmQ1fBBOwm/9IhAwHPQuydYIs4DxWbj +0MGSP4fDntU7e4UjsHNmhudDcYol0FaqdHHIIB9C/G4CzetRwHFOn3b4JwXMU7YU +6aJA3mXhi3hggMC3wkT2HHZ/TquuOdNc02fypWOCDOHz0alBBJNqoVUNFNqU3tfJ +wI4qF/KKq9BfyfucAs0ykA== +=szki +-----END PGP PUBLIC KEY BLOCK----- \ No newline at end of file diff --git a/src/libiconv-glibc-2.16.patch b/src/libiconv-glibc-2.16.patch new file mode 100644 index 0000000..1703cb8 --- /dev/null +++ b/src/libiconv-glibc-2.16.patch @@ -0,0 +1,11 @@ +--- srclib/stdio.in.h.orig 2011-08-07 16:42:06.000000000 +0300 ++++ srclib/stdio.in.h 2013-01-10 15:53:03.000000000 +0200 +@@ -695,7 +695,9 @@ + /* It is very rare that the developer ever has full control of stdin, + so any use of gets warrants an unconditional warning. Assume it is + always declared, since it is required by C89. */ +-_GL_WARN_ON_USE (gets, "gets is a security hole - use fgets instead"); ++#if defined(__GLIBC__) && !defined(__UCLIBC__) && !__GLIBC_PREREQ(2, 16) ++ _GL_WARN_ON_USE (gets, "gets is a security hole - use fgets instead"); ++#endif + #endif diff --git a/src/libmemcached-build.patch b/src/libmemcached-build.patch new file mode 100644 index 0000000..df58c9f --- /dev/null +++ b/src/libmemcached-build.patch @@ -0,0 +1,21 @@ +diff -up ./clients/memflush.cc.old ./clients/memflush.cc +--- ./clients/memflush.cc.old 2017-02-12 10:12:59.615209225 +0100 ++++ ./clients/memflush.cc 2017-02-12 10:13:39.998382783 +0100 +@@ -39,7 +39,7 @@ int main(int argc, char *argv[]) + { + options_parse(argc, argv); + +- if (opt_servers == false) ++ if (!opt_servers) + { + char *temp; + +@@ -48,7 +48,7 @@ int main(int argc, char *argv[]) + opt_servers= strdup(temp); + } + +- if (opt_servers == false) ++ if (!opt_servers) + { + std::cerr << "No Servers provided" << std::endl; + exit(EXIT_FAILURE); diff --git a/src/php5.3patch b/src/php5.3patch new file mode 100644 index 0000000..73a375f --- /dev/null +++ b/src/php5.3patch @@ -0,0 +1,80 @@ +diff --git a/main/rfc1867.c b/main/rfc1867.c +index b3f94ec..7613119 100644 +--- a/main/rfc1867.c ++++ b/main/rfc1867.c +@@ -33,6 +33,8 @@ + #include "php_variables.h" + #include "rfc1867.h" + #include "ext/standard/php_string.h" ++#include "ext/standard/php_smart_str.h" ++ + + #define DEBUG_FILE_UPLOAD ZEND_DEBUG + +@@ -462,6 +464,66 @@ static int find_boundary(multipart_buffer *self, char *boundary TSRMLS_DC) + static int multipart_buffer_headers(multipart_buffer *self, zend_llist *header TSRMLS_DC) + { + char *line; ++ mime_header_entry entry = {0}; ++ smart_str buf_value = {0}; ++ char *key = NULL; ++ ++ /* didn't find boundary, abort */ ++ if (!find_boundary(self, self->boundary TSRMLS_CC)) { ++ return 0; ++ } ++ ++ /* get lines of text, or CRLF_CRLF */ ++ ++ while( (line = get_line(self TSRMLS_CC)) && line[0] != '\0' ) ++ { ++ /* add header to table */ ++ char *value = NULL; ++ ++ /*if (php_rfc1867_encoding_translation(TSRMLS_C)) { ++ //self->input_encoding = zend_multibyte_encoding_detector((unsigned char *)line, strlen(line), self->detect_order, self->detect_order_size TSRMLS_CC); ++ }*/ ++ ++ /* space in the beginning means same header */ ++ if (!isspace(line[0])) { ++ value = strchr(line, ':'); ++ } ++ ++ if (value) { ++ if(buf_value.c && key) { ++ /* new entry, add the old one to the list */ ++ smart_str_0(&buf_value); ++ entry.key = key; ++ entry.value = buf_value.c; ++ zend_llist_add_element(header, &entry); ++ buf_value.c = NULL; ++ key = NULL; ++ } ++ ++ *value = '\0'; ++ do { value++; } while(isspace(*value)); ++ ++ key = estrdup(line); ++ smart_str_appends(&buf_value, value); ++ } else if (buf_value.c) { /* If no ':' on the line, add to previous line */ ++ smart_str_appends(&buf_value, line); ++ } else { ++ continue; ++ } ++ } ++ if(buf_value.c && key) { ++ /* add the last one to the list */ ++ smart_str_0(&buf_value); ++ entry.key = key; ++ entry.value = buf_value.c; ++ zend_llist_add_element(header, &entry); ++ } ++ ++ return 1; ++} ++static int multipart_buffer_headers_bak(multipart_buffer *self, zend_llist *header TSRMLS_DC) ++{ ++ char *line; + mime_header_entry prev_entry, entry; + int prev_len, cur_len; + diff --git a/tools/db_bk.sh b/tools/db_bk.sh new file mode 100644 index 0000000..d85aff9 --- /dev/null +++ b/tools/db_bk.sh @@ -0,0 +1,41 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +. ../options.conf +. ../include/check_dir.sh + +DBname=$1 +LogFile=${backup_dir}/db.log +DumpFile=${backup_dir}/DB_${DBname}_$(date +%Y%m%d_%H%M%S).sql +NewFile=${backup_dir}/DB_${DBname}_$(date +%Y%m%d_%H%M%S).tgz +OldFile=${backup_dir}/DB_${DBname}_$(date +%Y%m%d --date="${expired_days} days ago")*.tgz + +[ ! -e "${backup_dir}" ] && mkdir -p ${backup_dir} + +DB_tmp=`${db_install_dir}/bin/mysql -uroot -p${dbrootpwd} -e "show databases\G" | grep ${DBname}` +[ -z "${DB_tmp}" ] && { echo "[${DBname}] not exist" >> ${LogFile} ; exit 1 ; } + +if [ -n "`ls ${OldFile} 2>/dev/null`" ]; then + rm -f ${OldFile} + echo "[${OldFile}] Delete Old File Success" >> ${LogFile} +else + echo "[${OldFile}] Delete Old Backup File" >> ${LogFile} +fi + +if [ -e "${NewFile}" ]; then + echo "[${NewFile}] The Backup File is exists, Can't Backup" >> ${LogFile} +else + ${db_install_dir}/bin/mysqldump -uroot -p${dbrootpwd} --databases ${DBname} > ${DumpFile} + pushd ${backup_dir} > /dev/null + tar czf ${NewFile} ${DumpFile##*/} >> ${LogFile} 2>&1 + echo "[${NewFile}] Backup success ">> ${LogFile} + rm -f ${DumpFile} + popd > /dev/null +fi diff --git a/tools/mabs.sh b/tools/mabs.sh new file mode 100644 index 0000000..c386a99 --- /dev/null +++ b/tools/mabs.sh @@ -0,0 +1,168 @@ +#!/bin/bash +# Author: yeho +# Blog: http://linuxeye.com + +###################### proc defination ######################## +# ignore rule +ignore_init() { + # ignore password + array_ignore_pwd_length=0 + if [ -f ./ignore_pwd ]; then + while read IGNORE_PWD + do + array_ignore_pwd[$array_ignore_pwd_length]=$IGNORE_PWD + let array_ignore_pwd_length=$array_ignore_pwd_length+1 + done < ./ignore_pwd + fi + + # ignore ip address + array_ignore_ip_length=0 + if [ -f ./ignore_ip ]; then + while read IGNORE_IP + do + array_ignore_ip[$array_ignore_ip_length]=$IGNORE_IP + let array_ignore_ip_length=$array_ignore_ip_length+1 + done < ./ignore_ip + fi +} + +show_ver() { + echo "version: 1.0" + echo "updated date: 2014-06-08" +} + +show_usage() { + echo -e "`printf %-16s "Usage: $0"` [-h|--help]" + echo -e "`printf %-16s ` [-v|-V|--version]" + echo -e "`printf %-16s ` [-l|--iplist ... ]" + echo -e "`printf %-16s ` [-c|--config ... ]" + echo -e "`printf %-16s ` [-t|--sshtimeout ... ]" + echo -e "`printf %-16s ` [-T|--fttimeout ... ]" + echo -e "`printf %-16s ` [-L|--bwlimit ... ]" + echo -e "`printf %-16s ` [-n|--ignore]" +} + +IPLIST="iplist.txt" +CONFIG_FILE="config.txt" +IGNRFLAG="noignr" +SSHTIMEOUT=100 +SCPTIMEOUT=2000 +BWLIMIT=1024000 +[ ! -e 'logs' ] && mkdir logs + +TEMP=`getopt -o hvVl:c:t:T:L:n --long help,version,iplist:,config:,sshtimeout:,fttimeout:,bwlimit:,log:,ignore -- "$@" 2>/dev/null` + +[ $? != 0 ] && echo -e "\033[31mERROR: unknown argument! \033[0m\n" && show_usage && exit 1 + +eval set -- "$TEMP" + +while :; do + [ -z "$1" ] && break; + case "$1" in + -h|--help) + show_usage; exit 0 + ;; + -v|-V|--version) + show_ver; exit 0 + ;; + -l|--iplist) + IPLIST=$2; shift 2 + ;; + -c|--config) + CONFIG_FILE=$2; shift 2 + ;; + -t|--sshtimeout) + SSHTIMEOUT=$2; shift 2 + ;; + -T|--fttimeout) + SCPTIMEOUT=$2; shift 2 + ;; + -L|--bwlimit) + BWLIMIT=$2; shift 2 + ;; + --log) + LOG_FILE=$2; shift 2 + ;; + -n|--ignore) + IGNRFLAG="ignr"; shift + ;; + --) + shift + ;; + *) + echo -e "\033[31mERROR: unknown argument! \033[0m\n" && show_usage && exit 1 + ;; + esac +done + +################ main ####################### +BEGINDATETIME=`date "+%F %T"` +[ ! -f $IPLIST ] && echo -e "\033[31mERROR: iplist \"$IPLIST\" not exists, please check! \033[0m\n" && exit 1 + +[ ! -f $CONFIG_FILE ] && echo -e "\033[31mERROR: config \"$CONFIG_FILE\" not exists, please check! \033[0m\n" && exit 1 + +IP_count=$(egrep -v '^#|^$' $IPLIST|wc -l) +IP_init=1 +while [[ $IP_init -le $IP_count ]] +do + egrep -v '^#|^$' $IPLIST | sed -n "$IP_init,$(expr $IP_init + 50)p" > $IPLIST.tmp + + IPSEQ=0 + + while read IP PORT USER PASSWD PASSWD_2ND PASSWD_3RD PASSWD_4TH OTHERS + # while read Line + do + #[ -z "`echo $IP | grep -E '^[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}\.[0-9]{1,3}|CNS'`" ] && continue + if [ "$(../include/ois.${ARCH} conn_port --host ${IP} --port ${PORT})" == "false" ]; then + [ ! -e ipnologin.txt ] && > ipnologin.txt + [ -z "`grep $IP ipnologin.txt | grep $(date +%F)`" ] && echo "`date +%F_%H%M` $IP" >> ipnologin.txt + continue + fi + + #[ -e "~/.ssh/known_hosts" ] && grep $IP ~/.ssh/known_hosts | sed -i "/$IP/d" ~/.ssh/known_hosts + + let IPSEQ=$IPSEQ+1 + + if [ $IGNRFLAG == "ignr" ]; then + ignore_init + ignored_flag=0 + + i=0 + while [ $i -lt $array_ignore_pwd_length ] + do + [ ${PASSWD}x == ${array_ignore_pwd[$i]}x ] && ignored_flag=1 && break + let i=$i+1 + done + + [ $ignored_flag -eq 1 ] && continue + + j=0 + while [ $j -lt $array_ignore_ip_length ] + do + [ ${IP}x == ${array_ignore_ip[$j]}x ] && ignored_flag=1 && break + let j=$j+1 + done + + [ $ignored_flag -eq 1 ] && continue + fi + + PASSWD_USE=$PASSWD + + IPcode=$(echo "ibase=16;$(echo "$IP" | xxd -ps -u)"|bc|tr -d '\\'|tr -d '\n') + Portcode=$(echo "ibase=16;$(echo "$PORT" | xxd -ps -u)"|bc|tr -d '\\'|tr -d '\n') + #USER=$USER + PWcode=$(echo "ibase=16;$(echo "$PASSWD_USE" | xxd -ps -u)"|bc|tr -d '\\'|tr -d '\n') + Othercode=$(echo "ibase=16;$(echo "$OTHERS" | xxd -ps -u)"|bc|tr -d '\\'|tr -d '\n') + #echo $IPcode $Portcode $USER $PWcode $CONFIG_FILE $SSHTIMEOUT $SCPTIMEOUT $BWLIMIT $Othercode + ./thread.sh $IPcode $Portcode $USER $PWcode $CONFIG_FILE $SSHTIMEOUT $SCPTIMEOUT $BWLIMIT $Othercode | tee logs/$IP.log & + done < $IPLIST.tmp + sleep 3 + IP_init=$(expr $IP_init + 50) +done + +ENDDATETIME=`date "+%F %T"` + +echo "$BEGINDATETIME -- $ENDDATETIME" +echo "$0 $* --excutes over!" + +exit 0 diff --git a/tools/mscp.exp b/tools/mscp.exp new file mode 100644 index 0000000..3a93a04 --- /dev/null +++ b/tools/mscp.exp @@ -0,0 +1,158 @@ +#!/usr/bin/expect -- + +proc Usage_Exit {self} { + puts "" + puts "Usage: $self ip user passwd port sourcefile destdir direction bwlimit timeout" + puts "" + puts " sourcefile: a file or directory to be transferred" + puts " 需要拷贝目录时目录名后不要带 /, 否则会拷贝该目录下的所有文件" + puts " destdir: the location that the sourcefile to be put into" + puts " direction: pull or push" + puts " pull: remote -> local" + puts " push: local -> remote" + puts " bwlimit: bandwidth limit, kbit/s, 0 means no limit" + puts " timeout: timeout of expect, s, -1 means no timeout" + puts "" + exit 1 +} + +if { [llength $argv] < 9 } { + Usage_Exit $argv0 +} + +set ipcode [lindex $argv 0] +set ip [exec dc -e $ipcode] +set user [lindex $argv 1] +set passwduncode [lindex $argv 2] +set passwd [exec dc -e $passwduncode] +set portcode [lindex $argv 3] +set port [exec dc -e $portcode] +set sourcefile [lindex $argv 4] +set destdir [lindex $argv 5] +set direction [lindex $argv 6] +set bwlimit [lindex $argv 7] +set timeoutflag [lindex $argv 8] + +set yesnoflag 0 +set timeout $timeoutflag + +for {} {1} {} { + # for is only used to retry when "Interrupted system call" occured + + if { $direction == "pull" } { + + if { $bwlimit > 0 } { + spawn rsync -crazP --delete --bwlimit=$bwlimit -e "/usr/bin/ssh -o GSSAPIAuthentication=no -q -l$user -p$port" $ip:$sourcefile $destdir + } elseif { $bwlimit == 0 } { + spawn rsync -crazP --delete -e "/usr/bin/ssh -o GSSAPIAuthentication=no -q -l$user -p$port" $ip:$sourcefile $destdir + } else { + Usage_Exit $argv0 + } + + } elseif { $direction == "push" } { + + if { $bwlimit > 0 } { + spawn rsync -crazP --delete --bwlimit=$bwlimit -e "/usr/bin/ssh -o GSSAPIAuthentication=no -q -l$user -p$port" $sourcefile $ip:$destdir + } elseif { $bwlimit == 0 } { + spawn rsync -crazP --delete -e "/usr/bin/ssh -o GSSAPIAuthentication=no -q -l$user -p$port" $sourcefile $ip:$destdir + } else { + Usage_Exit $argv0 + } + + } else { + Usage_Exit $argv0 + } + + expect { + + "assword:" { + send "$passwd\r" + break; + } + + "yes/no" { + set yesnoflag 1 + send "yes\r" + break; + } + + "FATAL" { + puts "\nCONNECTERROR: $ip occur FATAL ERROR!!!\n" + exit 1 + } + + timeout { + puts "\nCONNECTERROR: $ip Logon timeout!!!\n" + exit 1 + } + + "No route to host" { + puts "\nCONNECTERROR: $ip No route to host!!!\n" + exit 1 + } + + "Connection Refused" { + puts "\nCONNECTERROR: $ip Connection Refused!!!\n" + exit 1 + } + + "Connection refused" { + puts "\nCONNECTERROR: $ip Connection Refused!!!\n" + exit 1 + } + + "Host key verification failed" { + puts "\nCONNECTERROR: $ip Host key verification failed!!!\n" + exit 1 + } + + "Illegal host key" { + puts "\nCONNECTERROR: $ip Illegal host key!!!\n" + exit 1 + } + + "Connection Timed Out" { + puts "\nCONNECTERROR: $ip Logon timeout!!!\n" + exit 1 + } + + "Interrupted system call" { + puts "\n$ip Interrupted system call!!!\n" + } + } + +} + +if { $yesnoflag == 1 } { + expect { + "assword:" { + send "$passwd\r" + } + + "yes/no)?" { + set yesnoflag 2 + send "yes\r" + } + } +} + +if { $yesnoflag == 2 } { + expect { + "assword:" { + send "$passwd\r" + } + } +} + +expect { + "assword:" { + send "$passwd\r" + puts "\nPASSWORDERROR: $ip Password error!!!\n" + exit 1 + } + + eof { + puts "OK_SCP: $ip\n" + exit 0; + } +} diff --git a/tools/mssh.exp b/tools/mssh.exp new file mode 100644 index 0000000..95eeb83 --- /dev/null +++ b/tools/mssh.exp @@ -0,0 +1,129 @@ +#!/usr/bin/expect -- + +if { [llength $argv] < 4 } { + puts "Usage: $argv0 ip user passwd port commands timeout" + exit 1 +} + +match_max 600000 + +set ipcode [lindex $argv 0] +set ip [exec dc -e $ipcode] +set user [lindex $argv 1] +set passwdcode [lindex $argv 2] +set passwd [exec dc -e $passwdcode] +set portcode [lindex $argv 3] +set port [exec dc -e $portcode] +set commands [lindex $argv 4] +set timeoutflag [lindex $argv 5] + +set yesnoflag 0 +set timeout $timeoutflag + + +for {} {1} {} { + # for is only used to retry when "Interrupted system call" occured + + spawn /usr/bin/ssh -o GSSAPIAuthentication=no -q -l$user -p$port $ip + + expect { + + "assword:" { + send "$passwd\r" + break; + } + + "yes/no)?" { + set yesnoflag 1 + send "yes\r" + break; + } + + "FATAL" { + puts "\nCONNECTERROR: $ip occur FATAL ERROR!!!\n" + exit 1 + } + + timeout { + puts "\nCONNECTERROR: $ip Logon timeout!!!\n" + exit 1 + } + + "No route to host" { + puts "\nCONNECTERROR: $ip No route to host!!!\n" + exit 1 + } + + "Connection Refused" { + puts "\nCONNECTERROR: $ip Connection Refused!!!\n" + exit 1 + } + + "Connection refused" { + puts "\nCONNECTERROR: $ip Connection Refused!!!\n" + exit 1 + } + + "Host key verification failed" { + puts "\nCONNECTERROR: $ip Host key verification failed!!!\n" + exit 1 + } + + "Illegal host key" { + puts "\nCONNECTERROR: $ip Illegal host key!!!\n" + exit 1 + } + + "Connection Timed Out" { + puts "\nCONNECTERROR: $ip Logon timeout!!!\n" + exit 1 + } + + "Interrupted system call" { + puts "\n$ip Interrupted system call!!!\n" + } + } +} + +if { $yesnoflag == 1 } { + expect { + "assword:" { + send "$passwd\r" + } + + "yes/no" { + set yesnoflag 2 + send "yes\r" + } + } +} + +if { $yesnoflag == 2 } { + expect { + "assword:" { + send "$passwd\r" + } + } +} + +expect { + "@" {send "$commands \r"} + "assword:" { + send "$passwd\r" + puts "\nPASSWORDERROR: $ip Password error!!!\n" + exit 1 + } +} + +expect { + "@" {send "sleep 1\r"} +} + +expect { + "@" {send "exit\r"} +} + +expect eof { + puts "OK_SSH: $ip\n" + exit 0; +} diff --git a/tools/thread.sh b/tools/thread.sh new file mode 100644 index 0000000..27fb0dd --- /dev/null +++ b/tools/thread.sh @@ -0,0 +1,46 @@ +#!/bin/bash +# Author: yeho +# Blog: http://linuxeye.com + +# Default Parameters +myIFS=":::" + +IP=$1P +PORT=$2P +USER=$3 +PASSWD=$4P +CONFIG_FILE=$5 +SSHTIMEOUT=$6 +SCPTIMEOUT=$7 +BWLIMIT=$8 + +while read eachline +do + [ -z "`echo $eachline | grep -E '^com|^file'`" ] && continue + + myKEYWORD=`echo $eachline | awk -F"$myIFS" '{ print $1 }'` + myCONFIGLINE=`echo $eachline | awk -F"$myIFS" '{ print $2 }'` + + if [ "$myKEYWORD"x == "file"x ]; then + SOURCEFILE=`echo $myCONFIGLINE | awk '{ print $1 }'` + DESTDIR=`echo $myCONFIGLINE | awk '{ print $2 }'` + DIRECTION=`echo $myCONFIGLINE | awk '{ print $3 }'` + ./mscp.exp $IP $USER $PASSWD $PORT $SOURCEFILE $DESTDIR $DIRECTION $BWLIMIT $SCPTIMEOUT + + [ $? -ne 0 ] && echo -e "\033[31mSCP Try Out All Password Failed\033[0m\n" + + elif [ "$myKEYWORD"x == "com"x ]; then + ./mssh.exp $IP $USER $PASSWD $PORT "${myCONFIGLINE}" $SSHTIMEOUT + [ $? -ne 0 ] && echo -e "\033[31mSSH Try Out All Password Failed\033[0m\n" + + else + echo "ERROR: configuration wrong! [$eachline] " + echo " where KEYWORD should not be [$myKEYWORD], but 'com' or 'file'" + echo " if you dont want to run it, you can comment it with '#'" + echo "" + exit + fi + +done < $CONFIG_FILE + +exit 0 diff --git a/tools/website_bk.sh b/tools/website_bk.sh new file mode 100644 index 0000000..653098f --- /dev/null +++ b/tools/website_bk.sh @@ -0,0 +1,38 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +. ../options.conf + +WebSite=$1 +LogFile=${backup_dir}/web.log +NewFile=${backup_dir}/Web_${WebSite}_$(date +%Y%m%d_%H).tgz +OldFile=${backup_dir}/Web_${WebSite}_$(date +%Y%m%d --date="${expired_days} days ago")*.tgz +[ ! -e "${backup_dir}" ] && mkdir -p ${backup_dir} +[ ! -e "${wwwroot_dir}/${WebSite}" ] && { echo "[${wwwroot_dir}/${WebSite}] not exist" >> ${LogFile} ; exit 1 ; } + +if [ `du -sm "${wwwroot_dir}/${WebSite}" | awk '{print $1}'` -lt 1024 ]; then + if [ -n "`ls ${OldFile} 2>/dev/null`" ]; then + rm -f ${OldFile} + echo "[${OldFile}] Delete Old File Success" >> ${LogFile} + else + echo "[${OldFile}] Delete Old Backup File" >> ${LogFile} + fi + + if [ -e "${NewFile}" ]; then + echo "[${NewFile}] The Backup File is exists, Can't Backup" >> ${LogFile} + else + pushd ${wwwroot_dir} > /dev/null + tar czf ${NewFile} ./${WebSite} >> ${LogFile} 2>&1 + echo "[${NewFile}] Backup success ">> ${LogFile} + popd > /dev/null + fi +else + rsync -crazP --delete ${wwwroot_dir}/${WebSite} ${backup_dir} +fi diff --git a/uninstall.sh b/uninstall.sh new file mode 100644 index 0000000..c38c842 --- /dev/null +++ b/uninstall.sh @@ -0,0 +1,739 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin +clear +printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# Uninstall OneinStack # +# For more information please visit https://oneinstack.com # +####################################################################### +" +# Check if user is root +[ $(id -u) != "0" ] && { echo "${CFAILURE}Error: You must be root to run this script${CEND}"; exit 1; } + +oneinstack_dir=$(dirname "`readlink -f $0`") +pushd ${oneinstack_dir} > /dev/null +. ./options.conf +. ./include/color.sh +. ./include/get_char.sh +. ./include/check_dir.sh + +Show_Help() { + echo + echo "Usage: $0 command ...[parameters].... + --help, -h Show this help message, More: https://oneinstack.com + --quiet, -q quiet operation + --all Uninstall All + --web Uninstall Nginx/Tengine/OpenResty/Apache/Tomcat/Caddy + --mysql Uninstall MySQL/MariaDB/Percona + --postgresql Uninstall PostgreSQL + --mongodb Uninstall MongoDB + --php Uninstall PHP (PATH: ${php_install_dir}) + --mphp_ver [53~83] Uninstall another PHP version (PATH: ${php_install_dir}\${mphp_ver}) + --allphp Uninstall all PHP + --phpcache Uninstall PHP opcode cache + --php_extensions [ext name] Uninstall PHP extensions, include zendguardloader,ioncube, + sourceguardian,imagick,gmagick,fileinfo,imap,ldap,calendar,phalcon, + yaf,yar,redis,memcached,memcache,mongodb,swoole,xdebug + --pureftpd Uninstall PureFtpd + --redis Uninstall Redis-server + --memcached Uninstall Memcached-server + --phpmyadmin Uninstall phpMyAdmin + --nodejs Uninstall Nodejs (PATH: ${nodejs_install_dir}) + " +} + +ARG_NUM=$# +TEMP=`getopt -o hvVq --long help,version,quiet,all,web,mysql,postgresql,mongodb,php,mphp_ver:,allphp,phpcache,php_extensions:,pureftpd,redis,memcached,phpmyadmin,nodejs -- "$@" 2>/dev/null` +[ $? != 0 ] && echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 +eval set -- "${TEMP}" +while :; do + [ -z "$1" ] && break; + case "$1" in + -h|--help) + Show_Help; exit 0 + ;; + -q|--quiet) + quiet_flag=y + uninstall_flag=y + shift 1 + ;; + --all) + all_flag=y + web_flag=y + mysql_flag=y + postgresql_flag=y + mongodb_flag=y + allphp_flag=y + nodejs_flag=y + pureftpd_flag=y + redis_flag=y + memcached_flag=y + phpmyadmin_flag=y + shift 1 + ;; + --web) + web_flag=y; shift 1 + ;; + --mysql) + mysql_flag=y; shift 1 + ;; + --postgresql) + postgresql_flag=y; shift 1 + ;; + --mongodb) + mongodb_flag=y; shift 1 + ;; + --php) + php_flag=y; shift 1 + ;; + --mphp_ver) + mphp_ver=$2; mphp_flag=y; shift 2 + [[ ! "${mphp_ver}" =~ ^5[3-6]$|^7[0-4]$|^8[0-1]$ ]] && { echo "${CWARNING}mphp_ver input error! Please only input number 53~81${CEND}"; exit 1; } + ;; + --allphp) + allphp_flag=y; shift 1 + ;; + --phpcache) + phpcache_flag=y; shift 1 + ;; + --php_extensions) + php_extensions=$2; shift 2 + [ -n "`echo ${php_extensions} | grep -w zendguardloader`" ] && pecl_zendguardloader=1 + [ -n "`echo ${php_extensions} | grep -w ioncube`" ] && pecl_ioncube=1 + [ -n "`echo ${php_extensions} | grep -w sourceguardian`" ] && pecl_sourceguardian=1 + [ -n "`echo ${php_extensions} | grep -w imagick`" ] && pecl_imagick=1 + [ -n "`echo ${php_extensions} | grep -w gmagick`" ] && pecl_gmagick=1 + [ -n "`echo ${php_extensions} | grep -w fileinfo`" ] && pecl_fileinfo=1 + [ -n "`echo ${php_extensions} | grep -w imap`" ] && pecl_imap=1 + [ -n "`echo ${php_extensions} | grep -w ldap`" ] && pecl_ldap=1 + [ -n "`echo ${php_extensions} | grep -w calendar`" ] && pecl_calendar=1 + [ -n "`echo ${php_extensions} | grep -w phalcon`" ] && pecl_phalcon=1 + [ -n "`echo ${php_extensions} | grep -w yaf`" ] && pecl_yaf=1 + [ -n "`echo ${php_extensions} | grep -w yar`" ] && pecl_yar=1 + [ -n "`echo ${php_extensions} | grep -w redis`" ] && pecl_redis=1 + [ -n "`echo ${php_extensions} | grep -w memcached`" ] && pecl_memcached=1 + [ -n "`echo ${php_extensions} | grep -w memcache`" ] && pecl_memcache=1 + [ -n "`echo ${php_extensions} | grep -w mongodb`" ] && pecl_mongodb=1 + [ -n "`echo ${php_extensions} | grep -w swoole`" ] && pecl_swoole=1 + [ -n "`echo ${php_extensions} | grep -w xdebug`" ] && pecl_xdebug=1 + ;; + --nodejs) + nodejs_flag=y; shift 1 + ;; + --pureftpd) + pureftpd_flag=y; shift 1 + ;; + --redis) + redis_flag=y; shift 1 + ;; + --memcached) + memcached_flag=y; shift 1 + ;; + --phpmyadmin) + phpmyadmin_flag=y; shift 1 + ;; + --) + shift + ;; + *) + echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 + ;; + esac +done + +Uninstall_status() { + if [ "${quiet_flag}" != 'y' ]; then + while :; do echo + read -e -p "Do you want to uninstall? [y/n]: " uninstall_flag + if [[ ! ${uninstall_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + fi +} + +Print_Warn() { + echo + echo "${CWARNING}You will uninstall OneinStack, Please backup your configure files and DB data! ${CEND}" +} + +Print_web() { + [ -d "${nginx_install_dir}" ] && echo ${nginx_install_dir} + [ -d "${tengine_install_dir}" ] && echo ${tengine_install_dir} + [ -d "${openresty_install_dir}" ] && echo ${openresty_install_dir} + [ -e "/etc/init.d/nginx" ] && echo /etc/init.d/nginx + [ -e "/lib/systemd/system/nginx.service" ] && echo /lib/systemd/system/nginx.service + [ -e "/etc/logrotate.d/nginx" ] && echo /etc/logrotate.d/nginx + + [ -d "${caddy_install_dir}" ] && echo ${caddy_install_dir} + [ -e "/lib/systemd/system/caddy.service" ] && echo /lib/systemd/system/caddy.service + + [ -d "${apache_install_dir}" ] && echo ${apache_install_dir} + [ -e "/lib/systemd/system/httpd.service" ] && echo /lib/systemd/system/httpd.service + [ -e "/etc/init.d/httpd" ] && echo /etc/init.d/httpd + [ -e "/etc/logrotate.d/apache" ] && echo /etc/logrotate.d/apache + + [ -d "${tomcat_install_dir}" ] && echo ${tomcat_install_dir} + [ -e "/etc/init.d/tomcat" ] && echo /etc/init.d/tomcat + [ -e "/etc/logrotate.d/tomcat" ] && echo /etc/logrotate.d/tomcat + [ -d "/usr/java" ] && echo /usr/java + [ -d "${apr_install_dir}" ] && echo ${apr_install_dir} +} + +Uninstall_Web() { + [ -d "${nginx_install_dir}" ] && { killall nginx > /dev/null 2>&1; rm -rf ${nginx_install_dir} /etc/init.d/nginx /etc/logrotate.d/nginx; sed -i "s@${nginx_install_dir}/sbin:@@" /etc/profile; echo "${CMSG}Nginx uninstall completed! ${CEND}"; } + [ -d "${tengine_install_dir}" ] && { killall nginx > /dev/null 2>&1; rm -rf ${tengine_install_dir} /etc/init.d/nginx /etc/logrotate.d/nginx; sed -i "s@${tengine_install_dir}/sbin:@@" /etc/profile; echo "${CMSG}Tengine uninstall completed! ${CEND}"; } + [ -d "${openresty_install_dir}" ] && { killall nginx > /dev/null 2>&1; rm -rf ${openresty_install_dir} /etc/init.d/nginx /etc/logrotate.d/nginx; sed -i "s@${openresty_install_dir}/nginx/sbin:@@" /etc/profile; echo "${CMSG}OpenResty uninstall completed! ${CEND}"; } + [ -d "${caddy_install_dir}" ] && { killall caddy > /dev/null 2>&1; rm -rf ${caddy_install_dir} /etc/init.d/caddy /etc/logrotate.d/caddy; sed -i "s@${caddy_install_dir}/bin:@@" /etc/profile; echo "${CMSG}Caddy uninstall completed! ${CEND}"; } + [ -e "/lib/systemd/system/nginx.service" ] && { systemctl disable nginx > /dev/null 2>&1; rm -f /lib/systemd/system/nginx.service; } + [ -e "/lib/systemd/system/caddy.service" ] && { systemctl disable caddy > /dev/null 2>&1; rm -f /lib/systemd/system/caddy.service; } + [ -d "${apache_install_dir}" ] && { service httpd stop > /dev/null 2>&1; rm -rf ${apache_install_dir} /etc/init.d/httpd /etc/logrotate.d/apache; sed -i "s@${apache_install_dir}/bin:@@" /etc/profile; echo "${CMSG}Apache uninstall completed! ${CEND}"; } + [ -e "/lib/systemd/system/httpd.service" ] && { systemctl disable httpd > /dev/null 2>&1; rm -f /lib/systemd/system/httpd.service; } + [ -d "${tomcat_install_dir}" ] && { killall java > /dev/null 2>&1; rm -rf ${tomcat_install_dir} /etc/init.d/tomcat /etc/logrotate.d/tomcat; echo "${CMSG}Tomcat uninstall completed! ${CEND}"; } + [ -d "/usr/java" ] && { rm -rf /usr/java; sed -i '/export JAVA_HOME=/d' /etc/profile; sed -i '/export CLASSPATH=/d' /etc/profile; sed -i 's@\$JAVA_HOME/bin:@@' /etc/profile; } + [ -e "${wwwroot_dir}" ] && /bin/mv ${wwwroot_dir}{,$(date +%Y%m%d%H)} + sed -i 's@^website_name=.*@website_name=@' ./options.conf + sed -i 's@^backup_content=.*@backup_content=@' ./options.conf + [ -d "${apr_install_dir}" ] && rm -rf ${apr_install_dir} +} + +Print_MySQL() { + [ -e "${db_install_dir}" ] && echo ${db_install_dir} + [ -e "/etc/init.d/mysqld" ] && echo /etc/init.d/mysqld + [ -e "/etc/my.cnf" ] && echo /etc/my.cnf +} + +Print_PostgreSQL() { + [ -e "${pgsql_install_dir}" ] && echo ${pgsql_install_dir} + [ -e "/etc/init.d/postgresql" ] && echo /etc/init.d/postgresql + [ -e "/lib/systemd/system/postgresql.service" ] && echo /lib/systemd/system/postgresql.service +} + +Print_MongoDB() { + [ -e "${mongo_install_dir}" ] && echo ${mongo_install_dir} + [ -e "/etc/init.d/mongod" ] && echo /etc/init.d/mongod + [ -e "/lib/systemd/system/mongod.service" ] && echo /lib/systemd/system/mongod.service + [ -e "/etc/mongod.conf" ] && echo /etc/mongod.conf +} + +Uninstall_MySQL() { + # uninstall mysql,mariadb,percona + if [ -d "${db_install_dir}/support-files" ]; then + service mysqld stop > /dev/null 2>&1 + rm -rf ${db_install_dir} /etc/init.d/mysqld /etc/my.cnf* /etc/ld.so.conf.d/*{mysql,mariadb,percona}*.conf + id -u mysql >/dev/null 2>&1 ; [ $? -eq 0 ] && userdel mysql + [ -e "${db_data_dir}" ] && /bin/mv ${db_data_dir}{,$(date +%Y%m%d%H)} + sed -i 's@^dbrootpwd=.*@dbrootpwd=@' ./options.conf + sed -i "s@${db_install_dir}/bin:@@" /etc/profile + echo "${CMSG}MySQL uninstall completed! ${CEND}" + fi +} + +Uninstall_PostgreSQL() { + # uninstall postgresql + if [ -e "${pgsql_install_dir}/bin/psql" ]; then + service postgresql stop > /dev/null 2>&1 + rm -rf ${pgsql_install_dir} /etc/init.d/postgresql + [ -e "/lib/systemd/system/postgresql.service" ] && { systemctl disable postgresql > /dev/null 2>&1; rm -f /lib/systemd/system/postgresql.service; } + [ -e "${php_install_dir}/etc/php.d/07-pgsql.ini" ] && rm -f ${php_install_dir}/etc/php.d/07-pgsql.ini + id -u postgres >/dev/null 2>&1 ; [ $? -eq 0 ] && userdel postgres + [ -e "${pgsql_data_dir}" ] && /bin/mv ${pgsql_data_dir}{,$(date +%Y%m%d%H)} + sed -i 's@^dbpostgrespwd=.*@dbpostgrespwd=@' ./options.conf + sed -i "s@${pgsql_install_dir}/bin:@@" /etc/profile + echo "${CMSG}PostgreSQL uninstall completed! ${CEND}" + fi +} + +Uninstall_MongoDB() { + # uninstall mongodb + if [ -e "${mongo_install_dir}/bin/mongo" ]; then + service mongod stop > /dev/null 2>&1 + rm -rf ${mongo_install_dir} /etc/mongod.conf /etc/init.d/mongod /tmp/mongo*.sock + [ -e "/lib/systemd/system/mongod.service" ] && { systemctl disable mongod > /dev/null 2>&1; rm -f /lib/systemd/system/mongod.service; } + [ -e "${php_install_dir}/etc/php.d/07-mongo.ini" ] && rm -f ${php_install_dir}/etc/php.d/07-mongo.ini + [ -e "${php_install_dir}/etc/php.d/07-mongodb.ini" ] && rm -f ${php_install_dir}/etc/php.d/07-mongodb.ini + id -u mongod > /dev/null 2>&1 ; [ $? -eq 0 ] && userdel mongod + [ -e "${mongo_data_dir}" ] && /bin/mv ${mongo_data_dir}{,$(date +%Y%m%d%H)} + sed -i 's@^dbmongopwd=.*@dbmongopwd=@' ./options.conf + sed -i "s@${mongo_install_dir}/bin:@@" /etc/profile + echo "${CMSG}MongoDB uninstall completed! ${CEND}" + fi +} + +Print_PHP() { + [ -e "${php_install_dir}" ] && echo ${php_install_dir} + [ -e "/etc/init.d/php-fpm" ] && echo /etc/init.d/php-fpm + [ -e "/lib/systemd/system/php-fpm.service" ] && echo /lib/systemd/system/php-fpm.service +} + +Print_MPHP() { + [ -e "${php_install_dir}${mphp_ver}" ] && echo ${php_install_dir}${mphp_ver} + [ -e "/etc/init.d/php${mphp_ver}-fpm" ] && echo /etc/init.d/php${mphp_ver}-fpm + [ -e "/lib/systemd/system/php${mphp_ver}-fpm.service" ] && echo /lib/systemd/system/php${mphp_ver}-fpm.service +} + +Print_ALLPHP() { + [ -e "${php_install_dir}" ] && echo ${php_install_dir} + [ -e "/etc/init.d/php-fpm" ] && echo /etc/init.d/php-fpm + [ -e "/lib/systemd/system/php-fpm.service" ] && echo /lib/systemd/system/php-fpm.service + for php_ver in 53 54 55 56 70 71 72 73 74 80 81; do + [ -e "${php_install_dir}${php_ver}" ] && echo ${php_install_dir}${php_ver} + [ -e "/etc/init.d/php${php_ver}-fpm" ] && echo /etc/init.d/php${php_ver}-fpm + [ -e "/lib/systemd/system/php${php_ver}-fpm.service" ] && echo /lib/systemd/system/php${php_ver}-fpm.service + done + [ -e "${imagick_install_dir}" ] && echo ${imagick_install_dir} + [ -e "${gmagick_install_dir}" ] && echo ${gmagick_install_dir} + [ -e "${curl_install_dir}" ] && echo ${curl_install_dir} + [ -e "${freetype_install_dir}" ] && echo ${freetype_install_dir} +} + +Uninstall_PHP() { + [ -e "/etc/init.d/php-fpm" ] && { service php-fpm stop > /dev/null 2>&1; rm -f /etc/init.d/php-fpm; } + [ -e "/lib/systemd/system/php-fpm.service" ] && { systemctl stop php-fpm > /dev/null 2>&1; systemctl disable php-fpm > /dev/null 2>&1; rm -f /lib/systemd/system/php-fpm.service; } + [ -e "${apache_install_dir}/conf/httpd.conf" ] && [ -n "`grep libphp ${apache_install_dir}/conf/httpd.conf`" ] && sed -i '/libphp/d' ${apache_install_dir}/conf/httpd.conf + [ -e "${php_install_dir}" ] && { rm -rf ${php_install_dir}; echo "${CMSG}PHP uninstall completed! ${CEND}"; } + sed -i "s@${php_install_dir}/bin:@@" /etc/profile +} + +Uninstall_MPHP() { + [ -e "/etc/init.d/php${mphp_ver}-fpm" ] && { service php${mphp_ver}-fpm stop > /dev/null 2>&1; rm -f /etc/init.d/php${mphp_ver}-fpm; } + [ -e "/lib/systemd/system/php${mphp_ver}-fpm.service" ] && { systemctl stop php${mphp_ver}-fpm > /dev/null 2>&1; systemctl disable php${mphp_ver}-fpm > /dev/null 2>&1; rm -f /lib/systemd/system/php${mphp_ver}-fpm.service; } + [ -e "${php_install_dir}${mphp_ver}" ] && { rm -rf ${php_install_dir}${mphp_ver}; echo "${CMSG}PHP${mphp_ver} uninstall completed! ${CEND}"; } +} + +Uninstall_ALLPHP() { + [ -e "/etc/init.d/php-fpm" ] && { service php-fpm stop > /dev/null 2>&1; rm -f /etc/init.d/php-fpm; } + [ -e "/lib/systemd/system/php-fpm.service" ] && { systemctl stop php-fpm > /dev/null 2>&1; systemctl disable php-fpm > /dev/null 2>&1; rm -f /lib/systemd/system/php-fpm.service; } + [ -e "${apache_install_dir}/conf/httpd.conf" ] && [ -n "`grep libphp ${apache_install_dir}/conf/httpd.conf`" ] && sed -i '/libphp/d' ${apache_install_dir}/conf/httpd.conf + [ -e "${php_install_dir}" ] && { rm -rf ${php_install_dir}; echo "${CMSG}PHP uninstall completed! ${CEND}"; } + sed -i "s@${php_install_dir}/bin:@@" /etc/profile + for php_ver in 53 54 55 56 70 71 72 73 74 80 81 82 83; do + [ -e "/etc/init.d/php${php_ver}-fpm" ] && { service php${php_ver}-fpm stop > /dev/null 2>&1; rm -f /etc/init.d/php${php_ver}-fpm; } + [ -e "/lib/systemd/system/php${php_ver}-fpm.service" ] && { systemctl stop php${php_ver}-fpm > /dev/null 2>&1; systemctl disable php${php_ver}-fpm > /dev/null 2>&1; rm -f /lib/systemd/system/php${php_ver}-fpm.service; } + [ -e "${php_install_dir}${php_ver}" ] && { rm -rf ${php_install_dir}${php_ver}; echo "${CMSG}PHP${php_ver} uninstall completed! ${CEND}"; } + done + [ -e "${imagick_install_dir}" ] && rm -rf ${imagick_install_dir} + [ -e "${gmagick_install_dir}" ] && rm -rf ${gmagick_install_dir} + [ -e "${curl_install_dir}" ] && rm -rf ${curl_install_dir} + [ -e "${freetype_install_dir}" ] && rm -rf ${freetype_install_dir} +} + +Uninstall_PHPcache() { + . include/zendopcache.sh + . include/xcache.sh + . include/apcu.sh + . include/eaccelerator.sh + Uninstall_ZendOPcache + Uninstall_XCache + Uninstall_APCU + Uninstall_eAccelerator + # reload php + [ -e "${php_install_dir}/sbin/php-fpm" ] && { [ -e "/bin/systemctl" ] && systemctl reload php-fpm || service php-fpm reload; } + [ -n "${mphp_ver}" -a -e "${php_install_dir}${mphp_ver}/sbin/php-fpm" ] && { [ -e "/bin/systemctl" ] && systemctl reload php${mphp_ver}-fpm || service php${mphp_ver}-fpm reload; } + [ -e "${apache_install_dir}/bin/apachectl" ] && ${apache_install_dir}/bin/apachectl -k graceful +} + +Uninstall_PHPext() { + # ZendGuardLoader + if [ "${pecl_zendguardloader}" == '1' ]; then + . include/ZendGuardLoader.sh + Uninstall_ZendGuardLoader + fi + + # ioncube + if [ "${pecl_ioncube}" == '1' ]; then + . include/ioncube.sh + Uninstall_ionCube + fi + + # SourceGuardian + if [ "${pecl_sourceguardian}" == '1' ]; then + . include/sourceguardian.sh + Uninstall_SourceGuardian + fi + + # imagick + if [ "${pecl_imagick}" == '1' ]; then + . include/ImageMagick.sh + Uninstall_ImageMagick + Uninstall_pecl_imagick + fi + + # gmagick + if [ "${pecl_gmagick}" == '1' ]; then + . include/GraphicsMagick.sh + Uninstall_GraphicsMagick + Uninstall_pecl_gmagick + fi + + # fileinfo + if [ "${pecl_fileinfo}" == '1' ]; then + . include/pecl_fileinfo.sh + Uninstall_pecl_fileinfo + fi + + # imap + if [ "${pecl_imap}" == '1' ]; then + . include/pecl_imap.sh + Uninstall_pecl_imap + fi + + # ldap + if [ "${pecl_ldap}" == '1' ]; then + . include/pecl_ldap.sh + Uninstall_pecl_ldap + fi + + # calendar + if [ "${pecl_calendar}" == '1' ]; then + . include/pecl_calendar.sh + Uninstall_pecl_calendar + fi + + # phalcon + if [ "${pecl_phalcon}" == '1' ]; then + . include/pecl_phalcon.sh + Uninstall_pecl_phalcon + fi + + # yaf + if [ "${pecl_yaf}" == '1' ]; then + . include/pecl_yaf.sh + Uninstall_pecl_yaf 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # yar + if [ "${pecl_yar}" == '1' ]; then + . include/pecl_yar.sh + Uninstall_pecl_yar 2>&1 | tee -a ${oneinstack_dir}/install.log + fi + + # pecl_memcached + if [ "${pecl_memcached}" == '1' ]; then + . include/memcached.sh + Uninstall_pecl_memcached + fi + + # pecl_memcache + if [ "${pecl_memcache}" == '1' ]; then + . include/memcached.sh + Uninstall_pecl_memcache + fi + + # pecl_redis + if [ "${pecl_redis}" == '1' ]; then + . include/redis.sh + Uninstall_pecl_redis + fi + + # pecl_mongodb + if [ "${pecl_mongodb}" == '1' ]; then + . include/pecl_mongodb.sh + Uninstall_pecl_mongodb + fi + + # swoole + if [ "${pecl_swoole}" == '1' ]; then + . include/pecl_swoole.sh + Uninstall_pecl_swoole + fi + + # xdebug + if [ "${pecl_xdebug}" == '1' ]; then + . include/pecl_xdebug.sh + Uninstall_pecl_xdebug + fi + + # reload php + [ -e "${php_install_dir}/sbin/php-fpm" ] && { [ -e "/bin/systemctl" ] && systemctl reload php-fpm || service php-fpm reload; } + [ -n "${mphp_ver}" -a -e "${php_install_dir}${mphp_ver}/sbin/php-fpm" ] && { [ -e "/bin/systemctl" ] && systemctl reload php${mphp_ver}-fpm || service php${mphp_ver}-fpm reload; } + [ -e "${apache_install_dir}/bin/apachectl" ] && ${apache_install_dir}/bin/apachectl -k graceful +} + +Menu_PHPext() { + while :; do + echo 'Please select uninstall PHP extensions:' + echo -e "\t${CMSG} 0${CEND}. Do not uninstall" + echo -e "\t${CMSG} 1${CEND}. Uninstall zendguardloader(PHP<=5.6)" + echo -e "\t${CMSG} 2${CEND}. Uninstall ioncube" + echo -e "\t${CMSG} 3${CEND}. Uninstall sourceguardian(PHP<=7.2)" + echo -e "\t${CMSG} 4${CEND}. Uninstall imagick" + echo -e "\t${CMSG} 5${CEND}. Uninstall gmagick" + echo -e "\t${CMSG} 6${CEND}. Uninstall fileinfo" + echo -e "\t${CMSG} 7${CEND}. Uninstall imap" + echo -e "\t${CMSG} 8${CEND}. Uninstall ldap" + echo -e "\t${CMSG} 9${CEND}. Uninstall phalcon(PHP>=5.5)" + echo -e "\t${CMSG}10${CEND}. Uninstall redis" + echo -e "\t${CMSG}11${CEND}. Uninstall memcached" + echo -e "\t${CMSG}12${CEND}. Uninstall memcache" + echo -e "\t${CMSG}13${CEND}. Uninstall mongodb" + echo -e "\t${CMSG}14${CEND}. Uninstall swoole" + echo -e "\t${CMSG}15${CEND}. Uninstall xdebug(PHP>=5.5)" + read -e -p "Please input a number:(Default 0 press Enter) " phpext_option + phpext_option=${phpext_option:-0} + [ "${phpext_option}" == '0' ] && break + array_phpext=(${phpext_option}) + array_all=(1 2 3 4 5 6 7 8 9 10 11 12 13 14 15) + for v in ${array_phpext[@]} + do + [ -z "`echo ${array_all[@]} | grep -w ${v}`" ] && phpext_flag=1 + done + if [ "${phpext_flag}" == '1' ]; then + unset phpext_flag + echo; echo "${CWARNING}input error! Please only input number 1 2 3 14 and so on${CEND}"; echo + continue + else + [ -n "`echo ${array_phpext[@]} | grep -w 1`" ] && pecl_zendguardloader=1 + [ -n "`echo ${array_phpext[@]} | grep -w 2`" ] && pecl_ioncube=1 + [ -n "`echo ${array_phpext[@]} | grep -w 3`" ] && pecl_sourceguardian=1 + [ -n "`echo ${array_phpext[@]} | grep -w 4`" ] && pecl_imagick=1 + [ -n "`echo ${array_phpext[@]} | grep -w 5`" ] && pecl_gmagick=1 + [ -n "`echo ${array_phpext[@]} | grep -w 6`" ] && pecl_fileinfo=1 + [ -n "`echo ${array_phpext[@]} | grep -w 7`" ] && pecl_imap=1 + [ -n "`echo ${array_phpext[@]} | grep -w 8`" ] && pecl_ldap=1 + [ -n "`echo ${array_phpext[@]} | grep -w 9`" ] && pecl_phalcon=1 + [ -n "`echo ${array_phpext[@]} | grep -w 10`" ] && pecl_redis=1 + [ -n "`echo ${array_phpext[@]} | grep -w 11`" ] && pecl_memcached=1 + [ -n "`echo ${array_phpext[@]} | grep -w 12`" ] && pecl_memcache=1 + [ -n "`echo ${array_phpext[@]} | grep -w 13`" ] && pecl_mongodb=1 + [ -n "`echo ${array_phpext[@]} | grep -w 14`" ] && pecl_swoole=1 + [ -n "`echo ${array_phpext[@]} | grep -w 15`" ] && pecl_xdebug=1 + break + fi + done +} + +Print_PureFtpd() { + [ -e "${pureftpd_install_dir}" ] && echo ${pureftpd_install_dir} + [ -e "/etc/init.d/pureftpd" ] && echo /etc/init.d/pureftpd + [ -e "/lib/systemd/system/pureftpd.service" ] && echo /lib/systemd/system/pureftpd.service +} + +Uninstall_PureFtpd() { + [ -e "${pureftpd_install_dir}" ] && { service pureftpd stop > /dev/null 2>&1; rm -rf ${pureftpd_install_dir} /etc/init.d/pureftpd; echo "${CMSG}Pureftpd uninstall completed! ${CEND}"; } + [ -e "/lib/systemd/system/pureftpd.service" ] && { systemctl disable pureftpd > /dev/null 2>&1; rm -f /lib/systemd/system/pureftpd.service; } +} + +Print_Redis_server() { + [ -e "${redis_install_dir}" ] && echo ${redis_install_dir} + [ -e "/etc/init.d/redis-server" ] && echo /etc/init.d/redis-server + [ -e "/lib/systemd/system/redis-server.service" ] && echo /lib/systemd/system/redis-server.service +} + +Uninstall_Redis_server() { + [ -e "${redis_install_dir}" ] && { service redis-server stop > /dev/null 2>&1; rm -rf ${redis_install_dir} /etc/init.d/redis-server /usr/local/bin/redis-*; echo "${CMSG}Redis uninstall completed! ${CEND}"; } + [ -e "/lib/systemd/system/redis-server.service" ] && { systemctl disable redis-server > /dev/null 2>&1; rm -f /lib/systemd/system/redis-server.service; } +} + +Print_Memcached_server() { + [ -e "${memcached_install_dir}" ] && echo ${memcached_install_dir} + [ -e "/etc/init.d/memcached" ] && echo /etc/init.d/memcached + [ -e "/usr/bin/memcached" ] && echo /usr/bin/memcached +} + +Uninstall_Memcached_server() { + [ -e "${memcached_install_dir}" ] && { service memcached stop > /dev/null 2>&1; rm -rf ${memcached_install_dir} /etc/init.d/memcached /usr/bin/memcached; echo "${CMSG}Memcached uninstall completed! ${CEND}"; } +} + +Print_phpMyAdmin() { + [ -d "${wwwroot_dir}/default/phpMyAdmin" ] && echo ${wwwroot_dir}/default/phpMyAdmin +} + +Uninstall_phpMyAdmin() { + [ -d "${wwwroot_dir}/default/phpMyAdmin" ] && rm -rf ${wwwroot_dir}/default/phpMyAdmin +} + +Print_openssl() { + [ -d "${openssl_install_dir}" ] && echo ${openssl_install_dir} +} + +Uninstall_openssl() { + [ -d "${openssl_install_dir}" ] && rm -rf ${openssl_install_dir} +} + +Print_Nodejs() { + [ -e "${nodejs_install_dir}" ] && echo ${nodejs_install_dir} + [ -e "/etc/profile.d/nodejs.sh" ] && echo /etc/profile.d/nodejs.sh +} + +Menu() { +while :; do + printf " +What Are You Doing? +\t${CMSG} 0${CEND}. Uninstall All +\t${CMSG} 1${CEND}. Uninstall Nginx/Tengine/OpenResty/Apache/Tomcat/Caddy +\t${CMSG} 2${CEND}. Uninstall MySQL/MariaDB/Percona +\t${CMSG} 3${CEND}. Uninstall PostgreSQL +\t${CMSG} 4${CEND}. Uninstall MongoDB +\t${CMSG} 5${CEND}. Uninstall all PHP +\t${CMSG} 6${CEND}. Uninstall PHP opcode cache +\t${CMSG} 7${CEND}. Uninstall PHP extensions +\t${CMSG} 8${CEND}. Uninstall PureFtpd +\t${CMSG} 9${CEND}. Uninstall Redis +\t${CMSG}10${CEND}. Uninstall Memcached +\t${CMSG}11${CEND}. Uninstall phpMyAdmin +\t${CMSG}12${CEND}. Uninstall Nodejs (PATH: ${nodejs_install_dir}) +\t${CMSG} q${CEND}. Exit +" + echo + read -e -p "Please input the correct option: " Number + if [[ ! "${Number}" =~ ^[0-9,q]$|^1[0-3]$ ]]; then + echo "${CWARNING}input error! Please only input 0~12 and q${CEND}" + else + case "$Number" in + 0) + Print_Warn + Print_web + Print_MySQL + Print_PostgreSQL + Print_MongoDB + Print_ALLPHP + Print_PureFtpd + Print_Redis_server + Print_Memcached_server + Print_openssl + Print_phpMyAdmin + Print_Nodejs + Uninstall_status + if [ "${uninstall_flag}" == 'y' ]; then + Uninstall_Web + Uninstall_MySQL + Uninstall_PostgreSQL + Uninstall_MongoDB + Uninstall_ALLPHP + Uninstall_PureFtpd + Uninstall_Redis_server + Uninstall_Memcached_server + Uninstall_openssl + Uninstall_phpMyAdmin + . include/nodejs.sh; Uninstall_Nodejs + else + exit + fi + ;; + 1) + Print_Warn + Print_web + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_Web || exit + ;; + 2) + Print_Warn + Print_MySQL + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_MySQL || exit + ;; + 3) + Print_Warn + Print_PostgreSQL + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_PostgreSQL || exit + ;; + 4) + Print_Warn + Print_MongoDB + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_MongoDB || exit + ;; + 5) + Print_ALLPHP + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_ALLPHP || exit + ;; + 6) + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_PHPcache || exit + ;; + 7) + Menu_PHPext + [ "${phpext_option}" != '0' ] && Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_PHPext || exit + ;; + 8) + Print_PureFtpd + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_PureFtpd || exit + ;; + 9) + Print_Redis_server + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_Redis_server || exit + ;; + 10) + Print_Memcached_server + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_Memcached_server || exit + ;; + 11) + Print_phpMyAdmin + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && Uninstall_phpMyAdmin || exit + ;; + 12) + Print_Nodejs + Uninstall_status + [ "${uninstall_flag}" == 'y' ] && { . include/nodejs.sh; Uninstall_Nodejs; } || exit + ;; + q) + exit + ;; + esac + fi +done +} + +if [ ${ARG_NUM} == 0 ]; then + Menu +else + [ "${web_flag}" == 'y' ] && Print_web + [ "${mysql_flag}" == 'y' ] && Print_MySQL + [ "${postgresql_flag}" == 'y' ] && Print_PostgreSQL + [ "${mongodb_flag}" == 'y' ] && Print_MongoDB + if [ "${allphp_flag}" == 'y' ]; then + Print_ALLPHP + else + [ "${php_flag}" == 'y' ] && Print_PHP + [ "${mphp_flag}" == 'y' ] && [ "${phpcache_flag}" != 'y' ] && [ -z "${php_extensions}" ] && Print_MPHP + fi + [ "${pureftpd_flag}" == 'y' ] && Print_PureFtpd + [ "${redis_flag}" == 'y' ] && Print_Redis_server + [ "${memcached_flag}" == 'y' ] && Print_Memcached_server + [ "${phpmyadmin_flag}" == 'y' ] && Print_phpMyAdmin + [ "${nodejs_flag}" == 'y' ] && Print_Nodejs + [ "${all_flag}" == 'y' ] && Print_openssl + Uninstall_status + if [ "${uninstall_flag}" == 'y' ]; then + [ "${web_flag}" == 'y' ] && Uninstall_Web + [ "${mysql_flag}" == 'y' ] && Uninstall_MySQL + [ "${postgresql_flag}" == 'y' ] && Uninstall_PostgreSQL + [ "${mongodb_flag}" == 'y' ] && Uninstall_MongoDB + if [ "${allphp_flag}" == 'y' ]; then + Uninstall_ALLPHP + else + [ "${php_flag}" == 'y' ] && Uninstall_PHP + [ "${phpcache_flag}" == 'y' ] && Uninstall_PHPcache + [ -n "${php_extensions}" ] && Uninstall_PHPext + [ "${mphp_flag}" == 'y' ] && [ "${phpcache_flag}" != 'y' ] && [ -z "${php_extensions}" ] && Uninstall_MPHP + [ "${mphp_flag}" == 'y' ] && [ "${phpcache_flag}" == 'y' ] && { php_install_dir=${php_install_dir}${mphp_ver}; Uninstall_PHPcache; } + [ "${mphp_flag}" == 'y' ] && [ -n "${php_extensions}" ] && { php_install_dir=${php_install_dir}${mphp_ver}; Uninstall_PHPext; } + fi + [ "${pureftpd_flag}" == 'y' ] && Uninstall_PureFtpd + [ "${redis_flag}" == 'y' ] && Uninstall_Redis_server + [ "${memcached_flag}" == 'y' ] && Uninstall_Memcached_server + [ "${phpmyadmin_flag}" == 'y' ] && Uninstall_phpMyAdmin + [ "${nodejs_flag}" == 'y' ] && { . include/nodejs.sh; Uninstall_Nodejs; } + [ "${all_flag}" == 'y' ] && Uninstall_openssl + fi +fi diff --git a/upgrade.sh b/upgrade.sh new file mode 100644 index 0000000..9cb06fd --- /dev/null +++ b/upgrade.sh @@ -0,0 +1,194 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin +clear +printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# Upgrade Software versions for OneinStack # +# For more information please visit https://oneinstack.com # +####################################################################### +" +# Check if user is root +[ $(id -u) != "0" ] && { echo "${CFAILURE}Error: You must be root to run this script${CEND}"; exit 1; } + +oneinstack_dir=$(dirname "`readlink -f $0`") +pushd ${oneinstack_dir} > /dev/null +. ./versions.txt +. ./options.conf +. ./include/color.sh +. ./include/check_os.sh +. ./include/check_dir.sh +. ./include/download.sh +. ./include/get_char.sh +. ./include/upgrade_web.sh +. ./include/upgrade_db.sh +. ./include/upgrade_php.sh +. ./include/upgrade_redis.sh +. ./include/upgrade_memcached.sh +. ./include/upgrade_phpmyadmin.sh +. ./include/upgrade_oneinstack.sh + +# get the out ip country +OUTIP_STATE=$(./include/ois.${ARCH} ip_state) + +Show_Help() { + echo + echo "Usage: $0 command ...[version].... + --help, -h Show this help message + --nginx [version] Upgrade Nginx + --tengine [version] Upgrade Tengine + --openresty [version] Upgrade OpenResty + --apache [version] Upgrade Apache + --tomcat [version] Upgrade Tomcat + --db [version] Upgrade MySQL/MariaDB/Percona + --php [version] Upgrade PHP + --redis [version] Upgrade Redis + --memcached [version] Upgrade Memcached + --phpmyadmin [version] Upgrade phpMyAdmin + --oneinstack Upgrade OneinStack latest + --acme.sh Upgrade acme.sh latest + " +} + +ARG_NUM=$# +TEMP=`getopt -o h --long help,nginx:,tengine:,openresty:,apache:,tomcat:,db:,php:,redis:,memcached:,phpmyadmin:,oneinstack,acme.sh -- "$@" 2>/dev/null` +[ $? != 0 ] && echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 +eval set -- "${TEMP}" +while :; do + [ -z "$1" ] && break; + case "$1" in + -h|--help) + Show_Help; exit 0 + ;; + --nginx) + nginx_flag=y; NEW_nginx_ver=$2; shift 2 + ;; + --tengine) + tengine_flag=y; NEW_tengine_ver=$2; shift 2 + ;; + --openresty) + openresty_flag=y; NEW_openresy_ver=$2; shift 2 + ;; + --apache) + apache_flag=y; NEW_apache_ver=$2; shift 2 + ;; + --tomcat) + tomcat_flag=y; NEW_tomcat_ver=$2; shift 2 + ;; + --db) + db_flag=y; NEW_db_ver=$2; shift 2 + ;; + --php) + php_flag=y; NEW_php_ver=$2; shift 2 + ;; + --redis) + redis_flag=y; NEW_redis_ver=$2; shift 2 + ;; + --memcached) + memcached_flag=y; NEW_memcached_ver=$2; shift 2 + ;; + --phpmyadmin) + phpmyadmin_flag=y; NEW_phpmyadmin_ver=$2; shift 2 + ;; + --oneinstack) + NEW_oneinstack_ver=latest; shift 1 + ;; + --acme.sh) + NEW_acme_ver=latest; shift 1 + ;; + --) + shift + ;; + *) + echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 + ;; + esac +done + +Menu() { + while :; do + printf " +What Are You Doing? +\t${CMSG} 1${CEND}. Upgrade Nginx/Tengine/OpenResty +\t${CMSG} 2${CEND}. Upgrade Apache +\t${CMSG} 3${CEND}. Upgrade Tomcat +\t${CMSG} 4${CEND}. Upgrade MySQL/MariaDB/Percona +\t${CMSG} 5${CEND}. Upgrade PHP +\t${CMSG} 6${CEND}. Upgrade Redis +\t${CMSG} 7${CEND}. Upgrade Memcached +\t${CMSG} 8${CEND}. Upgrade phpMyAdmin +\t${CMSG} 9${CEND}. Upgrade OneinStack latest +\t${CMSG}10${CEND}. Upgrade acme.sh latest +\t${CMSG} q${CEND}. Exit +" + echo + read -e -p "Please input the correct option: " Upgrade_flag + if [[ ! "${Upgrade_flag}" =~ ^[1-9,q]$|^10$ ]]; then + echo "${CWARNING}input error! Please only input 1~10 and q${CEND}" + else + case "${Upgrade_flag}" in + 1) + [ -e "${nginx_install_dir}/sbin/nginx" ] && Upgrade_Nginx + [ -e "${tengine_install_dir}/sbin/nginx" ] && Upgrade_Tengine + [ -e "${openresty_install_dir}/nginx/sbin/nginx" ] && Upgrade_OpenResty + ;; + 2) + Upgrade_Apache + ;; + 3) + Upgrade_Tomcat + ;; + 4) + Upgrade_DB + ;; + 5) + Upgrade_PHP + ;; + 6) + Upgrade_Redis + ;; + 7) + Upgrade_Memcached + ;; + 8) + Upgrade_phpMyAdmin + ;; + 9) + Upgrade_OneinStack + ;; + 10) + [ -e ~/.acme.sh/acme.sh ] && { ~/.acme.sh/acme.sh --force --upgrade; ~/.acme.sh/acme.sh --version; } + ;; + q) + exit + ;; + esac + fi + done +} + +if [ ${ARG_NUM} == 0 ]; then + Menu +else + [ "${nginx_flag}" == 'y' ] && Upgrade_Nginx + [ "${tengine_flag}" == 'y' ] && Upgrade_Tengine + [ "${openresty_flag}" == 'y' ] && Upgrade_OpenResty + [ "${apache_flag}" == 'y' ] && Upgrade_Apache + [ "${tomcat_flag}" == 'y' ] && Upgrade_Tomcat + [ "${db_flag}" == 'y' ] && Upgrade_DB + [ "${php_flag}" == 'y' ] && Upgrade_PHP + [ "${redis_flag}" == 'y' ] && Upgrade_Redis + [ "${memcached_flag}" == 'y' ] && Upgrade_Memcached + [ "${phpmyadmin_flag}" == 'y' ] && Upgrade_phpMyAdmin + [ "${NEW_oneinstack_ver}" == 'latest' ] && Upgrade_OneinStack + [ "${NEW_acme_ver}" == 'latest' ] && [ -e ~/.acme.sh/acme.sh ] && { ~/.acme.sh/acme.sh --force --upgrade; ~/.acme.sh/acme.sh --version; } +fi diff --git a/versions.txt b/versions.txt new file mode 100644 index 0000000..54ab49c --- /dev/null +++ b/versions.txt @@ -0,0 +1,130 @@ +# newest software version +# Web +nginx_ver=1.24.0 +caddy_ver=2.7.6 +tengine_ver=3.1.0 +openresty_ver=1.21.4.3 +openssl11_ver=1.1.1w +openssl_ver=1.0.2u + +tomcat10_ver=10.1.16 +tomcat9_ver=9.0.83 +tomcat8_ver=8.5.96 +tomcat7_ver=7.0.109 + +apache_ver=2.4.58 +pcre_ver=8.45 +apr_ver=1.7.0 +apr_util_ver=1.6.1 +nghttp2_ver=1.42.0 + +# DB +mysql82_ver=8.2.0 +mysql80_ver=8.0.36 +mysql57_ver=5.7.44 +mysql56_ver=5.6.51 +mysql55_ver=5.5.62 + +mariadb1011_ver=10.11.8 +mariadb105_ver=10.5.23 +mariadb104_ver=10.4.32 +mariadb55_ver=5.5.68 + +percona80_ver=8.0.33-25 +percona57_ver=5.7.42-46 +percona56_ver=5.6.51-91.0 +percona55_ver=5.5.62-38.14 + +pgsql_ver=12.7 + +mongodb_ver=4.0.26 + +# PHP +php53_ver=5.3.29 +php54_ver=5.4.45 +php55_ver=5.5.38 +php56_ver=5.6.40 +php70_ver=7.0.33 +php71_ver=7.1.33 +php72_ver=7.2.34 +php73_ver=7.3.33 +php74_ver=7.4.33 +php80_ver=8.0.30 +php81_ver=8.1.27 +php82_ver=8.2.14 +php83_ver=8.3.2 + +# Nodejs +nodejs_ver=20.10.0 + +libiconv_ver=1.16 +curl_ver=8.4.0 +libmcrypt_ver=2.5.8 +mcrypt_ver=2.6.8 +mhash_ver=0.9.9.9 +freetype_ver=2.10.1 +icu4c_ver=63_1 +libsodium_ver=1.0.18 +libsodium_up_ver=1.0.19 +libzip_ver=1.2.0 +argon2_ver=20171227 +imagemagick_ver=7.1.1-23 +imagick_ver=3.7.0 +imagick_oldver=3.4.4 +graphicsmagick_ver=1.3.40 +gmagick_ver=2.0.6RC1 +gmagick_oldver=1.1.7RC3 +zendopcache_ver=7.0.5 +apcu_ver=5.1.21 +apcu_oldver=4.0.11 +xcache_ver=3.2.0 +eaccelerator_ver=0.9.6.1 +phalcon_ver=5.4.0 +phalcon_oldver=3.4.5 +yaf_ver=3.3.2 +yar_ver=2.2.0 +swoole_ver=5.0.3 +swoole_oldver=4.8.12 +xdebug_ver=3.1.2 +xdebug_oldver=2.9.8 + +# Ftp +pureftpd_ver=1.0.51 + +# Redis +redis_ver=7.2.3 +redis_oldver=6.2.14 +pecl_redis_ver=6.0.2 + +# Memcached +memcached_ver=1.6.22 +libmemcached_ver=1.0.18 +pecl_memcached_ver=3.2.0 +pecl_memcached_oldver=2.2.0 +pecl_memcache_ver=8.2 +pecl_memcache_oldver=4.0.5.2 + +# MongoDB +pecl_mongodb_ver=1.16.2 +pecl_mongodb_oldver=1.9.2 +pecl_mongo_ver=1.6.16 + +# phpMyadmin +phpmyadmin_ver=5.2.1 +phpmyadmin_oldver=4.4.15.10 + +# jemalloc +jemalloc_ver=5.3.0 + +# boost +boost_ver=1.77.0 +boost_percona_ver=1.77.0 +boost_oldver=1.59.0 + +# Others +lua_nginx_module_ver=0.10.25 +luajit2_ver=2.1-20230410 +lua_resty_core_ver=0.1.27 +lua_resty_lrucache_ver=0.13 +lua_cjson_ver=2.1.0.12 +fail2ban_ver=master diff --git a/vhost.sh b/vhost.sh new file mode 100644 index 0000000..200cf1e --- /dev/null +++ b/vhost.sh @@ -0,0 +1,1297 @@ +#!/bin/bash +# Author: yeho +# BLOG: https://linuxeye.com +# +# Notes: OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ +# +# Project home page: +# https://oneinstack.com +# https://github.com/oneinstack/oneinstack + +export PATH=/sbin:/bin:/usr/sbin:/usr/bin:/usr/local/sbin:/usr/local/bin +clear +printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# For more information please visit https://oneinstack.com # +####################################################################### +" +# Check if user is root +[ $(id -u) != '0' ] && { echo "${CFAILURE}Error: You must be root to run this script${CEND}"; exit 1; } + +oneinstack_dir=$(dirname "`readlink -f $0`") +pushd ${oneinstack_dir} > /dev/null +. ./options.conf +. ./include/color.sh +. ./include/check_dir.sh +. ./include/check_os.sh +. ./include/get_char.sh +. ./include/openssl.sh + +Show_Help() { + echo + echo "Usage: $0 command ...[parameters].... + --help, -h Show this help message + --quiet, -q quiet operation + --list, -l List Virtualhost + --mphp_ver [53~81] Use another PHP version (PATH: /usr/local/php${mphp_ver}) + --proxy Use proxy + --add Add Virtualhost + --delete, --del Delete Virtualhost + --httponly Use HTTP Only + --selfsigned Use your own SSL Certificate and Key + --letsencrypt Use Let's Encrypt to Create SSL Certificate and Key + --dnsapi Use dns API to automatically issue Let's Encrypt Cert + " +} + +ARG_NUM=$# +TEMP=`getopt -o hql --long help,quiet,list,proxy,mphp_ver:,add,delete,del,httponly,selfsigned,letsencrypt,dnsapi -- "$@" 2>/dev/null` +[ $? != 0 ] && echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 +eval set -- "${TEMP}" +while :; do + [ -z "$1" ] && break; + case "$1" in + -h|--help) + Show_Help; exit 0 + ;; + -q|--quiet) + quiet_flag=y; shift 1 + ;; + -l|--list) + list_flag=y; shift 1 + ;; + --mphp_ver) + mphp_ver=$2; mphp_flag=y; shift 2 + [[ ! "${mphp_ver}" =~ ^5[3-6]$|^7[0-4]$|^8[0-1]$ ]] && { echo "${CWARNING}mphp_ver input error! Please only input number 53~81${CEND}"; unset mphp_ver mphp_flag; } + ;; + --proxy) + proxy_flag=y; shift 1 + ;; + --add) + add_flag=y; shift 1 + ;; + --delete|--del) + delete_flag=y; shift 1 + ;; + --httponly) + sslquiet_flag=y + httponly_flag=y + Domian_Mode=1 + shift 1 + ;; + --selfsigned) + sslquiet_flag=y + selfsigned_flag=y + Domian_Mode=2 + shift 1 + ;; + --letsencrypt) + sslquiet_flag=y + letsencrypt_flag=y + Domian_Mode=3 + shift 1 + ;; + --dnsapi) + sslquiet_flag=y + dnsapi_flag=y + letsencrypt_flag=y + shift 1 + ;; + --) + shift + ;; + *) + echo "${CWARNING}ERROR: unknown argument! ${CEND}" && Show_Help && exit 1 + ;; + esac +done + +Choose_ENV() { + if [ -e "${apache_install_dir}/bin/apachectl" ];then + [ "$(${apache_install_dir}/bin/apachectl -v | awk -F'.' /version/'{print $2}')" == '4' ] && { Apache_main_ver=24; Apache_grant='Require all granted'; } + [ "$(${apache_install_dir}/bin/apachectl -v | awk -F'.' /version/'{print $2}')" == '2' ] && Apache_main_ver=22 + fi + if [ -e "${php_install_dir}/bin/phpize" -a -e "${tomcat_install_dir}/conf/server.xml" ] && [[ -z ${proxy_flag} || "${proxy_flag}" != 'y' ]]; then + Number=11 + while :; do echo + echo "Please choose to use environment:" + echo -e "\t${CMSG}1${CEND}. Use php" + echo -e "\t${CMSG}2${CEND}. Use java" + read -e -p "Please input a number:(Default 1 press Enter) " ENV_FLAG + ENV_FLAG=${ENV_FLAG:-1} + if [[ ! ${ENV_FLAG} =~ ^[1-2]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~2${CEND}" + else + break + fi + done + case "${ENV_FLAG}" in + 1) + NGX_FLAG=php + ;; + 2) + NGX_FLAG=java + ;; + esac + elif [ -e "${php_install_dir}/bin/phpize" -a ! -e "${tomcat_install_dir}/conf/server.xml" ]; then + Number=10 + NGX_FLAG=php + elif [ ! -e "${php_install_dir}/bin/phpize" -a -e "${tomcat_install_dir}/conf/server.xml" ]; then + Number=01 + NGX_FLAG=java + else + Number=00 + NGX_FLAG=php + fi +} + +Create_SSL() { + if [ "${Domian_Mode}" == '2' ]; then + printf " +You are about to be asked to enter information that will be incorporated +into your certificate request. +What you are about to enter is what is called a Distinguished Name or a DN. +There are quite a few fields but you can leave some blank +For some fields there will be a default value, +If you enter '.', the field will be left blank. +" + echo + read -e -p "Country Name (2 letter code) [CN]: " SELFSIGNEDSSL_C + SELFSIGNEDSSL_C=${SELFSIGNEDSSL_C:-CN} + # shellcheck disable=SC2104 + [ ${#SELFSIGNEDSSL_C} != 2 ] && { echo "${CWARNING}input error, You must input 2 letter code country name${CEND}"; continue; } + echo + read -e -p "State or Province Name (full name) [Shanghai]: " SELFSIGNEDSSL_ST + SELFSIGNEDSSL_ST=${SELFSIGNEDSSL_ST:-Shanghai} + echo + read -e -p "Locality Name (eg, city) [Shanghai]: " SELFSIGNEDSSL_L + SELFSIGNEDSSL_L=${SELFSIGNEDSSL_L:-Shanghai} + echo + read -e -p "Organization Name (eg, company) [Example Inc.]: " SELFSIGNEDSSL_O + SELFSIGNEDSSL_O=${SELFSIGNEDSSL_O:-"Example Inc."} + echo + read -e -p "Organizational Unit Name (eg, section) [IT Dept.]: " SELFSIGNEDSSL_OU + SELFSIGNEDSSL_OU=${SELFSIGNEDSSL_OU:-"IT Dept."} + + openssl req -utf8 -new -newkey rsa:2048 -sha256 -nodes -out ${PATH_SSL}/${domain}.csr -keyout ${PATH_SSL}/${domain}.key -subj "/C=${SELFSIGNEDSSL_C}/ST=${SELFSIGNEDSSL_ST}/L=${SELFSIGNEDSSL_L}/O=${SELFSIGNEDSSL_O}/OU=${SELFSIGNEDSSL_OU}/CN=${domain}" > /dev/null 2>&1 + openssl x509 -req -days 36500 -sha256 -in ${PATH_SSL}/${domain}.csr -signkey ${PATH_SSL}/${domain}.key -out ${PATH_SSL}/${domain}.crt > /dev/null 2>&1 + elif [ "${Domian_Mode}" == '3' -o "${dnsapi_flag}" == 'y' ]; then + while :; do echo + echo 'Please select domain cert key length.' + echo "${CMSG}Enter one of 2048, 3072, 4096, 8192 will issue a RSA cert.${CEND}" + echo "${CMSG}Enter one of ec-256, ec-384, ec-521 will issue a ECC cert.${CEND}" + echo + read -e -p "Please enter your cert key length (default 2048): " CERT_KEYLENGTH + if [ "${CERT_KEYLENGTH}" == "" ]; then + CERT_KEYLENGTH="2048" + break + elif [[ "${CERT_KEYLENGTH}" =~ ^2048$|^3072$|^4096$|^8192$|^ec-256$|^ec-384$|^ec-521$ ]]; then + break + else + echo "${CWARNING}input error!${CEND}" + fi + done + if [ ! -e ~/.acme.sh/ca/acme.zerossl.com/v2/DV90/account.key ]; then + while :; do echo + read -e -p "Please enter your email: " EMAIL + echo + if [[ "${EMAIL}" =~ ^[A-Za-z0-9._-]+@[A-Za-z0-9._-]+\.[A-Za-z]{2,9}$ ]]; then + break + else + echo "${CWARNING}input error!${CEND}" + fi + done + ~/.acme.sh/acme.sh --register-account -m ${EMAIL} + fi + if [ "${moredomain}" == "*.${domain}" -o "${dnsapi_flag}" == 'y' ]; then + while :; do echo + echo 'Please select DNS provider:' + echo "${CMSG}dp${CEND},${CMSG}cx${CEND},${CMSG}ali${CEND},${CMSG}cf${CEND},${CMSG}aws${CEND},${CMSG}linode${CEND},${CMSG}he${CEND},${CMSG}namesilo${CEND},${CMSG}dgon${CEND},${CMSG}freedns${CEND},${CMSG}gd${CEND},${CMSG}namecom${CEND} and so on." + echo "${CMSG}More: https://oneinstack.com/faq/letsencrypt${CEND}" + read -e -p "Please enter your DNS provider: " DNS_PRO + if [ -e ~/.acme.sh/dnsapi/dns_${DNS_PRO}.sh ]; then + break + else + echo "${CWARNING}You DNS api mode is not supported${CEND}" + fi + done + while :; do echo + echo "Syntax: export Key1=Value1 ; export Key2=Value1" + read -e -p "Please enter your dnsapi parameters: " DNS_PAR + echo + eval ${DNS_PAR} + if [ $? == 0 ]; then + break + else + echo "${CWARNING}Syntax error! PS: export Ali_Key=LTq ; export Ali_Secret=0q5E${CEND}" + fi + done + [ "${moredomainame_flag}" == 'y' ] && moredomainame_D="$(for D in ${moredomainame}; do echo -d ${D}; done)" + ~/.acme.sh/acme.sh --force --issue -k ${CERT_KEYLENGTH} --dns dns_${DNS_PRO} -d ${domain} ${moredomainame_D} + else + if [ "${nginx_ssl_flag}" == 'y' ]; then + [ ! -d ${web_install_dir}/conf/vhost ] && mkdir ${web_install_dir}/conf/vhost + if [ -n "`ifconfig | grep inet6`" ]; then + echo "server { listen 80; listen [::]:80; server_name ${domain}${moredomainame}; root ${vhostdir}; access_log off; }" > ${web_install_dir}/conf/vhost/${domain}.conf + else + echo "server { listen 80; server_name ${domain}${moredomainame}; root ${vhostdir}; access_log off; }" > ${web_install_dir}/conf/vhost/${domain}.conf + fi + ${web_install_dir}/sbin/nginx -s reload + fi + if [ "${apache_ssl_flag}" == 'y' ]; then + [ ! -d ${apache_install_dir}/conf/vhost ] && mkdir ${apache_install_dir}/conf/vhost + cat > ${apache_install_dir}/conf/vhost/${domain}.conf << EOF + + ServerAdmin admin@example.com + DocumentRoot "${vhostdir}" + ServerName ${domain} + ${Apache_Domain_alias} + + SetOutputFilter DEFLATE + Options FollowSymLinks ExecCGI + ${Apache_grant} + AllowOverride All + Order allow,deny + Allow from all + DirectoryIndex index.html index.php + + +EOF + ${apache_install_dir}/bin/apachectl -k graceful + fi + auth_file="`< /dev/urandom tr -dc A-Za-z0-9 | head -c8`".html + auth_str='oneinstack'; echo ${auth_str} > ${vhostdir}/${auth_file} + for D in ${domain} ${moredomainame} + do + curl_str=`curl --connect-timeout 30 -4 -s $D/${auth_file} 2>&1` + [ "${curl_str}" != "${auth_str}" ] && { echo; echo "${CFAILURE}Let's Encrypt Verify error! DNS problem: NXDOMAIN looking up A for ${D}${CEND}"; } + done + rm -f ${vhostdir}/${auth_file} + [ "${moredomainame_flag}" == 'y' ] && moredomainame_D="$(for D in ${moredomainame}; do echo -d ${D}; done)" + ~/.acme.sh/acme.sh --force --issue -k ${CERT_KEYLENGTH} -w ${vhostdir} -d ${domain} ${moredomainame_D} + fi + [ -e "${PATH_SSL}/${domain}.crt" ] && rm -f ${PATH_SSL}/${domain}.{crt,key} + Nginx_cmd="/bin/systemctl restart nginx" + Apache_cmd="${apache_install_dir}/bin/apachectl -k graceful" + if [ -e "${web_install_dir}/sbin/nginx" -a -e "${apache_install_dir}/bin/httpd" ]; then + Command="${Nginx_cmd};${Apache_cmd}" + elif [ -e "${web_install_dir}/sbin/nginx" -a ! -e "${apache_install_dir}/bin/httpd" ]; then + Command="${Nginx_cmd}" + elif [ ! -e "${web_install_dir}/sbin/nginx" -a -e "${apache_install_dir}/bin/httpd" ]; then + Command="${Apache_cmd}" + fi + if [ -s ~/.acme.sh/${domain}/fullchain.cer ] && [[ "${CERT_KEYLENGTH}" =~ ^2048$|^3072$|^4096$|^8192$ ]]; then + ~/.acme.sh/acme.sh --force --install-cert -d ${domain} --fullchain-file ${PATH_SSL}/${domain}.crt --key-file ${PATH_SSL}/${domain}.key --reloadcmd "${Command}" > /dev/null + elif [ -s ~/.acme.sh/${domain}_ecc/fullchain.cer ] && [[ "${CERT_KEYLENGTH}" =~ ^ec-256$|^ec-384$|^ec-521$ ]]; then + ~/.acme.sh/acme.sh --force --install-cert --ecc -d ${domain} --fullchain-file ${PATH_SSL}/${domain}.crt --key-file ${PATH_SSL}/${domain}.key --reloadcmd "${Command}" > /dev/null + else + echo "${CFAILURE}Error: Create Let's Encrypt SSL Certificate failed! ${CEND}" + [ -e "${web_install_dir}/conf/vhost/${domain}.conf" ] && rm -f ${web_install_dir}/conf/vhost/${domain}.conf + [ -e "${apache_install_dir}/conf/vhost/${domain}.conf" ] && rm -f ${apache_install_dir}/conf/vhost/${domain}.conf + exit 1 + fi + fi +} + +Print_SSL() { + if [ "${Domian_Mode}" == '2' ]; then + echo "$(printf "%-30s" "Self-signed SSL Certificate:")${CMSG}${PATH_SSL}/${domain}.crt${CEND}" + echo "$(printf "%-30s" "SSL Private Key:")${CMSG}${PATH_SSL}/${domain}.key${CEND}" + echo "$(printf "%-30s" "SSL CSR File:")${CMSG}${PATH_SSL}/${domain}.csr${CEND}" + elif [ "${Domian_Mode}" == '3' -o "${dnsapi_flag}" == 'y' ]; then + echo "$(printf "%-30s" "Let's Encrypt SSL Certificate:")${CMSG}${PATH_SSL}/${domain}.crt${CEND}" + echo "$(printf "%-30s" "SSL Private Key:")${CMSG}${PATH_SSL}/${domain}.key${CEND}" + fi +} + +Input_Add_proxy() { + while :; do echo + read -e -p "Please input the correct proxy_pass: " Proxy_Pass + if [ -z "$(echo $Proxy_Pass | grep -E '^http://|https://')" ]; then + echo "${CFAILURE}input error! Please only input example http://192.168.1.1:8080${CEND}" + else + echo "proxy_pass=${Proxy_Pass}" + break + fi + done +} + +Input_Add_domain() { + if [ "${sslquiet_flag}" != 'y' ]; then + while :;do + printf " +What Are You Doing? +\t${CMSG}1${CEND}. Use HTTP Only +\t${CMSG}2${CEND}. Use your own SSL Certificate and Key +\t${CMSG}3${CEND}. Use Let's Encrypt to Create SSL Certificate and Key +\t${CMSG}q${CEND}. Exit +" + read -e -p "Please input the correct option: " Domian_Mode + if [[ ! "${Domian_Mode}" =~ ^[1-3,q]$ ]]; then + echo "${CFAILURE}input error! Please only input 1~3 and q${CEND}" + else + break + fi + done + fi + + #Multiple_PHP + if [ $(ls /dev/shm/php*-cgi.sock 2> /dev/null | wc -l) -ge 2 ]; then + if [ "${mphp_flag}" != 'y' ]; then + PHP_detail_ver=`${php_install_dir}/bin/php-config --version` + PHP_main_ver=${PHP_detail_ver%.*} + while :; do echo + echo 'Please select a version of the PHP:' + echo -e "\t${CMSG} 0${CEND}. PHP ${PHP_main_ver} (default)" + [ -e "/dev/shm/php53-cgi.sock" ] && echo -e "\t${CMSG} 1${CEND}. PHP 5.3" + [ -e "/dev/shm/php54-cgi.sock" ] && echo -e "\t${CMSG} 2${CEND}. PHP 5.4" + [ -e "/dev/shm/php55-cgi.sock" ] && echo -e "\t${CMSG} 3${CEND}. PHP 5.5" + [ -e "/dev/shm/php56-cgi.sock" ] && echo -e "\t${CMSG} 4${CEND}. PHP 5.6" + [ -e "/dev/shm/php70-cgi.sock" ] && echo -e "\t${CMSG} 5${CEND}. PHP 7.0" + [ -e "/dev/shm/php71-cgi.sock" ] && echo -e "\t${CMSG} 6${CEND}. PHP 7.1" + [ -e "/dev/shm/php72-cgi.sock" ] && echo -e "\t${CMSG} 7${CEND}. PHP 7.2" + [ -e "/dev/shm/php73-cgi.sock" ] && echo -e "\t${CMSG} 8${CEND}. PHP 7.3" + [ -e "/dev/shm/php74-cgi.sock" ] && echo -e "\t${CMSG} 9${CEND}. PHP 7.4" + [ -e "/dev/shm/php80-cgi.sock" ] && echo -e "\t${CMSG}10${CEND}. PHP 8.0" + [ -e "/dev/shm/php81-cgi.sock" ] && echo -e "\t${CMSG}11${CEND}. PHP 8.1" + [ -e "/dev/shm/php82-cgi.sock" ] && echo -e "\t${CMSG}12${CEND}. PHP 8.2" + [ -e "/dev/shm/php83-cgi.sock" ] && echo -e "\t${CMSG}13${CEND}. PHP 8.3" + read -e -p "Please input a number:(Default 0 press Enter) " php_option + php_option=${php_option:-0} + if [[ ! ${php_option} =~ ^[0-9]$|^1[0-2]$ ]]; then + echo "${CWARNING}input error! Please only input number 1~12${CEND}" + else + break + fi + done + fi + [ "${php_option}" == '1' ] && mphp_ver=53 + [ "${php_option}" == '2' ] && mphp_ver=54 + [ "${php_option}" == '3' ] && mphp_ver=55 + [ "${php_option}" == '4' ] && mphp_ver=56 + [ "${php_option}" == '5' ] && mphp_ver=70 + [ "${php_option}" == '6' ] && mphp_ver=71 + [ "${php_option}" == '7' ] && mphp_ver=72 + [ "${php_option}" == '8' ] && mphp_ver=73 + [ "${php_option}" == '9' ] && mphp_ver=74 + [ "${php_option}" == '10' ] && mphp_ver=80 + [ "${php_option}" == '11' ] && mphp_ver=81 + [ "${php_option}" == '12' ] && mphp_ver=82 + [ "${php_option}" == '13' ] && mphp_ver=83 + [ ! -e "/dev/shm/php${mphp_ver}-cgi.sock" ] && unset mphp_ver + fi + + case "${NGX_FLAG}" in + "php") + NGX_CONF=$(echo -e "location ~ [^/]\.php(/|$) {\n #fastcgi_pass remote_php_ip:9000;\n fastcgi_pass unix:/dev/shm/php${mphp_ver}-cgi.sock;\n fastcgi_index index.php;\n include fastcgi.conf;\n }") + ;; + "java") + NGX_CONF=$(echo -e "location ~ {\n proxy_pass http://127.0.0.1:8080;\n include proxy.conf;\n }") + ;; + esac + + if [ "${Domian_Mode}" == '3' -o "${dnsapi_flag}" == 'y' ] && [ ! -e ~/.acme.sh/acme.sh ]; then + pushd ${oneinstack_dir}/src > /dev/null + [ ! -e acme.sh-master.tar.gz ] && wget -qc ${mirror_link}/oneinstack/src/acme.sh-master.tar.gz + tar xzf acme.sh-master.tar.gz + pushd acme.sh-master > /dev/null + ./acme.sh --install > /dev/null 2>&1 + popd > /dev/null + popd > /dev/null + fi + [ -e ~/.acme.sh/account.conf ] && sed -i '/^CERT_HOME=/d' ~/.acme.sh/account.conf + if [[ "${Domian_Mode}" =~ ^[2-3]$ ]] || [ "${dnsapi_flag}" == 'y' ]; then + if [ -e "${web_install_dir}/sbin/nginx" ]; then + nginx_ssl_flag=y + PATH_SSL=${web_install_dir}/conf/ssl + [ ! -d "${PATH_SSL}" ] && mkdir ${PATH_SSL} + elif [ ! -e "${web_install_dir}/sbin/nginx" -a -e "${apache_install_dir}/bin/httpd" ]; then + apache_ssl_flag=y + PATH_SSL=${apache_install_dir}/conf/ssl + [ ! -d "${PATH_SSL}" ] && mkdir ${PATH_SSL} + fi + elif [ "${Domian_Mode}" == 'q' ]; then + exit 1 + fi + + while :; do echo + read -e -p "Please input domain(example: www.example.com): " domain + if [ -z "$(echo ${domain} | grep '.*\..*')" ]; then + echo "${CWARNING}Your ${domain} is invalid! ${CEND}" + else + break + fi + done + + if [ -e "${web_install_dir}/conf/vhost/${domain}.conf" -o -e "${apache_install_dir}/conf/vhost/${domain}.conf" -o -e "${tomcat_install_dir}/conf/vhost/${domain}.xml" ]; then + [ -e "${web_install_dir}/conf/vhost/${domain}.conf" ] && echo -e "${domain} in the Nginx/Tengine/OpenResty already exist! \nYou can delete ${CMSG}${web_install_dir}/conf/vhost/${domain}.conf${CEND} and re-create" + [ -e "${apache_install_dir}/conf/vhost/${domain}.conf" ] && echo -e "${domain} in the Apache already exist! \nYou can delete ${CMSG}${apache_install_dir}/conf/vhost/${domain}.conf${CEND} and re-create" + [ -e "${tomcat_install_dir}/conf/vhost/${domain}.xml" ] && echo -e "${domain} in the Tomcat already exist! \nYou can delete ${CMSG}${tomcat_install_dir}/conf/vhost/${domain}.xml${CEND} and re-create" + exit + else + echo "domain=${domain}" + fi + if [[ -z ${proxy_flag} || "${proxy_flag}" != 'y' ]]; then + while :; do echo + echo "Please input the directory for the domain:${domain} :" + read -e -p "(Default directory: ${wwwroot_dir}/${domain}): " vhostdir + if [ -n "${vhostdir}" -a -z "$(echo ${vhostdir} | grep '^/')" ]; then + echo "${CWARNING}input error! Press Enter to continue...${CEND}" + else + if [ -z "${vhostdir}" ]; then + vhostdir="${wwwroot_dir}/${domain}" + echo "Virtual Host Directory=${CMSG}${vhostdir}${CEND}" + fi + echo + echo "Create Virtul Host directory......" + mkdir -p ${vhostdir} + echo "set permissions of Virtual Host directory......" + chown -R ${run_user}:${run_group} ${vhostdir} + break + fi + done + fi + + while :; do echo + read -e -p "Do you want to add more domain name? [y/n]: " moredomainame_flag + if [[ ! ${moredomainame_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + + if [ "${moredomainame_flag}" == 'y' ]; then + while :; do echo + read -e -p "Type domainname or IP(example: example.com other.example.com): " moredomain + if [ -z "$(echo ${moredomain} | grep '.*\..*')" ]; then + echo "${CWARNING}Your ${domain} is invalid! ${CEND}" + else + [ "${moredomain}" == "${domain}" ] && echo "${CWARNING}Domain name already exists! ${CND}" && continue + echo domain list="$moredomain" + moredomainame=" $moredomain" + break + fi + done + Apache_Domain_alias=ServerAlias${moredomainame} + Tomcat_Domain_alias=$(for D in $(echo ${moredomainame}); do echo "${D}"; done) + + if [ -e "${web_install_dir}/sbin/nginx" ]; then + while :; do echo + read -e -p "Do you want to redirect from ${moredomain} to ${domain}? [y/n]: " redirect_flag + if [[ ! ${redirect_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + [ "${redirect_flag}" == 'y' ] && Nginx_redirect="if (\$host != ${domain}) { return 301 \$scheme://${domain}\$request_uri; }" + fi + fi + + if [ "${nginx_ssl_flag}" == 'y' ]; then + while :; do echo + read -e -p "Do you want to redirect all HTTP requests to HTTPS? [y/n]: " https_flag + if [[ ! ${https_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + + if [[ "$(${web_install_dir}/sbin/nginx -V 2>&1 | grep -Eo 'with-http_v2_module')" = 'with-http_v2_module' ]]; then + LISTENOPT="443 ssl http2" + else + LISTENOPT="443 ssl spdy" + fi + Create_SSL + if [ -n "`ifconfig | grep inet6`" ]; then + Nginx_conf=$(echo -e "listen 80;\n listen [::]:80;\n listen ${LISTENOPT};\n listen [::]:${LISTENOPT};\n ssl_certificate ${PATH_SSL}/${domain}.crt;\n ssl_certificate_key ${PATH_SSL}/${domain}.key;\n ssl_protocols TLSv1.2 TLSv1.3;\n ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;\n ssl_ciphers ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384:DHE-RSA-AES128-GCM-SHA256;\n ssl_conf_command Ciphersuites TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256;\n ssl_conf_command Options PrioritizeChaCha;\n ssl_prefer_server_ciphers on;\n ssl_session_timeout 10m;\n ssl_session_cache shared:SSL:10m;\n ssl_buffer_size 2k;\n add_header Strict-Transport-Security max-age=15768000;\n ssl_stapling on;\n ssl_stapling_verify on;\n") + else + Nginx_conf=$(echo -e "listen 80;\n listen ${LISTENOPT};\n ssl_certificate ${PATH_SSL}/${domain}.crt;\n ssl_certificate_key ${PATH_SSL}/${domain}.key;\n ssl_protocols TLSv1.2 TLSv1.3;\n ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;\n ssl_ciphers ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384:DHE-RSA-AES128-GCM-SHA256;\n ssl_conf_command Ciphersuites TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256;\n ssl_conf_command Options PrioritizeChaCha;\n ssl_prefer_server_ciphers on;\n ssl_session_timeout 10m;\n ssl_session_cache shared:SSL:10m;\n ssl_buffer_size 2k;\n add_header Strict-Transport-Security max-age=15768000;\n ssl_stapling on;\n ssl_stapling_verify on;\n") + fi + Apache_SSL=$(echo -e "SSLEngine on\n SSLCertificateFile \"${PATH_SSL}/${domain}.crt\"\n SSLCertificateKeyFile \"${PATH_SSL}/${domain}.key\"") + elif [ "${apache_ssl_flag}" == 'y' ]; then + Create_SSL + Apache_SSL=$(echo -e "SSLEngine on\n SSLCertificateFile \"${PATH_SSL}/${domain}.crt\"\n SSLCertificateKeyFile \"${PATH_SSL}/${domain}.key\"") + [ -z "$(grep 'Listen 443' ${apache_install_dir}/conf/httpd.conf)" ] && sed -i "s@Listen 80@&\nListen 443@" ${apache_install_dir}/conf/httpd.conf + [ -z "$(grep 'ServerName 0.0.0.0:443' ${apache_install_dir}/conf/httpd.conf)" ] && sed -i "s@ServerName 0.0.0.0:80@&\nServerName 0.0.0.0:443@" ${apache_install_dir}/conf/httpd.conf + else + if [ -n "`ifconfig | grep inet6`" ]; then + Nginx_conf=$(echo -e "listen 80;\n listen [::]:80;") + else + Nginx_conf=$(echo -e "listen 80;") + fi + fi +} + +Nginx_anti_hotlinking() { + while :; do echo + read -e -p "Do you want to add hotlink protection? [y/n]: " anti_hotlinking_flag + if [[ ! ${anti_hotlinking_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + + if [ -n "$(echo ${domain} | grep '.*\..*\..*')" ]; then + domain_allow="*.${domain#*.} ${domain}" + else + domain_allow="*.${domain} ${domain}" + fi + + if [ "${anti_hotlinking_flag}" == 'y' ]; then + if [ "${moredomainame_flag}" == 'y' -a "${moredomain}" != "*.${domain}" ]; then + domain_allow_all=${domain_allow}${moredomainame} + else + domain_allow_all=${domain_allow} + fi + domain_allow_all=`echo ${domain_allow_all} | tr ' ' '\n' | awk '!a[$1]++' | xargs` + anti_hotlinking=$(echo -e "location ~ .*\.(wma|wmv|asf|mp3|mmf|zip|rar|jpg|gif|png|swf|flv|mp4)$ {\n valid_referers none blocked ${domain_allow_all};\n if (\$invalid_referer) {\n return 403;\n }\n }") + fi +} + +Nginx_rewrite() { + [ ! -d "${web_install_dir}/conf/rewrite" ] && mkdir ${web_install_dir}/conf/rewrite + while :; do echo + read -e -p "Allow Rewrite rule? [y/n]: " rewrite_flag + if [[ ! "${rewrite_flag}" =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + if [ "${rewrite_flag}" == 'n' ]; then + rewrite="none" + touch "${web_install_dir}/conf/rewrite/${rewrite}.conf" + else + echo + echo "Please input the rewrite of programme :" + echo "${CMSG}wordpress${CEND},${CMSG}opencart${CEND},${CMSG}magento2${CEND},${CMSG}drupal${CEND},${CMSG}joomla${CEND},${CMSG}codeigniter${CEND},${CMSG}laravel${CEND}" + echo "${CMSG}thinkphp${CEND},${CMSG}pathinfo${CEND},${CMSG}discuz${CEND},${CMSG}typecho${CEND},${CMSG}ecshop${CEND},${CMSG}nextcloud${CEND},${CMSG}zblog${CEND},${CMSG}whmcs${CEND} rewrite was exist." + read -e -p "(Default rewrite: other): " rewrite + if [ "${rewrite}" == "" ]; then + rewrite="other" + fi + echo "You choose rewrite=${CMSG}$rewrite${CEND}" + [ "${NGX_FLAG}" == 'php' -a "${rewrite}" == "joomla" ] && NGX_CONF=$(echo -e "location ~ \\.php\$ {\n #fastcgi_pass remote_php_ip:9000;\n fastcgi_pass unix:/dev/shm/php${mphp_ver}-cgi.sock;\n fastcgi_index index.php;\n include fastcgi.conf;\n }") + [ "${NGX_FLAG}" == 'php' ] && [[ "${rewrite}" =~ ^codeigniter$|^thinkphp$|^pathinfo$ ]] && NGX_CONF=$(echo -e "location ~ [^/]\.php(/|\$) {\n #fastcgi_pass remote_php_ip:9000;\n fastcgi_pass unix:/dev/shm/php${mphp_ver}-cgi.sock;\n fastcgi_index index.php;\n include fastcgi.conf;\n fastcgi_split_path_info ^(.+?\.php)(/.*)\$;\n set \$path_info \$fastcgi_path_info;\n fastcgi_param PATH_INFO \$path_info;\n try_files \$fastcgi_script_name =404; \n }") + [ "${NGX_FLAG}" == 'php' -a "${rewrite}" == "typecho" ] && NGX_CONF=$(echo -e "location ~ .*\.php(\/.*)*\$ {\n #fastcgi_pass remote_php_ip:9000;\n fastcgi_pass unix:/dev/shm/php${mphp_ver}-cgi.sock;\n fastcgi_index index.php;\n include fastcgi.conf;\n set \$path_info \"\";\n set \$real_script_name \$fastcgi_script_name;\n if (\$fastcgi_script_name ~ \"^(.+?\.php)(/.+)\$\") {\n set \$real_script_name \$1;\n set \$path_info \$2;\n }\n fastcgi_param SCRIPT_FILENAME \$document_root\$real_script_name;\n fastcgi_param SCRIPT_NAME \$real_script_name;\n fastcgi_param PATH_INFO \$path_info;\n }") + if [[ ! "${rewrite}" =~ ^magento2$|^pathinfo$ ]]; then + if [ -e "config/${rewrite}.conf" ]; then + /bin/cp config/${rewrite}.conf ${web_install_dir}/conf/rewrite/${rewrite}.conf + else + touch "${web_install_dir}/conf/rewrite/${rewrite}.conf" + fi + fi + fi +} + +Nginx_log() { + while :; do echo + read -e -p "Allow Nginx/Tengine/OpenResty access_log? [y/n]: " access_flag + if [[ ! "${access_flag}" =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + if [ "${access_flag}" == 'n' ]; then + Nginx_log="access_log off;" + else + Nginx_log="access_log ${wwwlogs_dir}/${domain}_nginx.log combined;" + echo "You access log file=${CMSG}${wwwlogs_dir}/${domain}_nginx.log${CEND}" + fi +} + +Create_nginx_tomcat_conf() { + [ ! -d ${web_install_dir}/conf/vhost ] && mkdir ${web_install_dir}/conf/vhost + cat > ${web_install_dir}/conf/vhost/${domain}.conf << EOF +server { + ${Nginx_conf} + server_name ${domain}${moredomainame}; + ${Nginx_log} + index index.html index.htm index.jsp; + root ${vhostdir}; + ${Nginx_redirect} + #error_page 404 /404.html; + #error_page 502 /502.html; + ${anti_hotlinking} + location ~ .*\.(gif|jpg|jpeg|png|bmp|swf|flv|mp4|ico)$ { + expires 30d; + access_log off; + } + location ~ .*\.(js|css)?$ { + expires 7d; + access_log off; + } + location ~ /(\.user\.ini|\.ht|\.git|\.svn|\.project|LICENSE|README\.md) { + deny all; + } + location /.well-known { + allow all; + } + ${NGX_CONF} +} +EOF + + [ "${https_flag}" == 'y' ] && sed -i "s@^root.*;@&\nif (\$ssl_protocol = \"\") { return 301 https://\$host\$request_uri; }@" ${web_install_dir}/conf/vhost/${domain}.conf + + cat > ${tomcat_install_dir}/conf/vhost/${domain}.xml << EOF + ${Tomcat_Domain_alias} + + + + +EOF + [ -z "$(grep -o "vhost-${domain} SYSTEM" ${tomcat_install_dir}/conf/server.xml)" ] && sed -i "/vhost-localhost SYSTEM/a<\!ENTITY vhost-${domain} SYSTEM \"file://${tomcat_install_dir}/conf/vhost/${domain}.xml\">" ${tomcat_install_dir}/conf/server.xml + [ -z "$(grep -o "vhost-${domain};" ${tomcat_install_dir}/conf/server.xml)" ] && sed -i "s@vhost-localhost;@&\n \&vhost-${domain};@" ${tomcat_install_dir}/conf/server.xml + + echo + ${web_install_dir}/sbin/nginx -t + if [ $? == 0 ]; then + echo "Reload Nginx......" + ${web_install_dir}/sbin/nginx -s reload + service tomcat restart + else + rm -f ${web_install_dir}/conf/vhost/${domain}.conf + echo "Create virtualhost ... [${CFAILURE}FAILED${CEND}]" + exit 1 + fi + + printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# For more information please visit https://oneinstack.com # +####################################################################### +" + echo "$(printf "%-30s" "Your domain:")${CMSG}${domain}${CEND}" + echo "$(printf "%-30s" "Nginx Virtualhost conf:")${CMSG}${web_install_dir}/conf/vhost/${domain}.conf${CEND}" + echo "$(printf "%-30s" "Tomcat Virtualhost conf:")${CMSG}${tomcat_install_dir}/conf/vhost/${domain}.xml${CEND}" + echo "$(printf "%-30s" "Directory of:")${CMSG}${vhostdir}${CEND}" + Print_SSL +} + +Create_tomcat_conf() { + cat > ${tomcat_install_dir}/conf/vhost/${domain}.xml << EOF + ${Tomcat_Domain_alias} + + + +EOF + [ -z "$(grep -o "vhost-${domain} SYSTEM" ${tomcat_install_dir}/conf/server.xml)" ] && sed -i "/vhost-localhost SYSTEM/a<\!ENTITY vhost-${domain} SYSTEM \"file://${tomcat_install_dir}/conf/vhost/${domain}.xml\">" ${tomcat_install_dir}/conf/server.xml + [ -z "$(grep -o "vhost-${domain};" ${tomcat_install_dir}/conf/server.xml)" ] && sed -i "s@vhost-localhost;@&\n \&vhost-${domain};@" ${tomcat_install_dir}/conf/server.xml + + echo + service tomcat restart + + printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# For more information please visit https://oneinstack.com # +####################################################################### +" + echo "$(printf "%-30s" "Your domain:")${CMSG}${domain}${CEND}" + echo "$(printf "%-30s" "Tomcat Virtualhost conf:")${CMSG}${tomcat_install_dir}/conf/vhost/${domain}.xml${CEND}" + echo "$(printf "%-30s" "Directory of:")${CMSG}${vhostdir}${CEND}" + echo "$(printf "%-30s" "index url:")${CMSG}http://${domain}:8080/${CEND}" +} + +Create_nginx_phpfpm_conf() { + [ ! -d ${web_install_dir}/conf/vhost ] && mkdir ${web_install_dir}/conf/vhost + cat > ${web_install_dir}/conf/vhost/${domain}.conf << EOF +server { + ${Nginx_conf} + server_name ${domain}${moredomainame}; + ${Nginx_log} + index index.html index.htm index.php; + root ${vhostdir}; + ${Nginx_redirect} + include ${web_install_dir}/conf/rewrite/${rewrite}.conf; + #error_page 404 /404.html; + #error_page 502 /502.html; + ${anti_hotlinking} + ${NGX_CONF} + + location ~ .*\.(gif|jpg|jpeg|png|bmp|swf|flv|mp4|ico)$ { + expires 30d; + access_log off; + } + location ~ .*\.(js|css)?$ { + expires 7d; + access_log off; + } + location ~ /(\.user\.ini|\.ht|\.git|\.svn|\.project|LICENSE|README\.md) { + deny all; + } + location /.well-known { + allow all; + } +} +EOF + + [ "${rewrite}" == 'pathinfo' ] && sed -i '/pathinfo.conf;$/d' ${web_install_dir}/conf/vhost/${domain}.conf + if [ "${rewrite}" == 'magento2' -a -e "config/${rewrite}.conf" ]; then + /bin/cp config/${rewrite}.conf ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@/dev/shm/php-cgi.sock@/dev/shm/php${mphp_ver}-cgi.sock@g" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ set \$MAGE_ROOT.*;@ set \$MAGE_ROOT ${vhostdir};@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@ server_name ${domain}${moredomainame};@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ${Nginx_log}@" ${web_install_dir}/conf/vhost/${domain}.conf + if [ "${anti_hotlinking_flag}" == 'y' ]; then + sed -i "s@^ root.*;@&\n }@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n }@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n return 403;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n rewrite ^/ http://www.linuxeye.com/403.html;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n if (\$invalid_referer) {@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n valid_referers none blocked ${domain_allow_all};@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n location ~ .*\.(wma|wmv|asf|mp3|mmf|zip|rar|jpg|gif|png|swf|flv|mp4)\$ {@" ${web_install_dir}/conf/vhost/${domain}.conf + fi + + [ "${redirect_flag}" == 'y' ] && sed -i "s@^ root.*;@&\n if (\$host != ${domain}) { return 301 \$scheme://${domain}\$request_uri; }@" ${web_install_dir}/conf/vhost/${domain}.conf + + if [ "${nginx_ssl_flag}" == 'y' ]; then + sed -i "s@^ listen 80;@&\n listen ${LISTENOPT};@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_stapling_verify on;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_stapling on;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n add_header Strict-Transport-Security max-age=15768000;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_buffer_size 2k;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_session_cache shared:SSL:10m;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_session_timeout 10m;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_prefer_server_ciphers on;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_conf_command Options PrioritizeChaCha;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_conf_command Ciphersuites TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_ciphers ECDHE-ECDSA-AES256-GCM-SHA384:ECDHE-RSA-AES256-GCM-SHA384:ECDHE-ECDSA-CHACHA20-POLY1305:ECDHE-RSA-CHACHA20-POLY1305:ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:DHE-RSA-AES256-GCM-SHA384:DHE-RSA-AES128-GCM-SHA256;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_ecdh_curve X25519:prime256v1:secp384r1:secp521r1;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_protocols TLSv1.2 TLSv1.3;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_certificate_key ${PATH_SSL}/${domain}.key;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ server_name.*;@&\n ssl_certificate ${PATH_SSL}/${domain}.crt;@" ${web_install_dir}/conf/vhost/${domain}.conf + fi + fi + + [ "${https_flag}" == 'y' ] && sed -i "s@^ root.*;@&\n if (\$ssl_protocol = \"\") { return 301 https://\$host\$request_uri; }@" ${web_install_dir}/conf/vhost/${domain}.conf + + echo + ${web_install_dir}/sbin/nginx -t + if [ $? == 0 ]; then + echo "Reload Nginx......" + ${web_install_dir}/sbin/nginx -s reload + else + rm -f ${web_install_dir}/conf/vhost/${domain}.conf + echo "Create virtualhost ... [${CFAILURE}FAILED${CEND}]" + exit 1 + fi + + printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# For more information please visit https://oneinstack.com # +####################################################################### +" + echo "$(printf "%-30s" "Your domain:")${CMSG}${domain}${CEND}" + echo "$(printf "%-30s" "Virtualhost conf:")${CMSG}${web_install_dir}/conf/vhost/${domain}.conf${CEND}" + echo "$(printf "%-30s" "Directory of:")${CMSG}${vhostdir}${CEND}" + [ "${rewrite_flag}" == 'y' -a "${rewrite}" != 'magento2' -a "${rewrite}" != 'pathinfo' ] && echo "$(printf "%-30s" "Rewrite rule:")${CMSG}${web_install_dir}/conf/rewrite/${rewrite}.conf${CEND}" + Print_SSL +} + +Create_nginx_proxy_conf() { + [ ! -d ${web_install_dir}/conf/vhost ] && mkdir ${web_install_dir}/conf/vhost + cat > ${web_install_dir}/conf/vhost/${domain}.conf << EOF +server { + ${Nginx_conf} + server_name ${domain}${moredomainame}; + ${Nginx_log} + index index.html index.htm index.php; + ${Nginx_redirect} + location / { + proxy_pass ${Proxy_Pass}; + proxy_set_header X-Forwarded-For \$proxy_add_x_forwarded_for; + proxy_set_header Host \$http_host; + proxy_set_header X-NginX-Proxy true; + proxy_http_version 1.1; + proxy_set_header Upgrade \$http_upgrade; + proxy_set_header Connection "upgrade"; + proxy_max_temp_file_size 0; + } + + #error_page 404 /404.html; + #error_page 502 /502.html; + ${anti_hotlinking} + + location ~ .*\.(gif|jpg|jpeg|png|bmp|swf|flv|mp4|ico)$ { + expires 30d; + access_log off; + } + location ~ .*\.(js|css)?$ { + expires 7d; + access_log off; + } + location ~ /(\.user\.ini|\.ht|\.git|\.svn|\.project|LICENSE|README\.md) { + deny all; + } + location /.well-known { + allow all; + } +} +EOF + + [ "${redirect_flag}" == 'y' ] && sed -i "s@^ root.*;@&\n if (\$host != ${domain}) { return 301 \$scheme://${domain}\$request_uri; }@" ${web_install_dir}/conf/vhost/${domain}.conf + + if [ "${anti_hotlinking_flag}" == 'y' ]; then + sed -i "s@^ root.*;@&\n }@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n }@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n return 403;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n rewrite ^/ http://www.linuxeye.com/403.html;@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n if (\$invalid_referer) {@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n valid_referers none blocked ${domain_allow_all};@" ${web_install_dir}/conf/vhost/${domain}.conf + sed -i "s@^ root.*;@&\n location ~ .*\.(wma|wmv|asf|mp3|mmf|zip|rar|jpg|gif|png|swf|flv|mp4)\$ {@" ${web_install_dir}/conf/vhost/${domain}.conf + fi + + [ "${https_flag}" == 'y' ] && sed -i "s@^ root.*;@&\n if (\$ssl_protocol = \"\") { return 301 https://\$host\$request_uri; }@" ${web_install_dir}/conf/vhost/${domain}.conf + + echo + ${web_install_dir}/sbin/nginx -t + if [ $? == 0 ]; then + echo "Reload Nginx......" + ${web_install_dir}/sbin/nginx -s reload + else + rm -f ${web_install_dir}/conf/vhost/${domain}.conf + echo "Create virtualhost ... [${CFAILURE}FAILED${CEND}]" + exit 1 + fi + + printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# For more information please visit https://oneinstack.com # +####################################################################### +" + echo "$(printf "%-30s" "Your domain:")${CMSG}${domain}${CEND}" + echo "$(printf "%-30s" "Virtualhost conf:")${CMSG}${web_install_dir}/conf/vhost/${domain}.conf${CEND}" + #echo "$(printf "%-30s" "Directory of:")${CMSG}${vhostdir}${CEND}" + [ "${rewrite_flag}" == 'y' -a "${rewrite}" != 'magento2' -a "${rewrite}" != 'pathinfo' ] && echo "$(printf "%-30s" "Rewrite rule:")${CMSG}${web_install_dir}/conf/rewrite/${rewrite}.conf${CEND}" + Print_SSL +} + +Apache_log() { + while :; do echo + read -e -p "Allow Apache access_log? [y/n]: " access_flag + if [[ ! "${access_flag}" =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + + if [ "${access_flag}" == 'n' ]; then + Apache_log='CustomLog "/dev/null" common' + else + Apache_log="CustomLog \"${wwwlogs_dir}/${domain}_apache.log\" common" + echo "You access log file=${wwwlogs_dir}/${domain}_apache.log" + fi +} + +Create_apache_conf() { + if [ "${Apache_main_ver}" == '24' ]; then + if [ -e "${php_install_dir}/sbin/php-fpm" ] && [ -n "`grep -E ^LoadModule.*mod_proxy_fcgi.so ${apache_install_dir}/conf/httpd.conf`" ]; then + Apache_fcgi=$(echo -e "\n Order allow,deny\n Deny from all\n \n \n SetHandler \"proxy:unix:/dev/shm/php${mphp_ver}-cgi.sock|fcgi://localhost\"\n ") + fi + fi + [ ! -d ${apache_install_dir}/conf/vhost ] && mkdir ${apache_install_dir}/conf/vhost + cat > ${apache_install_dir}/conf/vhost/${domain}.conf << EOF + + ServerAdmin admin@example.com + DocumentRoot "${vhostdir}" + ServerName ${domain} + ${Apache_Domain_alias} + ErrorLog "${wwwlogs_dir}/${domain}_error_apache.log" + ${Apache_log} + ${Apache_fcgi} + + SetOutputFilter DEFLATE + Options FollowSymLinks ExecCGI + ${Apache_grant} + AllowOverride All + Order allow,deny + Allow from all + DirectoryIndex index.html index.php + + +EOF + [ "${apache_ssl_flag}" == 'y' ] && cat >> ${apache_install_dir}/conf/vhost/${domain}.conf << EOF + + ServerAdmin admin@example.com + DocumentRoot "${vhostdir}" + ServerName ${domain} + ${Apache_Domain_alias} + ${Apache_SSL} + ErrorLog "${wwwlogs_dir}/${domain}_error_apache.log" + ${Apache_log} + ${Apache_fcgi} + + SetOutputFilter DEFLATE + Options FollowSymLinks ExecCGI + ${Apache_grant} + AllowOverride All + Order allow,deny + Allow from all + DirectoryIndex index.html index.php + + +EOF + + echo + ${apache_install_dir}/bin/apachectl -t + if [ $? == 0 ]; then + echo "Restart Apache......" + ${apache_install_dir}/bin/apachectl -k graceful + else + rm -f ${apache_install_dir}/conf/vhost/${domain}.conf + echo "Create virtualhost ... [${CFAILURE}FAILED${CEND}]" + exit 1 + fi + + printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# For more information please visit https://oneinstack.com # +####################################################################### +" + echo "$(printf "%-30s" "Your domain:")${CMSG}${domain}${CEND}" + echo "$(printf "%-30s" "Virtualhost conf:")${CMSG}${apache_install_dir}/conf/vhost/${domain}.conf${CEND}" + echo "$(printf "%-30s" "Directory of:")${CMSG}${vhostdir}${CEND}" + Print_SSL +} + +Create_nginx_apache_modphp_conf() { + # Nginx/Tengine/OpenResty + [ ! -d ${web_install_dir}/conf/vhost ] && mkdir ${web_install_dir}/conf/vhost + cat > ${web_install_dir}/conf/vhost/${domain}.conf << EOF +server { + ${Nginx_conf} + server_name ${domain}${moredomainame}; + ${Nginx_log} + index index.html index.htm index.php; + root ${vhostdir}; + ${Nginx_redirect} + ${anti_hotlinking} + location / { + try_files \$uri @apache; + } + location @apache { + proxy_pass http://127.0.0.1:88; + include proxy.conf; + } + location ~ .*\.(php|php5|cgi|pl)?$ { + proxy_pass http://127.0.0.1:88; + include proxy.conf; + } + location ~ .*\.(gif|jpg|jpeg|png|bmp|swf|flv|mp4|ico)$ { + expires 30d; + access_log off; + } + location ~ .*\.(js|css)?$ { + expires 7d; + access_log off; + } + location ~ /(\.user\.ini|\.ht|\.git|\.svn|\.project|LICENSE|README\.md) { + deny all; + } + location /.well-known { + allow all; + } +} +EOF + + [ "${https_flag}" == 'y' ] && sed -i "s@^ root.*;@&\n if (\$ssl_protocol = \"\") { return 301 https://\$host\$request_uri; }@" ${web_install_dir}/conf/vhost/${domain}.conf + + echo + ${web_install_dir}/sbin/nginx -t + if [ $? == 0 ]; then + echo "Reload Nginx......" + ${web_install_dir}/sbin/nginx -s reload + else + rm -f ${web_install_dir}/conf/vhost/${domain}.conf + echo "Create virtualhost ... [${CFAILURE}FAILED${CEND}]" + fi + + # Apache + if [ "${Apache_main_ver}" == '24' ]; then + if [ -e "${php_install_dir}/sbin/php-fpm" ] && [ -n "`grep -E ^LoadModule.*mod_proxy_fcgi.so ${apache_install_dir}/conf/httpd.conf`" ]; then + Apache_fcgi=$(echo -e "\n Order allow,deny\n Deny from all\n \n \n SetHandler \"proxy:unix:/dev/shm/php${mphp_ver}-cgi.sock|fcgi://localhost\"\n ") + fi + fi + [ ! -d ${apache_install_dir}/conf/vhost ] && mkdir ${apache_install_dir}/conf/vhost + cat > ${apache_install_dir}/conf/vhost/${domain}.conf << EOF + + ServerAdmin admin@example.com + DocumentRoot "${vhostdir}" + ServerName ${domain} + ${Apache_Domain_alias} + ${Apache_SSL} + ErrorLog "${wwwlogs_dir}/${domain}_error_apache.log" + ${Apache_log} + ${Apache_fcgi} + + SetOutputFilter DEFLATE + Options FollowSymLinks ExecCGI + ${Apache_grant} + AllowOverride All + Order allow,deny + Allow from all + DirectoryIndex index.html index.php + + +EOF + + echo + ${apache_install_dir}/bin/apachectl -t + if [ $? == 0 ]; then + echo "Restart Apache......" + ${apache_install_dir}/bin/apachectl -k graceful + else + rm -f ${apache_install_dir}/conf/vhost/${domain}.conf + exit 1 + fi + + printf " +####################################################################### +# OneinStack for CentOS/RedHat 7+ Debian 9+ and Ubuntu 16+ # +# For more information please visit https://oneinstack.com # +####################################################################### +" + echo "$(printf "%-30s" "Your domain:")${CMSG}${domain}${CEND}" + echo "$(printf "%-30s" "Nginx Virtualhost conf:")${CMSG}${web_install_dir}/conf/vhost/${domain}.conf${CEND}" + echo "$(printf "%-30s" "Apache Virtualhost conf:")${CMSG}${apache_install_dir}/conf/vhost/${domain}.conf${CEND}" + echo "$(printf "%-30s" "Directory of:")${CMSG}${vhostdir}${CEND}" + Print_SSL +} + +Add_Vhost() { + if [ -e "${web_install_dir}/sbin/nginx" -a ! -e "${apache_install_dir}/bin/httpd" ]; then + Choose_ENV + Input_Add_domain + Nginx_anti_hotlinking + if [ "${proxy_flag}" == "y" ]; then + Input_Add_proxy + Create_nginx_proxy_conf + else + Nginx_rewrite + if [ "${NGX_FLAG}" == "java" ]; then + Nginx_log + Create_nginx_tomcat_conf + else + Nginx_log + Create_nginx_phpfpm_conf + fi + fi + elif [ ! -e "${web_install_dir}/sbin/nginx" -a -e "${apache_install_dir}/bin/httpd" ]; then + Choose_ENV + Input_Add_domain + Apache_log + Create_apache_conf + elif [ ! -e "${web_install_dir}/sbin/nginx" -a ! -e "${apache_install_dir}/bin/httpd" -a -e "${tomcat_install_dir}/conf/server.xml" ]; then + Choose_ENV + Input_Add_domain + Create_tomcat_conf + elif [ -e "${web_install_dir}/sbin/nginx" -a -e "${apache_install_dir}/bin/httpd" ]; then + Choose_ENV + Input_Add_domain + Nginx_anti_hotlinking + if [ "${NGX_FLAG}" == "java" ]; then + Nginx_rewrite + Nginx_log + Create_nginx_tomcat_conf + elif [ "${NGX_FLAG}" == "php" ]; then + Nginx_log + Apache_log + Create_nginx_apache_modphp_conf + fi + else + echo "Error! ${CFAILURE}Web server${CEND} not found!" + fi +} + +Del_NGX_Vhost() { + if [ -e "${web_install_dir}/sbin/nginx" ]; then + [ -d "${web_install_dir}/conf/vhost" ] && Domain_List=$(ls ${web_install_dir}/conf/vhost | sed "s@.conf@@g") + if [ -n "${Domain_List}" ]; then + echo + echo "Virtualhost list:" + echo ${CMSG}${Domain_List}${CEND} + while :; do echo + read -e -p "Please input a domain you want to delete: " domain + if [ -z "$(echo ${domain} | grep '.*\..*')" ]; then + echo "${CWARNING}Your ${domain} is invalid! ${CEND}" + else + if [ -e "${web_install_dir}/conf/vhost/${domain}.conf" ]; then + Directory=$(grep '^ root' ${web_install_dir}/conf/vhost/${domain}.conf | head -1 | awk -F'[ ;]' '{print $(NF-1)}') + rm -f ${web_install_dir}/conf/vhost/${domain}.conf + [ -e "${web_install_dir}/conf/ssl/${domain}.crt" ] && rm -f ${web_install_dir}/conf/ssl/${domain}.{crt,key} + ${web_install_dir}/sbin/nginx -s reload + while :; do echo + read -e -p "Do you want to delete Virtul Host directory? [y/n]: " Del_Vhost_wwwroot_flag + if [[ ! ${Del_Vhost_wwwroot_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + if [ "${Del_Vhost_wwwroot_flag}" == 'y' ]; then + if [ "${quiet_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=$(get_char) + fi + rm -rf ${Directory} + fi + echo + [ -d ~/.acme.sh/${domain} ] && ~/.acme.sh/acme.sh --force --remove -d ${domain} > /dev/null 2>&1 + [ -d ~/.acme.sh/${domain}_ecc ] && ~/.acme.sh/acme.sh --force --remove --ecc -d ${domain} > /dev/null 2>&1 + echo "${CMSG}Domain: ${domain} has been deleted.${CEND}" + echo + else + echo "${CWARNING}Virtualhost: ${domain} was not exist! ${CEND}" + fi + break + fi + done + else + echo "${CWARNING}Virtualhost was not exist! ${CEND}" + fi + fi +} + +Del_Apache_Vhost() { + if [ -e "${apache_install_dir}/bin/httpd" ]; then + if [ -e "${web_install_dir}/sbin/nginx" ]; then + rm -f ${apache_install_dir}/conf/vhost/${domain}.conf + ${apache_install_dir}/bin/apachectl -k graceful + else + Domain_List=$(ls ${apache_install_dir}/conf/vhost | grep -v '0.conf' | sed "s@.conf@@g") + if [ -n "${Domain_List}" ]; then + echo + echo "Virtualhost list:" + echo ${CMSG}${Domain_List}${CEND} + while :; do echo + read -e -p "Please input a domain you want to delete: " domain + if [ -z "$(echo ${domain} | grep '.*\..*')" ]; then + echo "${CWARNING}Your ${domain} is invalid! ${CEND}" + else + if [ -e "${apache_install_dir}/conf/vhost/${domain}.conf" ]; then + Directory=$(grep '^ /dev/null 2>&1 + [ -d ~/.acme.sh/${domain}_ecc ] && ~/.acme.sh/acme.sh --force --remove --ecc -d ${domain} > /dev/null 2>&1 + echo "${CSUCCESS}Domain: ${domain} has been deleted.${CEND}" + else + echo "${CWARNING}Virtualhost: ${domain} was not exist! ${CEND}" + fi + break + fi + done + + else + echo "${CWARNING}Virtualhost was not exist! ${CEND}" + fi + fi + fi +} + +Del_Tomcat_Vhost() { + if [ -e "${tomcat_install_dir}/conf/server.xml" ]; then + if [ -e "${web_install_dir}/sbin/nginx" ]; then + if [ -n "$(echo ${domain} | grep '.*\..*')" ] && [ -n "$(grep vhost-${domain} ${tomcat_install_dir}/conf/server.xml)" ]; then + sed -i /vhost-${domain}/d ${tomcat_install_dir}/conf/server.xml + rm -f ${tomcat_install_dir}/conf/vhost/${domain}.xml + service tomcat restart + fi + else + Domain_List=$(ls ${tomcat_install_dir}/conf/vhost | grep -v 'localhost.xml' | sed "s@.xml@@g") + if [ -n "${Domain_List}" ]; then + echo + echo "Virtualhost list:" + echo ${CMSG}${Domain_List}${CEND} + while :; do echo + read -e -p "Please input a domain you want to delete: " domain + if [ -z "$(echo ${domain} | grep '.*\..*')" ]; then + echo "${CWARNING}Your ${domain} is invalid! ${CEND}" + else + if [ -n "$(grep vhost-${domain} ${tomcat_install_dir}/conf/server.xml)" ]; then + sed -i /vhost-${domain}/d ${tomcat_install_dir}/conf/server.xml + rm -f ${tomcat_install_dir}/conf/vhost/${domain}.xml + service tomcat restart + while :; do echo + read -e -p "Do you want to delete Virtul Host directory? [y/n]: " Del_Vhost_wwwroot_flag + if [[ ! ${Del_Vhost_wwwroot_flag} =~ ^[y,n]$ ]]; then + echo "${CWARNING}input error! Please only input 'y' or 'n'${CEND}" + else + break + fi + done + + if [ "${Del_Vhost_wwwroot_flag}" == 'y' ]; then + if [ "${quiet_flag}" != 'y' ]; then + echo "Press Ctrl+c to cancel or Press any key to continue..." + char=$(get_char) + fi + rm -rf ${Directory} + fi + echo "${CSUCCESS}Domain: ${domain} has been deleted.${CEND}" + else + echo "${CWARNING}Virtualhost: ${domain} was not exist! ${CEND}" + fi + break + fi + done + + else + echo "${CWARNING}Virtualhost was not exist! ${CEND}" + fi + fi + fi +} + +List_Vhost() { + [ -e "${tomcat_install_dir}/conf/server.xml" -a ! -d "${web_install_dir}/sbin/nginx" ] && Domain_List=$(ls ${tomcat_install_dir}/conf/vhost | grep -v 'localhost.xml' | sed "s@.xml@@g") + [ -d "${web_install_dir}/conf/vhost" ] && Domain_List=$(ls ${web_install_dir}/conf/vhost | sed "s@.conf@@g") + [ -e "${apache_install_dir}/bin/httpd" -a ! -d "${web_install_dir}/conf/vhost" ] && Domain_List=$(ls ${apache_install_dir}/conf/vhost | grep -v '0.conf' | sed "s@.conf@@g") + if [ -n "${Domain_List}" ]; then + echo + echo "Virtualhost list:" + for D in ${Domain_List}; do echo ${CMSG}${D}${CEND}; done + else + echo "${CWARNING}Virtualhost was not exist! ${CEND}" + fi +} + +if [ ${ARG_NUM} == 0 ]; then + Install_openSSL | tee -a ${oneinstack_dir}/install.log + Add_Vhost +else + [ "${add_flag}" == 'y' -o "${proxy_flag}" == 'y' -o "${sslquiet_flag}" == 'y' ] && Add_Vhost + [ "${list_flag}" == 'y' ] && List_Vhost + [ "${delete_flag}" == 'y' ] && { Del_NGX_Vhost; Del_Apache_Vhost; Del_Tomcat_Vhost; } +fi